
L'opération Endgame démantèle l'infrastructure de Gootloader, CastleRAT et StealC et récupère plus de 6 millions d'identifiants.
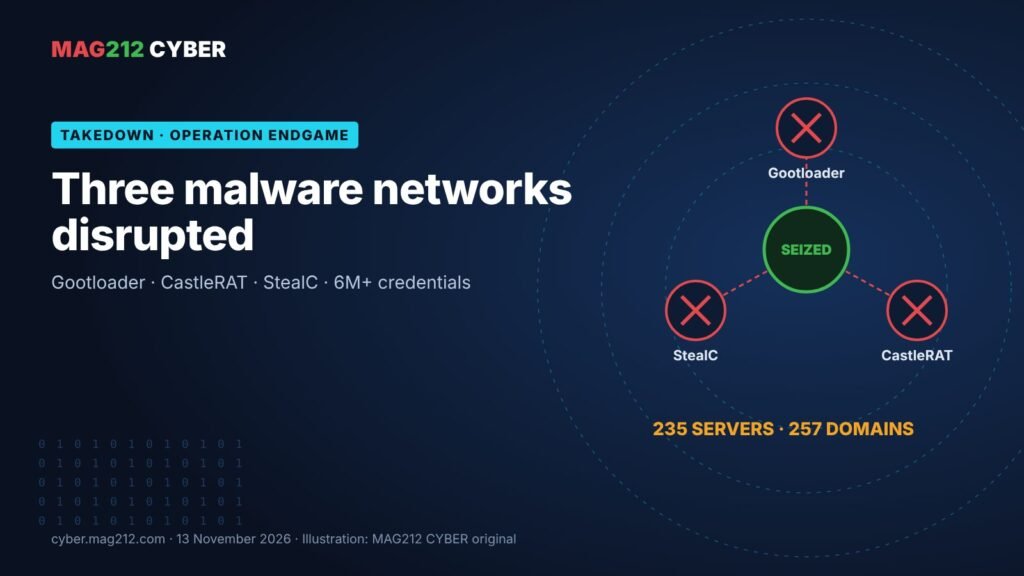
The latest phase of Operation Endgame went after three of the tools that sit at the start of many ransomware attacks: Gootloader, which lures people into downloading fake legal documents; CastleRAT, a remote-access trojan; and StealC, a credential stealer. Europol says agencies from nine countries, working with private partners, actioned 235 servers and 257 domains and identified more than 6 million stolen credentials. Victims will be told through Have I Been Pwned and other notification services. Europol mentions no arrests.
| Actioned | 235 servers, 257 domains |
| Informations d'identification | Over 6 million identified (6.4M datasets) |
| WordPress | 681 infected sites remediated |
| Notification | HIBP, DIVD, Shadowserver, NL-NCSC and others |
Ce qui s'est passé
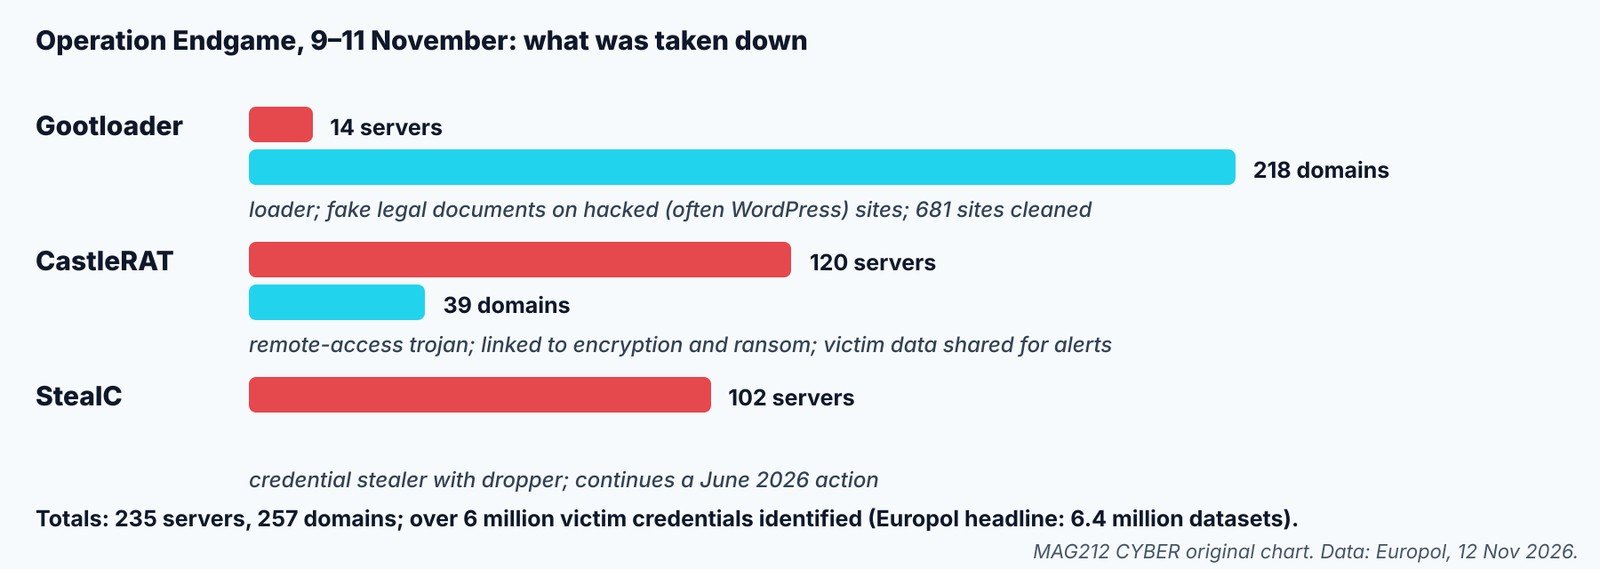
[Confirmé] Europol says law enforcement and private partners actioned 235 servers and 257 domains behind three “cybercrime-as-a-service” tools. Germany’s BKA dates the action to 9–11 November. Agencies from Bulgaria, Canada, Denmark, Germany, Moldova, the Netherlands, Poland, the UK and the US took part, with Europol’s EC3 and Eurojust. Europol mentions no arrests. (Europol) (BKA)
Who is affected and how the tools work
[Confirmé] Gootloader spread through fake legal documents on hacked, often WordPress, sites and led on to ransomware: 14 servers and 218 domains came down and 681 infected websites were cleaned. CastleRAT, a remote-access trojan known since 2025, was linked to encrypted data and ransom payments: 120 servers and 39 domains were seized, with victim data shared for alerts. StealC, a credential stealer with a dropper, lost 102 servers, continuing a June 2026 action. Victims of stolen CastleRAT credentials will be alerted through HaveIBeenPwned, DIVD, CheckjeHack, NoMoreLeaks, Sekoia, the Shadowserver Foundation and NL-NCSC. (Europol)
What to look for and do
- Watch the notification channels. Check your domains with Have I Been Pwned domain search, and your Shadowserver reports if you subscribe.
- [Analyse MAG212] For each validated hit: isolate the device, reset passwords from a clean machine, and revoke sessions and tokens, because stealers take cookies as well as passwords. Then review MFA methods, mailbox rules and OAuth grants for the account.
- [Analyse MAG212] Hunt Gootloader: look for a browser download of a
.zipfollowed bywscript.exeoucscript.exerunning a.jsfile, and for new scheduled tasks soon after. - WordPress owners: Europol urges updated credentials, MFA and patching. Also verify core, plugins and themes against clean copies.
Vérifier la récupération : old sessions are rejected, no new sign-ins from unknown locations, and the rebuilt device is clean. Prévention: see this issue’s awareness lesson on downloading templates safely.
What a takedown does and doesn’t do
[Analyse MAG212] Seizing servers and domains breaks the operators’ infrastructure and gives investigators the data on it, including stolen credentials and victim lists. It doesn’t clean infected computers, and it doesn’t make stolen passwords or session cookies stop working. Those still have to be reset and revoked by the organisations they belong to.
[Analyse MAG212] Past Endgame phases have shown that operators rebuild, sometimes within weeks. The lasting value of an action like this is the victim data it recovers and the notifications that follow, which tell organisations about compromises they would otherwise never have found.
[Confirmé] Gootloader relied on hacked websites, many running WordPress, to host its lures. Europol says 681 infected sites were cleaned and urges site owners to update credentials, turn on multi-factor authentication and keep software patched.
Pourquoi c'est important
Loaders, remote-access trojans and infostealers are how many ransomware intrusions begin. Stolen credentials and session cookies let attackers log in as real users, often bypassing multi-factor authentication. A notification that your users’ credentials were in this haul is a warning that someone may already have used them.
En résumé
Check your domains in Have I Been Pwned and watch Shadowserver and national CERT notifications. For each confirmed victim, isolate the device, reset passwords from a clean machine and revoke sessions and tokens. Hunt for the Gootloader pattern of a ZIP download followed by a script running, and if you run WordPress, check it against clean copies and enforce MFA for admins.
Comment nous étiquetons les preuves : [Confirmé] provient d'une source primaire telle qu'un fournisseur ou la CISA ; [Signalé] à partir d'une sortie secondaire ; [Revendiqué] d'un attaquant ou d'une partie non vérifiée ; [Analyse MAG212] est notre jugement; [Inconnu] Les termes « non établi » n'étaient pas encore disponibles au moment de la publication. Les commandes et indicateurs sont tirés des sources citées et n'ont pas été testés par MAG212 CYBER.
Cette histoire fait partie de MAG212 CYBER Daily, 13 November 2026, Retrouvez également les autres informations vérifiées du jour, la rubrique Action Desk du Defender et un registre complet des sources. Recevez gratuitement le briefing quotidien : abonnez-vous à MAG212 CYBER. Par El Mostafa Ouchen.