
Fireworks AI Breach Spreads to Uber, Cursor and Notion: What Each Company Has Confirmed
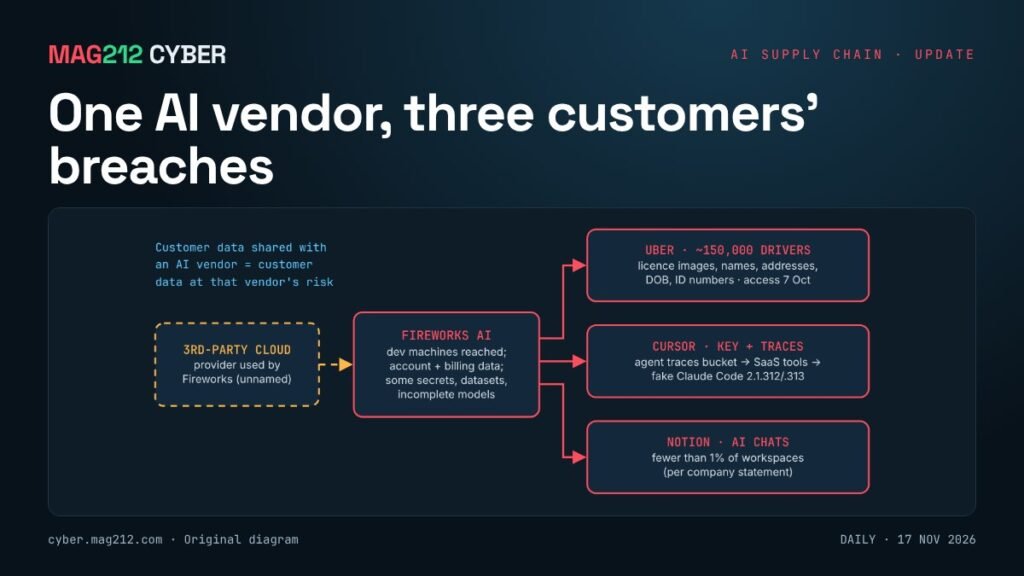
De la part de MAG212 CYBER Daily, 17 November 2026. Chaque commande est copiée de la documentation officielle ou de l'analyse citée et a été non testé par MAG212; exécutez-le uniquement sur les systèmes que vous êtes autorisé à administrer.
Statut: Confirmed by Uber, Cursor and Fireworks. Cursor published an incident update on 13 November naming Fireworks as the starting point; Uber’s breach notifications and Fireworks’ role were reported from 13 to 16 November. The attacker has not been identified. This updates our [14 November Weekly](https://cyber.mag212.com/cursor-extension-backdoor-fireworks-vendor-key-notion/). [1][2][3][7]
What changed since our Weekly
On 14 November we covered Cursor’s poisoned Claude Code extension. Since then: Cursor named Fireworks AI as the origin; Uber began notifying about 150,000 drivers whose data was held by Fireworks; Notion confirmed some AI chats were exposed; and Fireworks itself widened the scope of its incident in a 9 November update. [1][2][3][4]
Fireworks AI
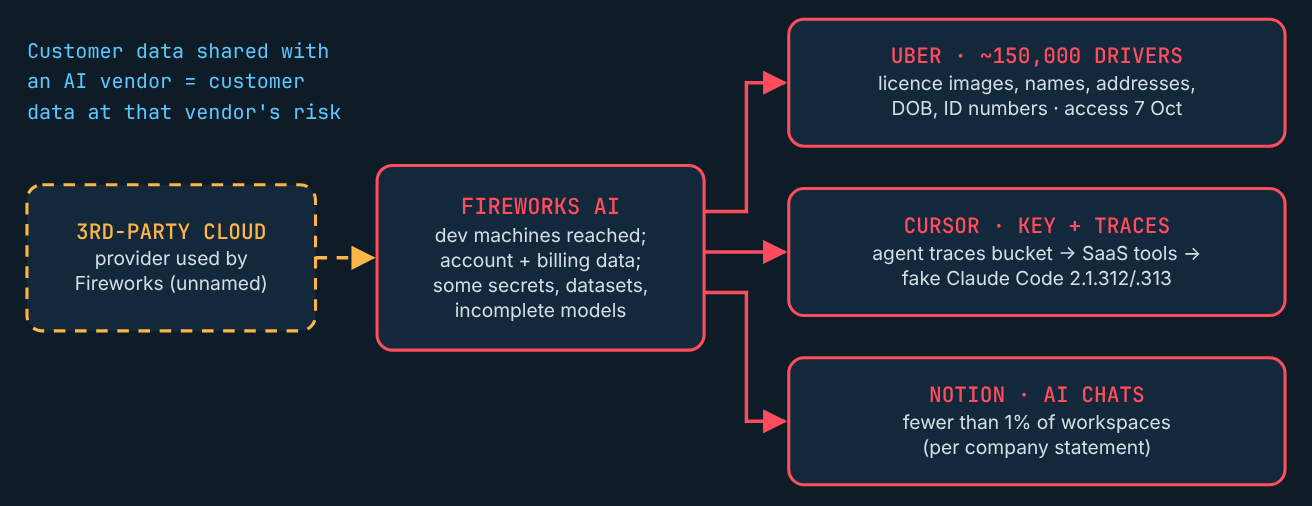
Fireworks runs and fine-tunes open-weight AI models for customers. Its first bulletin said it had found no evidence of access to customer models or datasets. Its 9 November update said attackers reached its development machines through a third-party cloud provider and affected account and billing information (not payment card numbers) and, for a limited set of accounts, secrets, datasets and incomplete model weights. [3][5]
Uber
- What happened: on 7 October, attackers used the service provider’s compromised credentials to access data Uber had shared with it. Uber learned of the incident on 9 October and confirmed the credential misuse on 13 October. [2]
- Who is affected: about 150,000 drivers; a Texas Attorney General filing reportedly lists 149,346. Riders are not mentioned. [2]
- Données: images of driver’s licences, names, addresses, dates of birth, driver’s licence numbers and other government ID numbers. [2]
- Notable detail: the data sat in an environment created and managed by Uber’s cloud security team. Alerts were enabled but did not fire, because the attacker used valid credentials. Uber says the compromised credentials gave no access to other Uber systems, and it is offering credit monitoring and fraud assistance. [2]
Curseur
- An attacker obtained an access key Cursor had issued to Fireworks, which Fireworks had exposed, and copied a read-only storage bucket of limited coding-agent traces, mostly from 2025, from sessions not in Privacy Mode. Some traces contained unredacted credentials; fewer than 0.01% of customers had API credentials exposed. [1]
- With those credentials the attacker reached SaaS tools and accessed archived non-production repositories, some support data and emails, usage metrics, agent conversation summaries and credentials users had sent to support. [1]
- On 29 October a stolen credential was used to place unauthorised copies of Anthropic’s Claude Code extension, versions 2.1.312 and 2.1.313, on the cache serving Cursor’s VS Code marketplace. At most 5,000 users requested them during about 11 hours before removal. Open VSX and Anthropic’s own extension were not affected. [1]
Notion
Notion has confirmed customer-related data exposure; Tech Times reports the company said fewer than 1% of workspaces may have lost unlabelled AI chats. [4]
Pourquoi c'est important
Companies send data to AI vendors for inference, fine-tuning and evaluation, often with less scrutiny than they apply to other processors. This incident shows the result: one vendor's breach becomes several customers' breach notifications, including identity documents. (Analyse MAG212)
How the attack worked
- Upstream entry: attackers reach Fireworks’ development machines via a third-party cloud provider (details not public). [5]
- Vol d'identifiants : keys and credentials that customers had given Fireworks are exposed. [1][3]
- Customer data access: those credentials are used against data customers shared with Fireworks (Uber) or against customer storage (Cursor).
- Onward movement: at Cursor, credentials found in traces lead into SaaS tools and the extension cache. [1]
Ce qu'il faut faire
- Utilisateurs du curseur : if you installed or updated Anthropic.claude-code 2.1.312 or 2.1.313 from Cursor’s marketplace on 29 October, follow Cursor’s 30 October security notice. Cursor warns that uninstalling the extension alone may not be enough. [1]
- Anyone notified by Cursor or Fireworks: rotate the keys listed in the notice. [1]
- Uber drivers: enrol in the monitoring offered, and watch for identity fraud using your licence details.
- All organisations: list the data you have shared with AI vendors and the credentials they hold for you; give each an owner, a scope and an expiry date.
Ce que les défenseurs doivent surveiller
- Use of credentials issued to AI vendors from unexpected networks or outside expected job windows.
- Bulk reads of storage buckets shared with vendors.
- Unexpected extension versions in developer environments.
Prévention et sensibilisation
- Équipes de sécurité : monitor shared data stores for access patterns, not just for alerts on unknown identities; valid credentials defeated Uber’s alerts.
- Procurement: require AI vendors to support short-lived credentials and to notify you quickly of incidents.
- Employés: never paste credentials into support tickets or AI tools.
Sujets connexes sur MAG212 CYBER
- MAG212 CYBER Daily, 17 November 2026: Keys that outlived the job (numéro complet et PDF)
- MAG212 CYBER Daily, 16 novembre 2026 : Les boîtes que personne ne répare
- MAG212 CYBER Hebdomadaire, 14 novembre 2026
- Abonnez-vous gratuitement à MAG212 CYBER
Sources
- [1] Cursor, “Security incident update“, 13 novembre 2026.
- [2] SecurityWeek, “Uber data breach impacts 150,000 people“, 16 novembre 2026.
- [3] PYMNTS (citing TechCrunch), “Hackers breach Fireworks AI and steal data from Uber, Notion and Cursor“, 16 novembre 2026.
- [4] Tech Times, “Uber data breach: hackers compromised AI vendor Fireworks“, 15 novembre 2026.
- [5] CybersecurityNews, “Hackers breach Fireworks AI through third-party cloud provider“, 10 Nov 2026.
- [7] MAG212 CYBER, “Cursor extension backdoor and the Fireworks AI vendor key (Weekly)“, 14 novembre 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 17 November 2026, 6:00 AM PT.