
Fortinet’s Ten Critical Advisories: Upgrade FortiMail, FortiManager and FortiOS, or Migrate Where No Fix Exists
Fortinet’s PSIRT index jumped from 324 to 370 advisories on 10 November, and ten of the new entries are rated critical. The worst give unauthenticated attackers code execution on FortiMail and on FortiManager and FortiAnalyzer through the FGFM management port. None is known to be exploited yet, every advisory says there is no workaround, and several older branches get no fix at all: the only remedy there is migrating to a supported release.
Ce qui s'est passé
[Confirmed] The FortiGuard PSIRT index grew from 324 to 370 advisories on 10 November. Every advisory page our researchers fetched says “Known Exploited: No” and offers no workaround, so upgrading is the only fix. (FortiGuard) (Fortinet RSS) [Reported] The fixes came from Fortinet’s AI-assisted testing programme; watchTowr’s Yordan Ganchev expects them to be “rapidly reverse-engineered, reproduced, and exploited” and advises restricting exposed management interfaces. (Cybernews)
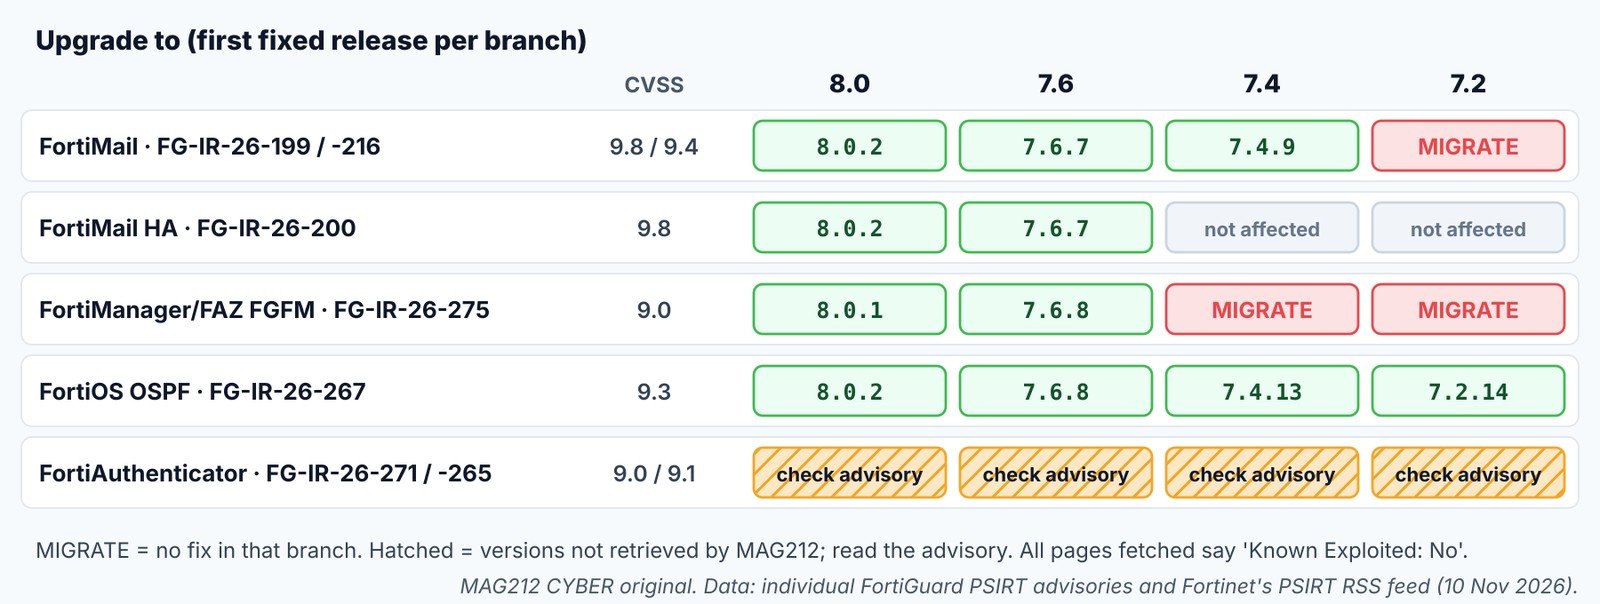
| Consultatif | Product · CVE | Flaw (Fortinet summary) | CVSS | Fixé |
|---|---|---|---|---|
| FG-IR-26-199 | FortiMail · CVE-2026-126147 | Unauth path traversal → code execution | 9.8 | 8.0.2 · 7.6.7 · 7.4.9 · 7.2 migrate · Cloud remediated |
| FG-IR-26-200 | FortiMail · CVE-2026-126148 | Unauth command injection via HA join-request packets | 9.8 | 8.0.2 · 7.6.7 · 7.4/7.2 not affected |
| FG-IR-26-216 | FortiMail · CVE-2026-126164 | Unauth SQL injection → code execution* | 9.4 | as -199; 7.2 migrate |
| -207 / -208 | FortiMail IBE | Unauth IBE session / recipient account takeover | 9.1 | not retrieved |
| FG-IR-26-275 | FortiManager & FortiAnalyzer FGFM · CVE-2026-126261 | Unauth code execution by anyone who can reach the FGFM port | 9.0 | 8.0.1 · 7.6.8 · 7.4/7.2 migrate |
| FG-IR-26-267 | FortiOS, FortiSASE OSPF · CVE-2026-126253 | OSPF auth bypass; adjacent attacker may broadcast LSAs; PoC exists (E:P) | 9.3 | 8.0.2 · 7.6.8 · 7.4.13 · 7.2.14; FortiSASE 26.3.2 (no action), 26.2–25.1 migrate |
| FG-IR-26-244 | FortiManager/FAZ (+Cloud) · CVE-2026-126229 | Authenticated admin reaches other VDOMs | 9.1 | not retrieved |
| FG-IR-26-271 | FortiAuthenticator | Hard-coded password; credential bypass “in certain circumstances” | 9.0 | check the advisory |
| FG-IR-26-265 | FortiAuthenticator | Incorrect authorization; authentication bypass | 9.1 | check the advisory |
*FG-IR-26-216’s Impact field says “Denial of service” while its summary describes code execution; treat it as the worse case. FortiAuthenticator advisories confirmed in Fortinet’s RSS feed; MAG212 has not retrieved their affected or fixed versions. Earlier social-post figures for FortiManager are superseded by FG-IR-26-275.
Contenir et remédier (dans l'ordre)
- [MAG212 analysis] Start with FortiManager/FortiAnalyzer reachable on FGFM from untrusted networks and internet-facing FortiMail: unauthenticated code execution, the class watchTowr expects to be weaponised.
- Schedule migrations now for FortiMail 7.2 and FortiManager/FortiAnalyzer 7.4/7.2, which have no in-branch fix. (FG-IR-26-199) (FG-IR-26-275)
- Upgrade FortiOS for the OSPF flaw. [MAG212 analysis] Meanwhile, OSPF authentication and passive interfaces on user segments reduce adjacency exposure (general hardening, not Fortinet guidance).
- Read FG-IR-26-271 and -265 for FortiAuthenticator versions and patch; it sits in front of VPN and admin MFA.
- Restrict all management interfaces to trusted networks. (Cybernews)
Look for and verify: [MAG212 analysis] no IOCs exist; watch FGFM and FortiMail HA traffic from unexpected sources and OSPF neighbour changes you didn’t make. Confirm firmware per device and, from outside, that FGFM and FortiMail admin/HA ports don’t answer.
Pourquoi c'est important
Fortinet management and mail products have a long history of rapid weaponisation once patches are public, and researchers expect these to be reverse-engineered quickly. FortiManager in particular controls the configuration of every FortiGate it manages, so one exposed FGFM port can become an estate-wide compromise.
The bottom line
Start with FortiManager and FortiAnalyzer reachable on FGFM and internet-facing FortiMail, schedule migrations for branches with no in-branch fix, upgrade FortiOS for the OSPF flaw, read the FortiAuthenticator advisories, and make sure no management interface answers from the internet.
How we label evidence: [Confirmed] comes from a primary source such as a vendor or CISA; [Reported] from a secondary outlet; [Claimed] from an attacker or an unverified party; [MAG212 analysis] is our judgement; [Unknown] means not established at press time. Commands and indicators are copied from the cited sources and were not tested by MAG212 CYBER.
This story is part of MAG212 CYBER Daily, 11 November 2026, with the day’s other verified stories, the Defender’s Action Desk and a full source register. Get the daily briefing free: subscribe to MAG212 CYBER. Par El Mostafa Ouchen.