
Infoblox Confirms Breach Through a SharePoint Migration Vendor: What NIOS Customers Should Do
De la part de MAG212 CYBER Daily, 17 November 2026. Chaque commande est copiée de la documentation officielle ou de l'analyse citée et a été non testé par MAG212; exécutez-le uniquement sur les systèmes que vous êtes autorisé à administrer.
Statut: Breach confirmed by Infoblox on 16 November 2026. Data types and the SharePoint path come from TechCrunch’s and The Register’s sources and an internal email The Register saw; Infoblox has not confirmed them or given counts. [1][2][3]
Ce qui s'est passé
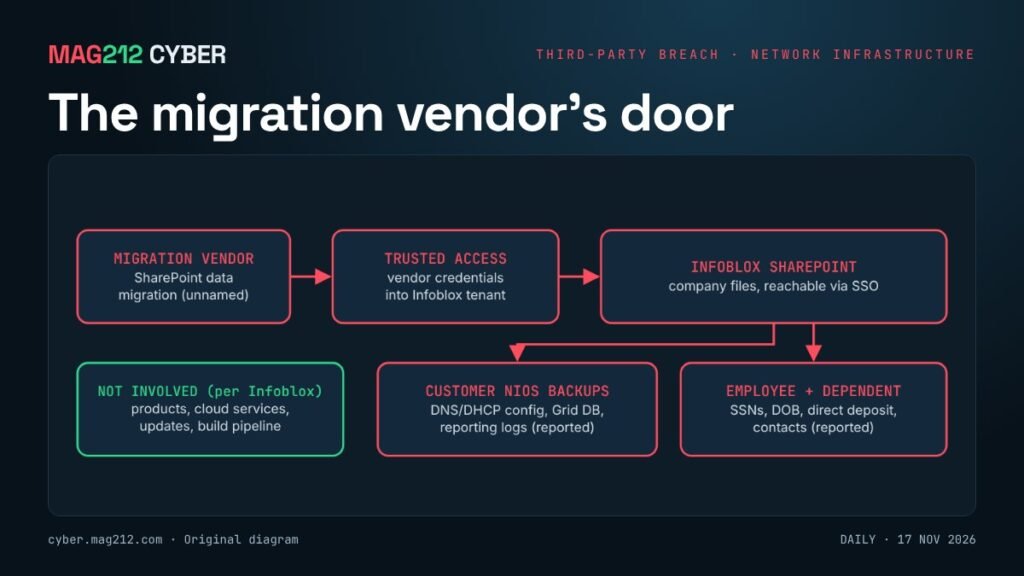
Infoblox said it is “investigating a security event involving unauthorized access to certain company information” through a compromised third-party data migration vendor. It activated incident response, took steps to contain the incident and engaged outside experts. [1]
According to a breach notification seen by two people who spoke to TechCrunch, the vendor provides SharePoint data migration services. One source said Infoblox has ended its work with the vendor; Infoblox did not comment. The vendor has not been named. [1]
Infoblox says it has no indication that any of its products, cloud services, software updates or build-and-release processes were involved. [1]
What was reportedly taken
- Customer data: The Register’s sources say the attackers used the vendor’s trusted access to take information from Infoblox’s Microsoft SharePoint system, including configuration snapshots for some customers’ NIOS deployments: saved copies of DNS and DHCP configuration, Grid databases and reporting logs that can be used to recover an appliance or Grid. [2][3]
- Employee data: an email from CEO Scott Harrell seen by The Register lists direct-deposit details, contact information, dates of birth and Social Security numbers of employees and their dependents. [2][3]
- Inconnu: the number of customers and employees affected, the intrusion date, the attacker and whether there has been an extortion demand. [1]
Qui est concerné ?
- Infoblox NIOS customers whose configuration snapshots were stored in the affected SharePoint environment. Infoblox says it has sent notifications. [3]
- Infoblox employees and their dependents.
Pourquoi c'est important
Infoblox runs DNS, DHCP and IP address management for many large organisations. A backup of that configuration is a blueprint of a network, so even without a product compromise, customers need to assess what an attacker could learn and reuse. (Analyse MAG212)
Comment fonctionne l'attaque
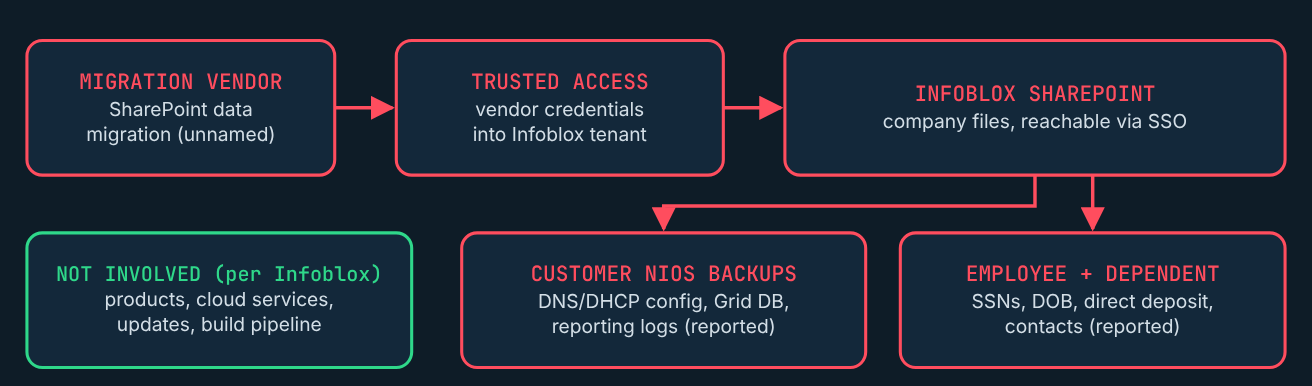
- Vendor compromise: a third-party SharePoint data migration vendor is compromised (how is not public).
- Trusted access: the attacker uses the vendor’s legitimate access into Infoblox’s Microsoft environment. TechCrunch notes Infoblox’s SharePoint server is reachable through its single sign-on provider. [1]
- Collection: files in SharePoint, including customer support artefacts and HR data, are taken. [2]
No exploit of Infoblox products is reported.
Why a NIOS backup matters (MAG212 analysis)
A Grid backup describes an organisation’s core network: DNS zones, subnets, DHCP scopes and server roles. Depending on how a Grid is configured, it may also contain secrets the Grid uses to integrate with other systems. Until Infoblox tells customers exactly which items were in scope, it is safest to plan as if a snapshot is in hostile hands.
What NIOS customers should do
- Check for an Infoblox notification and ask whether your Grid backups were in scope and from what date.
- If they were, rotate secrets stored in your Grid configuration: administrator and API accounts, TSIG and DNSSEC keys, and directory, RADIUS and SNMP integration credentials.
- Review Grid administrator audit logs for unfamiliar logins since the snapshot date.
- Brief help desks and network teams: expect targeted phishing that uses accurate internal hostnames and IP ranges.
Ce que les défenseurs doivent surveiller
- Logins to Grid Manager or the API from unfamiliar sources.
- DNS zone transfer requests from unexpected hosts.
- Phishing that references internal infrastructure names.
Comment vérifier la récupération
- Rotated credentials and keys are in use and old ones fail.
- No unexplained Grid administrative changes after the snapshot date.
Prévention et sensibilisation
- Administrateurs : migration vendors need broad but temporary access. Time-box it, scope it to the data being moved and revoke it on completion.
- Support teams: do not leave appliance backups or support bundles in collaboration sites longer than needed.
- Employés: watch for phishing that cites this breach and for signs of identity misuse.
Sujets connexes sur MAG212 CYBER
- MAG212 CYBER Daily, 17 November 2026: Keys that outlived the job (numéro complet et PDF)
- MAG212 CYBER Daily, 16 novembre 2026 : Les boîtes que personne ne répare
- MAG212 CYBER Hebdomadaire, 14 novembre 2026
- Abonnez-vous gratuitement à MAG212 CYBER
Sources
- [1] TechCrunch, “Cyber giant Infoblox confirms security incident after hackers access company information“, 16 novembre 2026.
- [2] SC Media (citing The Register), “Infoblox investigates data breach involving third-party vendor“, 16 novembre 2026.
- [3] The Register (via SecOpsNews), “Infoblox customer and staff data exposed in SharePoint breach“, 16 novembre 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 17 November 2026, 6:00 AM PT.