
La chaîne du froid est désormais une cible : OpenSSH exploité, WordPress KEV Deadline et Zyxel : MAG212 CYBER Daily, 6 novembre 2026
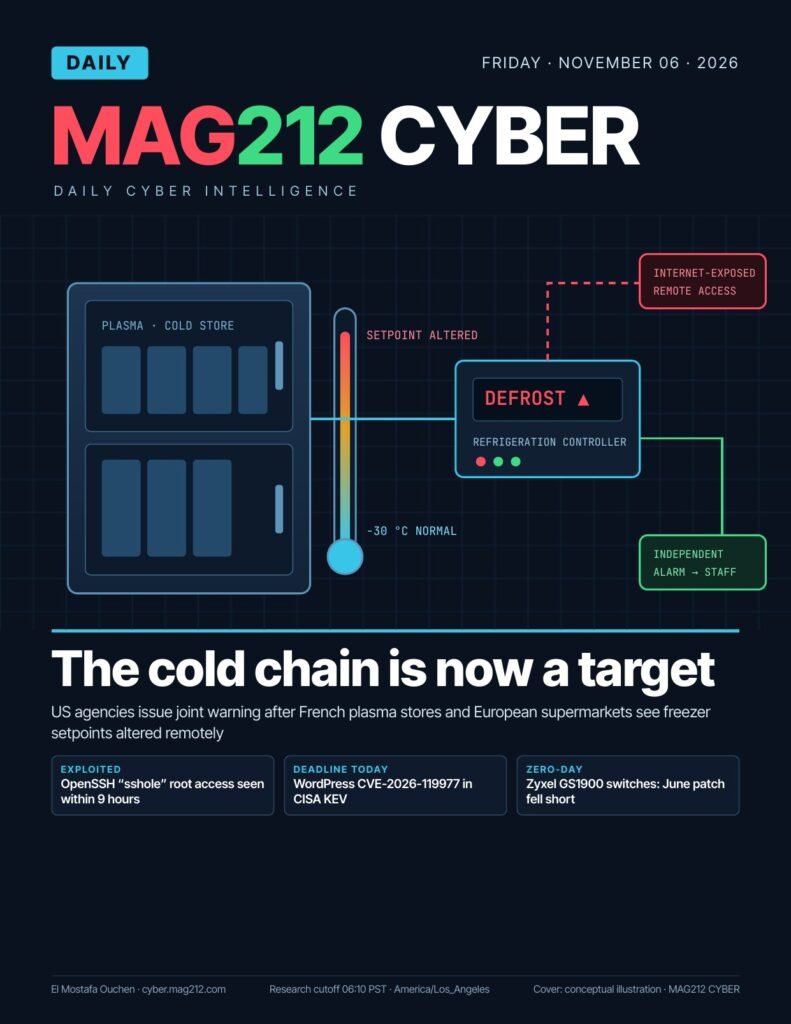
Today’s lead is the cold chain. After weeks of remotely triggered defrost cycles in European supermarkets and an attempt on three French plasma stores, five US agencies told operators on November 5 to harden refrigeration and cold-chain monitoring systems. Around it, two flaws moved from “patched” to “exploited”: OpenSSH’s password bypass on Alpine and other musl systems was used to gain root on a research honeypot, with the first attempt less than nine hours after disclosure, and today is the federal deadline for the WordPress core flaw CISA added to its exploited list. Every story was checked against vendor, government and original research sources.
Qu'est-ce qui requiert notre attention aujourd'hui ?
| Histoire | Statut | Faites ceci |
|---|---|---|
| Refrigeration & cold chain | US joint warning Nov 5 (CISA, FBI, HHS, USDA, DOT); EU warning Nov 4; EFS plasma sites hit Nov 2 | Take controllers off the internet, isolate them on their own VLAN, alert on setpoints outside safe ranges |
| OpenSSH “sshole” (CVE-2026-123158) | Root on an Alpine honeypot reported by Previdian; first attempt within 9 hours of disclosure | Install your Alpine branch’s fixed openssh and restart sshd, or set PasswordAuthentication no now |
| WordPress core (CVE-2026-119977) | In CISA KEV since Nov 3; federal deadline today | Confirm 7.1.4 or your branch’s back-port; run wp core verify-checksums |
| Zyxel GS1900 (CVE-2026-107441) | Zero-day per Binarly; ThaiCERT alert Nov 6 | Install Patch 3 firmware; restrict web management to an admin VLAN |
| Apache OFBiz 24.09.08 | 46 CVEs, several unauthenticated RCE; no exploitation reported | Upgrade, then rotate secrets (hard-coded JWT key fixed) |
| DreamHost File Manager | Credentials exposed for logins ~Aug to Oct 23 | Customers: check mail rules, FTP users and site files |
Corrigé depuis le premier rapport
- OpenSSH: early reports said exploitation was not established. Previdian has since reported successful root access on an Alpine honeypot (8 attempts, one source IP). No production compromises are reported.
- OpenAI kernel research: the figures are 1,169 working local privilege-escalation exploits and 948 separate patches, as reported by SecurityWeek, not 948 “unique” vulnerabilities.
- KELA bank phishing: the campaign impersonates 189 US financial institutions, 183 of them live on October 25.
Mises à jour sur les articles précédents
- Cold chain (3 November): new US and EU government warnings, and EFS confirmed its plasma was saved.
- WordPress core (4 November): the CISA deadline for federal agencies is today; fixed versions for every branch from 4.7 to 7.1 are in the edition.
- Zyxel GS1900 (5 November): ThaiCERT issued an alert on November 6; Zyxel still does not confirm exploitation of the new CVE.
Lisez chaque histoire en entier
- Cold Chain Under Attack: What the US and EU Warnings Say and How to Harden Refrigeration Controllers
- OpenSSH “sshole” (CVE-2026-123158): How the musl Password Bypass Works and Every Alpine Fix
- WordPress CVE-2026-119977: The Upgrade Race in CISA KEV, With Fixed Versions for Every Branch
- Zyxel GS1900 CVE-2026-107441: The June Patch That Didn’t Hold
- Apache OFBiz 24.09.08 Fixes 46 CVEs: What to Patch and Rotate
- DreamHost File Manager Breach: What Was Exposed and What Customers Should Check
- The Bank Phishing Kit That Fakes Its Own Takedown: 189 US Banks Impersonated
- ChatGPT Lockdown Mode Bypass: How the HTML Preview Sandbox Was Escaped
- OpenAI’s Kernel Research: What 1,169 AI-Built Root Exploits Mean for Linux Admins
Feuilletez l'édition
Sources include Defense One / Nextgov on the US joint warning, Euronews on EFS, Alpine Linux, OpenSSH, WordPress.org, ThaiCERT, Apache OFBiz, DreamHost et KELA; the full 29-source register is on page 16. Research cutoff 06:10 PST, 6 November 2026. Diagrams and the cover are original MAG212 CYBER illustrations. Command panels were checked against documentation but not executed; run them only on systems you are authorized to manage.