
France Blames Iran’s IRGC for Heating Supermarket Fridges: Refrigeration Controllers Become a State Target
France has formally blamed Iran’s Revolutionary Guard for the October cyberattack that switched supermarket refrigerators to heating across hundreds of stores. Paris prosecutors named the IRGC, and France’s national cyber agency ANSSI attributed the operation to the Shahid Kaveh group, which it describes as an IRGC-affiliated cyber unit, according to an AP report published by SecurityWeek on 10 November (SecurityWeek/AP). The attribution turns a facilities problem into a nation-state operational-technology issue for every retailer, cold-chain operator and building manager with controllers on the internet.
| Attribution | France (prosecutors and ANSSI): IRGC-linked Shahid Kaveh group |
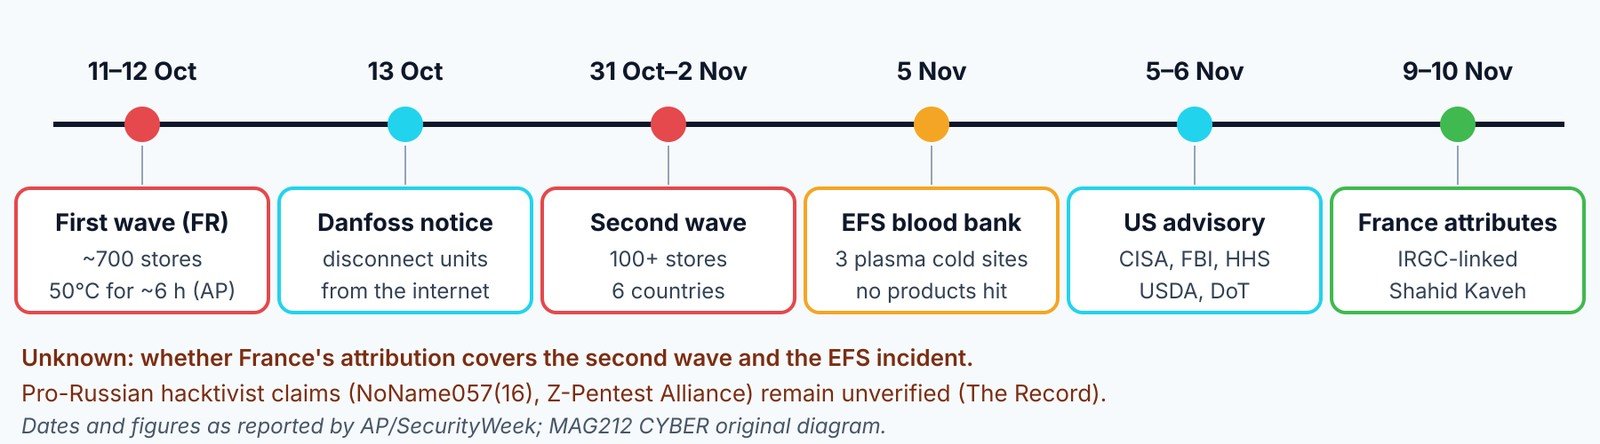
| Attaque | Overnight 11–12 October 2026; about 700 of France’s roughly 10,000 supermarkets affected (reported) |
| Impact | Fridges reached about 50°C for around six hours; Intermarché reported losses of tens of millions of euros (reported) |
| Devices named | Danfoss AK-SM/AK-SC and Copeland/Dixell XWEB (CERT-FR, as reported) |
| Still exposed | 3,124 controllers (47%) reachable on 5 November, per Censys |
| Legal action | Judicial investigation opened; arrest warrants sought, not yet issued; EU sanctions promised, not yet enacted |
Ce qui s'est passé
Prosecutor Laure Beccuau opened a judicial investigation into organised cybercrime carried out on behalf of a foreign power, targeting the group’s leader and two deputies. The evidence cited includes the use of Farsi and IP addresses linked to devices in Iran. International arrest warrants are being sought but had not been issued. Foreign minister Jean-Noël Barrot summoned Iran’s ambassador, called it “an attack of unprecedented scale and aggressiveness” and said France would seek sanctions at the European level (SecurityWeek/AP). Iran’s response had not been reported at press time.
The reported impact is unusually physical: attackers took control of refrigeration in hundreds of stores, temperatures reached about 50°C for roughly six hours, and around 700 supermarkets were affected. The AP account dates the attack to 12 October; earlier reporting places it overnight on 11–12 October (SecurityWeek, 3 Nov).
Competing claims, and what is still open
France’s attribution is official. Earlier, pro-Russian hacktivist groups NoName057(16) and Z-Pentest Alliance reportedly claimed to have hacked Danfoss (SecurityWeek, 6 Nov), claims The Record describes as unverified (Le Record). It is also not confirmed whether the attribution covers the second wave, overnight from 31 October to 2 November, which hit more than 100 stores in Belgium, Estonia, Ireland, Luxembourg, the Netherlands and Sweden (Semaine de la sécurité), or the incident at the French Blood Establishment (EFS), where attackers reached three plasma cold-storage sites through refrigeration supplier Coolworld and EFS says no blood products or samples were compromised (SecurityWeek/AP).
Qui est concerné ?
Five US agencies, CISA, the FBI, HHS, USDA and the Department of Transportation, say they are aware of malicious actors targeting electronic temperature controllers and commercial refrigeration controllers in retail grocery and cold-storage facilities (Semaine de la sécurité; advisory: IC3 joint advisory, which we could not retrieve directly). CERT-FR first flagged Danfoss AK-SM and AK-SC controllers, then added Copeland/Dixell XWEB. Danfoss said most of the hacked units were legacy products it no longer updated, and told customers on 13 October to disconnect them from the internet (Semaine de la sécurité).
Exposure is falling but far from gone. Censys counted 6,695 exposed controllers on 9 October and 3,124, or 47%, still reachable on 5 November. Copeland/Dixell XWEB exposure fell from 3,708 to 2,420 and Danfoss StoreView from 3,004 to 708 (Censys). These figures come from Censys, not from the government advisory.
Comment fonctionne l'attaque
As reported from the US advisory, attackers exploit unpatched or internet-accessible controllers through authentication bypass, code injection and weak configurations. They then change settings remotely to force continuous heating and defrost cycles, and cause “denial of view”, so operators cannot see the real state of the system (Semaine de la sécurité). No indicators of compromise were available to us because the advisory PDF could not be retrieved.
Que rechercher
- Setpoint or defrost-schedule changes nobody on your team made.
- Controller dashboards that freeze, go blank or show values that don’t match the store floor.
- Any controller or building-management interface reachable from the internet, tested from outside your network.
Contain and harden
The agencies’ recommended mitigations, as reported (Semaine de la sécurité):
- Remove control systems from the internet, or put them behind a firewall or edge device.
- Isolate OT networks from IT and guest networks.
- Restrict access to trusted identities using strong passwords and phishing-resistant MFA.
- Patch, or replace legacy controllers the vendor no longer supports.
- Keep offsite backups of controller configurations.
- Turn on logging and monitoring.
How to confirm you’re clean
- An external scan confirms controller interfaces are no longer reachable from the internet.
- Setpoints and defrost schedules match known-good values, compared against your offsite configuration backup.
- Remote access for maintenance contractors goes through a controlled, logged path.
Leçons pour les administrateurs, le personnel et les dirigeants
- MSPs and facilities teams: treat any internet-reachable building controller serving retail, food, pharmacy or healthcare clients as an incident waiting to happen.
- Store and site staff: report unexplained temperature alarms or dashboard outages to IT as a possible security event, not just a maintenance call.
- Dirigeants : the same pattern is appearing in other OT tools. A related example is the CVSS 10 Node-RED flaw (CVE-2026-58115, including Siemens SIMATIC IoT2050), which VulnCheck has seen exploited since 30 October against instances without admin authentication (Semaine de la sécurité).
Ce que nous ignorons encore
- Whether France’s attribution also covers the second wave and the EFS incident.
- The advisory’s technical indicators, pending retrieval of the IC3 document.
- Iran’s response, and whether EU sanctions and arrest warrants follow.
Sujets connexes sur MAG212 CYBER
Sources
- SecurityWeek/AP: France blames Iran for refrigerator cyberattack (10 Nov 2026)
- SecurityWeek: US agencies urge hardening of refrigeration controllers (6 Nov 2026)
- IC3 joint cybersecurity advisory 261105 (not retrieved)
- Censys: European refrigeration controller exposure
- SecurityWeek: Over 100 European stores hit as fridge attacks resume (3 Nov 2026)
- SecurityWeek/AP: French blood bank site hit (5 Nov 2026)
- The Record: pro-Russian hackers target European officials (9 Nov 2026)
- SecurityWeek: Critical Node-RED flaw exploited (3 Nov 2026)