
Puppet Server RCE (CVE-2026-115731) Is Now Exploited: How the Report Deserialization Flaw Works and How to Fix It
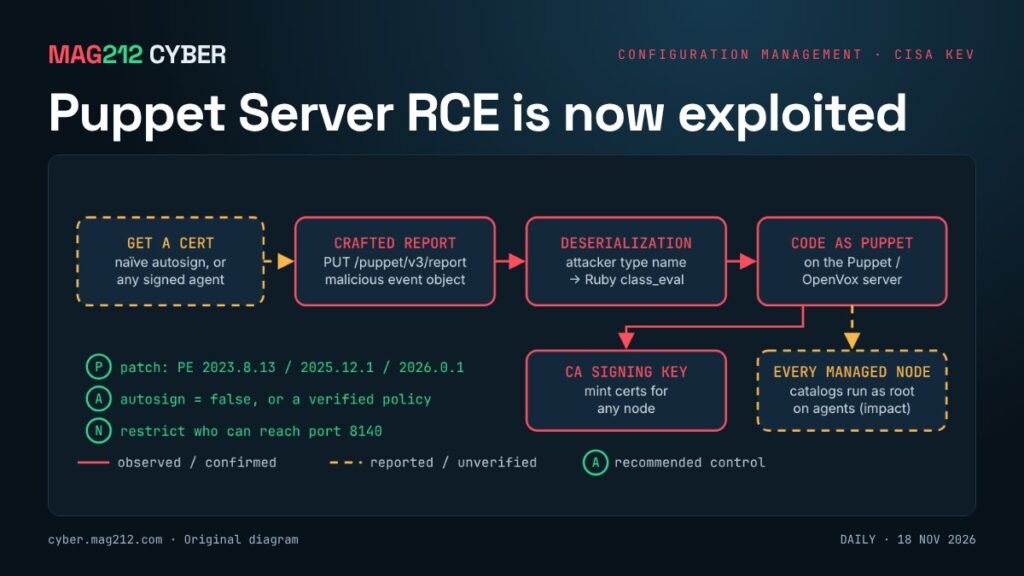
De la part de MAG212 CYBER Quotidien, 18 novembre 2026. Chaque commande est copiée de la documentation officielle ou de l'analyse citée et a été non testé par MAG212; exécutez-le uniquement sur les systèmes que vous êtes autorisé à administrer.
Statut: Actively exploited per CISA, which added CVE-2026-115731 to its Known Exploited Vulnerabilities catalog on 17 November 2026 with a remediation deadline of 1 December for US federal agencies. CISA lists ransomware use as unknown. Perforce, Vox Pupuli and researchers at Neodyme disclosed the flaw with fixes on 3 November; a working proof-of-concept is included in the OpenVox advisory. Severity: CVSS 4.0 score 9.4. [1][2][4][5]
Ce qui s'est passé
CVE-2026-115731 is a deserialization flaw in the report-processing code of Puppet Server, used by Puppet Enterprise, Puppet Core and the open-source fork OpenVox. Perforce describes it as allowing a client that holds any CA-signed agent certificate to execute arbitrary code on the Puppet Server with the permissions of its service account. SecurityWeek reports the flaw was flagged as exploited on 4 November, before CISA’s listing. [2][5]
Qui est concerné ?
| Produit | Fixé dans |
|---|---|
| Puppet Enterprise | 2023.8.13, 2025.12.1, 2026.0.1 |
| Puppet Core | 9.1.3, 8.22.2 |
| OpenVox Server and OpenVoxDB | 9.2.0 or 8.18.0 |
| OpenVox Agent | 9.3.0 or 8.32.0 |
| Open Source Puppet | no further updates; migrate |
Fixed versions as reported by SecurityOnline and SecurityWeek from the vendor and OpenVox advisories. Check the Perforce advisory before upgrading. [2][4][5]
Pourquoi c'est important
A Puppet server decides what runs on every machine it manages. Code execution on it exposes the certificate authority's signing key, which means an attacker can impersonate any node and, through the configurations it serves, potentially reach the whole fleet. A public exploit has existed since disclosure, so exploitation was a matter of time. (Analyse MAG212)
Comment fonctionne l'attaque
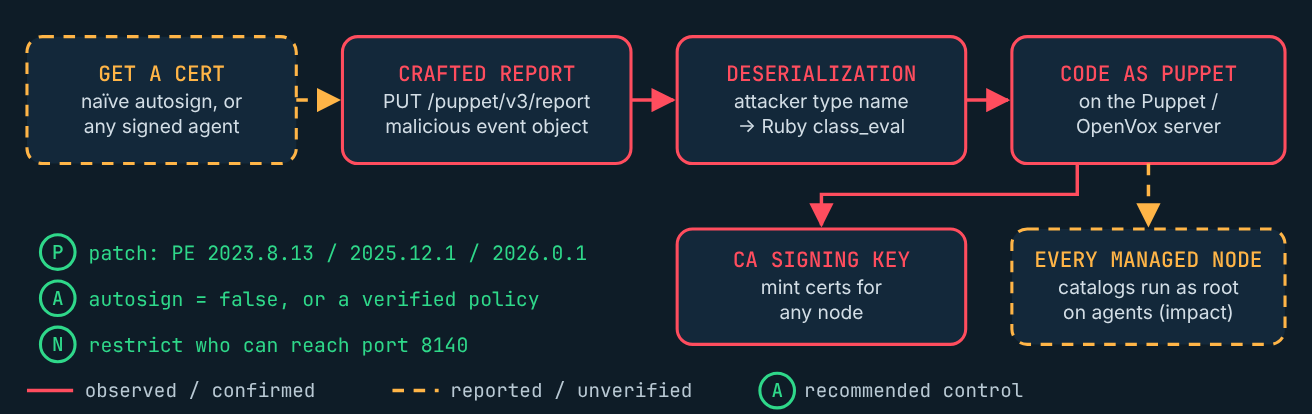
- A certificate: the attacker needs a CA-signed agent certificate. Any enrolled node has one. If the CA uses naïve autosigning, an outsider can simply request one, which turns this into an effectively unauthenticated attack chain. [4][6]
- A crafted report: after each run, agents send a JSON report to the server. An event inside that report can carry a serialized Ruby object. [4]
- Deserialization: the server trusts an attacker-supplied type name, which eventually reaches a Ruby
class_evalcall, so a malicious event object runs code on the server. [4] - Impact: code runs as the Puppet service user. That gives access to the CA signing key, which Red Hat notes enables further compromise of managed systems. [3][4]
A companion flaw, CVE-2026-115732 (CVSS 9.0), was fixed in the same releases. The trapperkeeper-authorization library treated plain hostname rules like wildcards, so a certificate for a subdomain could impersonate its parent host; Perforce says this can lead to remote command execution on managed nodes in Puppet Enterprise. One outlet reports it is also being exploited; MAG212 could not confirm that. [4]
Ce que les défenseurs doivent surveiller
- Certificates you do not recognise in the CA’s signed or pending list.
- Report submissions (
PUT /puppet/v3/report) from unexpected hosts or at unusual times. [3] - New processes, files or outbound connections started by the Puppet service user on the server.
- Changes to the CA directory or unexpected access to the CA private key.
Comment enquêter
These commands are lecture seule, run on the Puppet CA server, and come from Puppet’s documentation and the puppetserver-ca manual. Non testé par MAG212. [6][7]
puppet config print autosign --section server
puppetserver ca list --all
The first shows how the CA decides to sign requests: true means it signs every request (naïve autosigning); a file path means an allowlist file or a policy executable. The second lists signed and pending certificates so you can spot nodes you do not recognise.
Comment contenir et remédier
- Correctif to a fixed version from the table above. Patching is the only full fix. [4]
- Until you can patch, restrict network access to the Puppet server to the networks that need it, and restrict access to the report endpoint. [3][4]
- Disable or tighten autosigning: set
autosign = falsein the[server]section of the CA’s puppet.conf, or use a verified policy executable. [6] - After upgrading, review custom auth.conf rules. [4]
- If compromise is suspected, treat the CA as exposed: preserve evidence, then plan to regenerate the CA and re-issue agent certificates, and review the code and data the server distributed during the exposure.
Comment vérifier la récupération
- The server reports a fixed version after restart.
puppet config print autosign --section serverno longer returnstrue.- The certificate list contains only nodes you expect.
Prévention et sensibilisation
- For administrators: configuration-management servers are tier-zero systems. Keep them off general networks and patch them on the same timeline as domain controllers.
- For decision-makers: Open Source Puppet receives no further updates; budget a migration to a supported line or to OpenVox.
- For security teams: alert on new certificate signings and on new processes spawned by the Puppet service account.
Sujets connexes sur MAG212 CYBER
- MAG212 CYBER Quotidien, 18 novembre 2026 : Un signe égal de trop (numéro complet et PDF)
- MAG212 CYBER Daily, 17 novembre 2026 : Des clés qui ont survécu à l’emploi
- MAG212 CYBER Daily, 16 novembre 2026 : Les boîtes que personne ne répare
- MAG212 CYBER Hebdomadaire, 14 novembre 2026
- Abonnez-vous gratuitement à MAG212 CYBER
Sources
- [1] CISA, “CISA adds one known exploited vulnerability to catalog“, 17 novembre 2026.
- [2] Perforce, “CVE-2026-115731: report deserialization code execution“, 3 Nov 2026.
- [3] Red Hat, “CVE-2026-115731 description and mitigation“, novembre 2026.
- [4] SecurityOnline, “Puppet Server RCE CVE-2026-115731: public PoC“, novembre 2026.
- [5] SecurityWeek, “Critical Perforce Puppet RCE exploited in attacks“, 17 novembre 2026.
- [6] Puppet documentation, “Autosigning certificate requests“, Docs 2026.
- [7] Ubuntu manpages, “puppetserver-ca(1): Puppet Server CA management command“, Docs 2026.
Rédigé et édité par El Mostafa Ouchen pour MAG212 CYBER. Informations vérifiées auprès des sources ci-dessus le 18 novembre 2026 à 6h00 (heure du Pacifique).