
CISA KEV Deadlines on 23 and 24 November 2026: Eight Exploited Flaws to Close, and Why Vendor Advisories Under-Rate Them
De la part de MAG212 CYBER Daily, 22 November 2026. This article was written with AI assistance and edited by El Mostafa Ouchen. Commands, where included, were non testé par MAG212; run them only on systems you are authorised to administer.
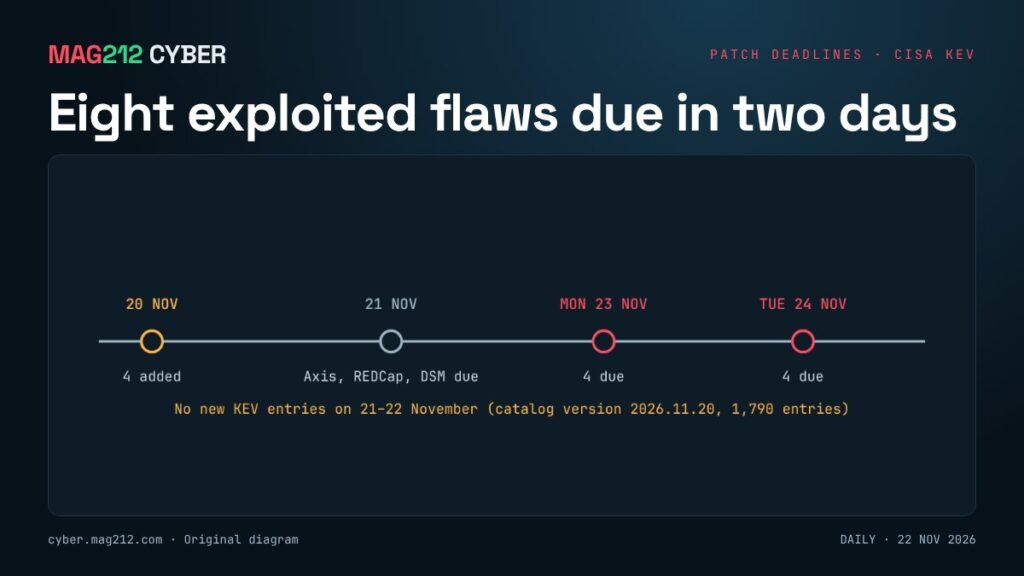
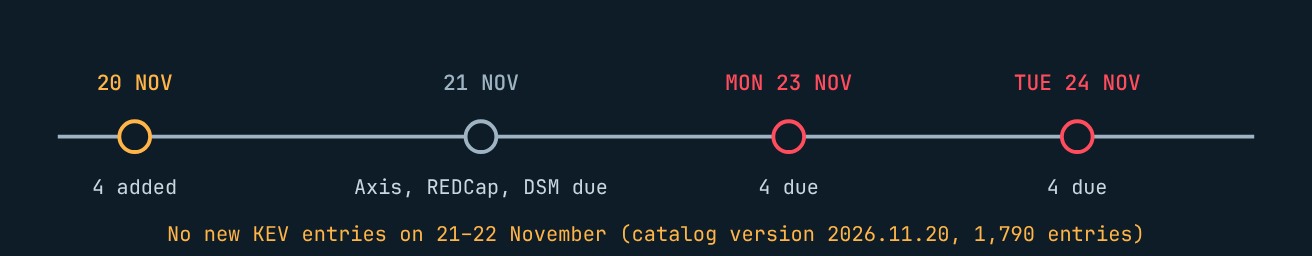
Statut: Exploité, per CISA. No new KEV entries on 21 or 22 November; catalog version 2026.11.20 has 1,790 entries. [1]
Due Monday 23 November
All four were added on 20 November and cite Binding Operational Directive 26-04. [1]
- CVE-2026-123890, VMware vCenter: authentication bypass in the VMware Directory Service.
- CVE-2026-76466, Cisco Expressway: hard-coded credentials giving root on clustered devices.
- CVE-2026-129448, Apache Roller: XML-RPC deserialization. CISA notes it is the same bug as CVE-2026-82384 but covers a broader range of versions, so recheck what you patched earlier.
- CVE-2025-42884, SAP NetWeaver Enterprise Portal: JNDI injection.
Pourquoi c'est important
KEV deadlines bind US federal agencies, but they are also the best free list of what attackers are using right now. Several items due this week sit at the edge of a network or control a whole virtualisation estate. When a vendor's own advisory does not mention exploitation, teams that prioritise by vendor wording alone will push these down the queue. (Analyse MAG212)
Due Tuesday 24 November
All four were added on 10 November. [1]
- CVE-2026-124194: Microsoft Outlook.
- CVE-2026-125350: Chromium.
- CVE-2026-20320: Cisco BroadWorks, XML external entity.
- CVE-2026-111793: Openwave Webtop Media Transcoder.
Why vendor pages are not enough
As of 22 November, Broadcom’s VMSA-2026-0009.1 for vCenter lists no workaround and does not acknowledge exploitation, and Cisco’s Expressway advisory is still at version 1.0 and says Cisco is “not aware” of malicious use, although CISA lists both as exploited. [2][3][1]
KEV entries tell agencies to apply vendor mitigations, follow CISA’s forensics triage guidance, or stop using the product if no mitigation exists. [1]
Pull the list yourself
Read-only; requires curl and jq. Not tested by MAG212.
KEV=https://raw.githubusercontent.com/cisagov/kev-data/develop/known_exploited_vulnerabilities.json
curl -s "$KEV" | jq -r '.vulnerabilities[] | select(.dueDate=="2026-11-23" or .dueDate=="2026-11-24") | [.cveID,.product] | @tsv'
Compare the output with your scanner’s open findings.
What to do this week
- vCenter: apply Broadcom’s fixed builds (9.1.1.0200, 9.0.2.0200, 8.0 U3m, VCF 5.2.5) and keep TCP 2012 reachable only from other vCenter nodes. [2]
- Cisco Expressway: upgrade to X15.5.20; X14 and earlier must migrate. [3]
- Apache Roller and SAP NetWeaver Portal: patch, or take them off the internet until you can.
- Outlook and Chromium-based browsers: confirm managed updates have landed on every endpoint.
- Vérifier: re-scan and close the tickets only when the scanner shows none of the eight open.
Sujets connexes sur MAG212 CYBER
- MAG212 CYBER Daily, 22 November 2026: Can police trust the record? (numéro complet et PDF)
- MAG212 CYBER Weekly, 21 November 2026: Machine Speed
- MAG212 CYBER Daily, 20 novembre 2026 : Les clés de vSphere
- Abonnez-vous gratuitement à MAG212 CYBER
Sources
- [1] CISA, “Known Exploited Vulnerabilities catalog, version 2026.11.20 (JSON)“, 20 novembre 2026.
- [2] Broadcom, “VMSA-2026-0009.1: VMware vCenter Server and Cloud Foundation updates“, 19-20 novembre 2026.
- [3] Cisco, “Cisco Expressway Series static credential vulnerability (cisco-sa-vcs-static-cred-hr7EWZ8t)“, 21 Oct 2026, v1.0.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 22 November 2026, 7:00 AM PT.