
The Keys to vSphere: MAG212 CYBER Daily, November 20, 2026
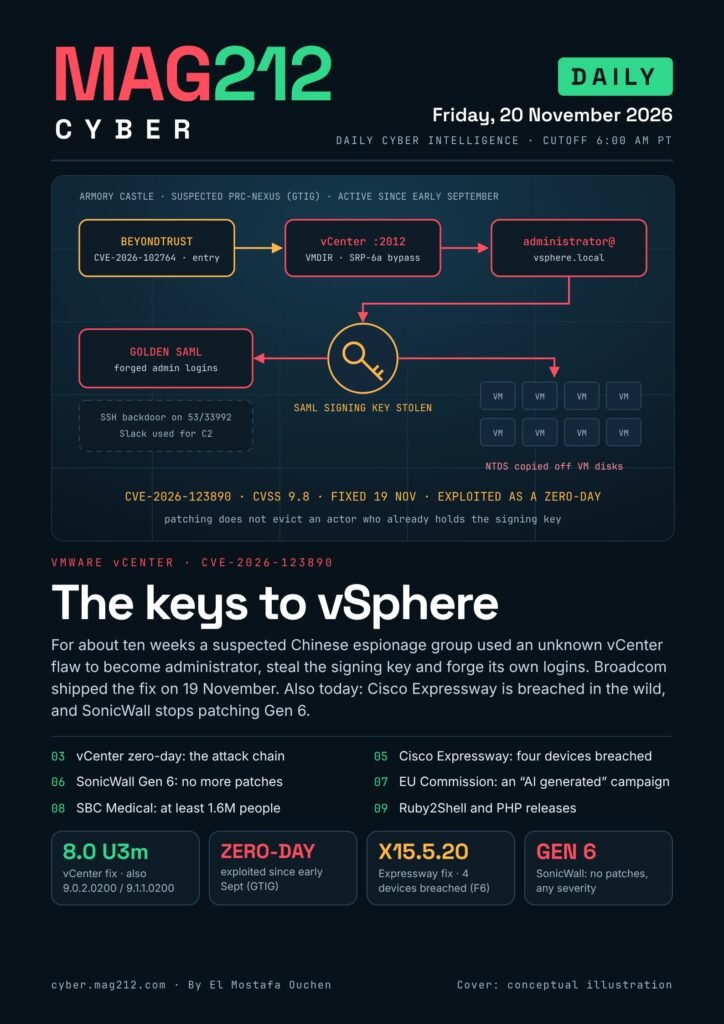
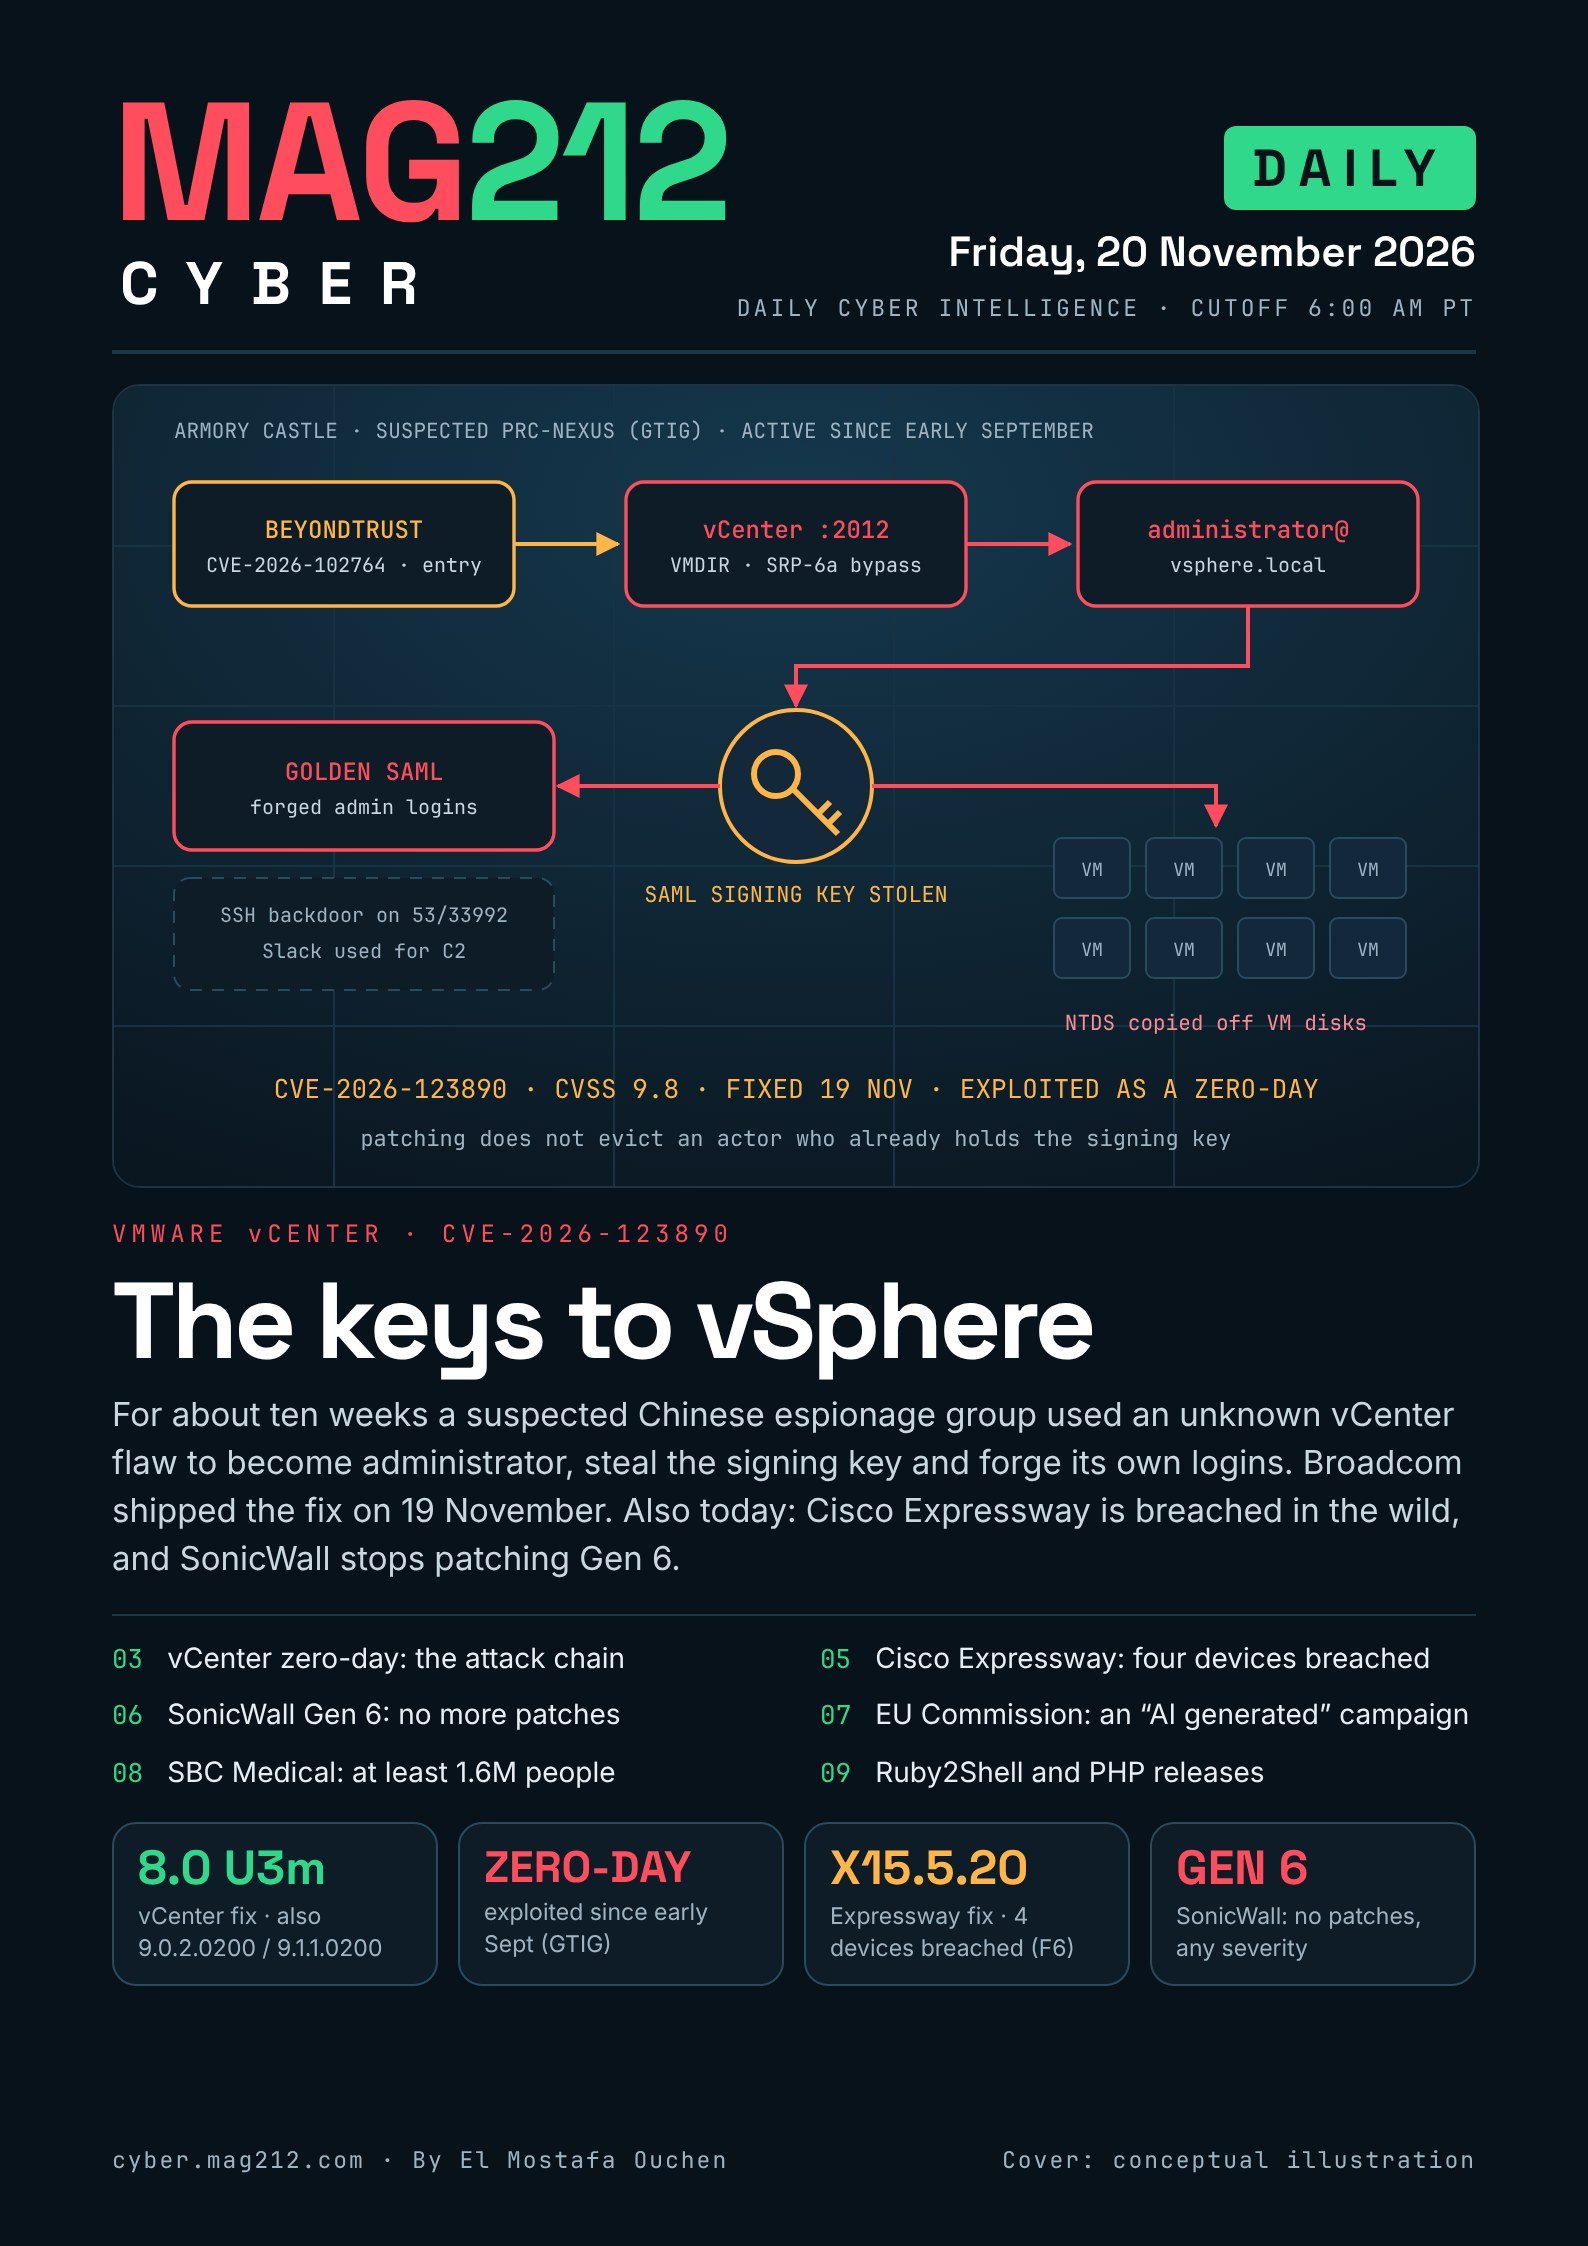
MAG212 CYBER · Daily Cyber Intelligence · Friday, November 20, 2026. A suspected China-nexus espionage group, ARMORY CASTLE, exploited a vCenter authentication bypass (CVE-2026-123890) as a zero-day from early September to forge admin logins and copy Active Directory secrets; Broadcom fixed it on 19 November. Attackers also breached four clustered Cisco Expressway devices through a hard-coded credential, SonicWall stopped patching Gen 6 firewalls, the European Commission confirmed an “AI generated” cyber campaign, and SBC Medical disclosed a breach affecting at least 1.6 million people. Plus: Ruby2Shell and PHP fixes.
Les trois actions prioritaires
- Patch vCenter to 8.0 U3m, 9.0.2.0200 or 9.1.1.0200, then hunt. Block TCP 2012 from everything except other vCenter nodes. Look for sps-*@vsphere.local accounts and GTIG's file paths; if found, rotate the STS signing certificate.
- Upgrade clustered Cisco Expressway to X15.5.20; migrate off X14. Allow TCP 4372 only between cluster peers and search logs for wombat@127.0.0.1.
- List every SonicWall Gen 6 and plan its replacement. Until then: no WAN management, SSL VPN off or restricted, MFA on, passwords reset.
Dans ce numéro
- VMware vCenter Zero-Day CVE-2026-123890: How ARMORY CASTLE Stole the Keys to vSphere, and How to Patch and Hunt (p. 3–4)
- Cisco Expressway CVE-2026-76466 Exploited: A Hard-Coded Cluster Credential, Four Breached Devices, and How to Fix It (p. 5)
- SonicWall Gen 6 Firewalls Get No More Patches: End-of-Support Dates, Risks, and What to Do Until You Replace Them (p. 6)
- European Commission Confirms an "AI Generated" Cyber Campaign: What Is Confirmed, What Is Only Reported (p. 7)
- SBC Medical Group Data Breach: At Least 1.6 Million People Exposed, What Was Taken and What to Do (p. 8)
- Ruby2Shell (CVE-2026-132825) and the November PHP Security Release: What to Update and Why "bundle update" Is Not Enough (p. 9)
- Cyber Briefs, 20 November 2026: CISA KEV Adds Four Exploited Flaws, N-able Cloud Breach, JPMorgan and Visa Vendor Leak (p. 10)
Also in the PDF: the Defender’s Action Desk (p. 11), an awareness lesson, “The devices nobody patches” (p. 12), and 43 linked sources (p. 13).
Feuilletez l'édition
Comment nous avons vérifié ce problème : stories were checked against primary sources where reachable (Broadcom’s VMSA and FAQ, GTIG/Mandiant, Cisco, SonicWall, SBC’s SEC filings, ruby-lang.org, php.net), with a research cutoff of 6:00 AM PT on 20 November. F6’s Expressway report, Politico’s Commission story and CISA’s site did not load; those details rely on The Hacker News, Ostorlab, SecurityWeek and Help Net Security and say so. Every command is marked non testé par MAG212.
Numéros précédents
- Un signe égal de trop, le quotidien du 18 novembre.
- A ten-year-old counter, the 19 November daily.
- Tous les numéros du magazine MAG212 CYBER