
Maileva Breach: 22 Million People Who Never Chose the Vendor
From the MAG212 CYBER Daily, 15 November 2026. Every command is copied from official documentation or the cited analysis and was not tested by MAG212; run it only on systems you are authorised to administer.
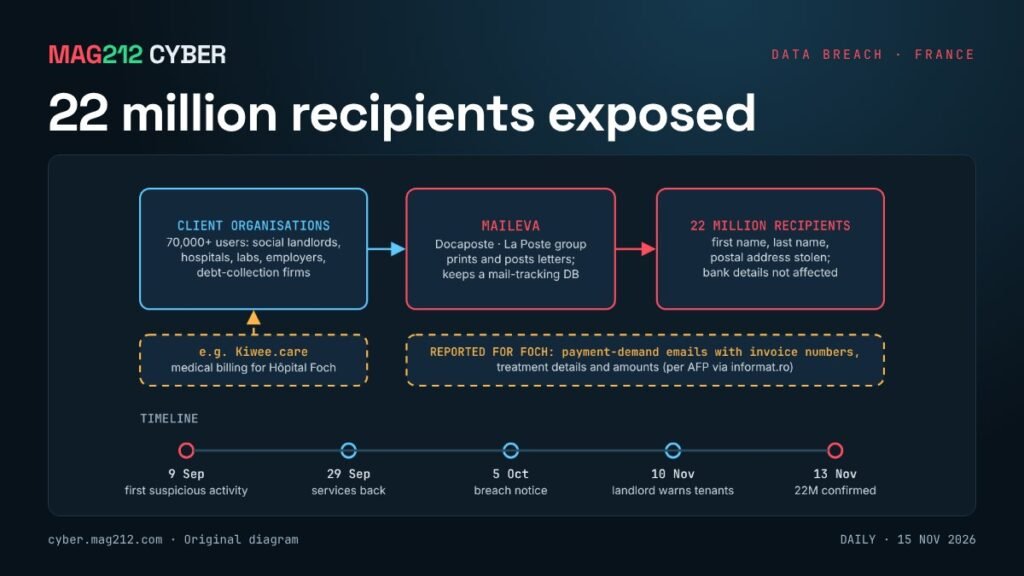
Status: Confirmed. La Poste told AFP that the first names, last names and postal addresses of 22 million people were stolen in a mid-September attack on its subsidiary Maileva. Bank details were not compromised. Maileva notified France’s data protection authority (CNIL), filed a criminal complaint and informed all affected client companies. [1][3]
Ce qui s'est passé
Maileva, part of La Poste’s Docaposte division, prints and posts documents such as payslips, registered letters, invoices and meeting notices on behalf of more than 70,000 business users. [1][3]
A Docaposte data-breach notice dated 5 October says an attacker reached a mail-tracking database covering about 22 million people, with data kept for up to ten years depending on the contract. Client organisations began warning their own customers and patients in October and November; a social landlord in Colomiers wrote to tenants on 10 November. On 13 November Maileva confirmed the 22 million figure. [2]
Why this matters
Most of the 22 million people have never heard of Maileva. Outsourced print, mail and billing services hold data on behalf of thousands of organisations, so one incident becomes a mass exposure, and a name plus the knowledge of who writes to you is enough for a convincing fake payment demand. (MAG212 analysis)
Chronologie
| Date | Événement |
|---|---|
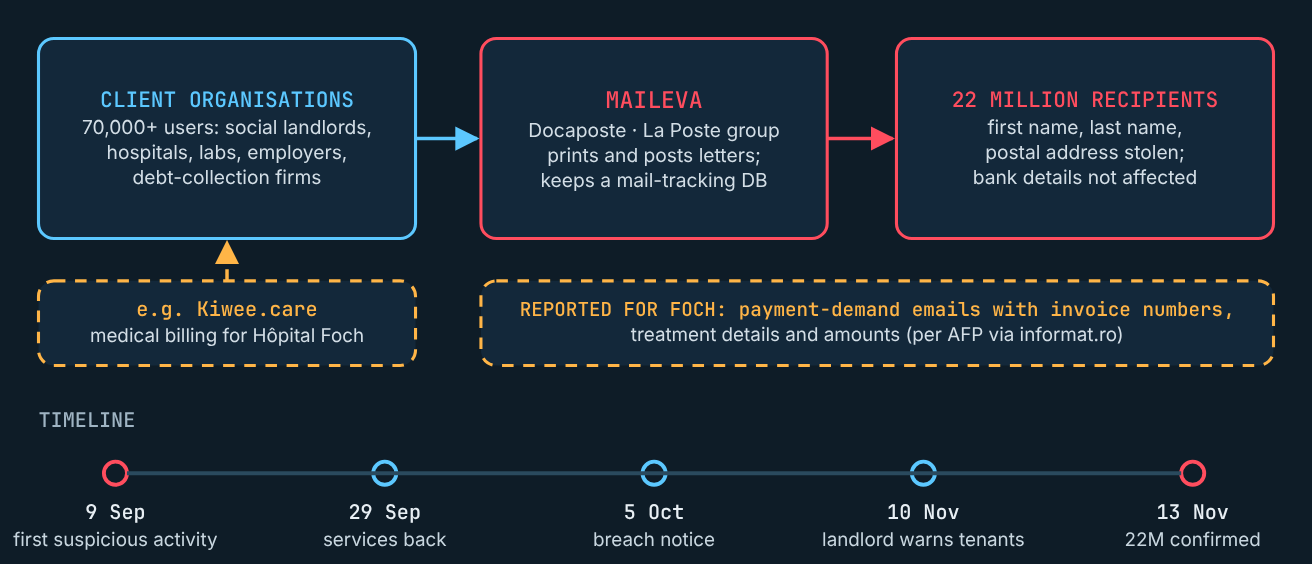
| 9 Sep 2026 | First suspicious activity on Maileva’s system, per Docaposte’s notice |
| 29 Sep 2026 | Maileva services fully operational again |
| 5 Oct 2026 | Docaposte breach notice confirms database access (about 22 million people) |
| 10 novembre 2026 | Client notifications reach tenants and patients |
| 13 Nov 2026 | Maileva confirms 22 million people affected |
| 14–15 Nov 2026 | La Poste confirms to AFP; CNIL notified, complaint filed |
Timeline compiled from the Docaposte notice and client letters as tracked by [2], with confirmation in [1] et [3].
Qui est concerné ?
People who received letters through Maileva’s business clients: tenants of social housing associations, patients of laboratories and hospitals, employees and debtors. At Hôpital Foch, the attackers reportedly accessed emails about payment demands containing invoice numbers, treatment details and amounts owed, via Kiwee.care, a medical-billing subcontractor that prints and mails through Maileva. [1][3]
Comment fonctionne l'attaque
Not disclosed. Neither the entry point nor the attacker has been named.
What defenders and individuals should look for
- Fake payment demands that name a real landlord, laboratory, hospital or employer.
- Requests to pay through a new link or to new bank details.
- Phishing emails and letters that combine the stolen name and address with details from other breaches.
If your organisation outsources print, mail or billing
- Ask the provider in writing whether your recipients’ data was in the affected database and how long it was kept.
- Warn recipients that you will never ask for payment through a new link or new bank details.
- Set retention limits in contracts; tracking data rarely needs to be kept for ten years.
- Map sub-processors: Hôpital Foch’s exposure came through a billing subcontractor.
- Check your GDPR notification duties with your DPO if your data subjects are affected.
If you received a letter
- Treat unexpected payment demands as suspect and call the sender on a number you already have.
- Expect phishing that names your landlord, laboratory or hospital.
Prévention et sensibilisation
Data minimisation is the strongest control here: a mail provider needs an address for as long as a letter is in transit, not for a decade. Leaders should ask which suppliers hold customers’ or patients’ data, and for how long.
Sujets connexes sur MAG212 CYBER
- MAG212 CYBER Daily, 15 November 2026: Machine speed, human gaps (full issue and PDF)
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] Security Affairs, “Data breach at La Poste subsidiary Maileva affects 22 million people in France“, 15 Nov 2026.
- [2] Anas Sahel (tracker), “Maileva: mail-tracking data of about 22 million people accessed (timeline, Docaposte notice)“, Nov 2026.
- [3] Informat.ro (AFP), “Branch of the French postal service confirms theft of data of 22 million people“, 15 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 15 November 2026, 7:45 AM PST.