
Exploitation d'une faille dans le VPN SonicWall, élargissement de la faille Chainalysis et fuite de secrets d'agents : MAG212 CYBER Daily, 7 novembre 2026
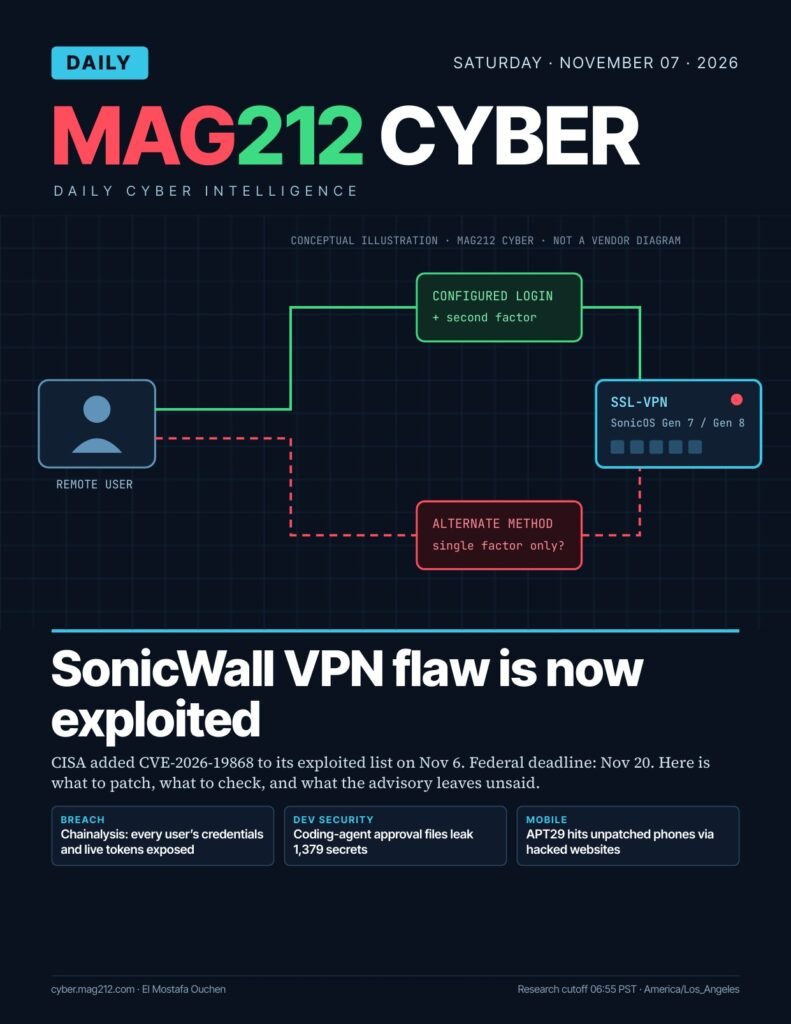
MAG212 CYBER · Daily Cyber Intelligence · Saturday, November 7, 2026. Research cutoff 06:55 PST. This technical edition adds three deep-dive pages: proving MFA was enforced on SonicWall SSL-VPN, the SSHole code path in OpenSSH, and block-update-hunt commands for every WordPress web stack.
Qu'est-ce qui requiert notre attention aujourd'hui ?
| Priority | Histoire | Action |
|---|---|---|
| 1 · Exploited | SonicWall SonicOS SSL-VPN, CVE-2026-19868 (CISA KEV Nov 6, due Nov 20) | Gen 8 → 8.2.3-8015; Gen 7 → newest 7.3.4 build. Save logs first; review VPN logins with no matching MFA event. |
| 2 · Breach | Chainalysis: names, usernames, password hashes and live tokens for all users exposed | Reset passwords; rotate API keys after IP allowlisting; review API logs since Oct 30. |
| 3 · Research | Claude Code “don’t ask again” files: 1,379 secrets in public repos | Find tracked .claude/ files and history; rotate anything found. |
| 4 · Update | OpenSSH “SSHole” CVE-2026-123158: 17 attempts, 11 IPs, 8 countries | Install Alpine’s fixed openssh and restart sshd, or disable password auth. |
| 5 · Update | WordPress CVE-2026-119977 first-update window | Block wp-content/upgrade, update, confirm 403, verify checksums. |
| 6 · Mobile | APT29 watering holes hit outdated iOS and Android (Sekoia) | Enforce current OS versions through MDM. |
What’s inside
- SonicWall lead story, version table and a technical deep dive with hunting logic and hardening controls
- Chainalysis breach scope and the rotation checklist
- Coding-agent approval files: how secrets leak, Git commands that don’t print secrets, and a gitleaks rule for inline passwords
- SSHole: why a 257–1,024-byte password matches “*”, read from OpenSSH source, plus Alpine hunting commands
- WordPress: Apache, LiteSpeed and nginx blocking rules, log and file hunting, WP-CLI integrity checks
- APT29 mobile exploit chains; briefs on DigiCert, Norad and Queens Public Library
- Japan’s emergency cyber package, OpenAI’s GPT-6 Cyber access controls, and a $129M AI deepfake fraud case
- Defender’s Action Desk, recent CISA KEV additions, awareness lesson and full source register
Mises à jour sur les articles précédents
- OpenSSH SSHole: exploitation attempts spread from one IP in Japan (Nov 6) to 11 IPs in 8 countries (Nov 7). The honeypot root login is a claim by Previdian’s CEO; no logs are public. Not in CISA KEV.
- WordPress CVE-2026-119977: Wordfence found the first-update window lasts seconds; Picus advises blocking the staging path in the root .htaccess before updating.
- Refrigeration controllers: no new information since our Nov 6 coverage, so not repeated.
Feuilletez l'édition
How we verified this issue: every story was checked against vendor, government or original-researcher sources. Confirmed facts, reported claims and MAG212 analysis are labelled separately. Commands were checked against official documentation but not executed on affected systems. Written and edited by El Mostafa Ouchen. Abonnez-vous gratuitement to get each issue by email.