
The Supplier Breach Ledger, November 2026: JPMorgan, Visa and Mastercard Vendors, Wellington IT, TfL, Rakuten and N-able
De la part de MAG212 CYBER Daily, 22 November 2026. This article was written with AI assistance and edited by El Mostafa Ouchen. Commands, where included, were non testé par MAG212; run them only on systems you are authorised to administer.
Statut: as of 22 November 2026. Facts are marked as confirmed by the company, reported, or claimed by attackers. [1][3]
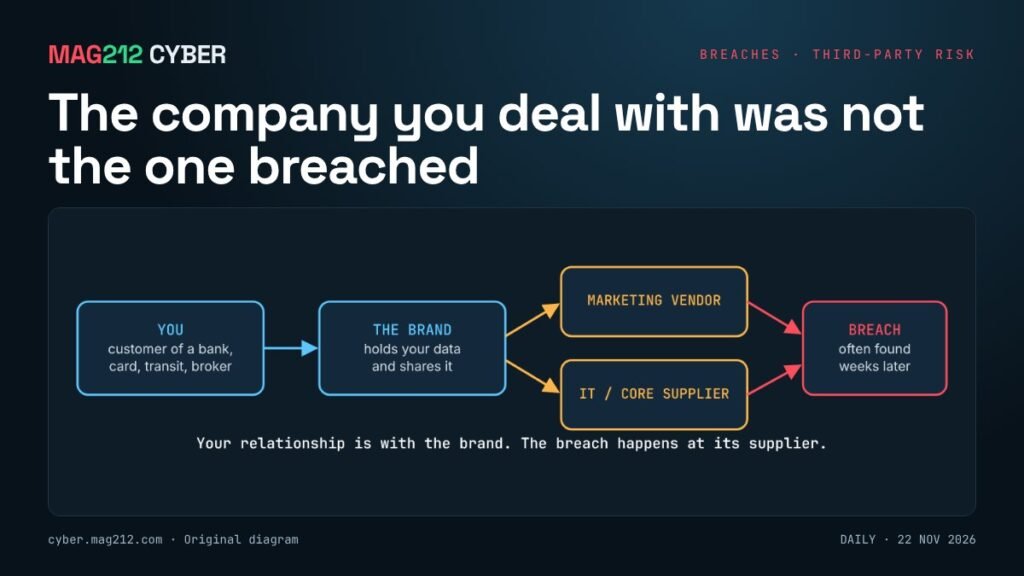
JPMorgan Chase, Visa and Mastercard vendors
- Confirmed: all three cite incidents at unnamed third-party vendors. JPMorgan says marketing data that may include customer names and email addresses was accessed, and it will offer credit monitoring “where appropriate”. Mastercard cites a limited amount of information from cardholders in one benefit programme. Visa cites a service provider in the Asia-Pacific region. All say payment systems were not affected. [1][2]
- Reported, not confirmed: Reuters’ review of leaked files found more than 16,000 JPMorgan customer email addresses. [2]
- Claimed: the n0n extortion group claims responsibility. None of the companies has confirmed that, and no vendor has been named. [1]
Background: SOCRadar describes n0n as getting in with stolen or weak credentials rather than exploits, and sometimes destroying data. [10]
Pourquoi c'est important
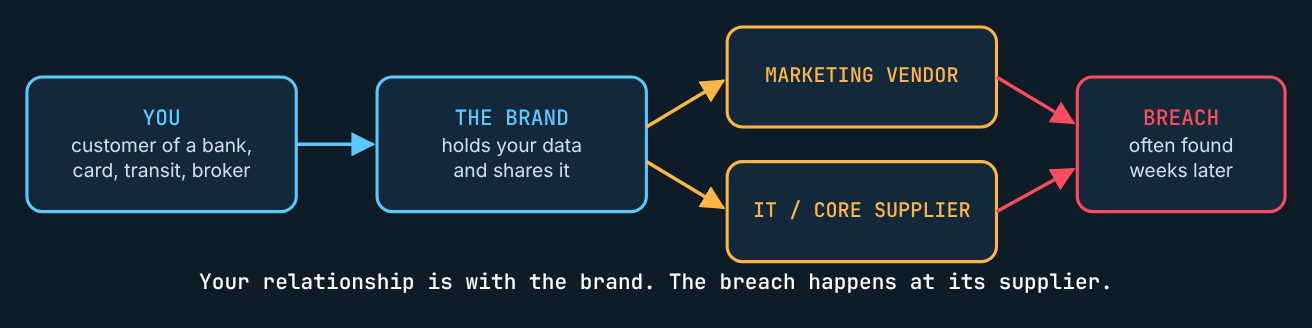
Customers trust a brand, but their data often sits with that brand's marketing agencies, IT suppliers and service providers. When one of those is breached, notices arrive late, details are thin, and scammers get the raw material for convincing fake "breach notice" messages. Knowing where each case actually stands is the first defence against that wave. (Analyse MAG212)
Wellington IT and Irish credit unions
Affected credit unions date the exploitation to 2–4 October; the flaw was closed on 6 October. Exposed data includes saved payee names, IBANs, sort codes, payment references and addresses; logins, passwords and PINs were not affected. Reports put the number of credit unions at about 40 to 43. Ireland’s Minister of State Robert Troy called the delay in notifying customers “not acceptable”. [4][5]
Transport for London
This one was not a supplier: TfL’s own mail systems were compromised. About 265,000 Oyster photocard holders are affected, with names, addresses, dates of birth and security questions and answers exposed. Payment data and journey history were not. The Information Commissioner’s Office has been informed. [6][7]
Rakuten Securities
Login IDs and customer codes for up to 11.25 million accounts may have been exposed, and a richer set covering up to 4.47 million accounts includes names, dates of birth, addresses, withdrawal bank details and holdings. No exposure of passwords or trading PINs and no fraud have been confirmed. [8]
N-able Mail Assure and SpamExperts
N-able says credentials stored on one breached server “may” have been accessed. It rotated internal credentials, revoked customer API and OAuth tokens and reset local-user passwords. MSPs should expect integrations to need new tokens. [3]
The Container Store
Systems have been restored after a weekend incident, and customer financial data “does not appear” to have been taken. The company has not addressed n0n’s earlier listing of it. [9]
Ce qu'il faut faire
- Customers: treat any message that mentions one of these breaches as suspect. Open the app or type the website address yourself, and call the number on your card rather than any number in a message.
- Credit union and bank customers: confirm any “your payee details changed” request by phone before money moves.
- MSPs on N-able: re-issue API and OAuth tokens and review logins.
- Businesses: list the suppliers that hold your customers’ data, put breach-notice deadlines in contracts, and prepare a “how we will and won’t contact you” message now. These are MAG212’s recommendations.
Sujets connexes sur MAG212 CYBER
- MAG212 CYBER Daily, 22 November 2026: Can police trust the record? (numéro complet et PDF)
- MAG212 CYBER Weekly, 21 November 2026: Machine Speed
- MAG212 CYBER Daily, 20 novembre 2026 : Les clés de vSphere
- Abonnez-vous gratuitement à MAG212 CYBER
Sources
- [1] SecurityWeek, “JPMorgan, Visa et Mastercard évoquent des incidents impliquant des tiers dans le contexte de la fuite de données.“, 20 novembre 2026.
- [2] Business Insurance (Reuters), “JPMorgan, Visa, Mastercard say third-party vendors targeted in cyberattack“, 20 novembre 2026.
- [3] SecurityWeek, “N-able attribue la perturbation de son service à une cyberattaque.“, 20 novembre 2026.
- [4] The Register, “Wellington IT breach: Irish credit unions and the six-week gap“, 19 novembre 2026.
- [5] The Irish Times, “Suspected data breach at 43 credit unions could affect hundreds of thousands of members“, 17 novembre 2026.
- [6] BleepingComputer, “Transport for London breach exposes 265,000 Oyster card users' data“, 19 novembre 2026.
- [7] Transport for London, “Cyber security incident“, novembre 2026.
- [8] CyberDelegate, “Rakuten Securities warns customer data from up to 11.25 million accounts may have been exposed“, 18 novembre 2026.
- [9] Le Record, “The Container Store restores systems after cyberattack“, 20 novembre 2026.
- [10] SOCRadar, “n0n ransomware: AI-assisted extortion (background)“, 28 Oct 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 22 November 2026, 7:00 AM PT.