
CVE-2026-101767: Oracle E-Business Suite Flaw Lets One HTTP Request Reach the Database and the Host
MAG212 CYBER | Critical CVEs | October 28, 2026
CVE-2026-101767 is a critical, unauthenticated vulnerability in Oracle E-Business Suite (EBS), the ERP platform many organizations use for finance, HR, procurement and payments. Horizon3.ai, which discovered it, shows how a request to a default-allowed servlet reaches the database as the powerful APPS schema and then chains to operating-system commands. Oracle fixed it in the October 2026 Critical Patch Update on 20 October. Exploitation attempts against honeypots began two days later.
Key facts
| Item | Detail |
|---|---|
| CVE | CVE-2026-101767 |
| Product | Oracle E-Business Suite, Application Object Library (Core) |
| Severity | CVSS 3.1 9.8 Critical (AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H) |
| Weakness | CWE-89 + CWE-306 per Horizon3.ai; CWE-287 + CWE-306 per CVE trackers |
| Authentication | None required |
| Affected | EBS 12.2.3 through 12.2.15 |
| Fixed | October 2026 Critical Patch Update (20 Oct; revised 26 Oct) |
| Exploitation | Attempts observed from 22 Oct 2026; no confirmed compromises reported |
| CISA KEV | Not listed as of 28 Oct 2026 |
| Credit | Brandon Peterson, Jimi Sebree and Noah King (Horizon3.ai) |
Oracle’s own advisory text describes the flaw as allowing takeover and does not use the words “SQL injection”; that characterization comes from Horizon3.ai’s research.
How the attack works
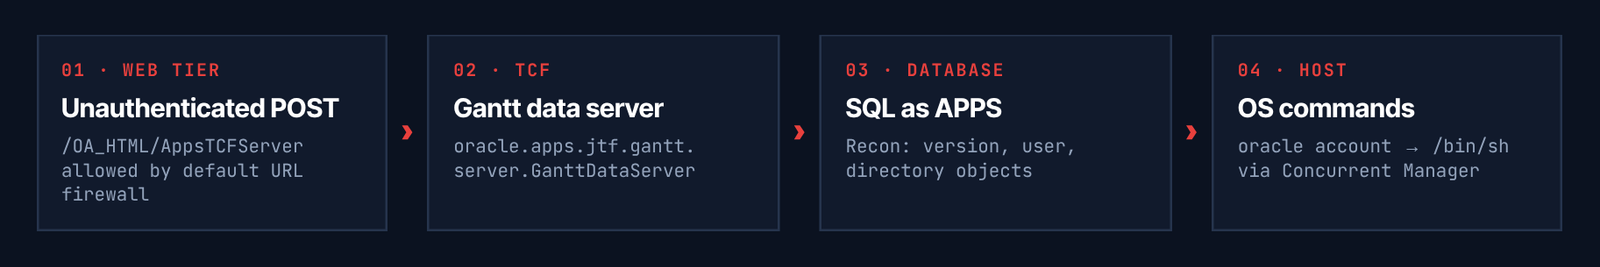
- Web tier. An unauthenticated POST reaches
/OA_HTML/AppsTCFServer, the Thin Client Framework socket servlet (oracle.apps.fnd.tcf.SocketServer). It is allowed by EBS’s default URL firewall. - TCF. The request invokes the Gantt data server (
oracle.apps.jtf.gantt.server.GanttDataServer). - Database. The attacker executes SQL as APPS, the schema that owns EBS’s business data, and typically starts with reconnaissance: database version, current user, directory objects.
- Host. The chain extends to OS command execution as the EBS application account (the
oracleuser in Horizon3’s indicators), for example a shell spawned through the Concurrent Manager.
OS execution as the oracle user is not automatic root access. But APPS can read and change financial, HR, supplier and payment records, which usually matters far more than the server itself.
Why EBS flaws get exploited fast
Oracle EBS has a recent history of mass exploitation. In 2025, CVE-2025-61882 (CVSS 9.8) was used in the Cl0p data-extortion campaign, which later reporting tied to more than 100 organizations. In June 2026, CVE-2026-46817 in Oracle Payments was exploited and added to KEV. Shadowserver counted about 950 internet-exposed EBS instances on 1 July 2026.
For CVE-2026-101767, Previdian’s sensors logged the first exploitation attempt at 17:28 UTC on 22 October: eight attempts from five IP addresses in five countries over the following week, six of them on 27 October. Defused reported exploratory hits on its EBS decoys on 27 October. Two GitHub repositories claiming to be proofs of concept appeared on 26 October; both are unverified and may contain malware. Do not run them.
How to fix and harden
- Apply the October 2026 Critical Patch Update for your EBS release, following Oracle’s patch availability document. Use your normal online patching (adop) cycle and record the patch IDs and cycle results.
- Remove AppsTCFServer from the URL firewall allowlist and restrict the EBS web tier to trusted networks, as Horizon3.ai recommends. Do this now, even before patching. Check first whether any features you use (such as Gantt views) depend on TCF.
- Close every route. Map load balancers, reverse proxies, partner VPNs and disaster-recovery nodes. An edge block is incomplete if a partner network or compromised workstation can still reach an origin server.
- Retest with an approved, non-destructive method after patching, and keep restrictions in place until the application owner accepts the residual risk.
A simple edge rule while you patch:
# reverse proxy: deny the TCF servlet
location ~* ^/OA_HTML/AppsTCFServer {
    deny all;
}
How to hunt for CVE-2026-101767 activity
Preserve evidence before you clean anything: OHS and web access logs, proxy and WAF logs, database audit records and endpoint telemetry. Record clock offsets between systems. On 12.2, collect the Oracle HTTP Server logs under the instance home. Don’t delete files in $APPLPTMP before responders image them.
| Layer | What to look for |
|---|---|
| Web | Unauthenticated POSTs to /OA_HTML/AppsTCFServer invoking GanttDataServer |
| Database | Reconnaissance soon after: v$version, current user, all_directories |
| Filesystem | Unexpected files in $APPLPTMP |
| Process | The oracle account spawning /bin/sh through the Concurrent Manager |
A quick read-only search of an exported log:
rg -n "AppsTCFServer" /path/to/exported-access.log
rg -n "POST .*AppsTCFServer" /path/to/*.log | \
  awk '{print $1}' | sort | uniq -c | sort -rn
A match is a lead, not proof of compromise. No match is not a clean bill of health if your logs are incomplete. Correlate web requests with database sessions and process activity in a narrow time window.
Frequently asked questions
Which Oracle EBS versions are affected by CVE-2026-101767?
Oracle E-Business Suite 12.2.3 through 12.2.15. The fix is in the October 2026 Critical Patch Update.
Is CVE-2026-101767 being exploited?
Exploitation attempts have been observed since 22 October 2026, but no confirmed compromises had been reported as of 28 October, and the flaw was not yet in CISA’s KEV catalog.
Does blocking the URL fix the vulnerability?
No. Blocking /OA_HTML/AppsTCFServer reduces exposure while you patch, but only the Critical Patch Update fixes the flaw. Make sure every route to the application is covered.
Is there a public exploit?
Researchers have not published a payload. Repositories claiming to be exploits appeared on 26 October but are unverified and may be malicious.
Sources
- Horizon3.ai: CVE-2026-101767
- Oracle Critical Patch Update Advisory, October 2026
- Previdian: CVE-2026-101767 exploitation telemetry
- CISA Known Exploited Vulnerabilities catalog
This article expands the Oracle EBS feature from the MAG212 CYBER October 28, 2026 Intelligence Edition. Score vulnerabilities with our free CVSS 3.1 calculator.