
When Trust Becomes Access: Brotli, Tailscale, Magento, Oracle EBS and SkyW4lker
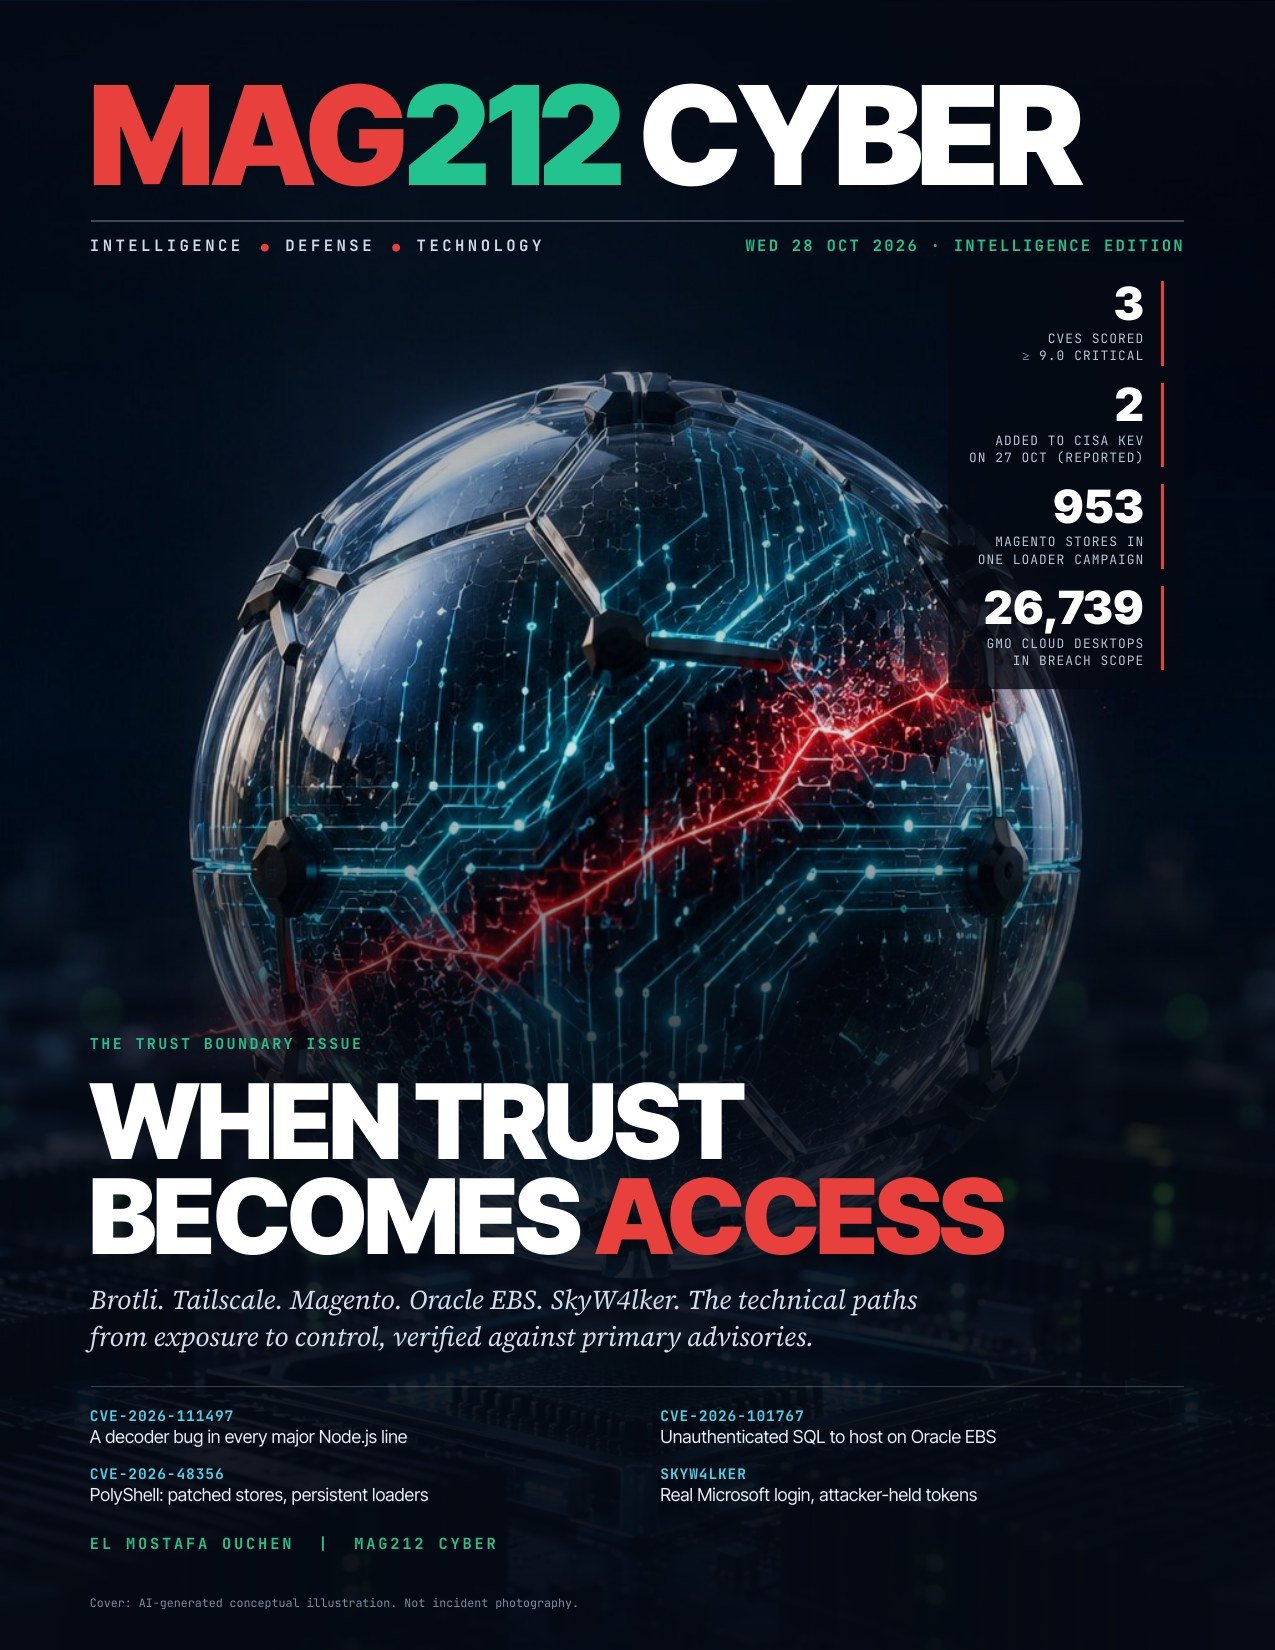
Flip through the magazine
Turn the pages below, or use full-screen mode for the best reading experience. Prefer a file? Use the download button above.
MAG212 CYBER | October 28, 2026
By El Mostafa Ouchen
Security headlines arrive as names and numbers. Defenders need a different view: which component accepts untrusted input, which permission boundary fails, which assets are reachable, and what proves a fix is actually running. This 28-page Intelligence Edition follows that chain across a JavaScript runtime, a private-network agent, a storefront database, an enterprise resource-planning suite and the Microsoft 365 sign-in itself. Every story was re-verified against vendor advisories and original research on October 28, 2026.
The briefing: what to act on first
| Issue | Severity | Exploitation | Fix |
|---|---|---|---|
| CVE-2026-111497 Node.js bundled Brotli decoder | CVSS v4 9.2 (Google CNA) CVSS v3.1 8.1 (Red Hat) | Added to CISA KEV on Oct 27 (reported), due Nov 10. Honeypot attempts only | Node 22.23.4 / 24.22.1 / 26.12.1; libbrotli 1.0.10 / 1.1.1 / 1.2.1 |
| CVE-2026-48356 “PolyShell” Adobe Commerce / Magento | 9.6 (Adobe) / 9.3 (CVE record) | Mass exploitation since March; KEV Oct 27 (reported) | APSB26-73 date builds (2.4.x-2026-jul) |
| CVE-2026-101767 Oracle E-Business Suite | CVSS 3.1 9.8 | Attempts since Oct 22; not in KEV at press | October 2026 CPU (12.2.3–12.2.15) |
| TS-2026-014 … 017 Tailscale SSH & Serve | No CVE / CVSS assigned | Requires an authorized foothold; PoC private | Tailscale v1.104.4 |
| SkyW4lker Microsoft 365 device-code phishing | No CVE: protocol abuse | 618 sandbox analyses, June to Oct 21 | Conditional Access: block device code flow |
Read the full analysis
- SkyW4lker device-code phishing: how it hijacks Microsoft 365 accounts, KQL hunts and how to block it
- CVE-2026-111497 (Node.js Brotli): fixed versions, attack paths and runtime checks
- CVE-2026-101767 (Oracle EBS): the AppsTCFServer chain, indicators and mitigation
- PolyShell (CVE-2026-48356): the Magento cms_block loader, IOCs and clean-up checklist
- Tailscale SSH TS-2026-014 to 017: what v1.104.4 fixed and how to harden
Inside this issue
- p. 03 · Threat dashboard: every CVE with score, vector, CWE, KEV status and fixed version, plus an editorial priority matrix.
- p. 04 · Nine days in October: the overlapping timeline of disclosure, patching, exploitation and extortion, Oct 20–28.
- p. 05 · Brotli / Node.js: how one mis-classified error code becomes a heap write; reachable entry points, upstream exposure, inventory commands and a proxy mitigation.
- p. 07 · Tailscale SSH: four bulletins, the “Tailworm” disclosure dispute, forwarding mitigation and policy hardening.
- p. 09 · Magento / PolyShell: a 953-store loader campaign hiding in
cms_block; SQL triage, IOCs and a closure checklist. - p. 11 · Oracle EBS: from an unauthenticated POST to SQL as APPS to a shell; Horizon3.ai indicators and a remediation proof plan.
- p. 13 · SkyW4lker (new): real Microsoft login, attacker-controlled authorization. The full attack chain, why MFA doesn’t stop it, KQL hunts, Conditional Access and eviction steps.
- p. 17 · GMO Desktop Cloud: a hosted trading-desktop breach, a refused US$50M demand and a US$1M cybercrime bounty.
- p. 19 · Intel × Classiq & post-quantum migration: NIST IR 8547 is final; RSA/ECC deprecated after 2030 and disallowed after 2035.
- p. 22–28: technology radar, detection engineering lab, the operator’s 72-hour plan, verification ledger, and sources.
Spotlight: SkyW4lker device-code phishing
ANY.RUN’s October 27 analysis describes SkyW4lker x365 Sentinel, a Microsoft 365 phishing kit that never needs a fake login page. A password-protected PDF, DOCX or XLSX lure leads through a CAPTCHA to a page on trusted hosting. The kit’s backend starts an OAuth device-code sign-in and asks the victim to enter the code on Microsoft’s genuine device sign-in page. The victim completes MFA, and Microsoft issues access and refresh tokens to the attacker. Phishing-resistant MFA does not stop it; blocking the device code flow with Conditional Access does. Read the full SkyW4lker analysis →
Do this now
- Hunt
SigninLogsforAuthenticationProtocol == "deviceCode"over the last 30 days. - Create a Conditional Access policy: Authentication flows → Device code flow → Block, in Report-only first, with narrow exclusions for Teams Rooms devices.
- Check whether the Microsoft-managed “Block device code flow” policy exists in your tenant and when it will be enforced.
- For any hit: disable the account, revoke sessions, remove attacker-registered devices, reset the password and clean inbox rules.
- Tell staff: never enter a code from an email, document or caller into a Microsoft page.
The 72-hour plan, in brief
- 0–4 hours, identify and contain: inventory running Node versions; set
TS_SSH_DISABLE_FORWARDING=1; run the Magentocms_blockquery; deny/OA_HTML/AppsTCFServerat the edge; hunt device-code sign-ins. - 4–24 hours, patch and prove: rebuild images on fixed Node releases; roll Tailscale 1.104.4; apply APSB26-73 and the Oracle October CPU; put the device-code block in Report-only.
- 24–72 hours, hunt and harden: review crash loops, enrollments, CMS writes and EBS indicators; rotate secrets after containment; enforce the device-code block.
How we verified this issue
Each claim is labeled Verified (confirmed in a primary source), Reported (attributed to secondary reporting) or Editorial (MAG212 analysis and guidance). A verification ledger on page 25 lists every correction made to our draft. Where sources disagree, such as conflicting CVSS scores or KEV status, the magazine shows both. Some items remained open at press time: CISA’s catalog could not be read directly, and GMO’s own notices could not be loaded. Confirm deadlines before acting on them.
Primary sources
- Node.js October 2026 security releases
- Tailscale: Tailscale SSH findings and fixes
- Sansec: Magento CMS block loader hits 953 stores
- Adobe Security Bulletin APSB26-73
- Horizon3.ai: CVE-2026-101767 and Oracle CPU October 2026
- ANY.RUN: SkyW4lker phishing kit analysis
- Microsoft Learn: block authentication flows with Conditional Access
- NIST IR 8547 (final)
The complete list of 30 numbered sources is on pages 26–27 of the magazine.
Editor and author: El Mostafa Ouchen
Publisher: MAG212 CYBER (cyber.mag212.com)
Issue date: October 28, 2026
Format: 28-page PDF, Intelligence Edition
Visuals: AI-generated editorial illustrations and original schematics, all labeled; no incident photography.