
CVE-2026-111497: The Node.js Brotli Flaw in CISA KEV, Explained, With Fixed Versions and Checks

MAG212 CYBER | Critical CVEs | October 28, 2026
CVE-2026-111497 is a memory-corruption flaw in the Brotli decompressor that ships inside Node.js. Malformed compressed input can make the decoder write past an eight-byte internal buffer, which can crash a process, leak memory or, under the right conditions, lead to code execution. Node.js fixed it on 21 October 2026, and CISA added it to its Known Exploited Vulnerabilities (KEV) catalog on 27 October with a 10 November deadline for US federal agencies. Red Hat calls it “node2shell”.
Key facts
| Item | Detail |
|---|---|
| CVE | CVE-2026-111497 |
| Component | Brotli decoder bundled with Node.js (node:zlib); upstream Google Brotli library |
| Weakness | CWE-787 out-of-bounds write; CWE-252 unchecked return value |
| Severity | CVSS v4 9.2 Critical (Google, the issuing CNA); CVSS v3.1 8.1 Important (Red Hat, AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H); “High” (Node.js) |
| Affected | Node.js 22.x, 24.x, 26.x; Brotli 1.0.3 through 1.2.0 |
| Fixed | Node.js 22.23.4, 24.22.1, 26.12.1; Brotli 1.0.10, 1.1.1, 1.2.1 |
| End-of-life | Node.js 20.x and older receive no fix |
| CISA KEV | Added 27 October 2026; federal due date 10 November 2026 (as reported) |
| Credit | OpenAI Codex Security (Khai Tran, Sylvie Mayer) |
What went wrong
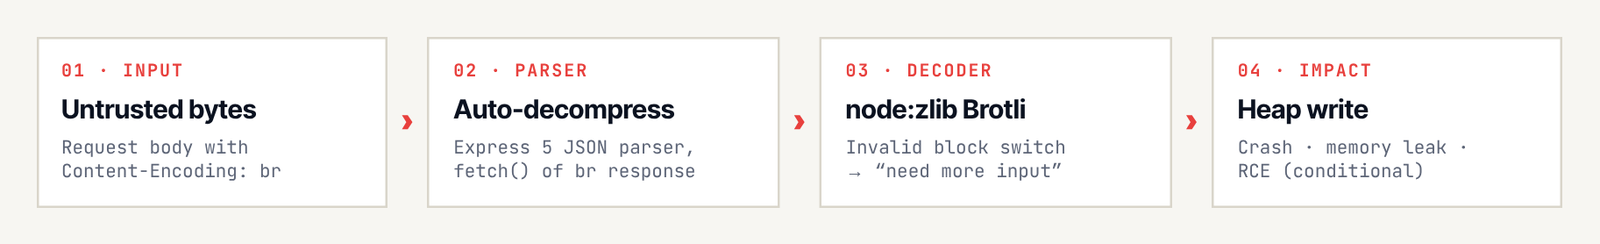
The Node.js advisory explains the root cause precisely: an invalid block switch in a Brotli stream “was reported as a temporary need for more input instead of a permanent format error”. The streaming decoder treated a fatal error as “send me more data”, kept appending incoming bytes, and those bytes landed beyond an eight-byte internal buffer in native memory.
How serious is it in practice?
The score depends on who you ask, and that tells you something. Google rates it 9.2 because it is reachable over the network without authentication. Red Hat rates it 8.1 with high attack complexity, because reliable code execution needs specific heap conditions and platform hardening gets in the way.
The public proof-of-concept released on 22 October reached code execution only on a deliberately weakened build; on standard builds it caused a crash and a limited memory leak. Observed exploitation is small so far: Previdian logged one attempt on 27 October, and ELLIO tracked one source targeting Node 24.22.0, the last unpatched 24.x release. CISA’s KEV listing means you should treat it as urgent anyway. Crashes alone can take down services.
Is your application exposed?
The vulnerable direction is decoding attacker-supplied Brotli data. A server that only sends Brotli-compressed responses is not exposed by that. Look for these paths:
| Entry point | Reported by |
|---|---|
zlib.brotliDecompress() / brotliDecompressSync() | Red Hat |
zlib.createBrotliDecompress() streams | Red Hat |
fetch() / undici decoding Content-Encoding: br responses | Red Hat, The Hacker News |
Express 5 default body parsing of Content-Encoding: br requests | Sysdig, via The Hacker News |
The bug is in Google’s Brotli library itself, so it also reaches beyond Node. Rapid7 and Red Hat list Bun, the Python brotli and brotlicffi packages, .NET, Envoy and Istio, brotli4j, Firefox, Thunderbird and RHEL 7 through 10 among affected software.
How to check your Node.js runtimes
Run these read-only commands inside each container or service, not just on your workstation. The Node binary in your shell may differ from the one a running worker uses.
node -p "process.version + ' brotli ' + process.versions.brotli"
node -p "process.config.variables.node_shared_brotli"
# if true, Node links the system Brotli library: patch it too
ldconfig -p | grep -i brotli
rpm -q libbrotli 2>/dev/null || dpkg -l 'libbrotli*'
On Ubuntu 22.04 and later, RHEL 10, and Node 22 on RHEL 8 and 9, Node uses the operating system’s Brotli library. In those environments, updating Node alone is not enough: update the OS package as well.
How to fix CVE-2026-111497
- Upgrade Node.js to 22.23.4, 24.22.1, 26.12.1 or later. If you are on Node 20 or older, upgrade to a supported line; no fix exists for end-of-life versions.
- Rebuild container images from patched base images and redeploy every replica. Track the image digest, not just the tag.
- Restart long-lived processes, including background workers, scheduled jobs, CI runners and build agents.
- Patch the OS Brotli package where Node uses the shared library, and update other affected runtimes (Bun, Python brotli, Envoy).
- Don’t forget bundled runtimes in Electron apps and Node single-executable applications.
Close the ticket only when the running process reports a fixed version, every replica has restarted, and normal application tests pass.
Temporary mitigation if you can’t patch today
Node.js publishes no workaround; upgrading is the only complete fix. Red Hat suggests rejecting or stripping Content-Encoding: br at the proxy for endpoints that don’t need compressed request bodies:
# nginx: reject Brotli-encoded request bodies
if ($http_content_encoding ~* "br") {
    return 415;
}
Test this against legitimate clients first. It protects inbound requests only; it does nothing for outbound fetch() calls that decode untrusted responses. Vercel deployed equivalent inbound firewall rules for its customers on 21 October.
How to spot attacks
There are no vendor-published detection rules yet. A practical signal is crash loops on unpatched runtimes: Node processes exiting with SIGSEGV, SIGABRT or allocator errors such as free(): invalid, shortly after requests carrying Content-Encoding: br. Pair container restart data with proxy logs that capture the request header.
The same release fixed nine more CVEs
The 21 October security release fixed 10 CVEs in total. Besides the Brotli flaw, it addressed high-severity issues in DNS NUL-byte handling (CVE-2026-105482) and TLS IP address matching (CVE-2026-105483, CVE-2026-106069), plus medium and low-severity fixes for HTTP keep-alive, certificate handling, random number entropy in snapshots and the Permission Model. It also distrusted compromised eMudhra intermediate certificates and updated undici, c-ares, OpenSSL and SQLite. That’s one more reason to take the update rather than a narrow workaround.
Frequently asked questions
Which Node.js versions fix CVE-2026-111497?
Node.js 22.23.4, 24.22.1 and 26.12.1, or later versions in those lines.
Is CVE-2026-111497 being exploited?
CISA added it to KEV on 27 October 2026, citing active exploitation. Publicly observed activity is limited to a handful of honeypot attempts, with no confirmed compromises reported as of 28 October.
Am I affected if my server only compresses responses with Brotli?
Compressing outgoing responses doesn’t trigger the bug. Exposure comes from decompressing untrusted Brotli data, such as request bodies or responses from untrusted servers.
Does upgrading Node.js fix it everywhere?
Not always. Where Node links the system Brotli library, and in other runtimes like Bun or Python, you must update those components too.
Sources
- Node.js: October 2026 security releases
- Red Hat: CVE-2026-111497
- Rapid7: Critical out-of-bounds write in the Node.js Brotli decoder
- The Hacker News: PolyShell attacks and Brotli exploit traffic (28 Oct 2026)
- Google Brotli releases
- CISA Known Exploited Vulnerabilities catalog
This article expands the Brotli feature from the MAG212 CYBER October 28, 2026 Intelligence Edition. Score other vulnerabilities with our free CVSS 3.1 calculator, or read CVE & CVSS explained.