
SonicWall CVE-2026-19868 Update: SSL-VPNs That Skip SAML MFA, Fixed SonicOS Builds and the 20 Nov Deadline
If your SonicWall SSL-VPN sends users through a SAML identity provider for MFA, a user holding credentials for a different login method can skip that MFA entirely. SonicWall has fixed the flaw, CVE-2026-19868, in SonicOS 7.3.4-7013 and 8.2.3-8015, there is no workaround, and CISA has listed it as exploited with a federal deadline of 20 November. We first reported the exploitation on 7 November (MAG212 CYBER Daily, 7 November); this update sets out exactly which devices are exposed, what to upgrade to and what else is in the same advisory.
| CVE | CVE-2026-19868, SonicOS SSL-VPN “use of single-factor authentication” (CWE-308) |
| Affecté | Gen7 TZ/NSa/NSsp/NSv on SonicOS 7.3.3-7015 or older; Gen8 TZ/NSa/NSv on 8.2.2-8015 or older |
| Exposure condition | Only when SSL-VPN is configured for SAML authentication |
| Fixé dans | SonicOS 7.3.4-7013 (Gen7) and 8.2.3-8015 (Gen8) |
| Workaround | Aucun |
| Exploité | SonicWall cites a report of potential exploitation; CISA KEV since 6 Nov |
| Deadline | Federal KEV due date 20 Nov 2026 |
| CVSS | 7.1 (SonicWall); 7.5 from CISA’s scoring, reported second-hand |
What has changed since our first report
CISA added CVE-2026-19868 to KEV on 6 November with a 20 November due date (CISA KEV), and The Hacker News covered CISA’s flagging of it on 9 November (Les actualités des hackers). Trade-press reporting has since filled in the details of SonicWall advisory SNWLID-2026-0014. SonicWall says it “investigated a report of potential exploitation” of the flaw but has not described the attacks (BleepingComputer). The issue was reported by Ryan Harris of The Electronic Office, and SonicWall is urging customers to upgrade as soon as possible.
Qui est concerné ?
According to SecurityWeek and BleepingComputer, the vulnerable builds are Gen7 TZ, NSa, NSsp and NSv appliances on SonicOS 7.3.3-7015 or older, and Gen8 TZ, NSa and NSv appliances on 8.2.2-8015 or older. A device is exposed to this particular flaw only if its SSL-VPN is configured for SAML authentication (Semaine de la sécurité; BleepingComputer).
The same advisory fixes six more SonicOS issues whose exploitation status is not stated: two management-interface flaws rated 8.8 (CVE-2026-107155 and CVE-2026-107154), a pre-authentication SSL-VPN heap overflow that causes denial of service (CVE-2026-82308, 7.5), two TACACS+ issues rated 5.9 (CVE-2026-77708 and CVE-2026-77709) and weak password hashing on virtual appliances (CVE-2026-19703, 5.2). Those details come from a secondary digest (Oflight).
Analyse CYBER MAG212 : MSPs and schools that front SonicWall SSL-VPN with Entra ID, Google or another SAML provider are the group directly at risk. Fleets that don’t use SAML should still upgrade, because of the two 8.8-rated management-interface flaws.
Comment fonctionne l'attaque
As reported, a user who holds valid credentials for an alternate authentication method on the appliance can get past the SAML controls on SSL-VPN logins, including MFA that the SAML provider would normally enforce (Semaine de la sécurité). In other words, the second door into the same portal does not check what the first door checks.
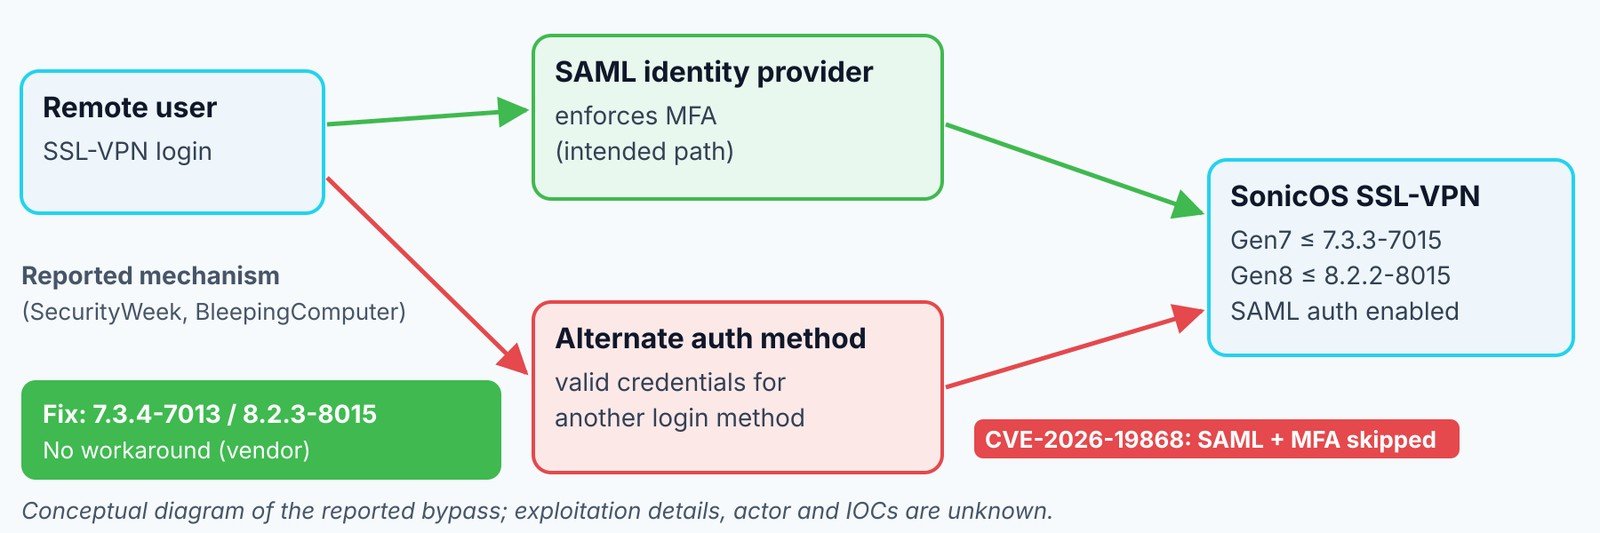
Much is still unknown: who exploited the flaw, how widely, where attackers obtained alternate-method credentials, and any indicators of compromise. None were published in the sources we reviewed, and no source links this flaw to ransomware. SSL-VPN is nonetheless one of the most common initial-access routes, which is why the fix should not wait.
Que rechercher
If SAML SSL-VPN is enabled, review recent VPN sessions that authenticated through a method other than SAML, and check what those sessions reached. SonicWall’s own detection guidance and the GUI path for confirming the SAML configuration are in its PSIRT advisory, which we could not retrieve at press time (SonicWall PSIRT SNWLID-2026-0014); read it before you act. We are not reproducing menu paths or commands we could not verify.
Investigate, contain and fix
- Inventory every SonicWall firewall on Gen7 7.3.3-7015 or older and Gen8 8.2.2-8015 or older, and flag those with SAML SSL-VPN enabled.
- Upgrade those first to 7.3.4-7013 or 8.2.3-8015, then the rest of the fleet. There is no workaround.
- Restrict the management interface to trusted networks, given the 8.8-rated management flaws in the same advisory.
- Where alternate-method VPN logins look suspicious, reset those credentials and review what the sessions accessed (MAG212 CYBER analysis).
How to prioritise a large fleet
Analyse CYBER MAG212 : for MSPs and multi-site schools with dozens of appliances, a simple order of work keeps the riskiest devices first:
| Priorité | Device profile | Action |
|---|---|---|
| 1 | SAML SSL-VPN enabled and management interface reachable from the internet | Upgrade today; restrict management access immediately |
| 2 | SAML SSL-VPN enabled, management restricted | Upgrade today; review alternate-method logins since early November |
| 3 | SSL-VPN without SAML | Upgrade this week for the DoS and management-interface fixes |
| 4 | No SSL-VPN, management restricted | Upgrade in the next maintenance window |
Whatever the tier, note that the federal KEV deadline of 20 November is a ceiling, not a target. SSL-VPN appliances sit at the edge, and edge flaws are typically exploited faster once details circulate.
How to confirm you’re clean
- Every appliance reports a firmware build at or above the fixed version.
- New SSL-VPN sessions on SAML-configured portals show SAML and MFA completion, not alternate-method authentication.
- Any credentials tied to suspicious alternate-method logins have been reset and their sessions ended.
Leçons pour les administrateurs, le personnel et les dirigeants
- Admins: MFA enforced at an identity provider protects only the login paths that actually go through it. Inventory every authentication method enabled on each VPN portal and disable the ones you don’t need.
- Staff: if your VPN login suddenly stops asking for your usual MFA step, report it rather than enjoying the shortcut.
- Dirigeants : ask for a single list of remote-access paths and the MFA each one enforces. Gaps like this are invisible until someone writes them down.
Ce que nous ignorons encore
- Who is exploiting CVE-2026-19868, and against how many organisations.
- Whether the six other flaws in the advisory are being exploited.
- SonicWall’s detection guidance and any indicators, pending direct review of the PSIRT page.
Sujets connexes sur MAG212 CYBER
- SonicWall VPN flaw now exploited (MAG212 CYBER Daily, 7 November 2026)
- MAG212 CYBER Quotidien, 10 novembre 2026
Sources
- SonicWall PSIRT SNWLID-2026-0014 (not retrieved at press time)
- BleepingComputer: SonicWall warns of new SSL-VPN MFA bypass (6 Nov 2026)
- SecurityWeek: SonicWall patches exploited SonicOS bug (7 Nov 2026)
- The Hacker News: CISA flags SonicWall SonicOS MFA bypass (9 Nov 2026)
- CISA KEV catalog, v2026.11.09
- Oflight vulnerability digest (7 Nov 2026)