
European Commission Confirms an “AI Generated” Cyber Campaign: What Is Confirmed, What Is Only Reported
De la part de MAG212 CYBER Daily, 20 November 2026. Chaque commande est copiée de la documentation officielle ou de l'analyse citée et a été non testé par MAG212; exécutez-le uniquement sur les systèmes que vous êtes autorisé à administrer.
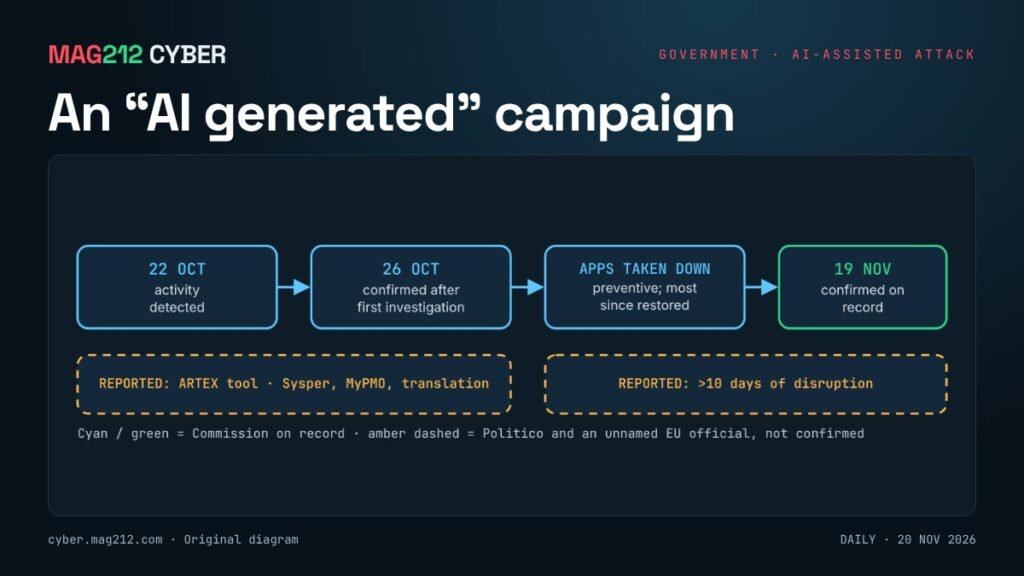
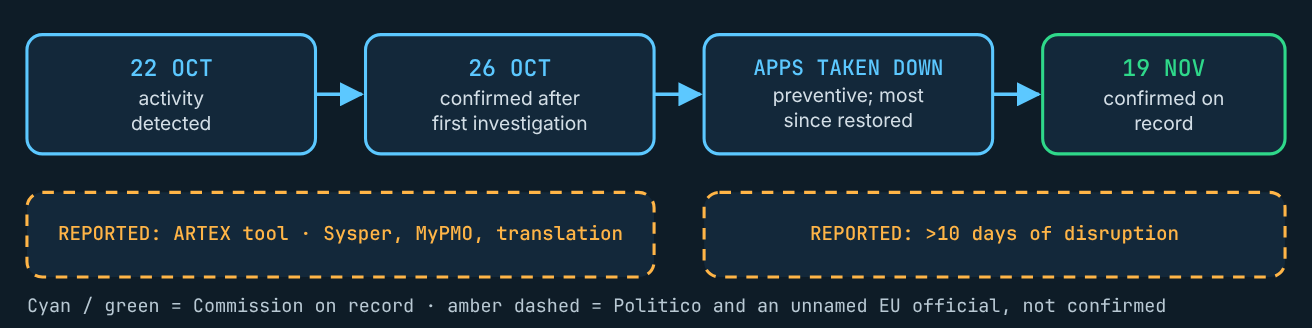
Statut: Confirmed on 19 November 2026 by Commission spokesperson Thomas Regnier at the midday press briefing. Detected 22 October, confirmed 26 October. Several applications were taken down as a precaution; most are restored. No attribution, no ransom demand known, and no evidence so far of a data breach “affecting Commission staff as a whole”. The tool name (ARTEX) is reported, not confirmed. [1][2][3]
Ce qui s'est passé
At the briefing in Brussels, Regnier said “we can confirm that this was an AI generated cyber campaign” involving “a misuse of an AI tool” that is publicly available, as reported by Help Net Security. The activity was detected on 22 October and confirmed on 26 October after an initial investigation. The Commission then “temporarily took down several applications” as a protective measure, and most have since been restored. [1][2][3]
Pourquoi c'est important
This is one of the first times a major government body has said on record that an attack against it was AI-generated. Agencies and vendors now plan for attackers who can scan, exploit and move faster with AI help. Whatever tool was used here, the practical effect is the same: shorter windows between exposure and compromise. (Analyse MAG212)
What is confirmed
- The campaign was described as “a series of incidents”. Regnier said “many elements” have been contained but would not say whether the attack is over. [3]
- At this stage, the Commission has “not detected any evidence of a data breach affecting Commission staff as a whole”. That careful wording does not rule out access to some individual records. [3]
- No ransom demand is known, and the Commission declined to attribute the attack. [2][3]
- The Commission is in close contact with CERT-EU and the European Data Protection Supervisor. [3]
- Regnier did not name the tool, the services targeted or the attack method. [3]
What is only reported
- The tool. Politico, citing an EU official, reported that CERT-EU saw the attackers use ARTEX, an AI-powered penetration-testing framework. SecurityWeek notes this is not confirmed. [2][3]
- The services. Reports name Sysper (HR: salaries, timesheets, leave), MyPMO (medical reimbursement) and translation systems. [2][4]
- The duration. Politico reported more than ten days of disruption. [2]
About ARTEX
Two recent documents describe ARTEX, but neither mentions the Commission. [5][6]
- An FBI FLASH advisory, reported by BleepingComputer on 15 November, says criminal and state-aligned actors have abused ARTEX since at least August 2026, sometimes going from first targeting to privileged access in under three hours. It describes ARTEX as a Go-based autonomous penetration-testing framework that connects to commercial large language models. [5]
- Google’s GTIG AI Threat Tracker of 16 November lists ARTEX among autonomous multi-agent offensive frameworks seen in real activity. [6]
Any link between ARTEX and the Commission rests on the unconfirmed report.
A difficult year for the Commission
Computing notes this is not the Commission’s first incident of 2026: a mobile-device management incident in January, and a cloud breach in March that CERT-EU traced to a compromised Trivy supply chain. [4][7]
What defenders can take from it
- Assume shorter timelines. If AI-assisted tools can chain discovery and exploitation, internet-facing systems need patching in days, not weeks.
- Watch for breadth. Alert on one source probing and exploiting many applications in a short window.
- Do not overread the label. “AI generated” does not mean “autonomous”; no public evidence shows how much a human steered this campaign.
(Analyse MAG212)
Sujets connexes sur MAG212 CYBER
- MAG212 CYBER Daily, 20 November 2026: The keys to vSphere (numéro complet et PDF)
- MAG212 CYBER Quotidien, 19 novembre 2026 : Un compteur vieux de dix ans
- MAG212 CYBER Quotidien, 18 novembre 2026 : Un signe égal de trop
- MAG212 CYBER Hebdomadaire, 14 novembre 2026
- Abonnez-vous gratuitement à MAG212 CYBER
Sources
- [1] European Commission, “Midday press briefing (video I-298222)“, 19 novembre 2026.
- [2] SecurityWeek, “European Commission confirms AI-assisted cyberattack disrupted services“, 20 Nov 2026.
- [3] Aide à la sécurité réseau, “European Commission: AI-generated cyberattack used publicly available tool“, 20 Nov 2026.
- [4] Computing, “European Commission hit by AI-assisted cyberattack“, 20 Nov 2026.
- [5] BleepingComputer, “FBI warns ARTEX AI hacking tool is powering global cyberattacks“, 15 novembre 2026.
- [6] Google GTIG, “AI Threat Tracker: agentic threat activity crosses a significant threshold“, 16 novembre 2026.
- [7] CERT-EU, “European Commission cloud breach: a supply-chain compromise“, 2 Apr 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 20 November 2026, 6:00 AM PT.