
Deadline Day: PHP2Shell, Ivanti, a Poisoned Extension & GitLab: MAG212 CYBER Daily Edition, 1 November 2026
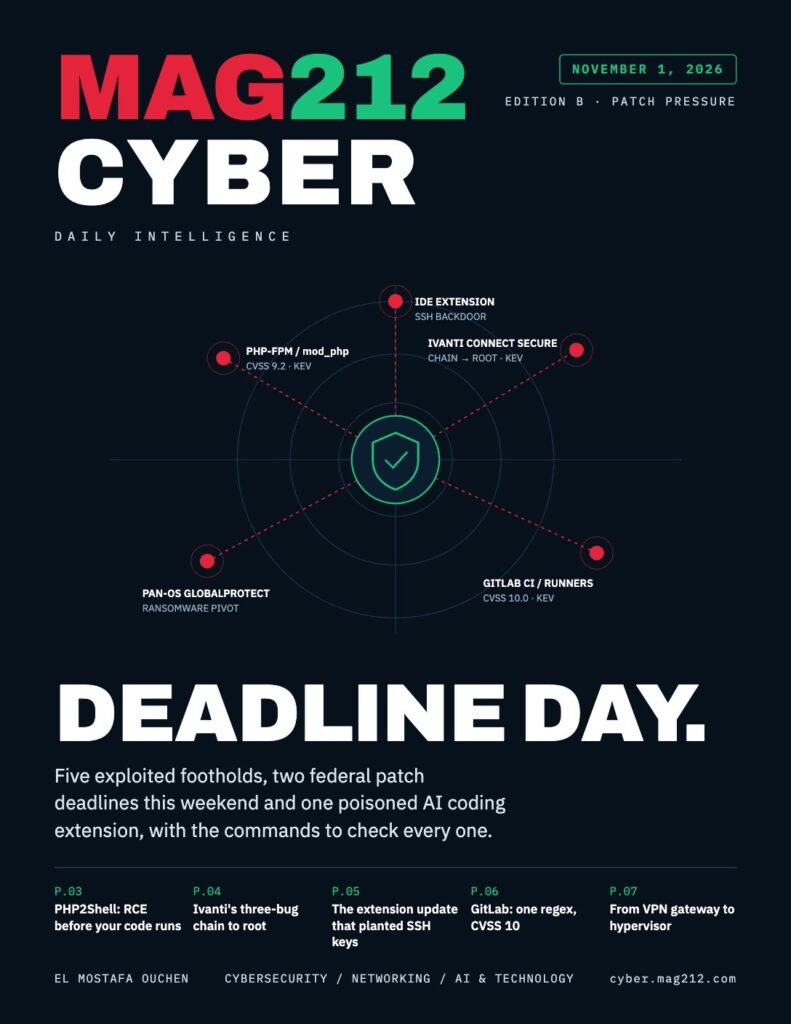
Deadline day: the federal remediation deadline for GitLab CVE-2026-97229 is today and Ivanti’s falls tomorrow, PHP2Shell is under active exploitation, and a trojanized Claude Code extension pushed SSH backdoors to developer machines. This companion edition covers five exploited footholds with attack-path diagrams, fixed versions and read-only check commands for Linux, macOS, Windows, PAN-OS and ESXi.
What needs attention today
| Story | ID | Severity | Exploited | Action |
|---|---|---|---|---|
| PHP2Shell (PHP runtime) | CVE-2026-109618 / 109619 | CVSS 9.2 | Yes, CISA KEV (26 Oct) | PHP 8.2.35 / 8.3.36 / 8.4.27 / 8.5.12, then restart every worker |
| Ivanti Connect Secure chain | CVE-2026-104935 / 111357 / 118527 | 8.6 / 8.8 / 4.3 | Yes, CISA KEV; federal deadline 2 Nov | Upgrade to 25.1.1.3 or 22.8R2.6 (no workaround) |
| Trojanized Claude Code extension (Cursor marketplace) | No CVE | High | Yes, 29 Oct; up to 5,000 users | Hunt for 2.1.312 / 2.1.313; remove key, startup item and tunnel |
| GitLab CI regex RCE | CVE-2026-97229 (+ CVE-2026-110264) | CVSS 10.0 | Yes, CISA KEV; federal deadline 1 Nov | Latest patch: 19.5.3 / 19.4.5 / 19.3.7 / 19.2.10 (21 Oct builds 19.5.1 / 19.4.3 / 19.3.6 / 19.2.9 are the minimum) |
| PAN-OS GlobalProtect | CVE-2026-0257 | CVSS 9.1 | Yes, Qilin and Inc ransomware | Confirm May fixes; dedicated Authentication Override certificate |
Inside this edition
- Today at a glance: KEV deadline board, CVSS chart and a weekend patch order.
- PHP2Shell: how an out-of-memory crash path becomes a shell, exposure by SAPI, and interim FPM hardening.
- Ivanti Connect Secure: the three-bug chain to root, a timeline back to 3 October, and a SIEM hunt for the X-DSCGI-PATH header.
- The extension update that planted SSH keys: payload sequence, affected sources and triage commands for macOS, Linux and Windows.
- GitLab: one regular expression, CVSS 10, why the 12 October builds are not enough, and what to rotate.
- From VPN gateway to hypervisor: the PAN-OS to vCenter to ESXi path, the PoC log fingerprint, and the execInstalledOnly check.
Flip through the edition
How we report: every story was checked against vendor advisories, CISA and named research teams on 1 November 2026, with secondary reporting used where primary pages were unavailable. Diagrams are schematic illustrations, not indicators of compromise, and console panels are illustrative layouts. Commands are proposed read-only checks, not tests run by MAG212 on affected systems. Advisories and fixed versions change, so verify with the vendor before acting. Corrections and tips: consultant@mag212.com.