
The Edge, the Cloud & the Code: MAG212 CYBER Daily Edition, 29 October 2026
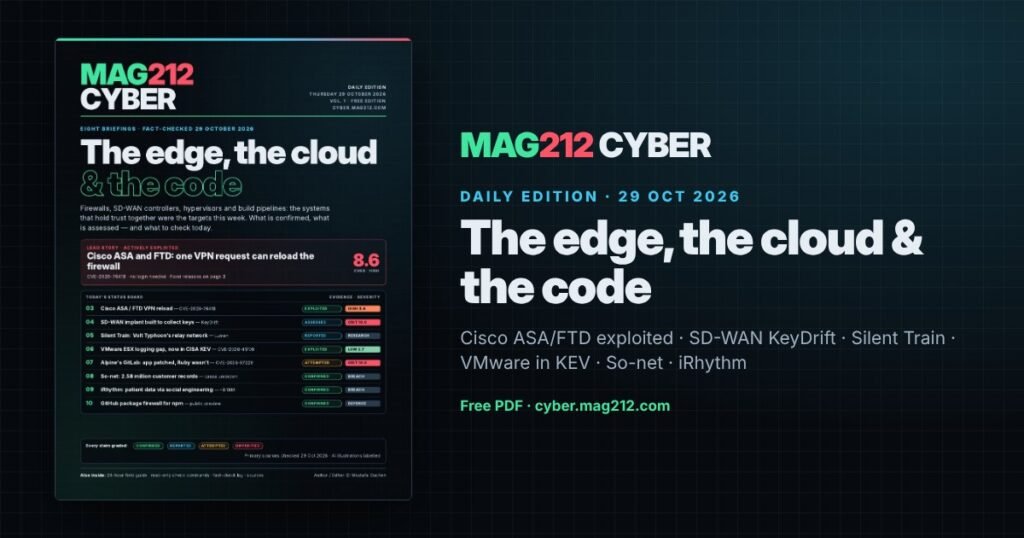
Firewalls, SD-WAN controllers, hypervisors and build pipelines: the systems that hold trust together were the targets this week. Today’s edition covers eight stories, each graded by how strong the evidence is, with fixed versions, read-only check commands and a 24-hour response plan.
What needs attention today
| Story | Status | Severity | Do this today |
|---|---|---|---|
| Cisco ASA/FTD SSL VPN reload (CVE-2026-76418) | Exploited | High 8.6 | Check for secondary authentication on any tunnel group, then upgrade to the fixed release |
| Cisco SD-WAN KeyDrift implant (CVE-2026-20127) | Assessed | Critical 10.0 | Confirm controllers run fixed releases; hunt for the listed artifacts |
| Silent Train, Volt Typhoon’s relay network | Reported | Research | Inventory internet-facing management platforms and who can reach them |
| VMware ESX logging flaw (CVE-2026-41709) | Exploited (CISA KEV, 28 Oct) | Low 2.7 | Patch the right branch; confirm logs reach a protected collector |
| Alpine GitLab: app patched, Ruby wasn’t (CVE-2026-97229) | Attempted | Critical 10.0 | Check the Ruby inside every GitLab image you run |
| So-net: 2.58 million customer records | Confirmed | Breach | Affected users: expect convincing phishing; follow the official notice |
| iRhythm: patient data via social engineering | Confirmed | Breach | Patients: consider a fraud alert or credit freeze; review insurance statements |
| GitHub package firewall for npm | Confirmed | Defence | Enterprise Cloud teams: pilot it on one CI workflow |
Inside the edition
- Cisco ASA and FTD: an unauthenticated request to the SSL VPN can reload the firewall when secondary authentication is configured on any tunnel group, including DefaultWEBVPNGroup. Cisco confirms active exploitation. MFA does not help; the fixed-release table is on page 3.
- Cisco SD-WAN KeyDrift: Cisco Talos dissects an implant planted on controllers through a flaw disclosed in February. It was built to collect IPsec key material; Talos does not report confirmed exfiltration. Talos links the group’s infrastructure to Silent Train.
- Silent Train: Lumen’s Black Lotus Labs maps Volt Typhoon’s disposable relay chains and at least four zero-days in management platforms.
- VMware ESX: a CVSS 2.7 logging flaw that CISA added to its Known Exploited Vulnerabilities catalog on 28 October, and why the same advisory needs a second update for CVE-2026-47876.
- Alpine’s GitLab: how upgrading GitLab left a vulnerable Ruby behind, and how to check your own images.
- So-net and iRhythm: what was confirmed, what remains unknown, and what affected customers and patients should do now.
- GitHub package firewall: a policy gate in front of npm installs for developers, CI and coding agents.
- Field guide: a 24-hour plan, read-only check commands by product, a fact-check log and 17 clickable primary sources.
Read it here
How we report: every story was checked against vendor advisories, filings and named research on 29 October 2026. Incident and reporting dates are given separately, and unknown causes stay unknown. Story banners are AI-generated conceptual illustrations, labelled as such. Advisories and fixed versions change, so verify with the vendor before acting. See our editorial policy. Corrections and tips: consultant@mag212.com.