
Barracuda CVE-2026-116606 and CVE-2026-111560: From Admin Interface to Root, and the Patch for Each Product
Barracuda has patched two flaws that, chained together, let an attacker who can reach an appliance’s admin interface run commands as root. CVE-2026-116606 affects the Email Security Gateway (ESG). CVE-2026-111560 affects six Barracuda products. No exploitation has been reported, but the first fix doesn’t need a patch: take admin interfaces off untrusted networks.
Key facts
| Item | Detail |
|---|---|
| Advisory | Barracuda, “Pre-Authentication Authorization Bypass and Command Injection”, November 2, 2026 |
| CVE-2026-116606 | CVSS 4.0 9.3 (CWE-288); ESG before 9.4.0.030; config import accepts a crafted backup (Mandiant MNDT-2026-0042) |
| CVE-2026-111560 | CVSS 4.0 8.6 (CWE-78); OS command injection via the timezone setting, runs as root (Mandiant MNDT-2026-0041) |
| Chained impact | Authorization bypass to root access, per Barracuda |
| Exploitation | None reported in sources we checked; no KEV listing found |
| Alerts | ThaiCERT (Nov 5); Canadian Cyber Centre AV26-1112 |
How the chain works
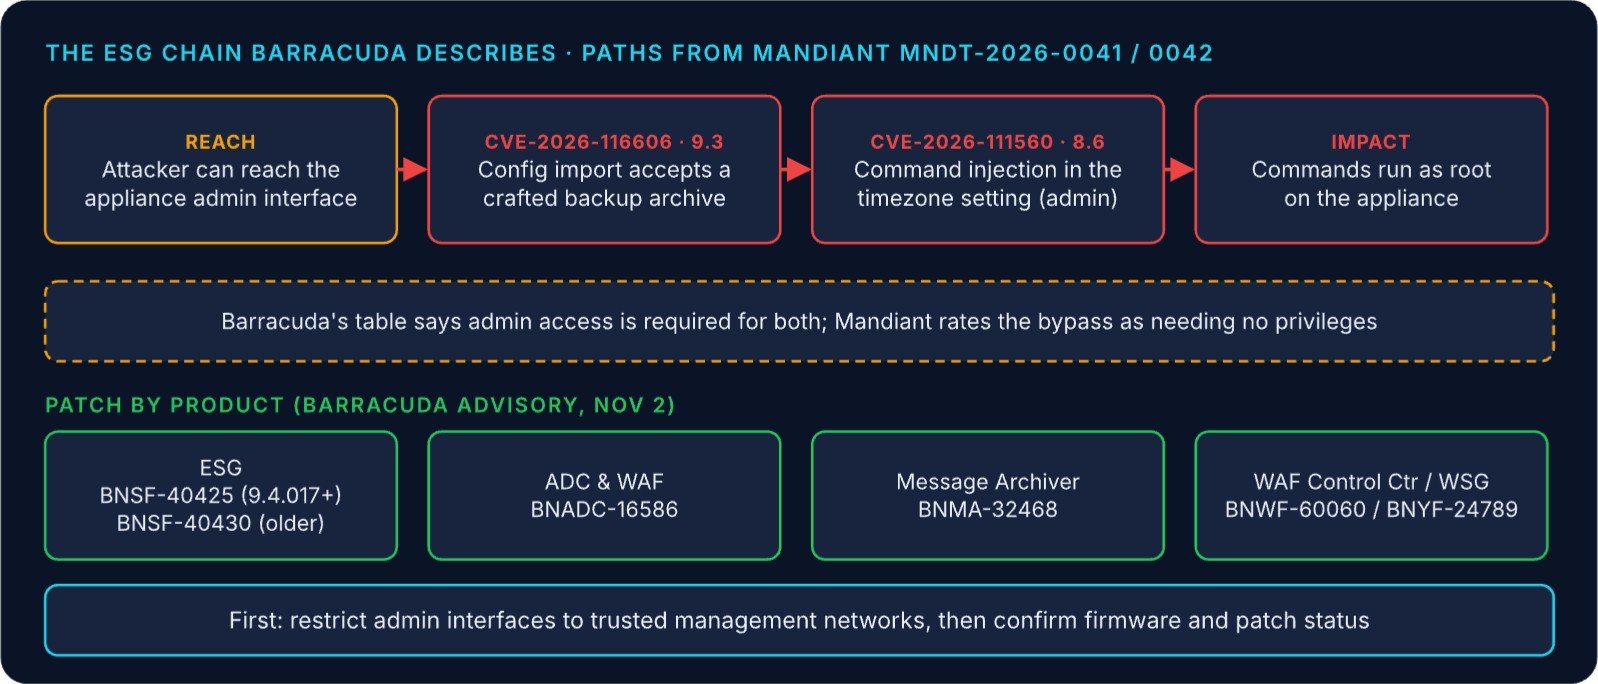
Mandiant’s advisory for CVE-2026-116606 says an unauthenticated attacker can reach ESG’s configuration-import function and restore a crafted backup archive. Its advisory for CVE-2026-111560 says an administrator-level attacker can inject operating-system commands through the timezone configuration field, and those commands run as root. Barracuda says that, chained, the flaws let an attacker “bypass authorization controls and obtain root access to the device.”
One conflict to know about: Barracuda’s own table says “Administrative access required” for both CVEs and labels both “High”. Mandiant rates the bypass as needing no privileges, and the CVE record rates 9.3 as Critical. In both readings, the attacker has to be able to reach the admin interface.
Affected products and patches
| Product | CVE-2026-111560 vulnerable up to | Patch |
|---|---|---|
| Email Security Gateway | 9.4.0.27 (and CVE-2026-116606 before 9.4.0.030) | BNSF-40425 (firmware 9.4.017 and later) or BNSF-40430 (older) |
| Load Balancer ADC | 6.4.0 | BNADC-16586 |
| Web Application Firewall | 11.0.1 | BNADC-16586 |
| Web Security Gateway | 16.1.100.100 | BNYF-24789 |
| Message Archiver | 5.5.4.0 | BNMA-32468 |
| WAF Control Center | 2.2.1 | BNWF-60060 |
Versions are from the CVE record and Mandiant; the Canadian Cyber Centre lists the same numbers as “prior to”. Version formats differ between sources, so confirm your build with Barracuda Support.
What to do, in order
- Restrict admin interfaces to trusted internal management networks. This is Barracuda’s first recommendation.
- Confirm the firmware is current, then apply the patch for each product. If automatic patching didn’t apply it, install it manually and turn auto-patching on.
- Devices several versions behind may need more than one update; Barracuda says to contact support.
- If root access is suspected, preserve evidence with vendor support before rebuilding, then rotate secrets the appliance held.
- Verify patch status on every node, standby units included. Confirm the admin UI is refused from untrusted zones and that mail flow, load balancing or archiving works normally.
What to look for
- Which networks can reach each appliance’s admin UI, tested separately from mail or web traffic.
- Configuration imports or restores, timezone changes and new administrators that don’t match maintenance records.
- Unexpected outbound connections or processes on the appliance. Ask Barracuda Support for diagnostics.
Scheduled restores and configuration pushes leave the same traces, so check change records before escalating.
Frequently asked questions
Is the Barracuda chain being exploited?
No source we checked reports exploitation, and we found no CISA KEV listing. That can change quickly for email gateways, so patch now.
Do I need to patch if my admin interface isn’t public?
Yes. Restricting access lowers the risk, but anyone who can reach the interface, including from inside the network, can attempt the chain.
Which ESG patch do I need?
BNSF-40425 for firmware 9.4.017 and later; BNSF-40430 for older firmware.
Sources
- Barracuda: Pre-authentication authorization bypass and command injection (Nov 2)
- Mandiant MNDT-2026-0042
- Mandiant MNDT-2026-0041
- ThaiCERT alert (Nov 5)
- Canadian Centre for Cyber Security AV26-1112
Related coverage on MAG212 CYBER
- The Patch That Didn’t Hold: MAG212 CYBER Daily, 5 November 2026
- Zyxel GS1900 Zero-Day: Why the June Patch Didn’t Hold
- Crafty Falcon: CERT-In Warns of AI-Assisted Attacks on Payment Firms
- AI Developer Platform Breaches: Rotate the Keys You Stored
- Rails Active Storage: Upgrade, Then Rotate Your Secrets
- Android CVE-2026-58868 and Chrome 157: November’s Patch Load
- Every issue in the Magazine Library