
CISA Gives Three Days to Fix Exploited FreeSWITCH, GPUStack and IBM Aspera Faspex Flaws
On 9 November CISA added four actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog and gave federal agencies just three days, until 12 November, to fix them. One is the OpenSSH “sshole” bypass. The other three hit very different corners of the network: the FreeSWITCH telephony engine, the GPUStack AI model-serving platform and IBM Aspera Faspex file transfer. All four carry a forensic-triage requirement, so CISA expects agencies to look for compromise, not just patch (CISA KEV).
| Product | CVE | Affected | Fixed in | CVSS |
|---|---|---|---|---|
| SignalWire FreeSWITCH | CVE-2026-116779 | 1.11.2 and earlier | 1.11.3 | 9.8 (reported) |
| GPUStack | CVE-2026-102895 | Before 2.2.0 | 2.2.0 (2.2.2 recommended) | 9.8 (reported) |
| IBM Aspera Faspex | CVE-2026-123218 | 5.0.0 to 5.0.19 | 5.0.19 PL1 | 9.8 (IBM; see conflict below) |
All three: added to KEV 9 Nov 2026, federal due date 12 Nov 2026, forensic triage required. CVSS scores were not verified against NVD.
Why the clock is so short
Each required action in the catalog cites CISA’s BOD 26-04 on prioritising security updates by risk, together with forensic-triage requirements (CISA KEV). MAG212 CYBER analysis: the three-day deadline appears to go with the forensic-triage flag under that directive; we could not read the directive text itself to confirm. For non-federal organisations, the signal is the same: these are being exploited now.
FreeSWITCH: a chat message that runs commands
CISA’s entry says the flaw permits configuration and credential disclosure, arbitrary call control and command execution (CISA KEV). According to SecurityOnline, which summarises the FreeSWITCH advisory of 28 October, an inbound SIP MESSAGE can reach the “api” chat protocol handler and run commands with the server’s privileges. Chat is on by default for internal and external profiles, authenticating a MESSAGE needs only one account on the profile, and older sample configurations include a directory user with no password. The advisory states that exploitation of this path has been observed in the wild (SecurityOnline). Two companion flaws, CVE-2026-116785 and CVE-2026-116790, are not reported as exploited.
Look for: unexpected SIP MESSAGE traffic and API activity in FreeSWITCH logs. Fix, in order:
- Upgrade to FreeSWITCH 1.11.3.
- Keep
enable-chat-api-protooff (the default). - Set
enable-chat=falseon profiles that don’t need SIP chat. - Remove directory users that have no password.
- Set
ice_verify_message_integrity. - Leave mod_xml_rpc
enable-websocketunset.
These are configuration settings reported by SecurityOnline; we could not retrieve the vendor advisory itself (GHSA-mg63-h38w-8p9p). We also don’t know which commercial PBX products embed a vulnerable FreeSWITCH, so ask your VoIP vendor directly.
GPUStack: admin access by pretending to be localhost
CISA describes unauthenticated administrative access that leads to persistent admin API keys, disclosure of worker and cloud-provider secrets, and code execution through a backend-creation endpoint (CISA KEV). SecurityOnline reports that builds before 2.2.0 trust requests from loopback as admin because force_auth_localhost defaults to false; an attacker can get there through a same-host reverse proxy or by spoofing the X-GPUStack-Real-IP: 127.0.0.1 header. Exploitation was reported against version 2.1.1, with attackers creating custom backends to launch reverse shells (SecurityOnline).
Fix: upgrade to 2.2.2 or later, which also closes a related SAML bypass (CVE-2026-102894, not reported as exploited). If you can’t upgrade immediately, the reported workarounds are to set force_auth_localhost=true, strip the X-GPUStack-Real-IP header at your proxy and block /auth/saml/callback. MAG212 CYBER analysis: because the flaw exposes cloud-provider and worker secrets, rotate those credentials on any instance that was reachable, even after patching.
IBM Aspera Faspex: patch as if no login is needed
IBM’s bulletin covers Faspex 5.0.0 through 5.0.19, fixed in 5.0.19 PL1, with no workarounds; after patching, the faspex-core image should report version 5.0.19 with Fix Pack 1. The bulletin does not mention exploitation; the KEV listing is the only exploitation evidence we have (IBM bulletin).
Conflict to note: IBM scores the flaw 9.8 with a vector that says no privileges are required, yet both IBM’s description and CISA’s entry say an authenticated user can craft a message to bypass authorisation and escalate privileges (IBM; CISA KEV). Until IBM clarifies, we recommend treating it as if no login is needed and patching internet-facing Faspex servers first.
Investigate, contain and fix
- Find every instance of the three products, starting with anything reachable from the internet.
- Patch to the fixed versions above, or apply the reported workarounds as a stopgap.
- Look for signs of prior compromise: unexpected admin keys or backends (GPUStack), SIP MESSAGE/API activity (FreeSWITCH), and unexpected privilege changes (Faspex).
- Rotate credentials and secrets the products held, especially cloud keys on GPUStack.
- Record what you checked; CISA’s forensic-triage flag is a reminder that “patched” is not the same as “clean”.
None of the sources supplied shell commands, so none are given here.
Everything else due this week
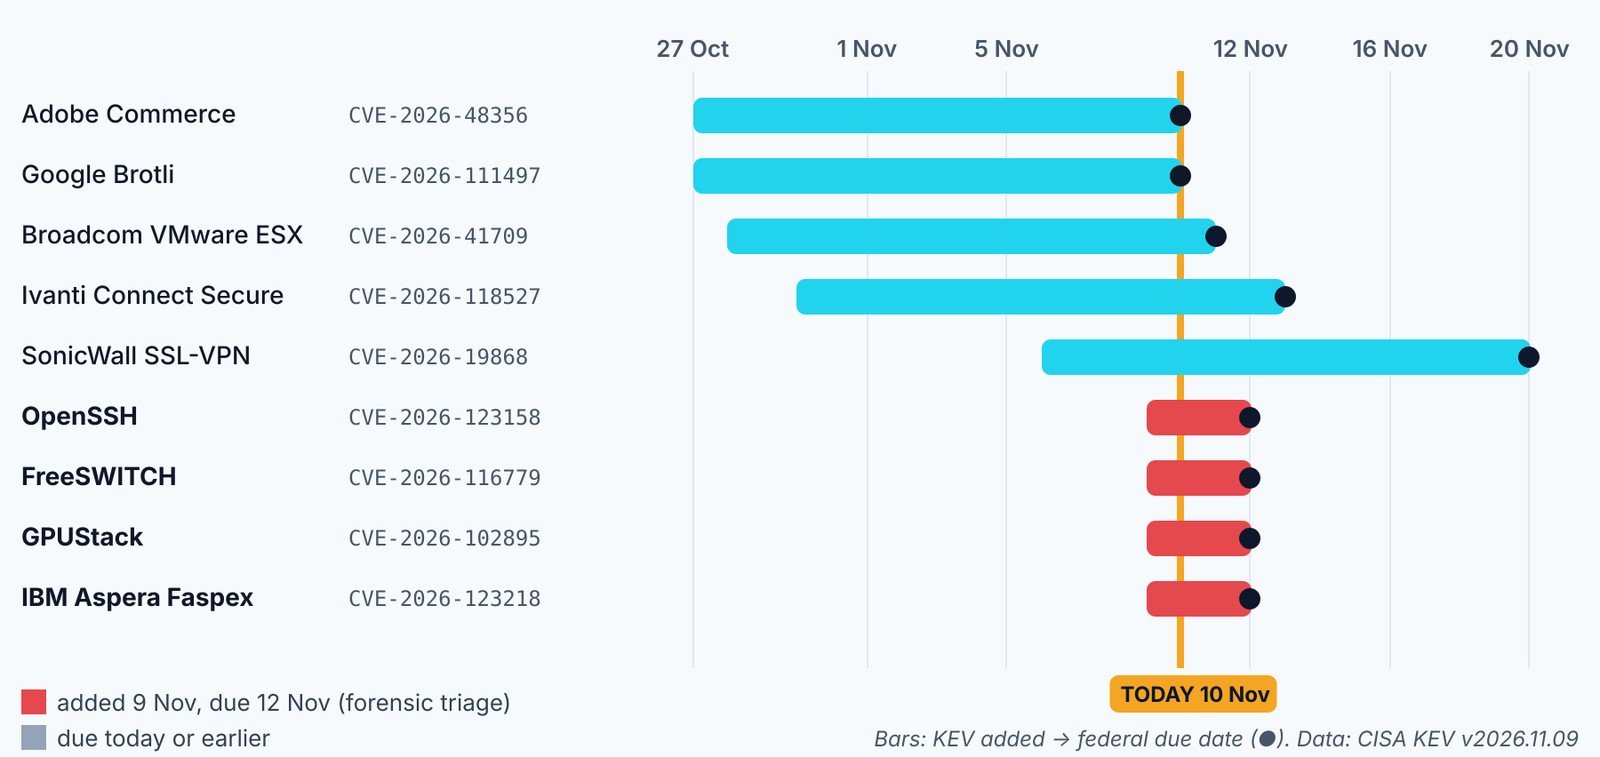
The 9 November batch lands on top of other KEV deadlines. Federal due dates for the coming days, from the catalog (CISA KEV):
| CVE | Product | Added | Due |
|---|---|---|---|
| CVE-2026-48356 | Adobe Commerce | 27 Oct | 10 Nov |
| CVE-2026-111497 | Google Brotli | 27 Oct | 10 Nov |
| CVE-2026-41709 | Broadcom VMware ESX | 28 Oct | 11 Nov |
| CVE-2026-123158 | OpenSSH | 9 Nov | 12 Nov |
| CVE-2026-116779 | FreeSWITCH | 9 Nov | 12 Nov |
| CVE-2026-102895 | GPUStack | 9 Nov | 12 Nov |
| CVE-2026-123218 | IBM Aspera Faspex | 9 Nov | 12 Nov |
| CVE-2026-118527 | Ivanti Connect Secure | 30 Oct | 13 Nov |
| CVE-2026-19868 | SonicWall SonicOS SSL-VPN | 6 Nov | 20 Nov |
Federal deadlines bind US civilian agencies, but they are a useful prioritisation signal for everyone: each entry has evidence of exploitation behind it.
Lessons for admins, staff and leaders
- Admins: default-on features (SIP chat) and default trust (loopback as admin) did the attacker’s work in two of these three cases. Review defaults, not just versions.
- AI platform owners: model-serving tools now hold cloud keys and GPU budgets. Put them behind authentication and never expose admin APIs directly.
- Leaders: a three-day federal deadline is a useful priority signal for everyone. Ask which of these products you run before the 12 November date passes.
What we still don’t know
- Who is exploiting each flaw and how widely.
- Which downstream PBX products embed vulnerable FreeSWITCH.
- Whether IBM’s CVSS vector or its text is correct about authentication.