
FBI Investigates Apparent Hack of NCIC, Its National Crime Database: What Is Confirmed, What Is Not, and What Police IT Should Check Now
From the MAG212 CYBER Daily, 22 November 2026. This article was written with AI assistance and edited by El Mostafa Ouchen. Commands, where included, were not tested by MAG212; run them only on systems you are authorised to administer.
Update, 22 November 2026, 10:00 AM PT: A law enforcement source confirmed to ABC News that the database was hacked; that source is also unnamed, and the FBI has still not commented (ABC7). Director of National Intelligence Jay Clayton told Fox News Sunday he was not in a position to give details about the origin of the hack or whether anything was compromised (AP via WBAL). Separately, Nextgov/FCW reports that the US Department of Agriculture took multiple applications offline after a security incident, affecting tools used for payments to farmers (Nextgov/FCW); no official source links it to NCIC.
Status: Under investigation, unconfirmed by the FBI. Two outlets report the investigation, citing unnamed sources. The FBI declined to comment. No advisory from the FBI or CISA had been published by 7:00 AM PT on 22 November 2026. [1][3]
What happened
On the night of Friday 20 November 2026, CNN reported that the FBI is investigating a hack targeting its criminal justice database, citing two people briefed on the investigation. On Saturday 21 November, the Associated Press confirmed the investigation through one person familiar with the matter who was not authorised to discuss it publicly. [3][1]
The FBI declined to comment to AP and did not respond to requests from CNN or BleepingComputer. BleepingComputer reports that the activity was discovered “in recent days”. SecurityWeek and Forbes carried the story on 21 November without new official detail. [1][2][4][5]
Why this matters
NCIC is not just a store of data; officers make decisions on what it returns. A stolen-vehicle record, an active warrant or a protection order can decide what happens at a roadside stop. If an intruder could read the database, that is a privacy problem. If an intruder could change it, that is a public-safety problem, and every agency that queries NCIC would need to know which records to re-check. (MAG212 analysis)
What is confirmed, and what is not
- Confirmed: the FBI is investigating, according to the sources cited by AP and CNN. The FBI itself has said nothing.
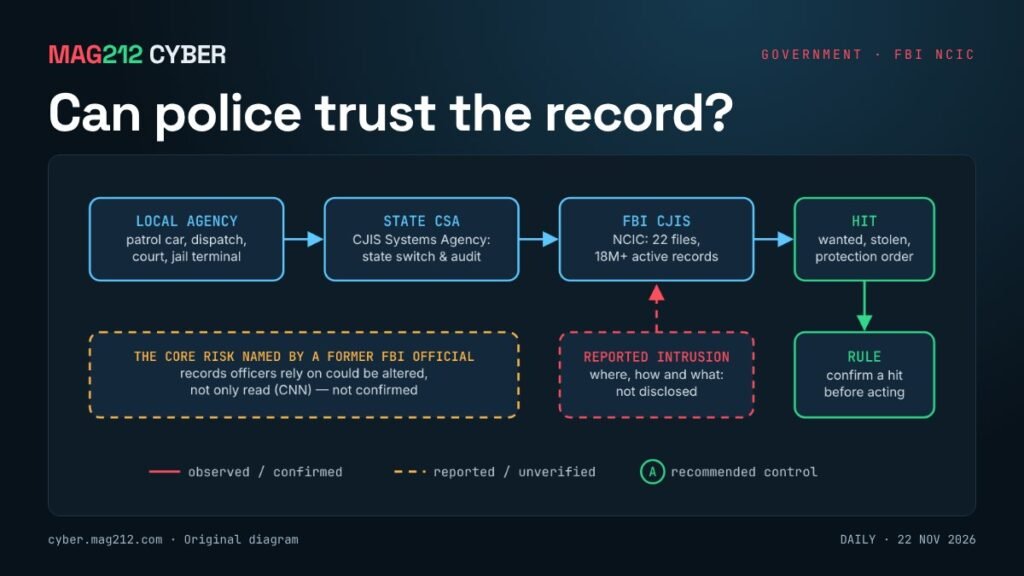
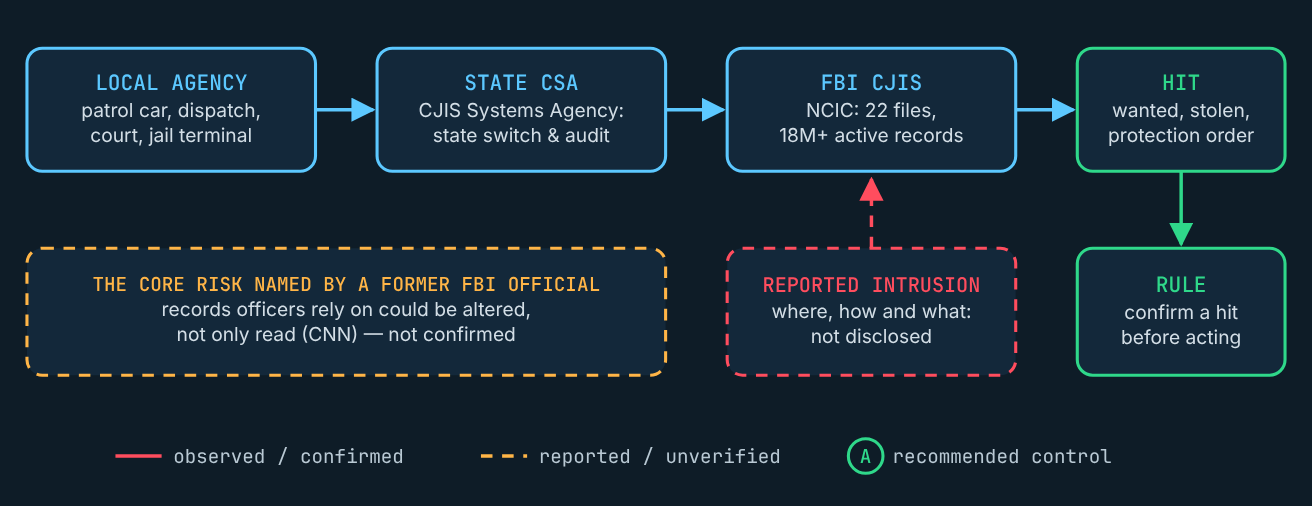
- Reported, not confirmed: that NCIC itself was the target, and the concern, raised by a former FBI official quoted by CNN, that records could have been altered rather than only read. [3]
- Unknown: the entry point, the timing, who did it, whether data was read, copied or changed, and whether state and local agencies are affected. No source links this incident to earlier 2026 incidents at the FBI.
Why NCIC matters
The National Crime Information Center is run by the FBI’s Criminal Justice Information Services (CJIS) Division. It holds files on wanted people, stolen vehicles and property, protection orders and more. FBI figures cited by Forbes put it at 22 files and more than 18 million active records, queried millions of times a day by police, courts and other agencies. [5][6]
A query usually travels from a local agency’s terminal through a state CJIS Systems Agency (CSA) to the FBI and back as a “hit”. NCIC’s rules already require agencies to confirm a hit with the agency that entered the record before acting on it, and each agency is responsible for validating the records it owns. [5]
What police and public-sector IT should check now
You cannot patch an incident that has not been described. You can make sure your own access to criminal justice information (CJI) is tight, logged and checked. These suggestions are MAG212’s, based on the CJIS Security Policy controls summarised by BleepingComputer and the NCIC rules cited by Forbes; audit against the policy text on le.fbi.gov before relying on control numbers. [7][5]
- Multi-factor authentication on every account that can reach CJI, privileged or not, local or remote. Version 6.1 of the policy requires it.
- Query logs. Ask your state CSA for your agency’s NCIC query history. Look for queries outside shift patterns, bulk queries, and unfamiliar terminals or vendor accounts.
- Account review. List every account with CJI access; remove leavers and shared logins.
- Record changes. Review recent entries, modifications and clears on records your agency owns.
- Passwords and scanning. Screen passwords against a compromised-password list updated at least quarterly, and run vulnerability scans at least monthly, as the policy summary describes.
- Hit confirmation. Remind staff that a hit must be confirmed with the originating agency before anyone acts on it.
If you find something: preserve logs first, report through your CSA and the FBI’s CJIS channels, disable affected accounts, rotate credentials and certificates, and re-validate the records you own before officers rely on them.
What to watch next
An FBI or CISA statement, any notice to state CSAs, and any detail on whether records were changed. Until then, treat claims about scope or attribution with caution: none has been confirmed.
Related on MAG212 CYBER
- MAG212 CYBER Daily, 22 November 2026: Can police trust the record? (full issue and PDF)
- MAG212 CYBER Weekly, 21 November 2026: Machine Speed
- MAG212 CYBER Daily, 20 November 2026: The keys to vSphere
- Subscribe free to MAG212 CYBER
Sources
- [1] AP via PBS NewsHour, “AP source: FBI investigating apparent hack of its key national criminal justice database“, 21 Nov 2026.
- [2] SecurityWeek (AP), “FBI investigating apparent hack of its key national criminal justice database, AP source says“, 21 Nov 2026.
- [3] CNN, “FBI hacked again, this time targeting crime database“, 20 Nov 2026.
- [4] BleepingComputer, “FBI reportedly hacked again, this time targeting nationwide police database“, 21 Nov 2026.
- [5] Forbes, “FBI reportedly hacked again: apparent breach hits NCIC crime database“, 21 Nov 2026.
- [6] FBI, “National Crime Information Center (NCIC)“, reference.
- [7] BleepingComputer, “FBI's CJIS v6.1: what security teams need to know“, 25 Jun 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 22 November 2026, 7:00 AM PT.