
Frontline Education Breach Climbs to 3.08 Million School Staff and Students; Amplifon, Revolve Counts Rise
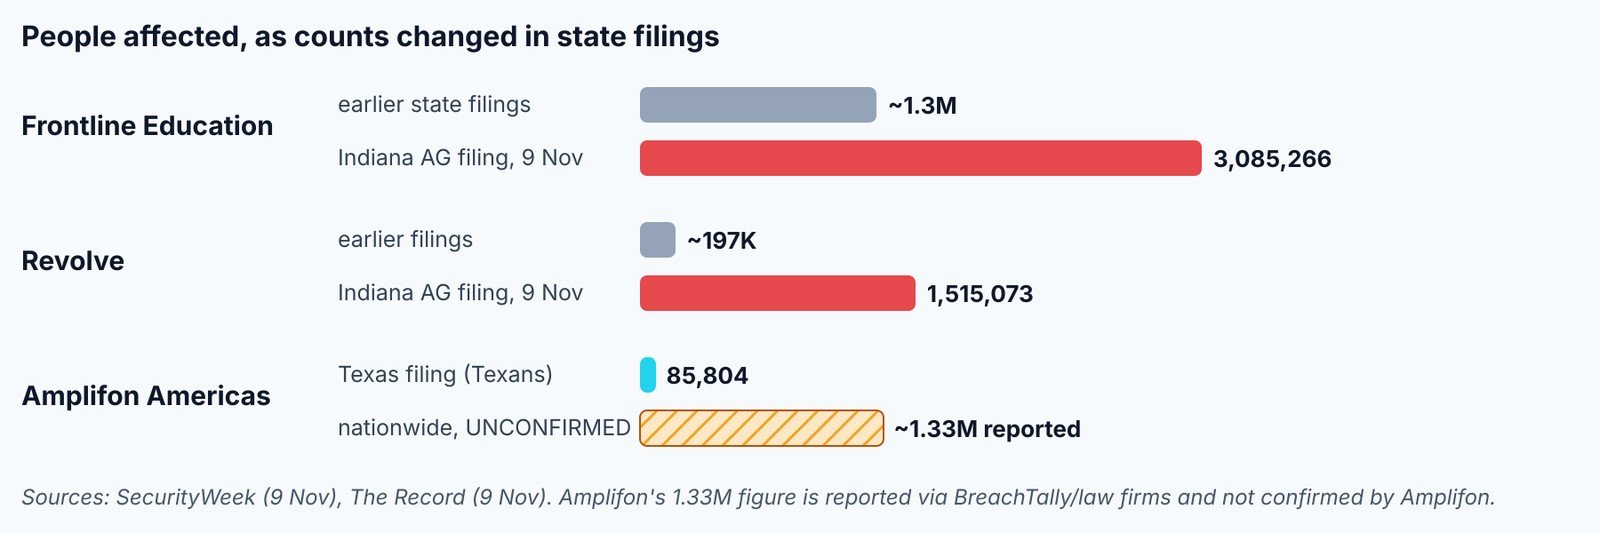
Frontline Education, whose software many US school districts use for HR, staff management and student health records, has told the Indiana Attorney General’s Office that its August breach affected 3,085,266 people. That is more than double the roughly 1.3 million in its earlier state filings (SecurityWeek). The update arrived on 9 November alongside revised counts from hearing-care company Amplifon Americas and fashion retailer Revolve, a reminder that the true size of a breach often emerges weeks or months later in regulator filings.
| Organisation | Frontline Education (K-12 software) |
| People affected | 3,085,266 (Indiana AG filing), up from about 1.3 million |
| Who | School district employees and students |
| Data | Varies: names, SSNs, dates of birth, driver’s licence/passport/government ID numbers, health insurance information (e.g. Medicaid IDs), student IDs |
| Timeline | Detected 14 August 2026; contained the next day, per Frontline |
| Entry point | A vulnerability in an unnamed third-party software product |
| Claimed by | No group has claimed it; not confirmed as ransomware |
What happened at Frontline
According to the reporting, attackers exploited a vulnerability in a third-party product that Frontline has not named, and stole data from Frontline Central and School Health Management. Frontline says it detected the intrusion on 14 August and contained it the next day. It is offering two years of credit monitoring to affected US adults and dark-web monitoring to eligible minors (SecurityWeek). We don’t know which third-party product was exploited.
Amplifon Americas: two very different numbers
Amplifon Americas says attackers copied files between 18 January and 8 February 2026, and that it noticed suspicious activity on 11 February (The Record). The data includes government ID numbers, dates of birth, hearing and medical information and health insurance details, with Social Security numbers and financial information exposed for some people. Amplifon says it is not aware of misuse (SecurityWeek).
The size of the breach is disputed. The Texas filing lists 85,804 Texans, and The Record also cites 1,027 in Vermont (The Record). A nationwide figure of about 1.33 million has been reported by SecurityWeek, sourced through the third-party site BreachTally (BreachTally), but it has not been confirmed by Amplifon (SecurityWeek). The Record attributes that total to class-action law firms and says Amplifon did not respond (The Record).
Revolve: stored payment cards exposed
Revolve told the Indiana Attorney General that 1,515,073 people were affected, up from about 197,000 in earlier filings. The intrusion happened on 11 September and Revolve learned of it on 29 September. Card numbers and expiry dates were exposed for customers who had stored payment methods; how the attackers got in has not been disclosed (SecurityWeek).
Why breach counts keep changing
MAG212 CYBER analysis: all three companies filed different numbers with different states over time. Early filings often cover only the people a company has confirmed so far, or only residents of one state, and the total grows as forensic review of the stolen files continues. That is why a breach first reported as affecting about 1.3 million people can more than double weeks later.
| Organisation | Key dates | Earlier or filed figure | Latest figure |
|---|---|---|---|
| Frontline Education | Detected 14 Aug 2026, contained next day | ~1.3M | 3,085,266 (Indiana AG) |
| Revolve | Intrusion 11 Sep 2026, aware 29 Sep | ~197,000 | 1,515,073 (Indiana AG) |
| Amplifon Americas | Files copied 18 Jan–8 Feb 2026, noticed 11 Feb | 85,804 (Texas filing) | ~1.33M reported, unconfirmed |
For anyone planning communications, the lesson is to describe early numbers as provisional, and to prepare for a second wave of notifications.
Who is affected, and what to look for
None of these incidents has been claimed by a group or confirmed as ransomware, so they are best described as data breaches. Because the compromise happened on the vendors’ side, there are no published indicators of compromise or technical fixes for customers to apply. MAG212 CYBER analysis: the realistic follow-on threat is targeted phishing and fraud that uses the leaked details, aimed at school staff, parents, patients and shoppers.
What school IT teams and affected organisations should do
- Confirm whether your district or organisation has received a notification, and which data types apply to your people.
- Prepare plain-language communications for staff, parents and students.
- Promote the free credit and dark-web monitoring through official channels only.
- Warn staff and families about phishing that quotes real personal details or mentions the breach.
- Ask your SaaS vendors which third-party components they rely on and how quickly they patch them.
These steps are MAG212 CYBER guidance drawn from the reporting, not instructions from Frontline.
Lessons for admins, staff and leaders
- Staff and families: an email that knows your date of birth or employee ID is not proof it is genuine. Reach any monitoring offer through your district’s or employer’s website, never through a link in an unsolicited message.
- IT teams: a breach at a vendor is still your incident to communicate. Keep a contact list and a template ready.
- Leaders: vendor due diligence should cover the vendor’s own suppliers. Frontline’s entry point was a third party’s software.
What we still don’t know
- Which third-party product was exploited at Frontline.
- Amplifon’s confirmed nationwide total.
- How Revolve’s attackers got in, and who is behind any of the three incidents.
Related on MAG212 CYBER
Sources
- SecurityWeek: 3 million people hit by Frontline Education data breach (9 Nov 2026)
- SecurityWeek: Amplifon Americas data breach impacts 1.3 million (9 Nov 2026)
- The Record: Amplifon hearing aid company data breach (9 Nov 2026)
- BreachTally: Texas AG record BR-0005495
- SecurityWeek: Revolve puts data breach victim count at 1.5 million (9 Nov 2026)