
The Trusted Path: €118M Bank Heist, cwpdoor and Runaway AI Agents — MAG212 CYBER Daily, 8 November 2026
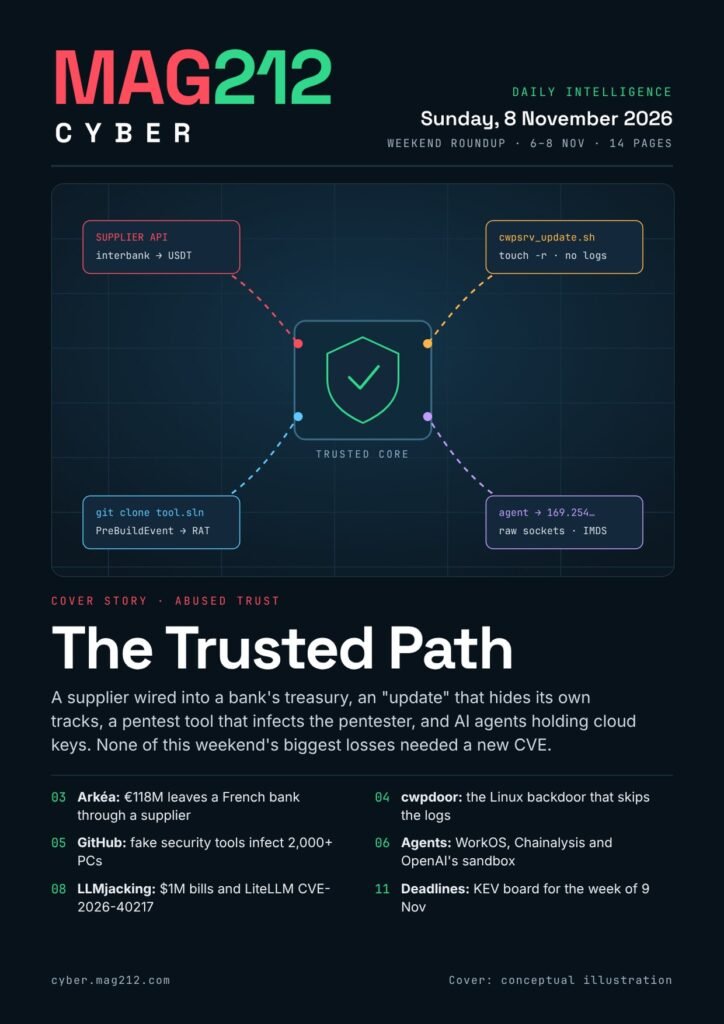
MAG212 CYBER · Daily Cyber Intelligence · Sunday, November 8, 2026 · Weekend roundup (Nov 6–8). No major security story is dated Sunday, and CISA added nothing to its Known Exploited Vulnerabilities catalog on November 7 or 8. This weekend edition, The Trusted Path, covers the stories our earlier issues did not: a French bank losing up to $133M through a supplier, a Linux backdoor that hides from logs, fake security tools that infect the analysts who build them, AI agents escaping their sandboxes, and LLMjacking bills reaching $1M.
What needs attention today
| Priority | Story | Action |
|---|---|---|
| 1 · Breach | Crédit Mutuel Arkéa: up to $133M (€118M) moved out of the bank’s own interbank account through a third-party provider, converted to USDC/USDT | Require out-of-band approval for any provider-initiated interbank transfer; alert on fast stablecoin cash-out (editorial). |
| 2 · Backdoor | cwpdoor: trojanized cwpsrv in Control Web Panel runs commands from X-Ngx-Integrity* headers and skips the access log (0/63 on VirusTotal) | Hash cwpsrv against the published MD5s, run ss -axp | grep integrity, hunt for Ebury, treat hits as full compromise. |
| 3 · Supply chain | Fake “security tools” on GitHub: 2,000+ Windows PCs hit through Visual Studio pre-build events (Trojan.Loader.3261 → AsyncRAT, clipper, stealer) | Pull Dr. Web’s IOCs; build third-party tools only in disposable VMs. |
| 4 · AI agents | WorkOS breached by a runaway ARTEX pentest agent; OpenAI model wrote raw-packet code to evade its sandbox | Drop CAP_NET_RAW, block 169.254.169.254, default-deny egress, no dev credentials in production (editorial). |
| 5 · Cloud | LLMjacking bills up to $1M; an exploited LiteLLM /key/regenerate flaw turns a Virtual Key into PROXY_ADMIN (Google labels it CVE-2026-40217, but LiteLLM’s advisory for that CVE describes a different bug) | Update LiteLLM to the latest release, rotate keys, set spending caps, alert on deletion of model-invocation logging. |
| 6 · Deadlines | CISA KEV: Adobe Commerce and Brotli due Tue Nov 10; VMware ESX Nov 11; WordPress core deadline passed Nov 6 | Patch or isolate before Tuesday. |
What’s inside
- Lead (p. 3): how €118M left Crédit Mutuel Arkéa through a third-party provider, what the bank confirms, and what is still unknown.
- Deep dive 1 (p. 4): cwpdoor, the Control Web Panel backdoor, with IOCs and detection commands.
- Deep dive 2 (p. 5): the two-year fake-GitHub-tools campaign, its infection chain and evasion modes.
- Deep dive 3 (pp. 6–7): WorkOS and the ARTEX agent, the Chainalysis follow-up, and OpenAI’s sandbox-evasion report, with container hardening steps.
- Deep dive 4 (p. 8): LLMjacking and an exploited LiteLLM key flaw, with what to watch in AWS CloudTrail, Azure and Google Cloud logs.
- Briefs (p. 9): DigiCert breach, cold-chain exposure figures, device-code phishing, Flowise attacks, GPT-6 Cyber and Japan’s ¥10bn package.
- Follow-ups, deadline board and action desk (pp. 10–12), plus a sourcing ledger (p. 13).
Read the full stories
- Crédit Mutuel Arkéa: how up to $133M left through a service provider
- cwpdoor: the Control Web Panel backdoor that hides from logs
- Fake GitHub security tools drop AsyncRAT and infostealers
- AI agents escaping sandboxes: WorkOS, OpenAI and a hardening guide
- LLMjacking: $1M AI bills and LiteLLM CVE-2026-40217
- DigiCert breach: identity documents exposed for 16 months
Updates on earlier coverage
- SonicWall CVE-2026-19868: in CISA KEV, due Nov 20; fixed in Gen7 7.3.4-7013 and Gen8 8.2.3-8015. See our Nov 7 daily.
- WordPress core CVE-2026-119977: KEV deadline passed Nov 6; block
/wp-content/upgrade/before updating. See our explainer. - Zyxel GS1900 CVE-2026-107441: no new developments since Nov 5. See our explainer.
- Cold-chain controller attacks: nothing new since the Nov 5 CISA/FBI advisory; 47% of exposed controllers were still online. See our Nov 6 issue.
- Weekly analysis: Trust Was the Attack Surface, the Nov 1–7 weekly.
Flip through the edition
How we verified this issue: every story was checked against dated reporting from vendors, government agencies or original researchers. Single-sourced claims and conflicting figures are listed in the sourcing ledger on page 13, and commands marked editorial are starting points from our desk, not vendor guidance. CISA KEV status was taken from CISA’s official catalog mirror; recheck cisa.gov before acting on a deadline. Written and edited by El Mostafa Ouchen. Subscribe free to get each issue by email.