
Xen Orchestra Auth Bypass (VSA-2026-062) Is Exploited: An Empty-Object Cookie Hands Over XCP-ng Hosts
Xen Orchestra, the web console many MSPs, hosting providers and schools use to run XCP-ng virtualisation, has a critical authentication bypass that is already being exploited. Vates’ advisory VSA-2026-062 explains that a crafted login cookie is parsed into an empty object that the token check accepts. From there an attacker is an Xen Orchestra administrator, can run code across pools and ends up as root on the hosts. There is no CVE yet, and Vates warns that successful exploitation leaves no log entry.
| Advisory | Vates VSA-2026-062 · Critical |
| Fixed | XO 6.9.2 (stable) · 6.10.1 (latest) |
| CVSS | Not available yet |
| Logs | Exploitation leaves none |
What happened
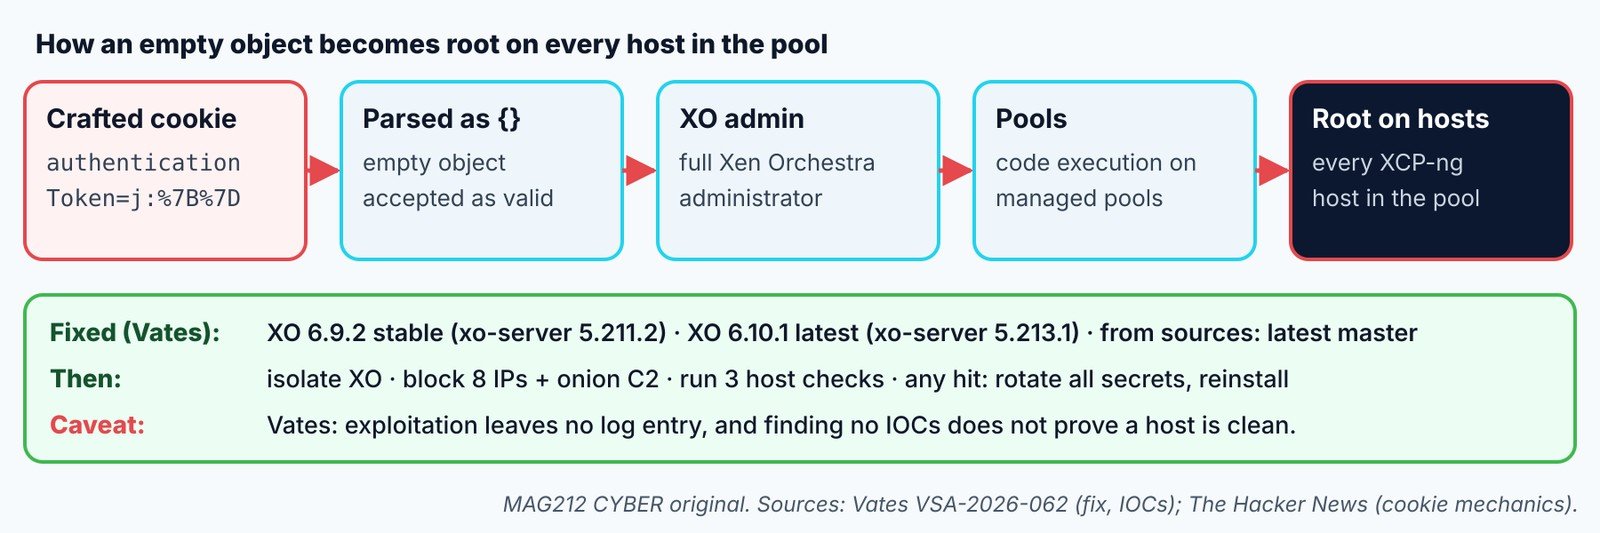
[Confirmed] Vates rates VSA-2026-062, “Empty-object login token”, Critical and says it is being actively exploited by an actor operating initially from 91.211.251.112:8001 and an onion address. There is no CVE yet. (Vates) [Reported] Credited to Filip Magic and Christoffer Olsen (TDC NET Security); THN adds that VirusTotal flags that IP as a RedLine Stealer C2. A crafted cookie, authenticationToken=j:%7B%7D, is parsed into an empty object that the token provider accepts, giving XO admin, then code execution on pools and root on hosts. (The Hacker News) [Unknown] Start date and victim count.
Who is affected
| Install type | Affected | Fixed (vendor) |
|---|---|---|
| Xen Orchestra, stable channel | before 6.9.2 | XO 6.9.2 (xo-server 5.211.2) |
| Xen Orchestra, latest channel | before 6.10.1 | XO 6.10.1 (xo-server 5.213.1) |
| Xen Orchestra Appliance (XOA) | yes | update to the versions above |
| From-sources builds | yes | latest master (PR #10748) |
Source: Vates. Conflict: THN gives 6.9.1 / 6.10.0 with the same xo-server versions; we use the vendor’s figures.
What to look for (vendor IOCs)
| Type | Indicator (all from Vates VSA-2026-062) |
|---|---|
| Request pattern | authenticationToken=j:%7B%7D or j:{} |
| Host artifacts | a VM named pivot2; VMs with hvm_serial: file |
| Files | /etc/cron.d/zz-ustar2, /etc/cron.d/zz-ustar, /.ustar5, /.ustar6 |
| IPs to block | 91.211.251.112 193.148.56.72 37.221.208.216 45.66.35.11 64.65.0.120 64.65.62.160 89.47.51.90 92.60.37.247 |
| Onion C2 | ustar3rqxgnskzgnwkgpofgtvxevm6cx3lxdbwt4mndtveqyaohid.onion:3333 |
Vendor caveat: successful exploitation leaves no log entry, and finding no IOCs does not prove a host is clean. Vates
Host checks
OS: XCP-ng (dom0) · Shell: bash · Privileges: root (MAG212 analysis; vendor doesn't state) · READ-ONLY
# VMs whose platform settings include a file-backed serial port (IOC: hvm_serial: file)
xe vm-list params=name-label,platform | grep -B1 'hvm_serial: file'
# Search current and rotated xensource logs for file-backed serial configuration
zgrep -- '-serial file:' /var/log/xensource.log*
# Preload hijack and the published persistence files
ls -la /etc/ld.so.preload /.ustar* /etc/cron.d/zz-ustar*
Run on every XCP-ng host. Any output naming the IOCs above is a hit; “No such file” for the last command is the expected clean result. Commands not tested by MAG212 CYBER; copied from the Vates advisory.
Contain and remediate (in order, per Vates)
- Take XO off the internet onto a dedicated management network; block the IPs and onion address.
- Upgrade to XO 6.9.2 or 6.10.1 (xo-server 5.211.2 / 5.213.1); from-sources builds to latest master.
- Optional interim WAF or reverse-proxy rule for the token patterns; Vates warns regex rules can be bypassed.
- Run the host checks above on every host.
- If compromised: rotate all secrets (proxy, backup remotes, root, pool secret, users, OTP, mail) and fully reinstall. (Vates)
Verify recovery: confirm the XO version, that the interface is unreachable from untrusted networks, re-run the checks, and confirm rotated secrets are in use. [MAG212 analysis] With no logs, reinstalling is the only high-confidence recovery for a host with any hit. Virtualisation control planes belong on an isolated network, especially for MSPs and schools that chose XCP-ng to save cost.
Why it matters
A virtualisation control plane is a master key: whoever holds it can snapshot, copy, modify or destroy every virtual machine it manages. Organisations that chose XCP-ng to save licence costs often run lean IT teams that publish the console for convenience. Because exploitation is silent, a clean log review proves nothing.
The bottom line
Take Xen Orchestra off the internet now, upgrade to 6.9.2 or 6.10.1, run the vendor’s host checks on every XCP-ng host, and if anything matches, rotate every secret and rebuild rather than clean.
How we label evidence: [Confirmed] comes from a primary source such as a vendor or CISA; [Reported] from a secondary outlet; [Claimed] from an attacker or an unverified party; [MAG212 analysis] is our judgement; [Unknown] means not established at press time. Commands and indicators are copied from the cited sources and were not tested by MAG212 CYBER.
This story is part of MAG212 CYBER Daily, 11 November 2026, with the day’s other verified stories, the Defender’s Action Desk and a full source register. Get the daily briefing free: subscribe to MAG212 CYBER. By El Mostafa Ouchen.