
Heists, Hijacked Scripts & Hostile Regex: MAG212 CYBER Daily Edition, 30 October 2026
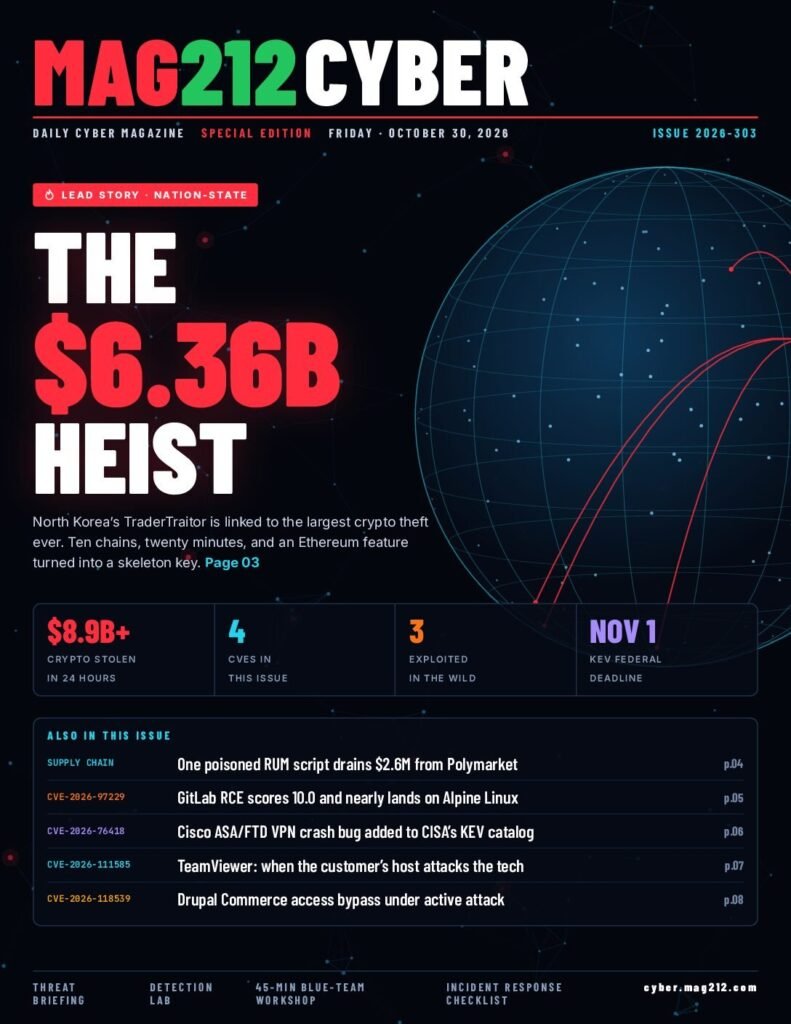
A $6.36 billion exchange heist, a poisoned analytics script and a CVSS 10.0 regex bug: on 29 October, trusted components turned out to be the weak points. Today’s edition covers six stories with attack-chain diagrams, fixed versions, ready-to-run check commands and a 45-minute blue-team workshop.
What needs attention today
| Story | ID | Severity | Exploited | Action |
|---|---|---|---|---|
| Binance hot-wallet theft | No CVE | Critical | Yes, Oct 29; attributed to TraderTraitor (TRM, Chainalysis) | Freeze, re-key signers, monitor EIP-7702 delegations |
| Polymarket RUM script (DebugBear) | No CVE | High | Yes, Oct 29 (about $2.6M) | Remove third-party script, SRI, CSP |
| GitLab / Ruby Onigmo | CVE-2026-97229 | CVSS 10.0 | Yes, CISA KEV | GitLab 19.5.1 / 19.4.3 / 19.3.6+, Ruby 3.3.13 / 3.4.12 / 4.0.9 |
| Cisco ASA / FTD RA-VPN | CVE-2026-76418 | CVSS 8.6 (DoS) | Yes, CISA KEV | Fixed ASA/FTD release, or disable secondary auth |
| TeamViewer viewer | CVE-2026-111585 | CVSS 8.8 | No known exploitation | 15.83 or patched legacy build |
| Drupal Commerce Core | CVE-2026-118539 | Highly critical 21/25 | Yes, per Drupal | 3.3.13 or 8.x-2.41 |
Inside the edition
- Lead: The $6.36B heist. How Binance’s hot-wallet signer was turned against it, why TRM Labs and Chainalysis point to North Korea’s TraderTraitor, and how to watch for EIP-7702 delegations.
- Supply chain: one poisoned monitoring script from DebugBear drained about 700 Polymarket accounts in under an hour.
- DevSecOps: the CVSS 10.0 GitLab/Ruby regex flaw that came close to working against Alpine Linux, and why upgrading GitLab alone wasn’t enough.
- Network edge: the Cisco ASA/FTD VPN crash bug: who is exposed, fixed releases and the Nov 1 KEV deadline.
- Remote access: TeamViewer’s reverse attack, where a malicious host can hit the technician.
- Applications: the Drupal Commerce access bypass under active attack, and how to audit your orders.
- Detection lab: a 45-minute blue-team workshop, four starter hunts and an incident response checklist.
- Sources and fact-check notes: what we verified, and where outlets disagree.
Read it here
How we report: every story was checked against vendor advisories, the affected organisation’s own statements and named research on 30 October 2026. Loss figures are estimates, and attribution is an intelligence assessment, not a court finding. Diagrams are schematic illustrations, not indicators of compromise. Advisories and fixed versions change, so verify with the vendor before acting. Corrections and tips: consultant@mag212.com.