
Security Deadlines to 30 November: Barracuda, Xen Orchestra, eMudhra Distrust and Four Asus Router Flaws
Not every important security story is new today. Several this month come with dates attached, and missing them has consequences: an exploited Barracuda flaw pair whose federal deadline is tomorrow, an exploited Xen Orchestra bypass that still has no CVE number for scanners to find, a certificate authority whose certificates stop being trusted by Microsoft, Chrome, Firefox and Apple over the next three weeks, and four new Asus router flaws, one of which gives a nearby attacker root.
Barracuda: one day left
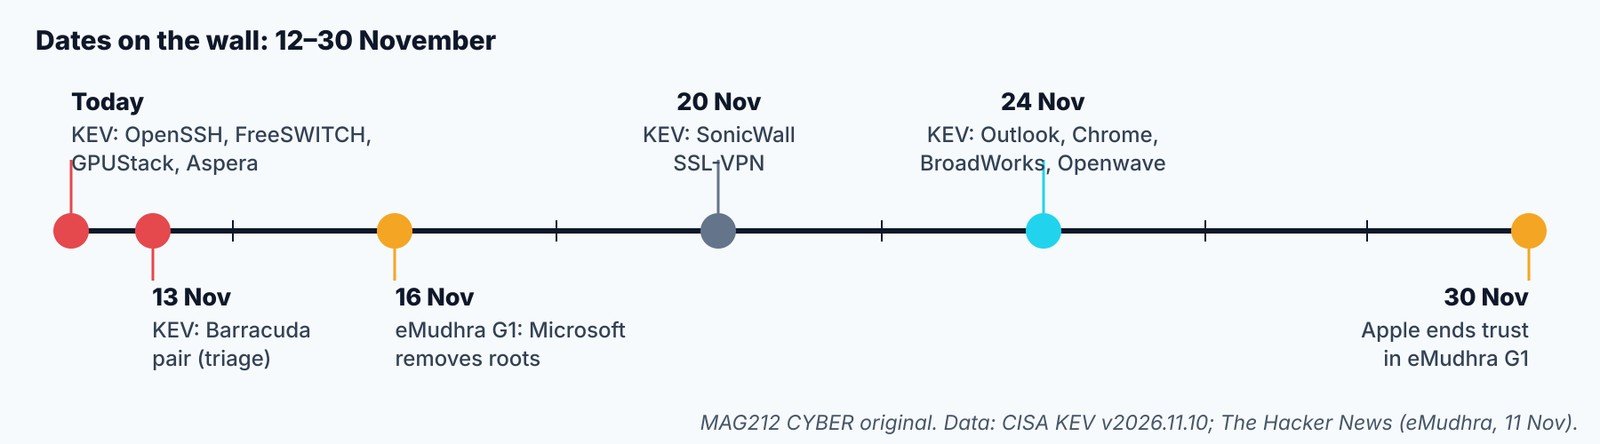
[Confirmed] CVE-2026-116606 and CVE-2026-111560 are due 13 November, with forensic triage flagged. Barracuda’s workaround is to restrict the admin UI to trusted networks; patch IDs are on the advisory. No IOCs have been published. (CISA KEV) (Barracuda) To do: confirm patch IDs on every ESG, ADC, BMA, WCC, WAF and WSG; review config-import and restore history on any box whose admin UI was reachable.
Xen Orchestra: exploited, still no CVE
[Confirmed] Vates’ VSA-2026-062 (exploited “empty-object” token bypass, root on XCP-ng hosts) still lists no CVE; fixed in XO 6.9.2 and 6.10.1. VSA-2026-063 (Important) was published the same day. Exploitation leaves no log entries, so run the vendor’s host checks and block its published IPs and onion C2. (Vates) [Unknown] MAG212 couldn’t locate SecurityWeek’s 11 November article on these flaws, so we can’t say whether it reports VSA-2026-063 as exploited.
eMudhra: certificates stop being trusted
[Reported] After a key-transfer script truncated private keys at an April 2025 key ceremony, eMudhra revoked eight more intermediates (six TLS, two code-signing), using a revocation reason Mozilla participants have questioned. From 16 November G1 issuance stops, Microsoft starts removing ten eMudhra roots, and Chrome and Firefox distrust G1 certificates issued after that date. Apple ends trust in all G1 certificates on 30 November. eMudhra reports no known misuse and is leaving public TLS. The main remaining G1 user is “a North American university federation”. (The Hacker News) (Microsoft) [MAG212 analysis] To do: search your certificate inventory and code-signing chains for emSign/eMudhra issuers and replace them before 16 November. Universities in federated identity schemes should ask their federation today.
Asus routers: four CVEs, none known exploited
[Reported] SecurityWeek says Asus disclosed four high- and medium-severity router firmware flaws that could allow root command execution or memory overwrite. (SecurityWeek) CVE records published on 10 November match that count, all for firmware series 3.0.0.4.386, 3.0.0.4.388 and 3.0.0.6.102:
| CVE | Flaw | Who can attack | CVSS 4 |
|---|---|---|---|
| CVE-2026-88710 | OS command injection, root commands | Unauthenticated, adjacent network | 8.7 |
| CVE-2026-88707 | Out-of-bounds write | Not stated | High |
| CVE-2026-88709 | Command injection via USB device with crafted folder name, root | Physical access | 7.0 |
| CVE-2026-88708 | Off-by-one memory overwrite, service crash | Unauthenticated, nearby | 5.3 |
Sources: CVE record mirrors OffSeq, OffSeq, Vulners. Asus’s advisory page was not opened by MAG212; fixed firmware builds are listed there.
To do: update router firmware from Asus’s advisory page; until then, keep untrusted devices off the router’s local network and disable unused USB and remote-admin features. [MAG212 analysis] Small offices and home workers are the exposure here.
Why it matters
Deadlines are where security work most often slips: the patch was planned, the certificate renewal was on someone’s list, the router was at a home office nobody inventoried. Certificate distrust in particular fails loudly, with browsers and Windows refusing connections, and a missing CVE means vulnerability scanners may not flag an exploited Xen Orchestra server at all.
The bottom line
Confirm Barracuda patch IDs and review configuration history today, upgrade Xen Orchestra and run Vates’ host checks, replace any emSign or eMudhra certificate before 16 November, and update Asus router firmware or disable USB and remote features until you can.
How we label evidence: [Confirmed] comes from a primary source such as a vendor or CISA; [Reported] from a secondary outlet; [Claimed] from an attacker or an unverified party; [MAG212 analysis] is our judgement; [Unknown] means not established at press time. Commands and indicators are copied from the cited sources and were not tested by MAG212 CYBER.
This story is part of MAG212 CYBER Daily, 12 November 2026, with the day’s other verified stories, the Defender’s Action Desk and a full source register. Get the daily briefing free: subscribe to MAG212 CYBER. By El Mostafa Ouchen.