
Citrix NetScaler: 28 Flaws in ADC and Gateway, One Affecting Every Appliance, Plus a 9.4 Console Bypass
NetScaler appliances carry remote access and application traffic for a large share of the world’s enterprises, and their vulnerabilities have a history of being exploited quickly. This week Citrix fixed 28 of them in a single ADC and Gateway bulletin. Most need a particular feature to be switched on, but one, CVE-2026-120868, affects every deployment including the default configuration. A separate bulletin fixes an unauthenticated bypass in NetScaler Console, the management tool many teams use to run their fleets. Citrix does not report exploitation of any of them.
| Every appliance | CVE-2026-120868, packet processing, 9.3 |
| Highest score | CVE-2026-107412, Gateway/AAA, 9.5 |
| Fix ADC/Gateway | 14.1-73.57 · 13.1-64.39 · FIPS 14.1-73.58 / 13.1-37.293 |
| Console | CVE-2026-120869, 9.4 · fix 14.1-74.34 |
What happened
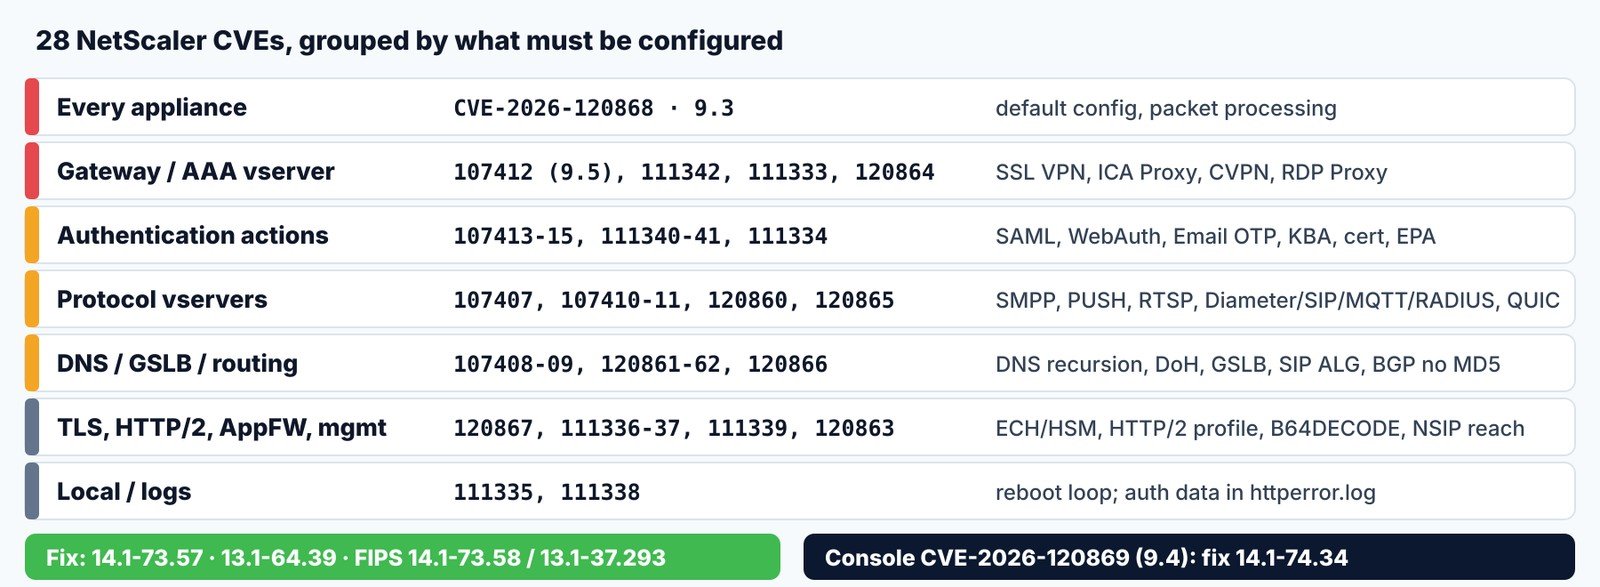
[Confirmed] Citrix bulletin CTX697305 lists 28 CVEs in NetScaler ADC and Gateway, almost all memory-safety bugs that Citrix says “can lead to unpredictable or erroneous behavior or Denial of Service”. The one that matters to everyone is CVE-2026-120868 (CVSS 4.0: 9.3), in core packet processing: all deployments are affected, “including those deployed with the default configuration”. The highest score, 9.5, goes to CVE-2026-107412, a set of memory overflows on appliances configured as a Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA virtual server. Separately, CTX697320 fixes CVE-2026-120869 (9.4), an unauthenticated bypass in NetScaler Console. (CTX697305) (CTX697320)
[Confirmed] Neither bulletin reports exploitation. Credits include JPMorgan Chase’s XOR team, CapitalOne and watchTowr, and Citrix says it found several issues itself with AI-assisted code analysis. Secure Private Access hybrid deployments that use NetScaler instances also need the upgrade; Citrix-managed cloud services are patched by Citrix. (Citrix) [MAG212 analysis] NetScaler bugs have been weaponised quickly in past years, and watchTowr often publishes technical detail after a patch, so don’t treat “not exploited” as “not urgent”.
Who is affected
[Confirmed] NetScaler ADC and Gateway 14.1 before 14.1-73.57, 13.1 before 13.1-64.39, 14.1-FIPS before 14.1-73.58 and 13.1-FIPS/NDcPP before 13.1-37.293. Console 14.1 before 14.1-74.34. The Console flaw needs network access to the Console IP (attack vector “adjacent”). Other notable preconditions include a management-plane flaw exploitable by any untrusted host that can reach the NSIP (CVE-2026-120863), and authentication material written to /var/log/httperror.log after logouts (CVE-2026-111338). (Citrix)
Build and exposure check
OS: NetScaler 13.1 / 14.1 · Shell: NetScaler CLI, then shell · Privileges: nsroot or read-only admin · READ-ONLY
# CLI: running build (run on every node, both HA peers)
show ns version
# shell: features that widen exposure (patterns from CTX697305)
shell
grep -E '^add (vpn|authentication) vserver' /nsconfig/ns.conf
grep -E 'http2 ENABLED|B64DECODE' /nsconfig/ns.conf
exit
Compare the build with the fixed versions above; every node below them needs the upgrade regardless of the grep results, because CVE-2026-120868 hits default configurations. The grep results show which extra CVEs apply. Commands not tested by MAG212 CYBER; patterns follow CTX697305 and NetScaler docs.
Contain, remediate and verify
- Upgrade internet-facing Gateway and AAA appliances first, then everything else, then Console. Back up the configuration before each upgrade.
- Restrict NSIP and Console access to management networks (this addresses CVE-2026-120863 and CVE-2026-120869 exposure).
- [MAG212 analysis] Treat old
httperror.logfiles as sensitive (CVE-2026-111338): limit who can read them and consider rotating credentials if they were copied off-box.
Verify recovery: both HA peers report the fixed build, HA sync is healthy, VPN and SSO logins work, and a test from an untrusted segment can’t reach the Console. Prevention [MAG212 analysis]: subscribe to Citrix bulletin alerts, and keep a list of which features each appliance uses, so the next precondition check takes minutes.
Planning the rollout
[MAG212 analysis] Because one flaw affects every appliance, the question is not whether to upgrade but in what order. Internet-facing Gateway and AAA virtual servers come first: they carry the highest-scoring flaw and sit where attackers look first. Internal load balancers come next, then Console.
[MAG212 analysis] High-availability pairs make NetScaler upgrades routine but not trivial. Upgrade the secondary, fail over, confirm VPN and SSO logins work, then upgrade the former primary. Keep a configuration backup from before each step, and schedule the work in a window when a failed login is noticed quickly.
[MAG212 analysis] Citrix credits external researchers including watchTowr, which has published detailed technical analyses of past NetScaler patches. Whether or not that happens here, defenders should assume the time between a NetScaler patch and a working exploit can be short.
Why it matters
NetScaler Gateway is the front door to remote work for many organisations, and past NetScaler flaws such as CitrixBleed were used to steal sessions and breach large networks within weeks of disclosure. A flaw that affects default configurations removes the comfort of “we don’t use that feature”. Console is just as sensitive: it holds credentials and configuration for every appliance it manages.
The bottom line
Upgrade every NetScaler ADC and Gateway to 14.1-73.57 or 13.1-64.39 (FIPS: 14.1-73.58 or 13.1-37.293), starting with internet-facing Gateway and AAA, then move Console to 14.1-74.34. Restrict NSIP and Console access to management networks, treat old httperror.log files as sensitive, and confirm both HA peers report the fixed build.
How we label evidence: [Confirmed] comes from a primary source such as a vendor or CISA; [Reported] from a secondary outlet; [Claimed] from an attacker or an unverified party; [MAG212 analysis] is our judgement; [Unknown] means not established at press time. Commands and indicators are copied from the cited sources and were not tested by MAG212 CYBER.
This story is part of MAG212 CYBER Daily, 13 November 2026, with the day’s other verified stories, the Defender’s Action Desk and a full source register. Get the daily briefing free: subscribe to MAG212 CYBER. By El Mostafa Ouchen.