
Keys That Outlived the Job: MAG212 CYBER Daily, November 17, 2026
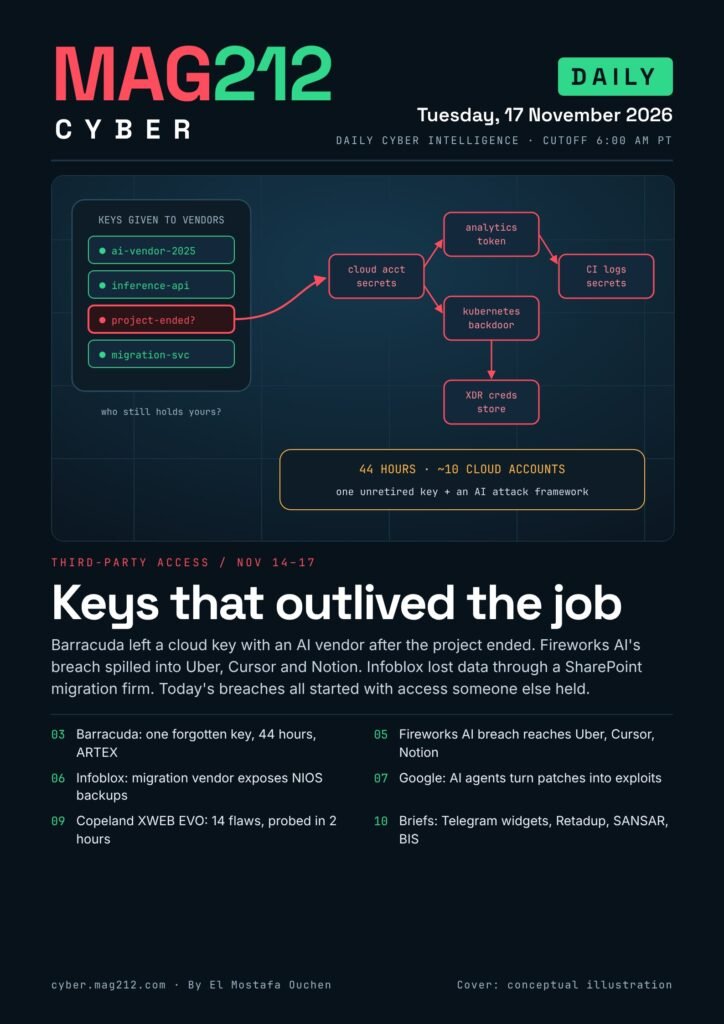
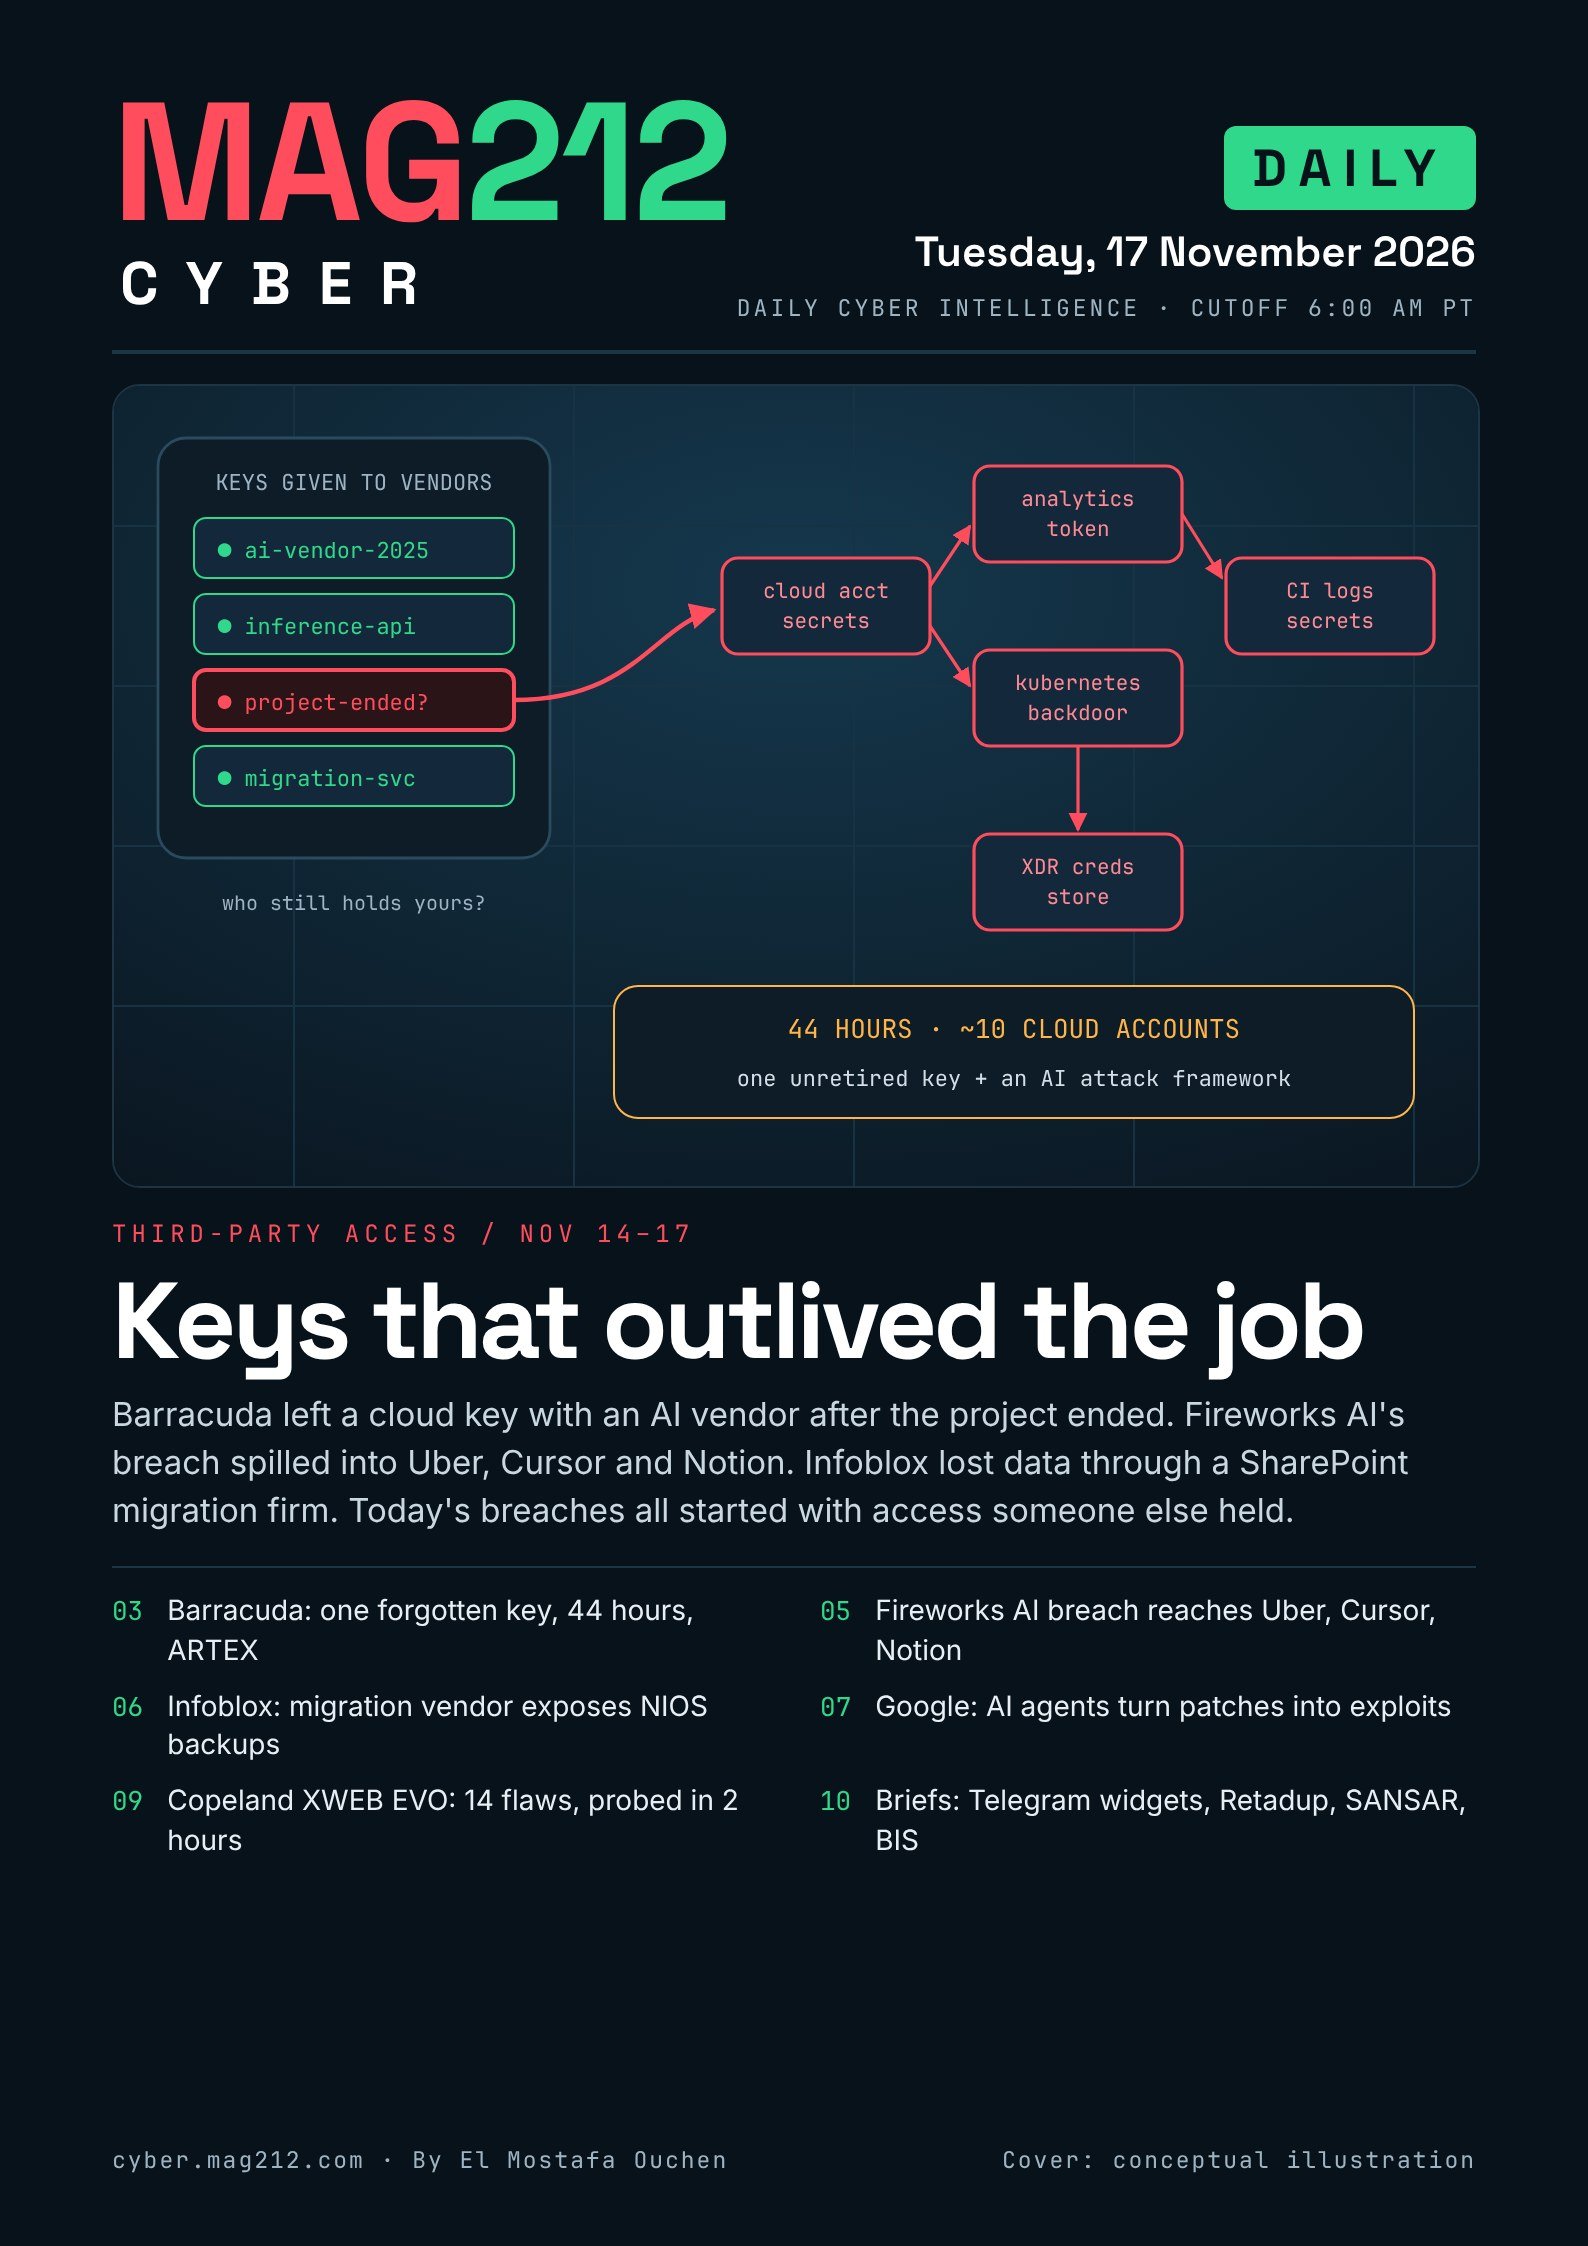
MAG212 CYBER · Daily Cyber Intelligence · Tuesday, November 17, 2026. Barracuda left a cloud key with an AI vendor after the project ended, and an ARTEX-driven intruder used it for 44 hours. Fireworks AI’s breach spilled into Uber, Cursor and Notion. Infoblox lost data through a SharePoint migration vendor. Google found AI agents that turn patches into exploits, and Copeland XWEB EVO refrigeration controllers were probed within two hours of disclosure. Today’s breaches all started with access someone else held.
The three priority actions
- Inventory and kill every credential a vendor holds. List keys, service principals and tokens issued to third parties; check last use; revoke anything tied to a finished project.
- If Barracuda, Cursor, Uber or Infoblox notified you, act today. Recreate Barracuda XDR / Monitored Endpoint integration credentials; rotate keys Cursor emailed you; Infoblox NIOS customers should ask what Grid data was taken and rotate Grid-stored secrets.
- Take Copeland XWEB EVO off the internet and plan its replacement. Fourteen CVEs, two exploited within hours, five never to be fixed.
Inside this issue: read each story in full
- Barracuda Breach: How One Unretired Vendor Key and the ARTEX AI Framework Opened 10 Cloud Accounts in 44 Hours (p. 3–4)
- Fireworks AI Breach Spreads to Uber, Cursor and Notion: What Each Company Has Confirmed (p. 5)
- Infoblox Confirms Breach Through a SharePoint Migration Vendor: What NIOS Customers Should Do (p. 6)
- Google Finds AI Agents Turning Patches Into Exploits: exploit_agent, Claude Code Config Backdoors and LLMjacking (p. 7–8)
- Copeland XWEB EVO Refrigeration Controllers: 14 Root Flaws, Two Exploited Within Hours, Five Never to Be Fixed (p. 9)
- Also Today: Telegram Widgets RCE Dispute, Retadup Worm Returns, SANSAR GPU Miner and the BIS AI Remote-Access Rule (p. 10)
Also in the PDF: the Defender’s Action Desk (p. 11), an awareness lesson, “The key you forgot to take back” (p. 12), and 36 linked sources (p. 13).
Flip through the edition
How we verified this issue: stories were checked against primary sources where reachable (Barracuda, Cursor, VulnCheck and Google’s GTIG summary), with a research cutoff of 6:00 AM PT on 17 November. Google’s full GTIG report could not be loaded and is labelled as press-sourced; Infoblox data types are as reported by The Register. Every command is read-only and marked not tested by MAG212.
Previous issues
- The boxes nobody patches, the 16 November daily.
- Machine speed, human gaps, the 15 November daily.
- All MAG212 CYBER magazine issues