
Cold-Chain Sabotage Gets a Name: France Blames IRGC-Linked Unit as US Agencies Harden Refrigeration Controllers
From the MAG212 CYBER Weekly, 14 November 2026. Status labels: confirmed by vendor, reported by researchers, or unverified. Every command below is copied from official documentation and was not tested by MAG212; run it only on systems you are authorised to administer.
Status:
- France’s attribution: confirmed by government (French Ministry for Europe and Foreign Affairs, 9 Nov) [53].
- US joint advisory: reported by The Hacker News (9 Nov). CISA’s page, advisory ID and exact date were not retrieved [52].
- ICS Patch Tuesday: per SecurityWeek (11 Nov) [55].
What happened
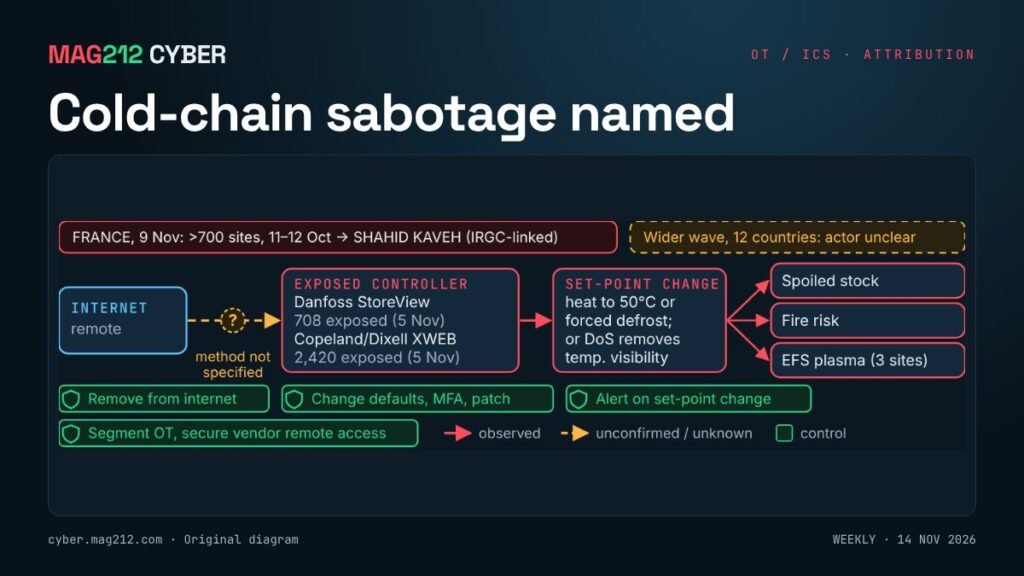
On 9 November France formally attributed the night-of-11–12 October attack on supermarket refrigeration controllers to SHAHID KAVEH, linked to the IRGC’s cyber and electronic centre [53]. That attack hit more than 700 French retail sites and caused fires and food losses estimated at “several tens of millions of euros”. France called it “the first cyber-offensive campaign carried out purely for sabotage on national territory”. It summoned Iran’s ambassador, will propose new EU sanctions, and published a joint C4 technical report [53]. CERT-FR’s CTI report CERTFR-2026-CTI-009 exists, but MAG212 did not fetch it [54].
The same day, The Hacker News reported a joint CISA, FBI, HHS, USDA and DOT advisory urging hardening of industrial refrigeration and cold-chain monitoring systems [52]. Across Europe, hundreds of supermarkets in 12 countries were hit, with temperatures raised to 50°C or units forced into defrost. The French Blood Establishment (EFS) confirmed altered settings at three blood-plasma storage sites. THN says the actor behind the wider European campaign is unclear [52]. Do not extend France’s attribution to every country.
Who is affected
Censys exposure counts, via THN [52]. These are internet-exposed instances, not compromises:
| Controller | 9 Oct | 5 Nov |
|---|---|---|
| Danfoss StoreView (mostly in France) | 3,004 | 708 |
| Copeland/Dixell XWEB | 3,708 | 2,420 |
Sekoia has a write-up on exploitation of unpatched Danfoss controllers [94]. MAG212 did not fetch it, and its date is unverified.
Why this matters
Refrigeration controllers rarely appear in security inventories, yet tampering with them can spoil medicines and food or create fire risk. A government attribution to a state-linked unit raises this from nuisance to strategic threat for food, health and logistics operators. (MAG212 analysis)

How the attack works
- The attacker reaches an internet-exposed refrigeration or monitoring controller. The method (default credentials versus an unpatched flaw) is not specified in the sources fetched.
- They change set-points to force continuous heating or defrost, or they cause a denial of service that removes temperature visibility.
- The result is inventory loss, fire hazard and potential consumer harm [52].
What defenders should look for
Unexpected set-point or defrost-schedule changes, loss of telemetry from monitoring dashboards, and logins to controller web UIs from outside your maintenance vendor’s known addresses (MAG212 inference). No IOCs were published in the sources fetched.
How to investigate
Inventory every refrigeration controller and check whether it is reachable from the internet. Pull controller audit logs and remote-access vendor session logs. Compare current set-points with engineering baselines.
Contain and remediate (in order)
These are the advisory’s mitigations as reported by THN [52]:
- Remove the controllers from internet exposure.
- Change default passwords and enforce strong authentication.
- Patch.
- Isolate OT networks.
- Remove or secure remote access.
- Retire legacy devices.
Verify recovery
Run an external scan to confirm the controllers are not reachable. Confirm set-points match the baseline. Confirm alarms reach the people on call.
ICS Patch Tuesday (10 Nov) sidebar [55]:
- Siemens: 9 advisories covering 10 vulnerabilities, two of them about Node2Shell impact.
- High severity: ROS#, Simcenter Femap, Mendix Studio Pro MCP Server, Simatic SCADA and PCS 7, SIMATIC IOT2050, Simatic WinCC Graphics Designer.
- Low severity: the FortiGate NGFW used in Ruggedcom APE1808.
- Some products have no patch yet.
- Schneider: SEVD-2026-314-01, EcoStruxure Power Build Rapsody (malicious files can lead to code execution).
- CERT@VDE: 8 advisories (Beckhoff, MB Connect Line, Helmholz, Weidmueller, Bender, ads-tec), several involving PHP2Shell.
- Phoenix Contact: PHP2Shell and PLCnext advisories.
- Hitachi Energy: at least one product affected by PHP2Shell.
- Johnson Controls: EasyIO Neo IO Manager (privilege escalation and code execution), and a C•CURE 9000 3.20 / victor 8.0 installer issue that could expose admin credentials.
- Rockwell and ABB: none found.
Node2Shell (CVE-2026-111497, Brotli decoder out-of-bounds write) had a KEV due date of 10 Nov [56]. CISA ICSA-26-316-02 (“Siemens Desigo, Gridscale”) is likely dated 12 Nov but could not be read [58].
Prevention and awareness
OT owners should inventory embedded Node.js, Brotli and PHP in HMIs, edge devices and web UIs, because the October web-stack bugs are now showing up in OT advisories (MAG212 inference from [55]).
No command panels.
Related on MAG212 CYBER
- MAG212 CYBER Weekly, 14 November 2026: The keys were already inside (full issue and PDF)
- Subscribe free to MAG212 CYBER
Sources
- [52] The Hacker News, “US agencies warn on refrigeration and cold-chain system attacks”, 9 Nov 2026. link
- [53] French Ministry for Europe and Foreign Affairs, “Déclaration d’attribution à l’Iran de cyberattaques visant la France”, 9 Nov 2026. link
- [54] CERT-FR, “CERTFR-2026-CTI-009 (not fetched)”, Not verified. link
- [55] SecurityWeek, “ICS Patch Tuesday: Siemens flags high-severity flaws, Node2Shell exposure”, 11 Nov 2026. link
- [56] SecurityWeek, “CISA warns of Node2Shell exploitation as honeypots log attack attempts (background)”, 28 Oct 2026. link
- [58] CISA, “ICSA-26-316-02 Siemens Desigo, Gridscale (not fetched)”, ~12 Nov 2026 (inferred). link
- [94] Sekoia, “The cold chain on fire: unpatched Danfoss controllers exploited (not fetched)”, Not verified. link
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 14 November 2026, 10:05 AM PST. Diagrams are original MAG212 CYBER illustrations.