
The Keys Were Already Inside: MAG212 CYBER Weekly, November 14, 2026
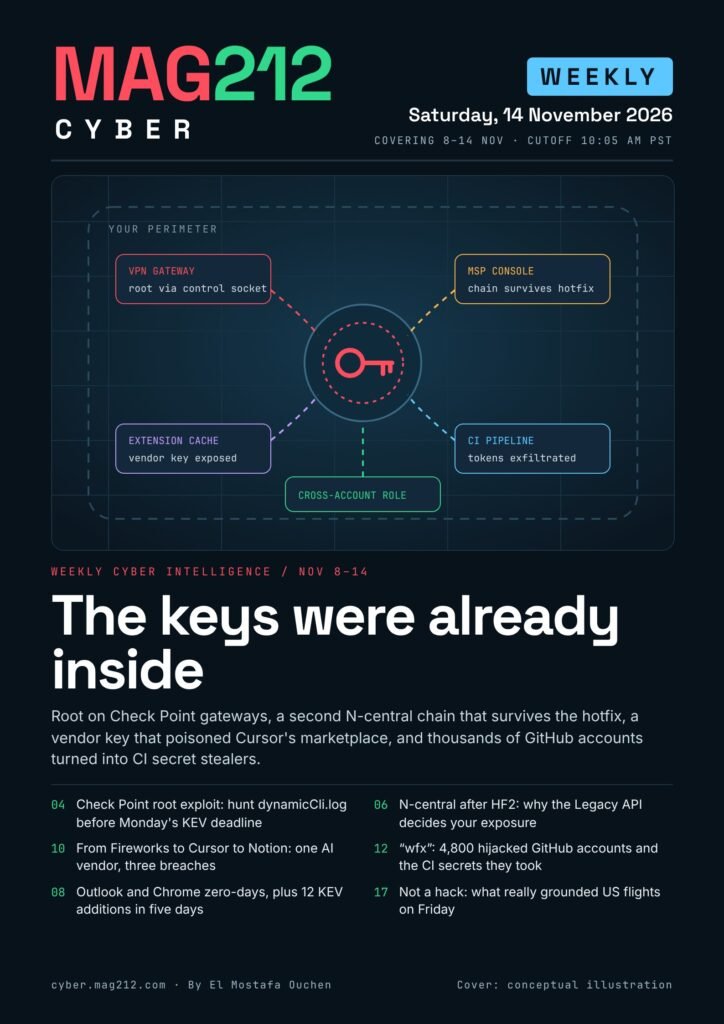
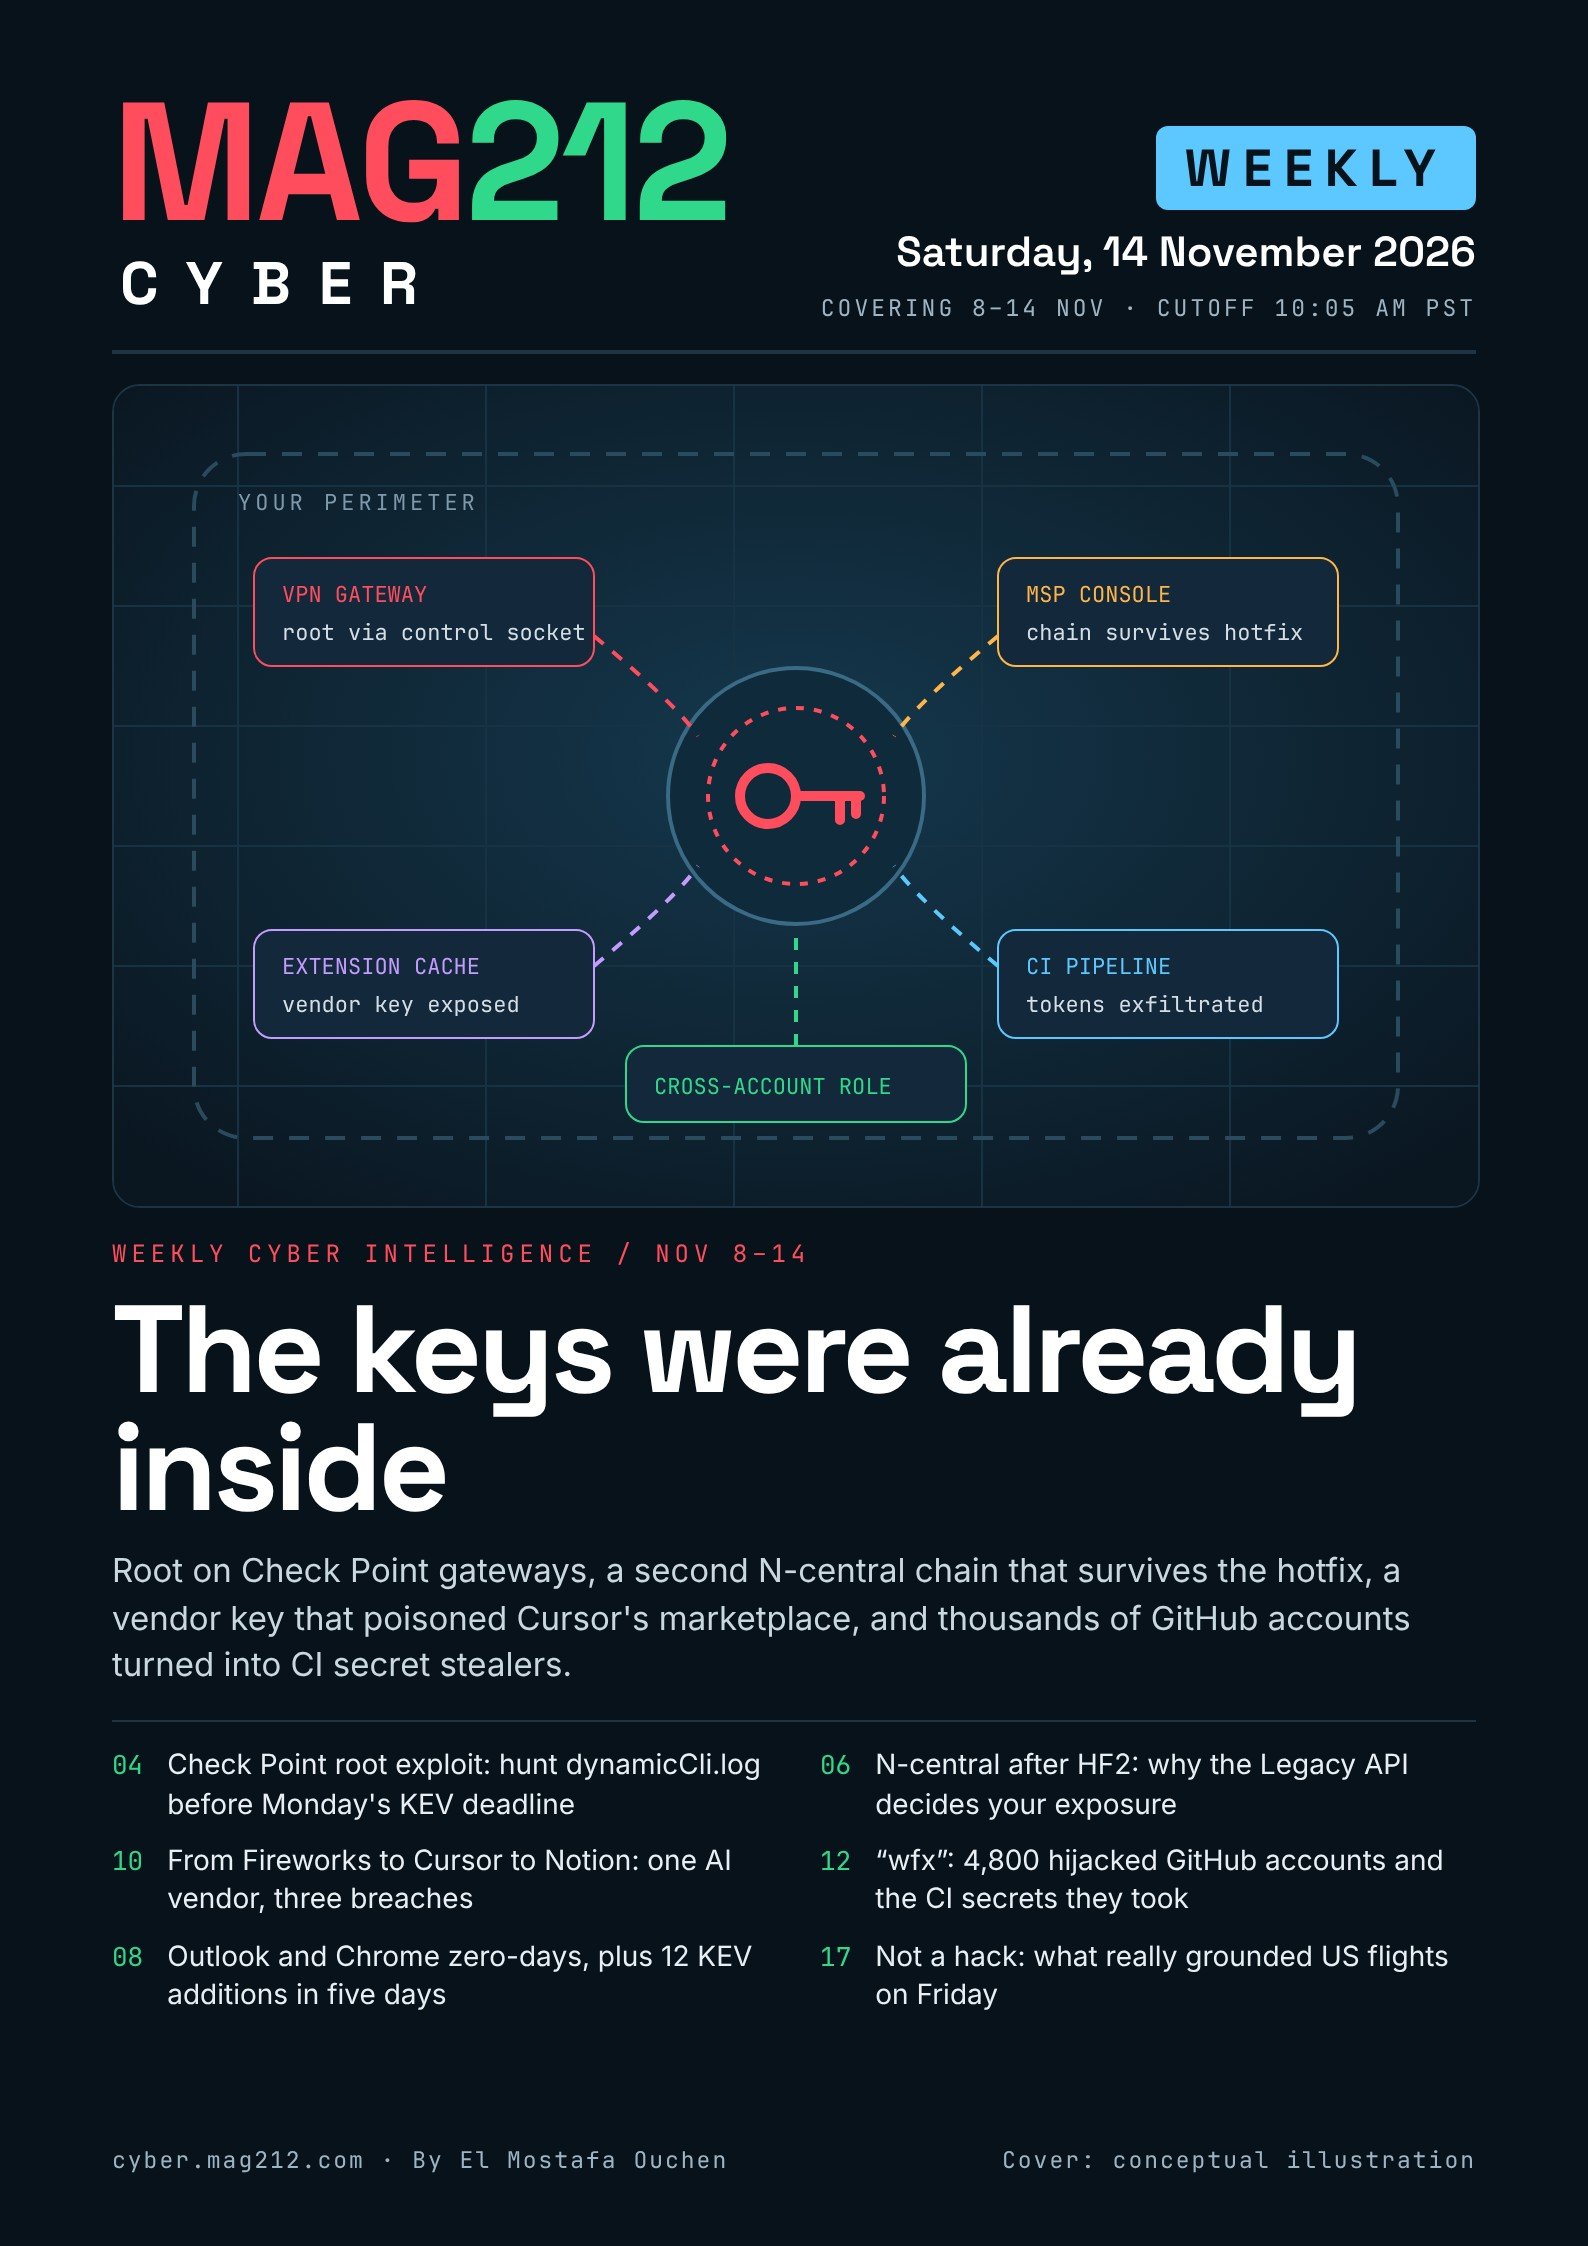
MAG212 CYBER · Weekly Cyber Intelligence · Saturday, November 14, 2026 · Covering Nov 8–14. This week, attackers came in through access defenders had already granted: a root control socket on Check Point gateways, an N-central API that survives the hotfix, an AI vendor’s exposed key that poisoned Cursor’s marketplace, hijacked GitHub accounts stealing CI secrets, and a vendor’s dormant AWS roles. Plus Outlook and Chrome zero-days, 12 CISA KEV additions, Operation Endgame, France’s IRGC attribution for cold-chain sabotage, and why Friday’s FAA ground stop was not a cyberattack.
The three priority actions
- Patch and hunt your edge and management planes today. Check Point: run the sk1000362 log greps and install the fixed Jumbo Hotfix take (KEV due Nov 16). Barracuda: confirm the patches (KEV deadline passed Nov 13). N-central: Legacy API off or unreachable, apply HF2, upgrade Agents and Probes.
- Hunt your developer and cloud trust paths. Search GitHub for the wfx probe pull requests, review CloudTrail for CreateAccessKey and UpdateAssumeRolePolicy, remove dormant third-party cross-account roles, and act on the Cursor, Notion and Apify notices.
- Close the exploited client bugs. Chrome 157.0.8103.50 or later with a forced restart, the November Office update per channel for Outlook CVE-2026-124194 (KEV due Nov 24), and the OpenSSH SSHole fix on Alpine and other musl hosts.
Inside this issue: read each feature in full
- Check Point CVE-2026-123039: Root Through the Gateway, and How to Hunt dynamicCli.log (p. 4–5)
- N-able N-central After HF2: Able2Shell, 4EverAble2Shell and the Legacy API Question (p. 6)
- Barracuda ESG Exploited: Pre-Auth Bypass Plus Command Injection Chains to Root (p. 7)
- November 2026 Patch Tuesday: Outlook Leaks NTLM Hashes, Chrome Patches an Exploited Zero-Day (p. 8)
- SSHole (CVE-2026-123158): The Narrow OpenSSH Bypass CISA Says Is Exploited (p. 9)
- One Vendor Key, Three Breaches: How Fireworks' Exposed Key Led to Cursor's Backdoored Extension and Notion's Exposure (p. 10–11)
- wfx: Hijacked GitHub Accounts Turn CI Into a Secret Stealer, and bee-js Shows Provenance Is Not Safety (p. 12)
- When the Vendor's Identity Is the Attacker: Qubole's AWS Roles, Railway's Build Escape and AntiFox (p. 13)
- Operation Endgame Hits Gootloader as DOJ Moves on Binance-Theft Funds and FaceStealer (p. 14)
- Cold-Chain Sabotage Gets a Name: France Blames IRGC-Linked Unit as US Agencies Harden Refrigeration Controllers (p. 15)
Also in the PDF: a day-by-day timeline (p. 3), patch briefs for PostgreSQL, Fortinet, SAP and Adobe (p. 16), breaches, education incidents, policy and the FAA ground stop (p. 17), the full KEV and patch board (p. 18), the Defender’s Action Desk with 19 prioritised actions (p. 19), an awareness lesson for staff and leaders (p. 20), and all 94 sources (p. 21–22).
Flip through the edition
How we verified this issue: stories were checked against the CISA KEV feed (catalogVersion 2026.11.13), CVE records, vendor advisories and government statements, with a research cutoff of 10:05 AM PST on November 14. Disputed or single-sourced claims are labelled where they appear; N-central exploitation, for example, is printed as disputed. Every command panel is copied from official documentation and was not tested by MAG212. The cover and diagrams are original conceptual illustrations.
Previous issues
- The Trusted Path, the November 8 daily.
- Trust Was the Attack Surface, the Nov 1–7 weekly.
- All MAG212 CYBER magazine issues