
Operation Endgame Hits Gootloader as DOJ Moves on Binance-Theft Funds and FaceStealer
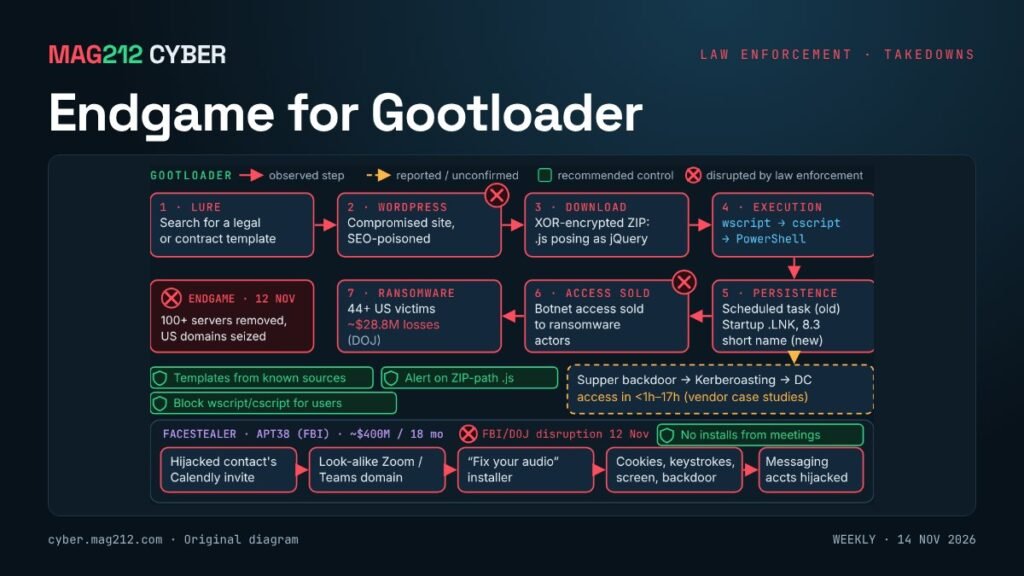
From the MAG212 CYBER Weekly, 14 November 2026. Status labels: confirmed by vendor, reported by researchers, or unverified. Every command below is copied from official documentation and was not tested by MAG212; run it only on systems you are authorised to administer.
Status: Confirmed by government. DOJ Press Release 26-1351 (12 Nov) covers Gootloader [47]. The Binance and FaceStealer actions are reported by The Record (12 Nov); the DOJ and FBI primary releases were not fetched [51]. Europol’s own totals are unverified because its newsroom could not be retrieved [48].
What happened — Gootloader
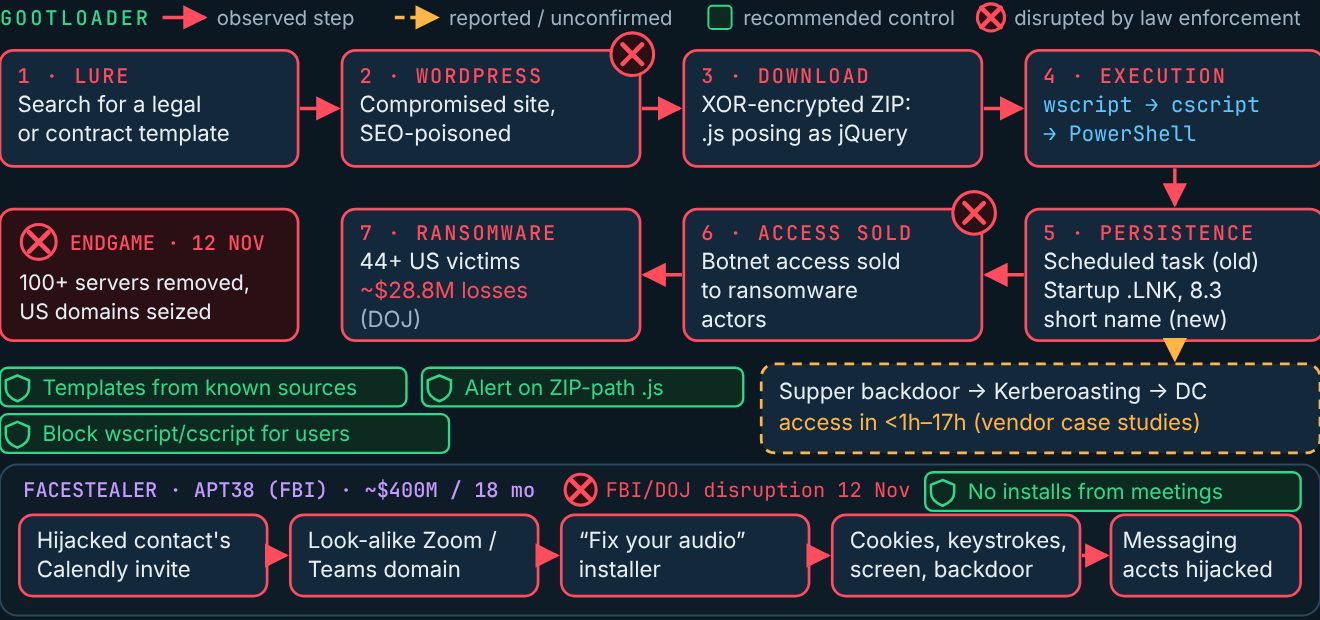
On 12 November DOJ said Gootloader had been removed from “over 100 servers, including compromised WordPress sites”, and that US domains used to deliver and control it had been seized under court authorisation, as part of Operation Endgame [47]. According to DOJ [47]:
Why this matters
Takedowns disrupt the delivery networks behind ransomware, but operators rebuild. Defenders should use the window to hunt for existing Gootloader footholds and close the search-poisoning and script-execution paths it relies on. The DOJ actions also show how fake meeting invitations now deliver infostealers. (MAG212 analysis)
- at least 25,000 computers infected worldwide since 2018
- ransomware attacks on at least 44 US victims, with about $28.8 million in losses
- targets included the US Department of War and the Defense Industrial Base
- infected machines joined a botnet, and operators sold access to ransomware actors
The Record says the wider action dismantled more than 100 StealC servers on Thursday and disrupted 235 servers and 257 domains used by Gootloader, CastleRAT and StealC. Seized domains show a seizure banner, and Shadowserver is notifying victims [48]. No arrests or defendants were named [47][48].
Partners [47]:
- Law enforcement: BKA (Germany), the Netherlands Police, RCMP and Ottawa Police (Canada), Danish Police, BL2C (Paris), the UK NCA, the AFP and Europol.
- Technical and private: Shadowserver, Fraunhofer FKIE, Registrar of Last Resort, OpenAI and Sharktech.
What happened — Binance and FaceStealer
DOJ obtained court authorisation to seize or restrain more than $1.2 billion from October’s roughly $6.3 billion Binance theft. That sum is part of $2.7 billion frozen by platforms. Binance and the FBI attribute the theft to North Korea’s TraderTraitor [51]. FBI and DOJ also disrupted cloud infrastructure behind “FaceStealer”, fake-meeting malware the FBI attributes to APT38, with about $400 million stolen over 18 months [51]. The scheme works like this [51]:
- Calendly invites to Zoom or Teams arrive from hijacked accounts.
- The links lead to look-alike domains.
- The fake meeting replays the victim’s contacts’ videos or deepfakes.
- A fake “fix your audio” prompt installs a cookie harvester, keylogger, screen capture and backdoor.
- The malware hijacks the victim’s Telegram, LinkedIn, Slack and Discord accounts.
The FBI also obtained a warrant covering more than 900 victim webcam videos. It is unclear whether FaceStealer was used in the Binance breach [51].
Who is affected
Gootloader affects two separate groups:
- people who downloaded and ran a lure, who need endpoint remediation
- operators of compromised WordPress sites, who need site remediation
The takedown does not clean infected hosts. FaceStealer targets crypto, finance and executive staff who take external meeting invites.
How Gootloader works
This is background vendor research, not this week’s DOJ release, from Huntress [49] and Red Canary [50]:
- Lure: an SEO-poisoned, compromised WordPress site offers a legal-style document. DOJ says only “tricking users into downloading” [47].
- Download: the download triggers a POST to
/wp-comments-post.php, which returns an XOR-encrypted ZIP. - Execution: the ZIP holds a JavaScript file masquerading as jQuery. It runs through
wscript, thencscript, then PowerShell. - Persistence: older variants used scheduled tasks. Newer ones use a Startup-folder
.LNKwith 8.3 short names. - Follow-on: the Supper SOCKS5 backdoor (Vanilla Tempest), Kerberoasting,
nltest, domain-controller access within about 17 hours (or under 1 hour in one case), NTDS.dit dumping and log clearing [49].
What defenders should look for
These come from Red Canary [50] and Huntress [49]:
- Script execution:
wscript.exewith a command line containing an AppData.jspath (for exampleAppData\Local\Temp\Temp1_<name>.zip)cscript.exerunning a~1.js8.3 short name, which Red Canary calls “an uncommon pattern”- the chain
wscript→cscript→ PowerShell
- Persistence and staging:
- second-stage files written as
.dator.logand renamed to.jsin AppData\Roaming - scheduled tasks named with two or three unrelated words that run AppData\Roaming scripts
- staging folders that mimic Teams, Zoom, FortiClient, Adobe or UltraVNC
- registry keys under
HKCU\SOFTWARE\Microsoft\Phone|Personalization|Fax\%USERNAME%
- second-stage files written as
- Historical C2 (Huntress, Nov 2025):
103.253.42[.]91,178.32.224[.]219
False positives: legitimate admin scripts run through wscript, but rarely from ZIP temp paths.
For FaceStealer: look for meeting links to non-vendor domains, and for any “audio driver” or “fix” installer run straight after a call.
How to investigate
Watch for Shadowserver notifications. Hunt for both older and newer Gootloader persistence. If you find any, scope Kerberoasting and DC access straight away, given the fast escalation timelines above [49]. On WordPress hosts, compare core, plugin and theme files with trusted originals and look for rogue admin users.
Contain and remediate (in order)
- Isolate hosts showing execution evidence.
- Reset credentials, prioritising service accounts exposed to Kerberoasting.
- Rebuild compromised WordPress sites from trusted code.
- For FaceStealer victims, revoke sessions and tokens on every messaging platform, and move crypto to new wallets.
Verify recovery
Confirm no persistence remains in Startup, scheduled tasks or the registry keys above. Confirm site files match trusted originals.
Prevention and awareness
Teach staff to get templates from known sources rather than search results, and to treat any meeting that asks them to install something as hostile. See the awareness lesson in section 8.
No command panels. No official command documentation is cited.
Related on MAG212 CYBER
- MAG212 CYBER Weekly, 14 November 2026: The keys were already inside (full issue and PDF)
- Subscribe free to MAG212 CYBER
Sources
- [47] US Department of Justice, “Gootloader malware disrupted in international cyber operation (Press Release 26-1351)”, 12 Nov 2026. link
- [48] The Record, “Gootloader: DOJ details takedown”, 13 Nov 2026. link
- [49] Huntress, “Gootloader threat detection: WOFF2 obfuscation (background)”, Nov 2025. link
- [50] Red Canary, “Threat Detection Report: Gootloader (background)”, Undated. link
- [51] The Record, “Stolen Binance crypto recovered; DOJ disrupts FaceStealer”, 12 Nov 2026. link
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 14 November 2026, 10:05 AM PST. Diagrams are original MAG212 CYBER illustrations.