
Ivanti and Citrix Ship Critical Fixes for Management Platforms: EPM 2024 SU8, CSA 5.0.8.1 and XenServer
Ivanti and Citrix have released fixes for nineteen vulnerabilities across their management products, and two of Ivanti’s are critical. An Endpoint Manager SQL injection (CVE-2026-121653, 9.8) can lead to unauthenticated remote code execution, and a missing-authentication flaw in Cloud Services Application (CVE-2026-121683, 9.4) lets an attacker add or delete trusted EPM Core certificates. Citrix’s XenServer update fixes a flaw that could let an attacker infer the pool secret and take over the host. Ivanti says none of its flaws is known to be exploited.
| Total | 19 flaws: 13 Ivanti, 6 Citrix |
| Top fix | EPM 2024 SU8 (CVE-2026-121653) |
| CSA | 5.0.8.1 (CVE-2026-121683) |
| XenServer | CTX697316 (CVE-2026-102705) |
What happened, who is affected and how it works
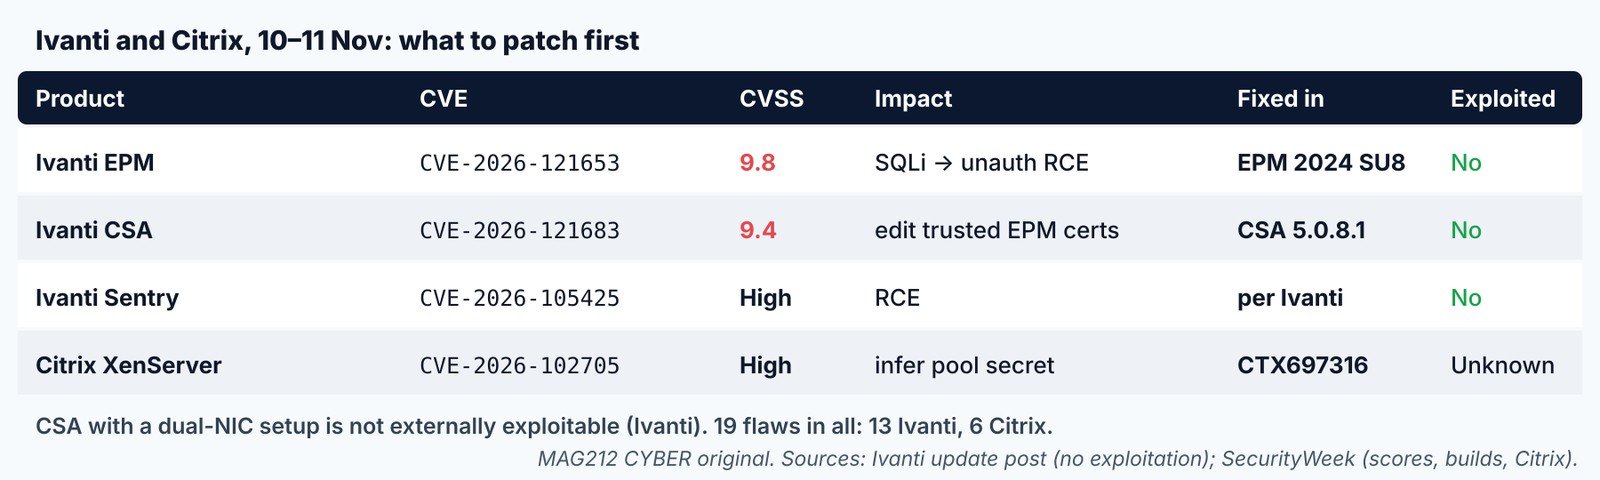
[Reported] Ivanti fixed an Endpoint Manager SQL injection that can lead to unauthenticated remote code execution (CVE-2026-121653, 9.8; EPM 2024 SU8) and a Cloud Services Application missing-authentication flaw that lets an attacker add or delete trusted EPM Core certificate entries (CVE-2026-121683, 9.4; CSA 5.0.8.1). CSA with a dual-NIC setup isn’t externally exploitable. A high-severity Sentry RCE (CVE-2026-105425) is also fixed. [Confirmed] Ivanti’s own update post says it has no evidence of these flaws being exploited and names four Sentry CVEs (CVE-2026-105425, -105669, -123179, -123181), a User Workspace Manager flaw (CVE-2026-105813) and CVE-2026-121683 for CSA, plus EPM and EPMM advisories. (Ivanti) [Reported] Citrix’s XenServer update fixes CVE-2026-102705, which could let an attacker infer the pool secret and compromise the host, plus five privilege-escalation and task-termination issues and mitigations for AMD guest-to-host flaws; Citrix doesn’t state exploitation. (SecurityWeek) MAG212 opened Ivanti’s summary post but not the per-product advisories or Citrix’s bulletin, so the EPM score and fixed builds come from SecurityWeek. (Citrix)
What to look for, then fix (in order)
- EPM core servers first: upgrade to 2024 SU8. [MAG212 analysis] Ivanti flaws have a history of fast weaponisation once patches are diffed; don’t wait for a KEV entry.
- CSA: 5.0.8.1; check whether yours runs single-NIC.
- [MAG212 analysis] After patching, review EPM’s trusted certificate list for entries you didn’t add.
- XenServer: apply CTX697316; keep the management network isolated (the same lesson as this week’s Xen Orchestra attacks).
Verify recovery: versions confirmed; EPM certificate list reviewed. Prevention [MAG212 analysis]: endpoint-management servers can push code to every machine, like the ScreenConnect consoles in story 1. Give them the same isolation as a domain controller.
Why management platforms keep making the news
[MAG212 analysis] Endpoint managers, mobile-device managers and remote-support consoles share one property attackers love: by design, they can run code on every machine they manage. A single flaw in the server therefore becomes a flaw in the whole estate, and the server itself is often exposed to the internet so that laptops can check in from home.
[MAG212 analysis] The practical response is the same regardless of vendor. Keep the management server off the open internet where the product allows it, or put it behind a VPN or an identity-aware proxy; give its administrative accounts phishing-resistant multi-factor authentication; log and alert on new administrators, new certificates and mass software deployments; and treat its database and backups as tier-zero assets, like a domain controller.
[MAG212 analysis] For the CSA flaw specifically, check how your appliance is cabled. Ivanti says a dual-NIC setup is not externally exploitable, so a single-NIC CSA facing the internet should move to the front of the queue.
Why it matters
Endpoint-management and virtualisation platforms can push code to every machine an organisation owns, which is why this week’s ScreenConnect campaign was so damaging. Ivanti products in particular have a history of being weaponised soon after patches are published and analysed, often by state-backed actors, and schools, councils and MSPs run EPM widely.
The bottom line
Upgrade EPM core servers to 2024 SU8 first, move CSA to 5.0.8.1, apply Citrix CTX697316 to XenServer pools, and afterwards review EPM’s trusted certificate list for entries nobody added.
How we label evidence: [Confirmed] comes from a primary source such as a vendor or CISA; [Reported] from a secondary outlet; [Claimed] from an attacker or an unverified party; [MAG212 analysis] is our judgement; [Unknown] means not established at press time. Commands and indicators are copied from the cited sources and were not tested by MAG212 CYBER.
This story is part of MAG212 CYBER Daily, 12 November 2026, with the day’s other verified stories, the Defender’s Action Desk and a full source register. Get the daily briefing free: subscribe to MAG212 CYBER. By El Mostafa Ouchen.