
N-central Update: Miners on Patched Servers, and the HF3 Fix Slips Again
From the MAG212 CYBER Daily, 15 November 2026. Every command is copied from official documentation or the cited analysis and was not tested by MAG212; run it only on systems you are authorised to administer.
Status: Exploited in the wild; fix pending. N-able’s next hotfix, HF3, was not released on 14 November as targeted. Huntback’s public report shows exploitation of internet-exposed servers with the Legacy API enabled, including servers on Hotfix 2. [1][2]
Correction: our 14 November Weekly described N-central exploitation as disputed and Huntback’s figures as unverified because we could not locate the source. We have now read Huntback’s 12 November report, and N-able has published indicators of compromise for servers with the Legacy API enabled. [2][3]
What happened
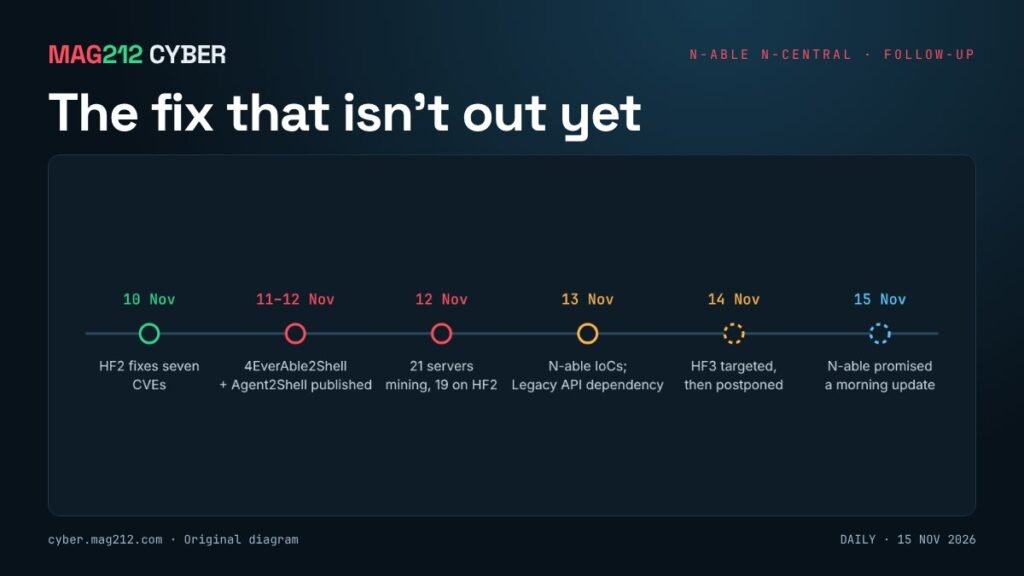
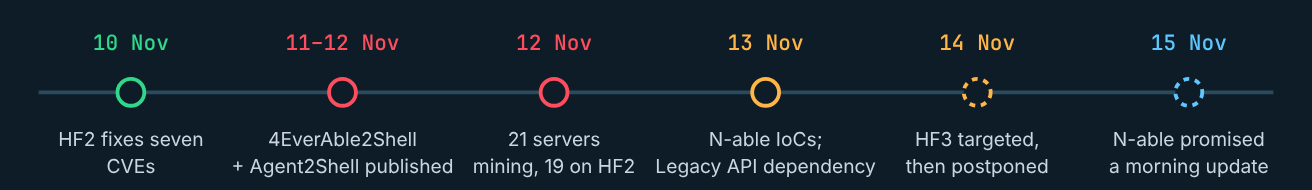
On 10 November N-able released N-central 2026.4 Hotfix 2 (build 2026.4.1.26), fixing seven CVEs from the Able2Shell disclosure. Late on 11 November, or on 12 November depending on the source, the same researcher published two more exploit chains, 4EverAble2Shell and Agent2Shell, that work against Hotfix 2 when the non-default Legacy API is enabled. [3][6]
Huntback’s decoy servers received the 4EverAble2Shell exploit on 12 November. Public mining-pool statistics for the attacker’s wallet showed 21 active rigs named nc_<victim-ip>; 19 reported build 2026.4.1.26 (Hotfix 2) and one reported 2025.3.1.9. Huntback treats 21 as a lower bound. [2]
On 14 November N-able said HF3 was close to general availability, then said later the same day that it “will not be available today” while validation continued, promising an update on the morning of 15 November (US Eastern). No HF3 had shipped at our cutoff. [1][7]
Who is affected
- On-premises N-central servers with the Legacy API enabled and reachable from the internet, including servers already on Hotfix 2. [3][4]
- Managed Windows endpoints, through Agent2Shell, which N-able says also requires the Legacy API. [3]
- Hosted N-central is not affected by the 4EverAble2Shell server chain, according to N-able. Hosted customers still need to upgrade Agents and Probes. [3][4]
Why this matters
An RMM server holds standing administrative access to every managed customer. Until HF3 ships, the only effective control for 4EverAble2Shell is configuration: the Legacy API must be off and unreachable. Installing Hotfix 2 alone has not been enough. (MAG212 analysis)
How the attack works
According to Huntback’s analysis of the exploit traffic: [2]
- A crafted SOAP fault is sent to the Apache Axis endpoint
/dms/services/ServerUI, first as a benign probe and then as a weaponised payload. - The server executes code as the
nableservice account. - The exploit escalates to root by abusing N-central’s maintenance helper
nable_wrapper.pland a symlink in its flag path, then restores the original script to hide traces. - A root command downloads and runs a miner installer that drops XMRig, sets persistence and reports back.
Unknown: whether the 19 Hotfix 2 servers were compromised before or after they were patched. Victim addresses have not been published.
What defenders should look for
- A symlink at
/var/opt/n-central/flag/flag_default.json. serverchild-*.bak,.shor.outfiles in/var/opt/n-central/tmp/./tmp/.xvd/or/var/tmp/.xvd/, axvd.servicesystemd unit,/etc/cron.d/xvd, or a crontab line tagged# xvkeep.- Processes started with
--rig-id nc_or--donate-level 1. - Outbound connections to
157.20.241[.]16(port 8080 and TCP 19202–19418) and mining pools139.99.69[.]109:10128and79.76.51[.]56:39100. - Web logs with POSTs to
/dms/services/ServerUIcontaining a SOAP fault with anexceptionNameelement, especiallyjline.internal.TerminalLineSettings. [2]
Command reference
Check an N-central server for the miner’s artefacts
Linux shell on the N-central server · root · read-only · not tested by MAG212
ls -la /var/opt/n-central/flag/flag_default.json /tmp/.xvd /var/tmp/.xvd 2>/dev/null
ls -la /var/opt/n-central/tmp/ | grep serverchild
systemctl status xvd.service --no-pager; grep -rs 'xvkeep' /etc/cron.d /var/spool/cron
ps aux | grep -E -- '--rig-id nc_|--donate-level 1' | grep -v grep
Any hit means the server should be treated as fully compromised: the exploit grants root on a host that manages customer endpoints. These indicators come from a single vendor’s analysis. [2]
Contain and remediate (in order)
- Confirm the Legacy API is disabled using N-able’s knowledge-base procedure, and block it at the network edge. [3]
- Keep Hotfix 2 installed and upgrade every Agent and Probe.
- Block
157.20.241[.]16and the two mining pools after checking your own telemetry. - If you find any indicator: isolate the server, rebuild it from trusted media, and rotate RMM, integration and customer credentials from a clean control plane.
- Install HF3 as soon as N-able releases it, then re-scan from outside.
Verify recovery
- The Legacy API path is unreachable from an external vantage point.
- No SOAP faults with
exceptionNameappear in ServerUI logs. - No mining-pool traffic, and CPU usage back at baseline.
- N-able confirms patch state. Huntress notes that live hotfixes do not always change the displayed version number. [5]
Prevention and awareness
RMM consoles are a key to every customer. Put them behind VPN or zero-trust access, keep optional APIs off, log administrative actions off the server, and give each technician a separate identity with phishing-resistant MFA. Business leaders should ask their MSP today whether it runs N-central and whether the Legacy API was ever enabled.
Related on MAG212 CYBER
- MAG212 CYBER Daily, 15 November 2026: Machine speed, human gaps (full issue and PDF)
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] N-able, “Status dashboard, event 202613 (HF3 updates)“, 14–15 Nov 2026.
- [2] Huntback, “4EverAble2Shell is already mining Monero on live N-central servers“, 12 Nov 2026.
- [3] Huntress, “N-able disables cloud services following disclosure of Able2Shell exploit chains (updates to 13 Nov)“, 10–13 Nov 2026.
- [4] SOCRadar, “4EverAble2Shell: N-central zero-day exploited“, 13 Nov 2026.
- [5] Hard2bit, “Able2Shell and N-central: 33 flaws with public exploits“, 13 Nov 2026.
- [6] BleepingComputer, “N-able releases security hotfixes for zero-day vulnerabilities“, 12 Nov 2026.
- [7] DEV Community (Varaxon), “N-central vulnerabilities (Able2Shell): what MSPs should do now (HF3 status)“, 15 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 15 November 2026, 7:45 AM PST.