
UnrealIRCd CVE-2026-114713: Exploited Server-Command Injection, KEV Deadline 16 November
From the MAG212 CYBER Daily, 15 November 2026. Every command is copied from official documentation or the cited analysis and was not tested by MAG212; run it only on systems you are authorised to administer.
Status: Exploited; fixed. CISA added CVE-2026-114713 to its KEV catalog on 13 November with a 16 November due date for US federal civilian agencies. The maintainer says attackers are exploiting it. [1][2]
What happened
CVE-2026-114713 (CVSS 8.6) is an improper neutralisation of delimiters in UnrealIRCd, the widely used open-source IRC server. The maintainer, Bram Matthys (Syzop), said attackers were exploiting it on the internet; exploitation attempts reportedly began the day after the 7 November hotfix. [1]
CISA added it to the KEV catalog on 13 November together with Check Point CVE-2026-123039, the DynamicCLI root flaw covered in our 14 November Weekly. Both are due on 16 November. [2][3]
Who is affected
- UnrealIRCd 6.0.0 up to, but not including, 6.2.7.1.
- Networks with two or more linked servers. Any connected user can trigger the flaw; no IRC operator rights are needed. [1]
Why this matters
The flaw lets any connected user inject commands that run with server authority across a linked IRC network, and the maintainer says it is being exploited. CISA gave US federal agencies only three days to fix it. (MAG212 analysis)
How the attack works
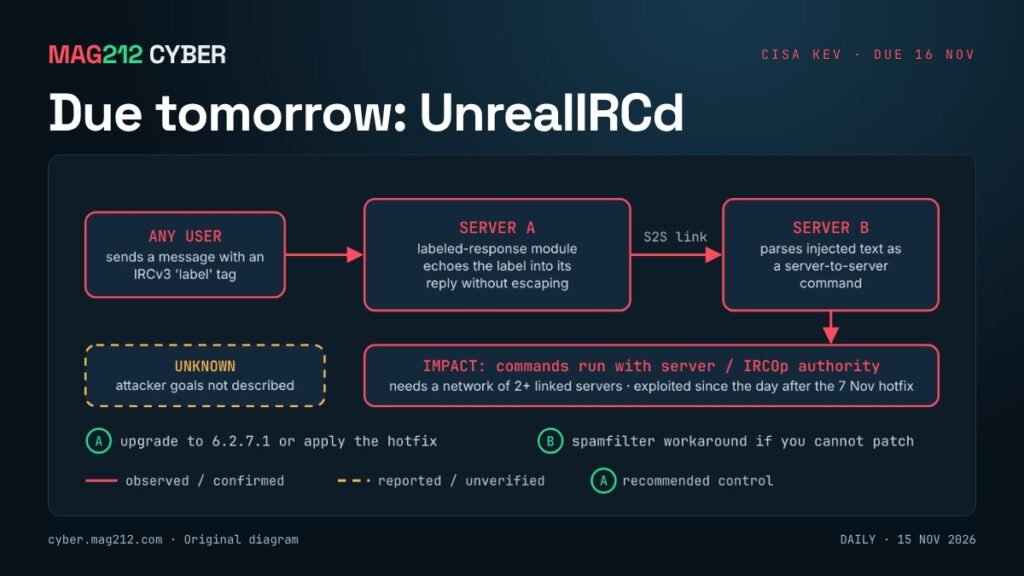
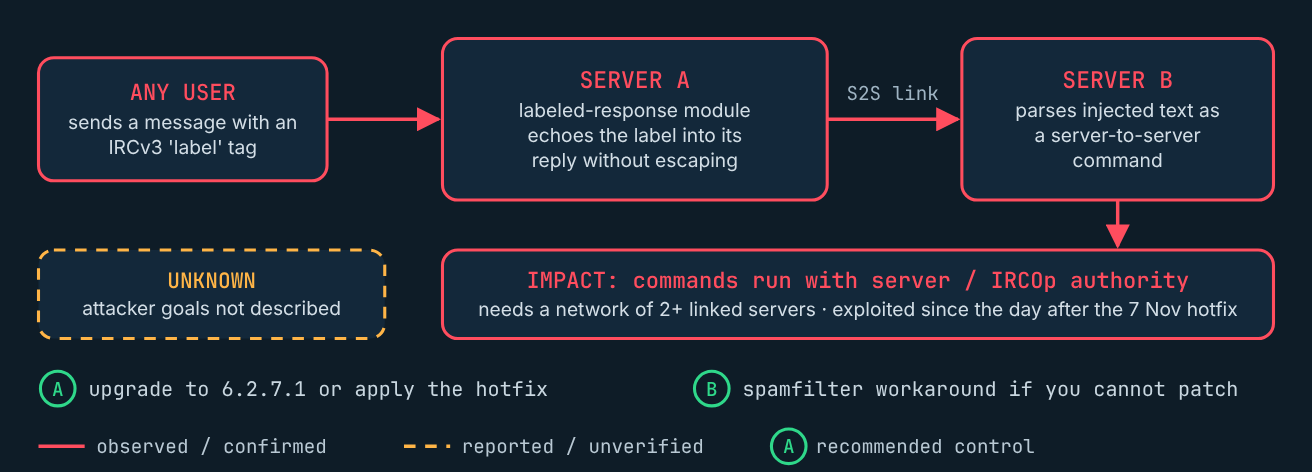
According to the maintainer’s description as reported by The Hacker News: [1]
- A user sends a message carrying an IRCv3
labelmessage tag. - The labeled-response module echoes the label into its reply without escaping it.
- The unescaped text crosses the server-to-server link, where it is parsed as a server command.
- The injected command runs with server or IRC-operator authority.
Unknown: what attackers have done with the access. The reports do not describe their activity or goals.
What defenders should look for
- Unexpected IRC operator actions, new server links, K-lines or G-lines you did not set.
- Configuration changes or rehashes since 7 November that no administrator made.
- Unusual messages carrying
labeltags in server logs.
How to fix and verify
- Upgrade every linked server to UnrealIRCd 6.2.7.1, or apply the maintainer’s hotfix. Use the spamfilter workaround only as a temporary measure. [1]
- From an IRC client, run
/VERSIONagainst each server and confirm it reports 6.2.7.1 or later. - Review operator actions, links, bans and configuration changes since 7 November.
- If you find unexplained changes, rotate operator and link passwords and rebuild the affected server’s configuration from a known-good copy.
The other KEV deadline: Check Point
CVE-2026-123039 lets attackers who already have low-privilege code execution on a Check Point Gaia gateway or management server run commands as root through the DynamicCLI control socket. Check Point says it is exploited against a couple of dozen customers. Install the fixed Jumbo Hotfix take for your release and run the sk1000362 log hunt; our Check Point article has the details. [2][3][4]
Prevention and awareness
Community infrastructure such as IRC networks often runs on volunteer time, but linked-server designs mean one unpatched node exposes the whole network. Subscribe to the project’s security announcements and keep every linked server on the same patch level.
Related on MAG212 CYBER
- MAG212 CYBER Daily, 15 November 2026: Machine speed, human gaps (full issue and PDF)
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] The Hacker News, “Attackers exploit UnrealIRCd flaw that enables server-level command injection“, 14 Nov 2026.
- [2] CISA, “CISA adds two known exploited vulnerabilities to catalog“, 13 Nov 2026.
- [3] Security Affairs, “U.S. CISA adds Check Point and UnrealIRCd flaws to its KEV catalog“, 14 Nov 2026.
- [4] MAG212 CYBER, “Check Point CVE-2026-123039: Root Through the Gateway, and How to Hunt dynamicCli.log“, 14 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 15 November 2026, 7:45 AM PST.