
When the Update Becomes the Attack: WordPress Core, cPGuard, APT29 Mobile & 3AM Ransomware: MAG212 CYBER Daily, 4 November 2026
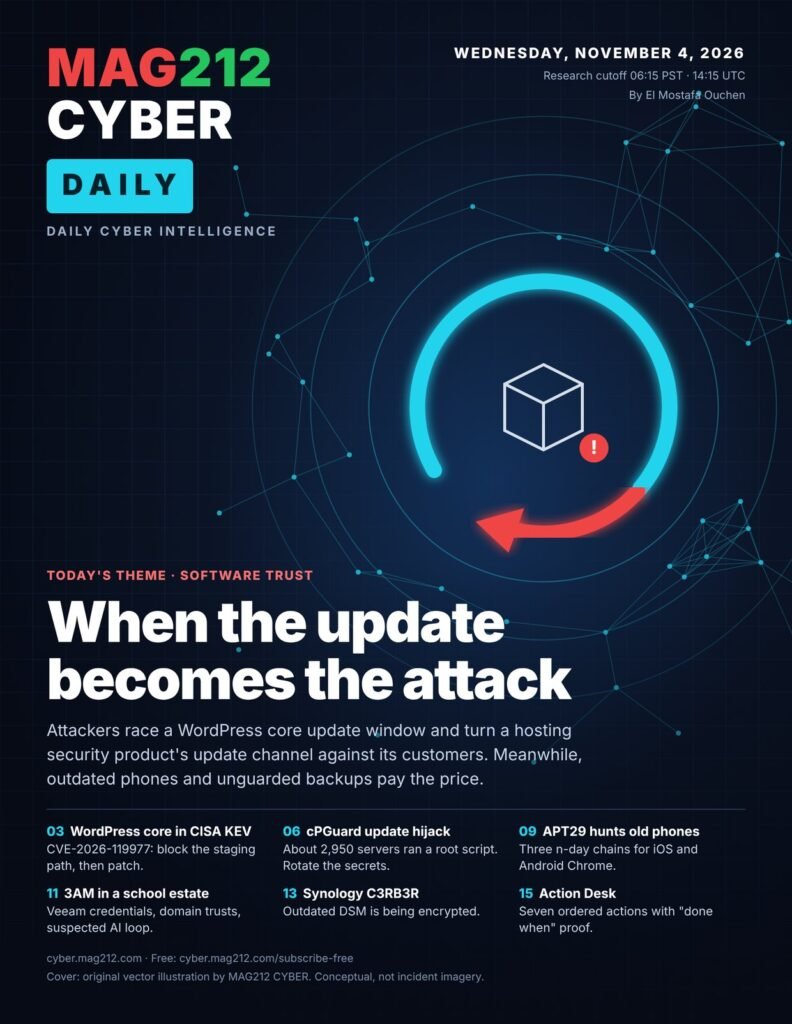
Today the routine maintenance window is the entry point. A WordPress core flaw can be exploited during the seconds a site spends updating itself, and a Linux hosting security product’s own update channel delivered a root-level data thief to thousands of servers. Alongside them, Russia’s APT29 is serving patched-but-effective exploits to phones that missed updates, and two ransomware cases show attackers going straight for backups. Every story is checked against vendor, government or original research sources, with ordered steps to contain, fix and verify.
What needs attention today
| Story | Status | Do this |
|---|---|---|
| WordPress core race (CVE-2026-119977) | CISA KEV, added Nov 3; federal due date Nov 6 | Block HTTP to /wp-content/upgrade/, then update to 7.1.4 or your branch fix (7.0.8, 6.9.11, 6.8.12 …) |
| cPGuard update channel hijack | Confirmed: fake update ran as root on ~2,950 servers, Nov 2 02:08–03:20 UTC | Update to the latest (5.88.26+), remove artifacts, rotate root, SSH, MySQL and cloud secrets, remove old keys fleet-wide |
| APT29 mobile watering holes | Observed campaign (Sekoia, Nov 4) | Enforce current iOS and Chrome/WebView via MDM; revoke sessions for exposed users |
| 3AM ransomware, UK school estate | Single case study (Bitdefender, Nov 3) | Isolate backup servers, rotate stored backup credentials, alert on new domain trusts |
| Synology C3RB3R | Vendor-confirmed attacks on outdated DSM | Install the latest DSM (SA-26:13 minimums, e.g. 7.2.2-72806-9), turn on auto-update, remove internet exposure |
Corrected since early reporting
- An early draft of today’s issue described Google’s “LLMjacking” research as new. The GTIG reporting it relied on dates from September 2026, so it has been removed from today’s news.
- cPGuard: the vendor disclosure names 5.88.26 as the clean build; its earlier advisory said “5.88.25 or later.” Use the latest available.
- Synology: its September 2026 advisory (SA-26:13) sets newer minimum DSM builds than the 2024 advisory its statement links to. The issue lists both.
Inside this issue
- WordPress core: attackers race the update window. How the upgrade-window race works, the full fixed-version table for every branch, NGINX and Apache deny rules, WP-CLI checks, and how to verify recovery.
- cPGuard: a security tool’s update channel turned on its customers. OPSSHIELD’s UTC timeline, artifacts, IPs and SHA-256 hashes, plus a credential-rotation worksheet for every secret the script took.
- APT29 mobile: one page visit, three n-day exploit chains. The iOS 16.x, iOS 18.5 (DarkSword) and Chrome-for-Android chains, the indicators Sekoia published, and why session revocation matters more than password resets.
- 3AM ransomware: backups, domain trusts and a suspected AI loop. Veeam credential theft, backdoor Domain Admins and cross-domain trusts at a UK school estate, with event IDs and read-only PowerShell hunts.
- Synology NAS: C3RB3R targets outdated DSM. Minimum fixed builds from both advisories and what to do if you’re hit.
- Briefs: the exploited Drupal Commerce Core access bypass, and Chainalysis’s breach disclosure.
- Defender’s Action Desk: seven actions, each with “done when” proof, plus a five-minute staff lesson and a printable break-room card.
Read each story in full
- CVE-2026-119977: The WordPress Core Update Race in CISA KEV, Explained, With Fixed Versions for Every Branch
- cPGuard Update Channel Hijacked: What Ran on 2,950 Linux Servers and How to Rotate Every Exposed Secret
- APT29 Watering Holes Serve n-day Exploits to Outdated iPhones and Android Phones: How to Check Your Fleet
- 3AM Ransomware at a UK School Estate: Veeam Credentials, Rogue Domain Trusts and a Suspected AI Loop
- Synology C3RB3R Ransomware: Which DSM Builds Are Safe and What to Do If Your NAS Is Hit
- Drupal Commerce Core CVE-2026-118539 Is Being Exploited: Patch, Then Audit Your Orders
Flip through the edition
Sources: CISA, WordPress, Patchstack, OPSSHIELD, Sekoia, Bitdefender, Synology and Drupal; the full 24-source register is on page 17. Research cutoff 06:15 PST, 4 November 2026. Diagrams are original MAG212 CYBER illustrations. Command panels were checked against vendor documentation but not executed; run them only on systems you are authorized to manage.