
Java4Shell (CVE-2026-114938): How One Base64 Byte Leads to Pre-Auth RCE in Jira, Jenkins and Keycloak, and How to Patch
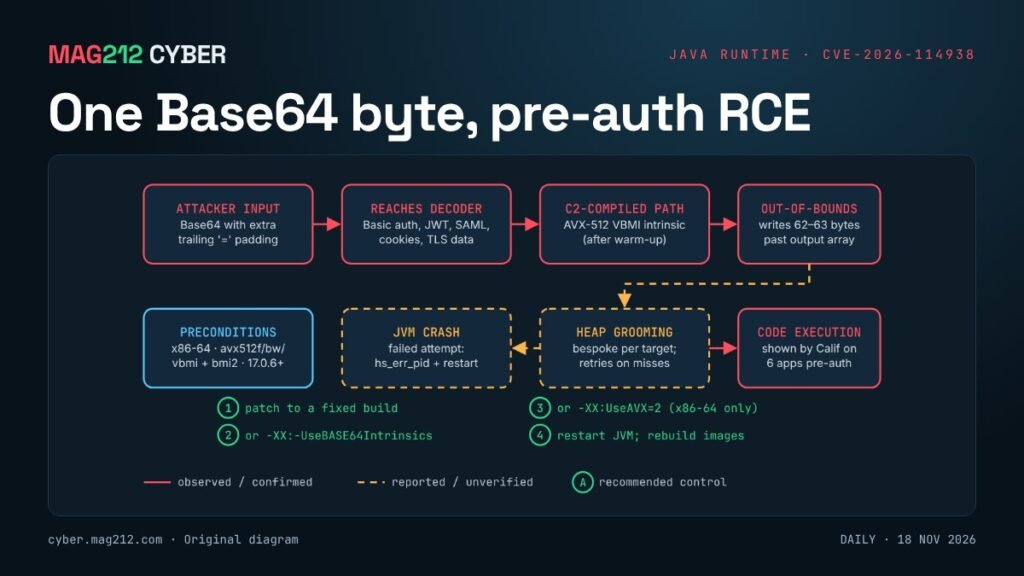
From the MAG212 CYBER Daily, 18 November 2026. Every command is copied from official documentation or the cited analysis and was not tested by MAG212; run it only on systems you are authorised to administer.
Status: Fixed on 17 November 2026 by Oracle and the OpenJDK project. Pre-auth remote code execution was demonstrated by Calif, which is withholding its application exploits. No exploitation in the wild is known, and the flaw was not in CISA’s KEV catalog when checked. Severity scores differ by scorer: 9.2 (CVSS 4.0, Calif), 8.1 (CVSS 3.1, Oracle and CERT-EU), 9.8 preliminary (Red Hat) and 8.8 (Amazon). [1][2][3][4][5]
What happened
On 17 November 2026, Oracle and the OpenJDK project released fixes for CVE-2026-114938, a memory-corruption flaw in the x86-64 Base64 decoder of the HotSpot Java Virtual Machine. Researchers at Calif, who found it while auditing HotSpot with an AI coding agent, named it Java4Shell. Calif says it took about an hour to find the bug and two more hours to build a first working exploit. [1][3]
Calif reports that it used the flaw to run code without logging in on Keycloak, Atlassian Jira, Atlassian Confluence, JFrog Artifactory, Jenkins and PingFederate, all in default configurations. It also reached code execution after login on Apache Kafka, Apache Solr, Elasticsearch, Gerrit and Spinnaker, and on sample Struts and Spring Boot applications. Calif stresses that these lists are not complete. [1]
Who is affected
All of these conditions must be true for the vulnerable code to run: [1][4][5]
- Java version: OpenJDK 17.0.6 and later on the 17 line, plus Java 21, 25 and 27 before the 17 November fixes, in every distribution built from OpenJDK (Oracle JDK, Corretto, Temurin, Microsoft Build of OpenJDK, Azul Zulu, Liberica, SapMachine, Red Hat). Oracle also lists Java SE 8 Performance Pack 8u511b33-perf and GraalVM for JDK 17 and 21. Standard Java 8 and Java 11 are not affected.
- CPU: an x86-64 processor with the avx512f, avx512bw, avx512vbmi and bmi2 features, which means Intel Xeon Ice Lake or newer, or AMD Zen 4 or newer. ARM64 servers are not affected.
- Configuration: the Base64 intrinsic is enabled, which is the default on supporting CPUs.
- Reachability: attacker-controlled Base64 reaches the decoder, for example through HTTP Basic authentication, JSON Web Tokens, SAML messages, cookies or TLS data.
Products that bundle their own Java runtime stay vulnerable until their vendor ships an updated runtime, even if the host’s system Java is patched. [4]
Why this matters
Java runs identity providers, CI servers and ticketing systems that sit on the internet and hold the keys to everything else. This bug is reachable before login on default configurations, the fix needs a runtime update plus a restart of every JVM and a rebuild of every container image, and the researchers plan to publish their application exploits once users have had time to upgrade. The window to patch quietly is now. (MAG212 analysis)
How the attack works
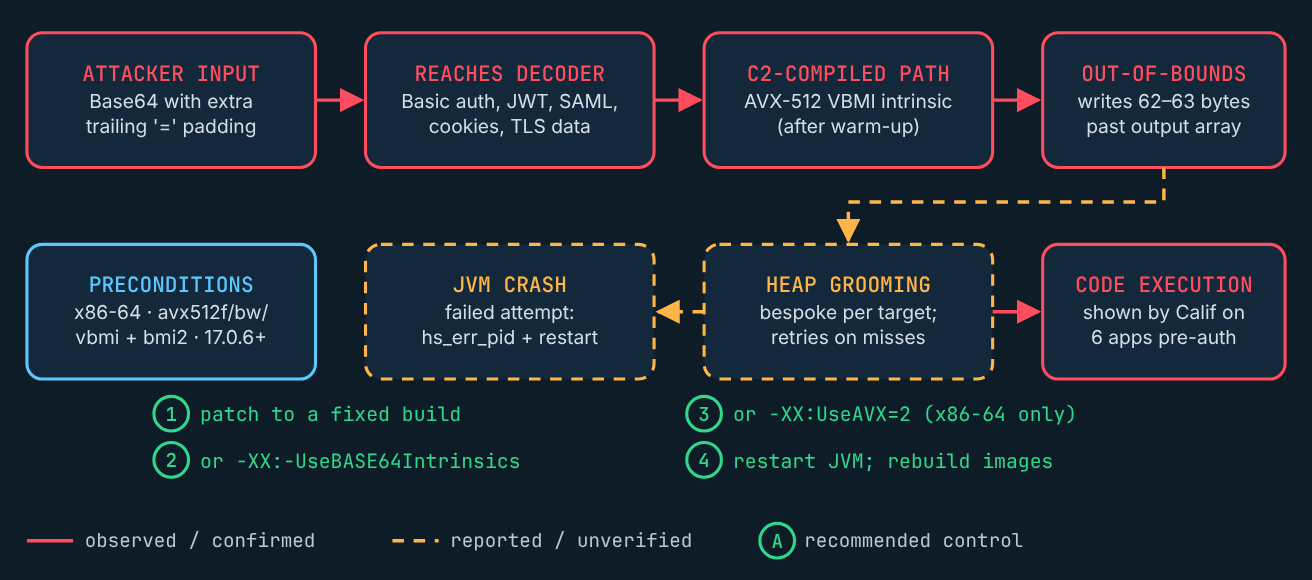
- Input: the attacker sends a Base64 string with an unexpected number of trailing
=padding characters, for example inside an Authorization header. [1][5] - Fast path: once a decoding method has been called often enough, the C2 just-in-time compiler swaps in a hand-tuned AVX-512 VBMI routine. Calif notes the decoder must first be warmed up with valid input. [1]
- Out-of-bounds write: with the malformed padding, the routine miscalculates the output length and writes 62 or 63 bytes past the end of its output array. Java only rejects the input after the write. [5]
- Steering the write: the overflowing bytes are fixed, but the attacker controls where they land. Calif’s technique, which it calls JavaBleed, grooms the heap so the write corrupts useful objects and turns into read and write access to memory. [5]
- Code execution: from there the exploit reaches code-execution paths in the target application. Each target needs its own exploit profile, and remote attempts are sensitive to network timing. [1]
- Failure mode: a miss can crash the JVM, and attackers can often retry. [1][5]
Calif adds two points defenders should note. A Java client that opens a TLS connection to a hostile server can also be compromised, even without exposing a service. And request buffering in nginx is not a general mitigation: it does not stop the Elasticsearch chain, and WebSocket frames bypass it. [1]
Fixed versions
| Distribution | Affected | Fixed build |
|---|---|---|
| Oracle Java SE 17 | 17.0.6 to 17.0.21.0.3 | 17.0.21.1 |
| Oracle Java SE 21 / 25 / 27 | 21.0.13.0.3, 25.0.5.0.3, 27.0.1.0.3 and earlier | 21.0.13.1, 25.0.5.1, 27.0.1.1 |
| Oracle Java 8 Performance Pack | 8u511b33-perf | 8u513 |
| Amazon Corretto | earlier builds | 17.0.21.1.2, 21.0.13.1.2, 25.0.5.1.2, 27.0.1.1.4 |
| Azul Zulu | earlier builds | 17.70.201, 21.54.201, 25.38.201, 27.30.201 |
| Red Hat build of OpenJDK | 17.0.6 and later | not yet released when checked; see RHSB-2026-018 |
| Eclipse Temurin, Microsoft, BellSoft Liberica | affected | no fixed builds listed when checked |
Sources: Oracle, CERT-EU and the vendor table compiled by The Hacker News. Check your vendor’s page before deploying. [3][4][5][7]
What defenders should look for
The Hacker News, summarising researchers, lists these signals. None proves compromise, and their absence does not prove safety. [5]
- Base64 tokens of 32 or more characters that end in
=and whose length is not a multiple of four, especially in Authorization headers. - Bursts of
IllegalArgumentExceptionthrown fromjava.util.Base64$Decoder. - Unexplained
hs_err_pid*.logcrash files or repeated JVM restarts on Jira, Confluence, Jenkins, Keycloak or similar services.
How to investigate
These commands are read-only and come from Calif, CERT-EU and The Hacker News. Not tested by MAG212. [1][4][5]
Check whether a Linux host’s CPU has all four required features. If any one is missing, the vulnerable routine does not run:
grep -m1 '^flags' /proc/cpuinfo \
  | tr ' ' '\n' \
  | grep -E '^(avx512f|avx512bw|avx512vbmi|bmi2)$'
Check the Java version and whether the Base64 intrinsic is enabled. Run these with the same java binary and options your service uses, including any runtime bundled inside an application:
java -version
java -XX:+PrintFlagsFinal -version | grep UseBASE64Intrinsics
Start with internet-facing identity providers, CI servers, artifact repositories and ticketing systems.
How to contain and remediate
- Patch: install a fixed build from your Java vendor and from any vendor whose product bundles Java. [3][4]
- If no fixed build exists yet, apply a temporary workaround (see below); both options change JVM behaviour and need a restart. [4]
- Restart every JVM and rebuild and redeploy container images; patching the host alone does not update images. [4][5]
- Preserve evidence if you saw crash bursts or suspicious Base64 traffic before patching: keep
hs_err_pidfiles, application logs and proxy logs, and investigate the host for follow-on activity.
Temporary workarounds
These JVM startup options change system behaviour. Not tested by MAG212. Disable only the vulnerable Base64 fast path: [4]
-XX:+UnlockDiagnosticVMOptions -XX:-UseBASE64IntrinsicsOr, on x86-64 hosts only, disable AVX-512 entirely. It can cost performance, and ARM64 JVMs will not start with it: [1][4]
-XX:UseAVX=2Upwind reports that using -XX:DisableIntrinsic=_base64_decodeBlock on its own stops Java from starting. Remove workaround flags once a fixed build is installed. [5]
How to verify recovery
java -versionon each restarted service shows a fixed build, orPrintFlagsFinalshowsUseBASE64Intrinsicsset to false where the workaround is in place. [4]- Running containers come from rebuilt images, not cached ones.
- Crash files and decoder exception bursts stop after the change.
Prevention and awareness
- For administrators: keep an inventory of every Java runtime, including those bundled inside vendor products and container images, so a runtime bug can be scoped in minutes rather than days.
- For developers: decoding attacker-controlled data before authentication enlarges the pre-login attack surface. Authenticate first where the protocol allows it.
- For decision-makers: budget for coordinated restart windows. A Java patch is only applied when every JVM has been restarted.
Related on MAG212 CYBER
- MAG212 CYBER Daily, 18 November 2026: One equals sign too many (full issue and PDF)
- MAG212 CYBER Daily, 17 November 2026: Keys that outlived the job
- MAG212 CYBER Daily, 16 November 2026: The boxes nobody patches
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] Calif, “Java4Shell (CVE-2026-114938) technical write-up“, 17 Nov 2026.
- [2] OpenJDK Vulnerability Group, “OpenJDK vulnerability advisory 2026-11-17“, 17 Nov 2026.
- [3] Oracle, “Critical Security Patch Update, November 2026“, 17 Nov 2026.
- [4] CERT-EU, “Security Advisory 2026-021: Java SE and OpenJDK (PDF)“, 17 Nov 2026.
- [5] The Hacker News, “Java4Shell enables pre-auth RCE in Jira, Jenkins, Keycloak and more“, 17 Nov 2026.
- [7] Red Hat, “Security bulletin RHSB-2026-018 (Java4Shell)“, 17 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 18 November 2026, 6:00 AM PT.