
One Equals Sign Too Many: MAG212 CYBER Daily, November 18, 2026
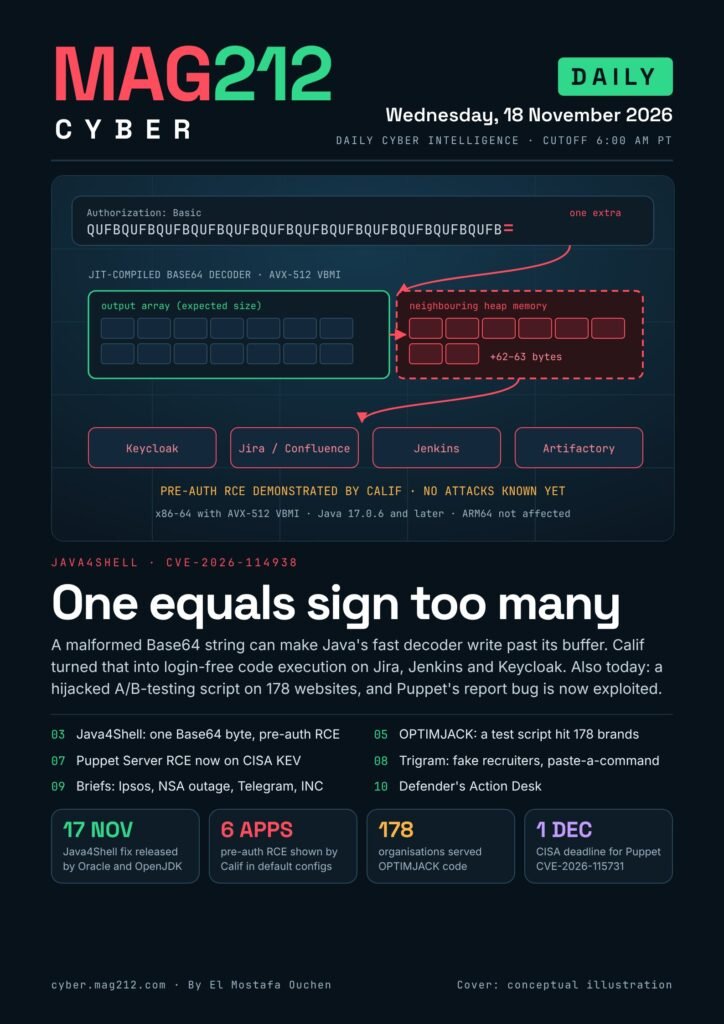
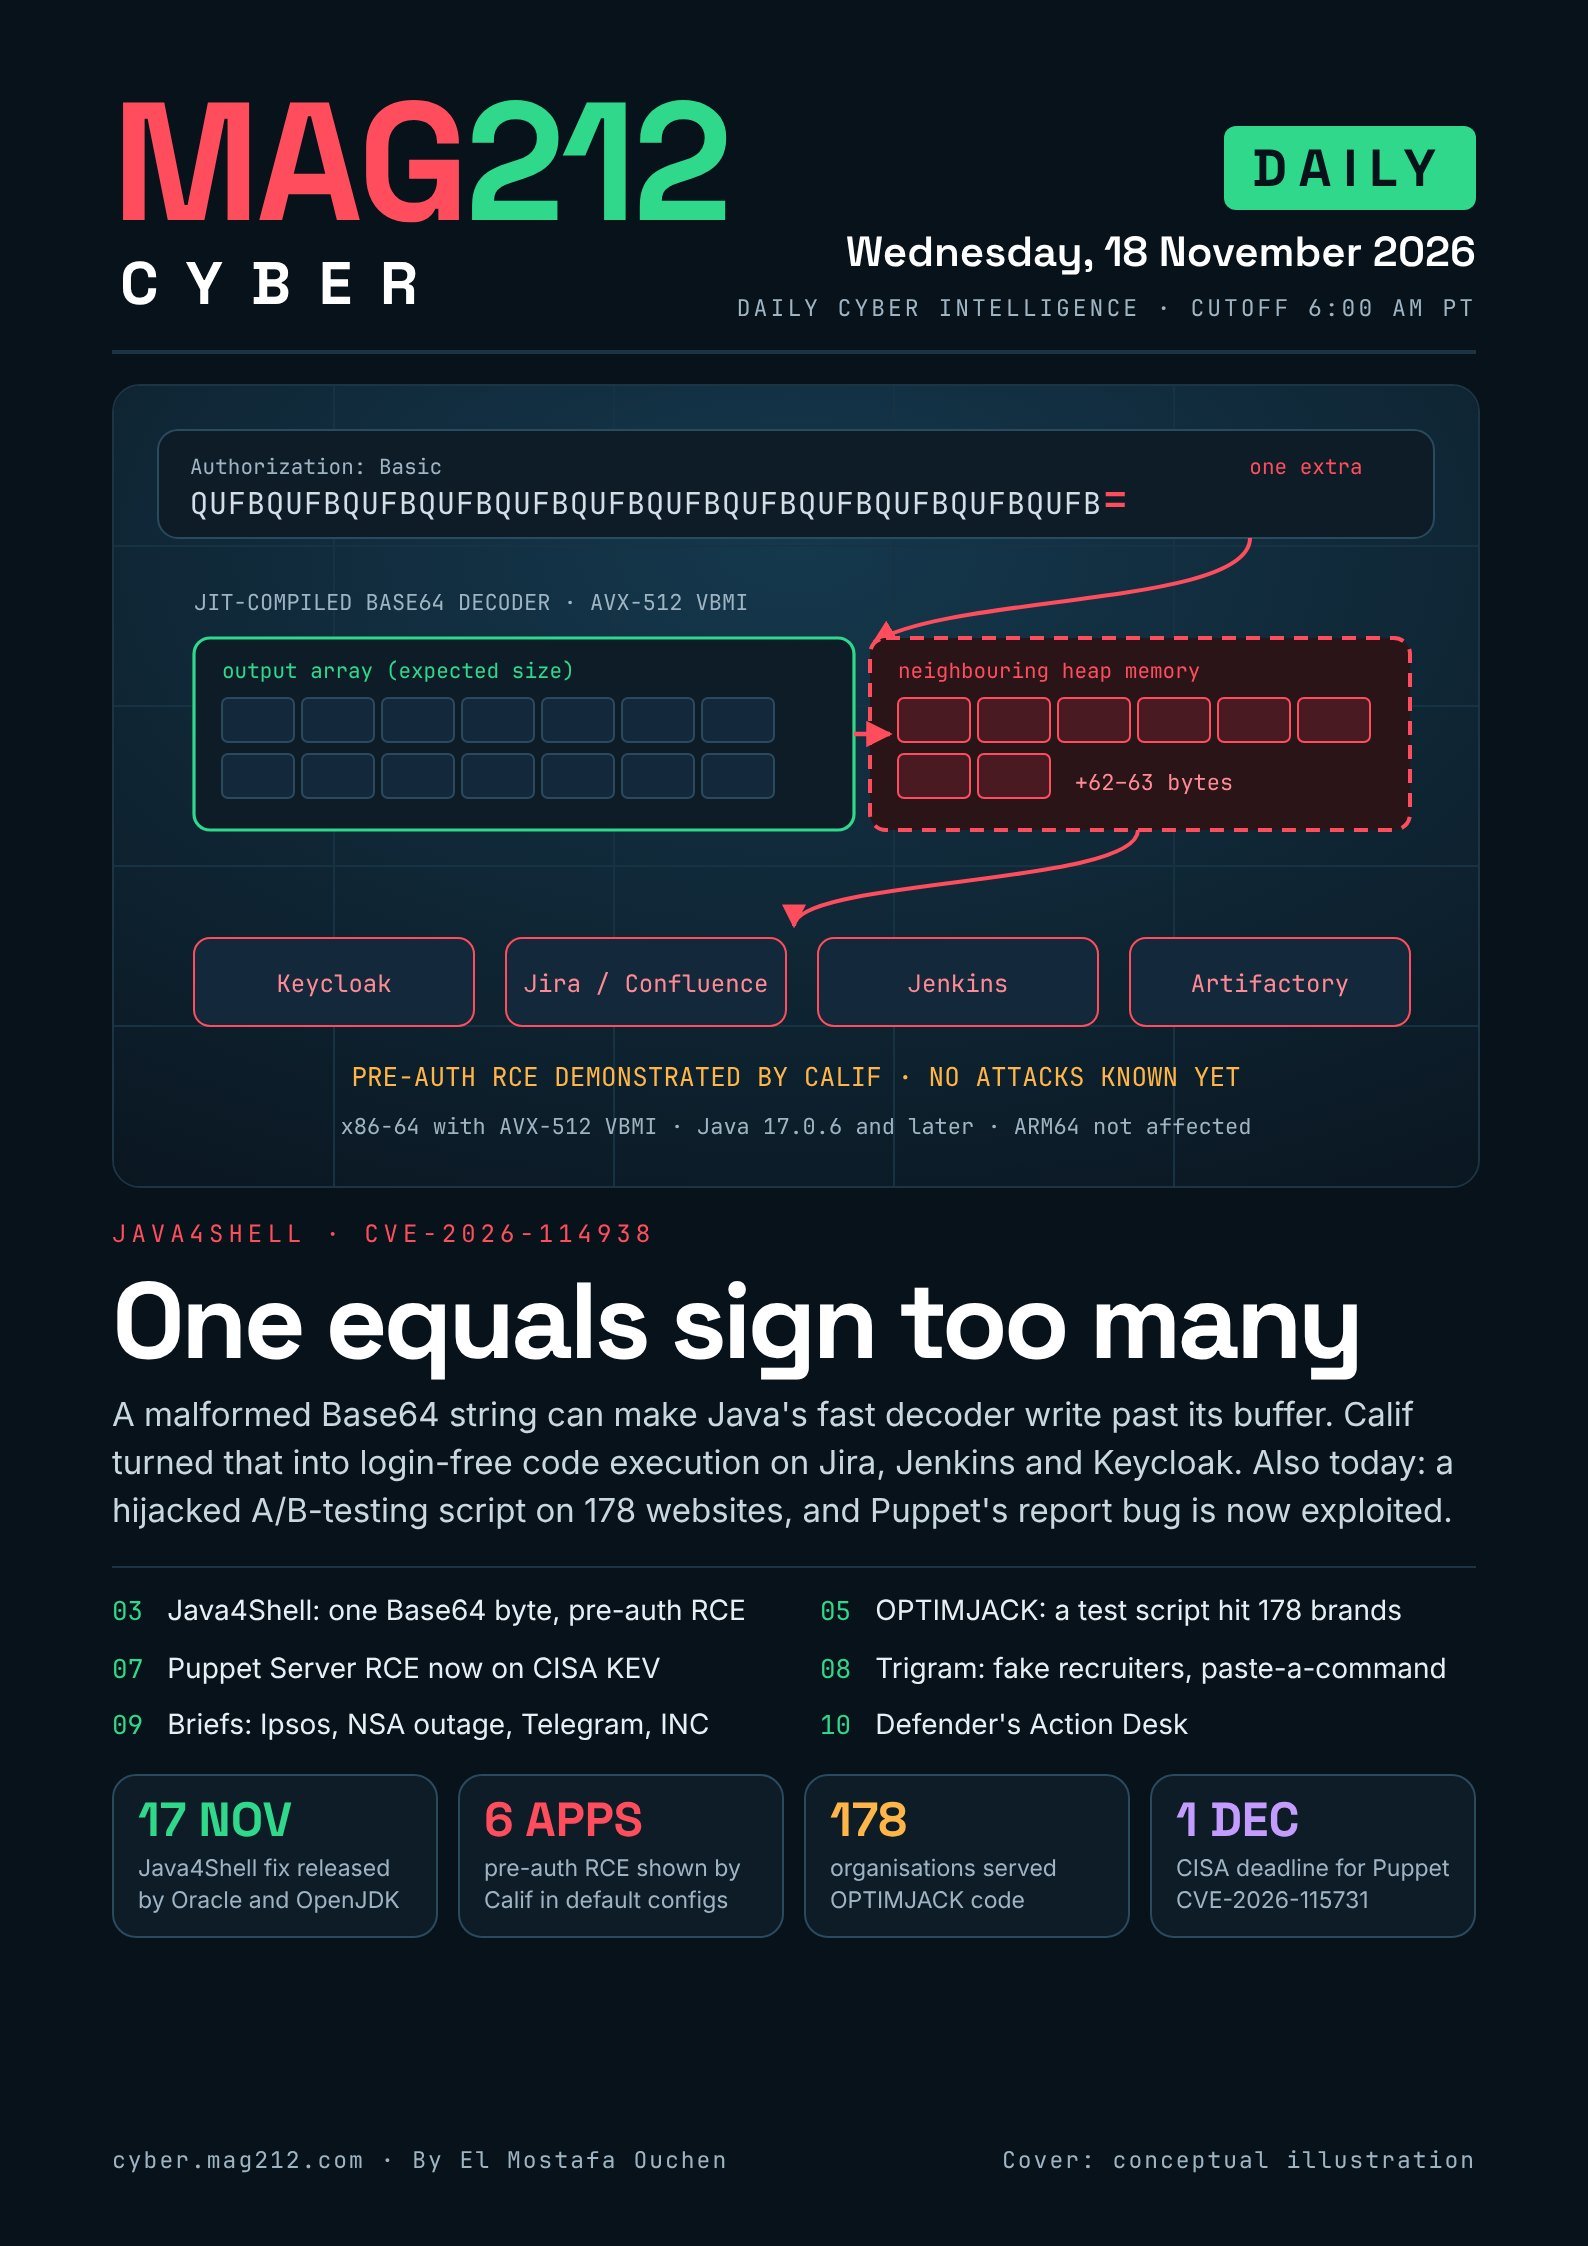
MAG212 CYBER · Daily Cyber Intelligence · Wednesday, November 18, 2026. A malformed Base64 string can make Java’s AVX-512 decoder write past its buffer; Calif turned that into login-free code execution on Jira, Jenkins and Keycloak, and Oracle and OpenJDK shipped fixes on 17 November. A hijacked Optimizely script served a crypto clipper, card skimmer and iPhone exploit loader to visitors of 178 organisations. CISA says Puppet Server’s report-deserialization flaw is now exploited, and Stormshield’s Trigram campaign lures developers into pasting an infostealer.
The three priority actions
- Patch Java on x86-64 servers first. Start with internet-facing Jira, Confluence, Jenkins, Keycloak, Artifactory and PingFederate. Fixed Oracle builds are 17.0.21.1, 21.0.13.1, 25.0.5.1 and 27.0.1.1; where no fixed build exists, set the Base64-intrinsic workaround flag and restart.
- Patch or isolate Puppet and OpenVox servers today. Upgrade to PE 2023.8.13, 2025.12.1 or 2026.0.1, or OpenVox Server 9.2.0 / 8.18.0. Turn off naïve autosigning and restrict who can reach the server.
- If your site runs Optimizely Web, read every Project JavaScript field. One loader variant is base64-encoded and another is inline with an eval fallback, so a domain search is not enough. Treat cards entered on affected checkouts as compromised.
Inside this issue
- Java4Shell (CVE-2026-114938): How One Base64 Byte Leads to Pre-Auth RCE in Jira, Jenkins and Keycloak, and How to Patch (p. 3–4)
- OPTIMJACK: How a Hijacked Optimizely Script Served a Crypto Clipper, Card Skimmer and iPhone Exploit Loader to 178 Websites (p. 5–6)
- Puppet Server RCE (CVE-2026-115731) Is Now Exploited: How the Report Deserialization Flaw Works and How to Fix It (p. 7)
- Trigram Campaign: Fake Recruiters, a Pasted Command and an Infostealer Aimed at AI and Blockchain Developers (p. 8)
- Also Today: Ipsos Investigates Breach, NSA Network Outage, Telegram Widget Sandbox Bypasses and an INC/Lynx Extradition (p. 9)
Also in the PDF: the Defender’s Action Desk (p. 10), an awareness lesson, “Never paste a command a website gives you” (p. 11), and 28 linked sources (p. 12).
Flip through the edition
How we verified this issue: stories were checked against primary sources where reachable (Calif, CERT-EU, Oracle, Unit 42, Stormshield, CISA and Ipsos), with a research cutoff of 6:00 AM PT on 18 November. The OpenJDK advisory and SecurityWeek’s Puppet article did not load; fixed versions come from Oracle, CERT-EU and other reporting and are labelled. OPTIMJACK iOS infections are not confirmed. Every command is marked not tested by MAG212.
Previous issues
- Keys that outlived the job, the 17 November daily.
- The boxes nobody patches, the 16 November daily.
- All MAG212 CYBER magazine issues