
Also Today: KEV Deadline for UnrealIRCd and Check Point, Coles Incident, Rspamd 4.3.0 and Intune Remote Lock
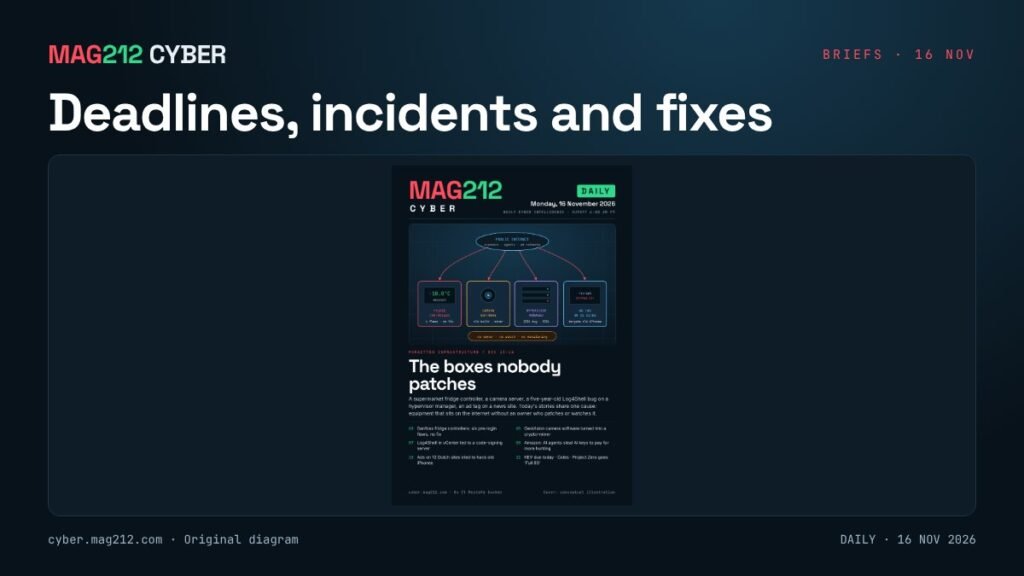
From the MAG212 CYBER Daily, 16 November 2026. Facts are sourced below; analysis is marked as MAG212’s.
Status: Facts below are confirmed by the cited official sources unless marked otherwise. [1][2][5][6]
CISA KEV: UnrealIRCd and Check Point due today
CISA added two vulnerabilities to its Known Exploited Vulnerabilities catalog on 13 November, based on evidence of active exploitation: [3]
| CVE | Product | Added | Due |
|---|---|---|---|
| CVE-2026-114713 | UnrealIRCd (improper neutralisation of delimiters) | 13 Nov | 16 Nov |
| CVE-2026-123039 | Check Point multiple products (incorrect permission assignment) | 13 Nov | 16 Nov |
The due date binds US federal civilian agencies, but anyone running these products should treat it as a strong signal. Our earlier articles have the details: [UnrealIRCd CVE-2026-114713](https://cyber.mag212.com/unrealircd-cve-2026-114713-kev-due-november-16/) and the Check Point coverage in our 14 November Weekly. Confirm the fix is installed and that the log hunt has been completed. [4]
Why this matters
None of these four items needs a long feature, but each needs an action from someone today: a patch to confirm, a scam wave to watch for, a mail-filter upgrade to test, or a lost-device process to update. (MAG212 analysis)
Coles investigates a cyber security incident
Australian supermarket group Coles says it is investigating a cyber security incident and is working with global cyber security experts to contain and secure its IT environment, and with the Australian Cyber Security Centre. [1][2]
- Operations: stores and online shopping continue normally.
- Data: based on its investigation so far, Coles says it has found no evidence that customer, team or supplier data has been compromised. That is an interim finding, not a final one.
- Services: no indication that Flybuys accounts are affected; Coles Plus, Coles Plus Delivery and QuiteLike subscriptions are working, and gift cards still work. A small number of Liquorland click-and-collect orders have problems that Coles is investigating; it has not linked them to the incident.
- Unknown: the attacker, the entry method and whether ransomware was involved. [1][2]
Coles reminds customers that it will never ask for a password or other sensitive account information through an unsolicited email or SMS. Expect scammers to use the news as a lure. [1]
Rspamd 4.3.0 stops forwarded mail from softening DMARC rejects
The open-source spam filter’s new release changes how it handles ARC, the mechanism forwarders use to vouch for earlier authentication results. Previously, ARC sets added after a genuine one could weaken a DMARC reject. Rspamd now trusts a forwarder only for what it vouches for, and requires the forwarder’s own dmarc=pass before changing a DMARC result. [5]
The release also fixes:
- sender-controlled text placed unescaped into the Authentication-Results header, which let a sender make a fake “dmarc=pass” look genuine;
- a worker crash triggered by a single unauthenticated HTTP request (a header line without a colon, or an empty Deliver-To header);
- a use-after-free in the milter proxy in versions 4.0.0 to 4.2.3 (3.14 is not affected). [5]
Scoring also changes: SPF evaluates terms in record order, DKIM fails RSA keys under 1024 bits and rejects duplicate tags and l=0 on messages with a body. Test local scores, scripts that read symbol options and mixed-case signing-domain maps before deploying. [5]
Microsoft previews Intune remote lock for Windows
Microsoft is previewing a way for administrators to lock a lost, stolen or compromised Windows device through Intune without wiping it. It applies to Windows 11, Windows 10 and Windows Server 2016, 2019 and 2022 (Enterprise, Education or Pro), on devices that are Entra joined, hybrid joined or MDM-enrolled. [6]
- How it works: a custom configuration profile with
LockStateset to 1 is assigned to a device group; the lock applies at the next Intune check-in. SettingLockStateto 0 through an unlock group reverses it. - Behaviour: active sessions end, sign-in options are hidden, and the lock survives restarts and works offline. Only an Intune instruction can unlock it.
- Limits: user accounts stay valid on other devices, the device is not isolated from the network, and Windows Recovery Environment, Safe Mode and booting from USB are not blocked. Keep BitLocker enabled and revoke sessions in Entra ID. [6]
What to do today
- Confirm the UnrealIRCd and Check Point fixes and hunts are complete.
- Warn customer-facing and finance teams about Coles-themed scams if you operate in Australia.
- Plan and test the Rspamd 4.3.0 upgrade if you run Rspamd.
- Add remote lock to your lost-device runbook once it reaches general availability, alongside account disablement.
Related on MAG212 CYBER
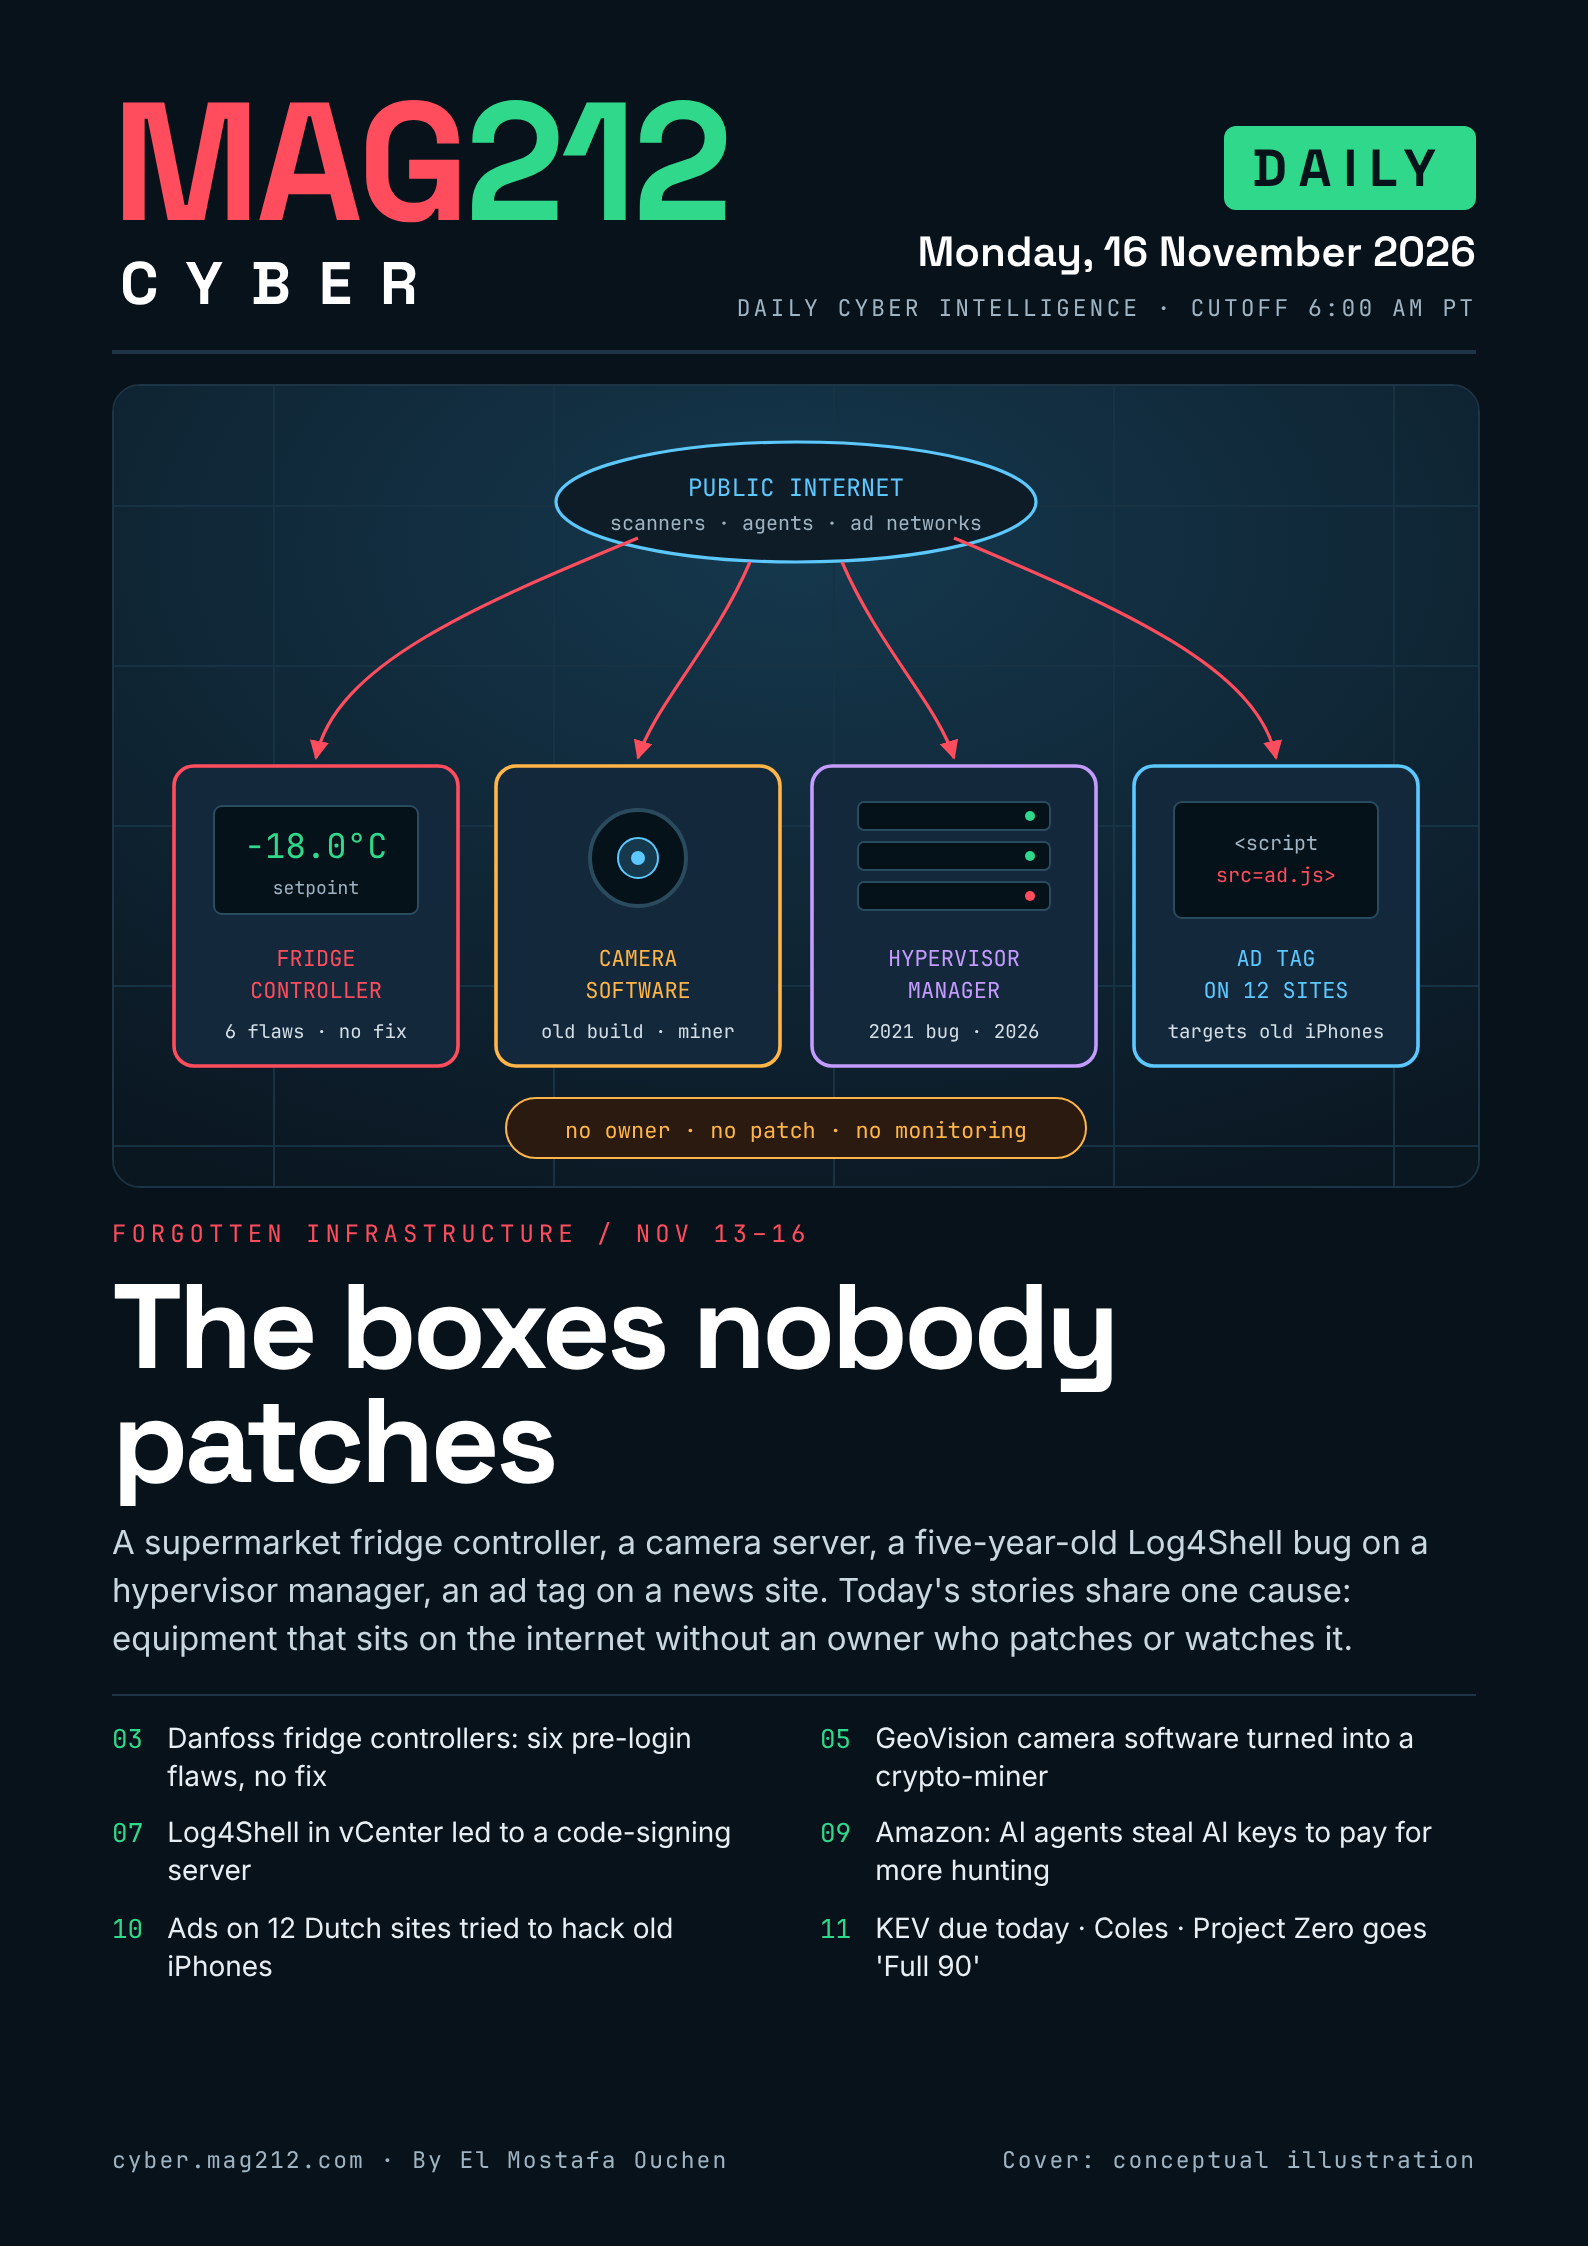
- MAG212 CYBER Daily, 16 November 2026: The boxes nobody patches (full issue and PDF)
- MAG212 CYBER Daily, 15 November 2026: Machine speed, human gaps
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] Coles Group, “Updates: cyber security incident“, 16 Nov 2026.
- [2] CybersecurityNews, “Australia's supermarket chain Coles investigates cyber security incident“, 16 Nov 2026.
- [3] CISA, “CISA adds two known exploited vulnerabilities to catalog“, 13 Nov 2026.
- [4] MAG212 CYBER, “UnrealIRCd CVE-2026-114713 exploited: patch by November 16“, 15 Nov 2026.
- [5] Help Net Security, “Rspamd 4.3.0 stops forwarded mail from softening DMARC rejects“, 16 Nov 2026.
- [6] Help Net Security, “Microsoft previews remote lock for lost or stolen Windows devices“, 16 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 16 November 2026, 6:00 AM PT.