
Ruby2Shell (CVE-2026-132825) and the November PHP Security Release: What to Update and Why “bundle update” Is Not Enough
From the MAG212 CYBER Daily, 20 November 2026. Every command is copied from official documentation or the cited analysis and was not tested by MAG212; run it only on systems you are authorised to administer.
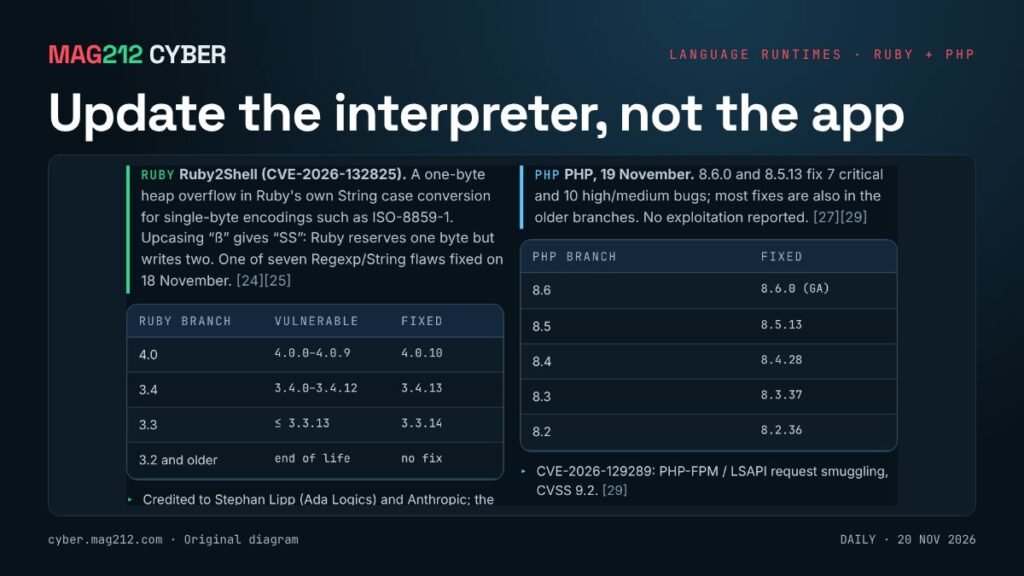
Status: Ruby fixed on 18 November 2026 (4.0.10, 3.4.13, 3.3.14); Ruby 3.2 and older get no fix. PHP fixed on 19 November (8.6.0, 8.5.13, 8.4.28, 8.3.37, 8.2.36). No exploitation reported for either. Ruby2Shell’s severity varies by source: CVSS 7.4 per SecurityWeek, “critical” per The Hacker News. [1][2][3][4][6]
Ruby: what happened
On 18 November the Ruby project fixed seven memory-safety flaws in Regexp and String case conversion and warned it was “aware of PoCs” showing that some can lead to remote code execution. The most discussed is Ruby2Shell, CVE-2026-132825 (GHSA-34m4-m9fh-gqp5), credited to Stephan Lipp of Ada Logics and Anthropic. The name comes from Veria Labs’ research. [1][3]
Why this matters
These bugs live in the language runtimes themselves, which sit under huge numbers of web applications. Updating application dependencies does nothing; the interpreter in every server, worker and container image has to be replaced. Proofs of concept exist for some of the Ruby flaws, and attackers have targeted PHP heavily this year. (MAG212 analysis)
The Ruby bug
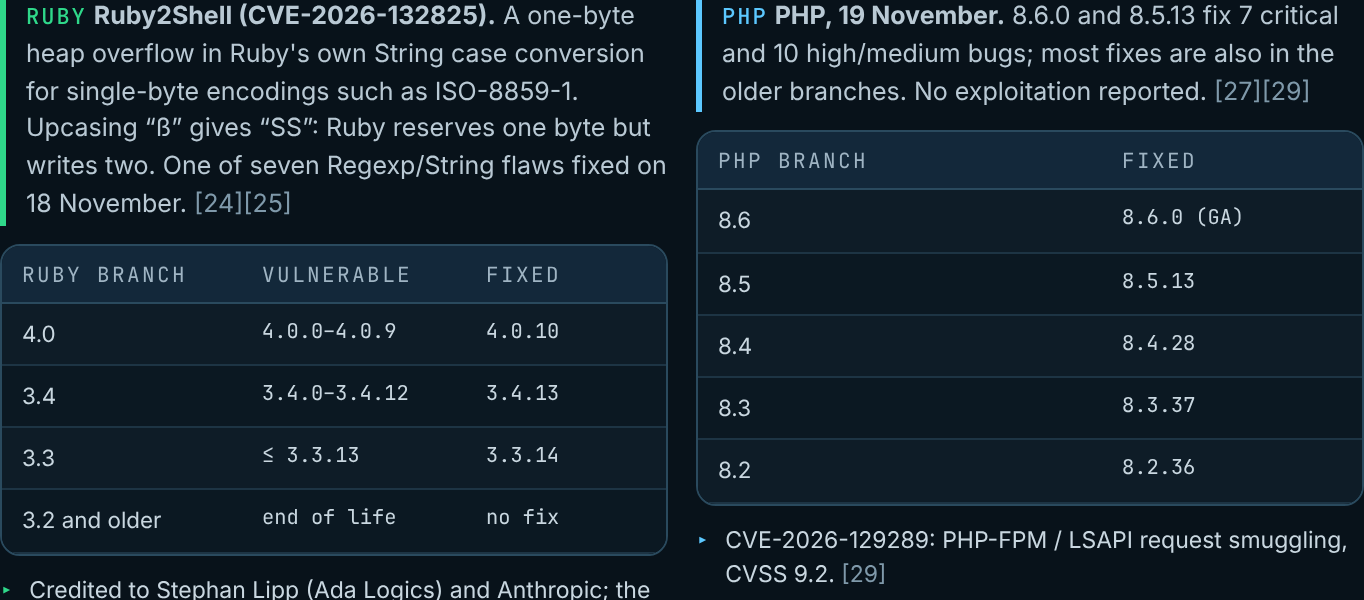
In some single-byte encodings, such as ISO-8859-1 and Windows-1252, changing the case of a string can write one byte past the output buffer. Upcasing “ß” produces “SS”: Ruby checks there is room for one byte but writes two. Researchers say it can be reached in some web applications that change the case of incoming text. [2][3]
Exploitation is not easy. watchTowr says turning it into code execution in production needs a non-glibc memory allocator, specific runtime configuration and application logic, plus a way around address-space randomisation. SecurityWeek expects malformed requests most likely to cause crashes. Veria Labs plans to publish its proof of concept about a week after disclosure. [2][3]
| Ruby branch | Vulnerable | Fixed |
|---|---|---|
| 4.0 | 4.0.0–4.0.9 | 4.0.10 |
| 3.4 | 3.4.0–3.4.12 | 3.4.13 |
| 3.3 | 3.3.13 and earlier | 3.3.14 |
| 3.2 and older | end of life | no fix |
Source: ruby-lang.org. The advisory lists no workaround. GitHub Enterprise Server is affected; GitLab and others have patched. [1][2][3]
PHP: what happened
On 19 November PHP released 8.6.0 and 8.5.13, fixing 7 critical and 10 high or medium bugs. Most fixes also landed in 8.4.28, 8.3.37 and 8.2.36. Highlights: [4][5][6]
- CVE-2026-129289: request smuggling in PHP-FPM and LSAPI, CVSS 9.2. [6]
- CVE-2026-115560: a session deserialization bug that can lead to code execution, but only where
session.serialize_handleris changed at runtime. Aikido’s stop-gap is to setsession.upload_progress.enabled=0. [5] - CVE-2026-129481 and CVE-2026-129182: related to PHP2Shell, the widely exploited October bug. [6]
How to check
These are standard version checks, a MAG212 suggestion to compare with the fixed releases above. They were not tested by MAG212.
ruby -vbundle exec ruby -vdocker run --rm IMAGE ruby -vphp -vphp -i | grep upload_progress.enabledReplace IMAGE with each of your container images.
Why “bundle update” is not enough
- Ruby2Shell lives in the interpreter binary. Updating gems or Rails does not touch it.
- Rebuild base images, redeploy and restart long-running workers such as Sidekiq.
- For PHP, update the PHP-FPM or mod_php package and restart the pool; application code changes do not help.
- On managed platforms (PaaS, hosted CI), confirm the provider has rolled out the new runtime.
- Ruby 3.2 apps get no fix: plan the upgrade now.
Related on MAG212 CYBER
- MAG212 CYBER Daily, 20 November 2026: The keys to vSphere (full issue and PDF)
- MAG212 CYBER Daily, 19 November 2026: A ten-year-old counter
- MAG212 CYBER Daily, 18 November 2026: One equals sign too many
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] ruby-lang.org, “Multiple vulnerabilities in Regexp and String case conversion“, 18 Nov 2026.
- [2] SecurityWeek, “Ruby patches Ruby2Shell vulnerability that could lead to RCE“, 19 Nov 2026.
- [3] The Hacker News, “Ruby releases fixes for 7 regex and string flaws“, 19 Nov 2026.
- [4] PHP, “PHP 8 ChangeLog“, 19 Nov 2026.
- [5] Aikido, “PHP security release, 19 November 2026 (CVE-2026-115560)“, 19 Nov 2026.
- [6] SecurityWeek, “PHP patches seven critical RCE vulnerabilities“, 19 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 20 November 2026, 6:00 AM PT.