
A Ten-Year-Old Counter: MAG212 CYBER Daily, November 19, 2026
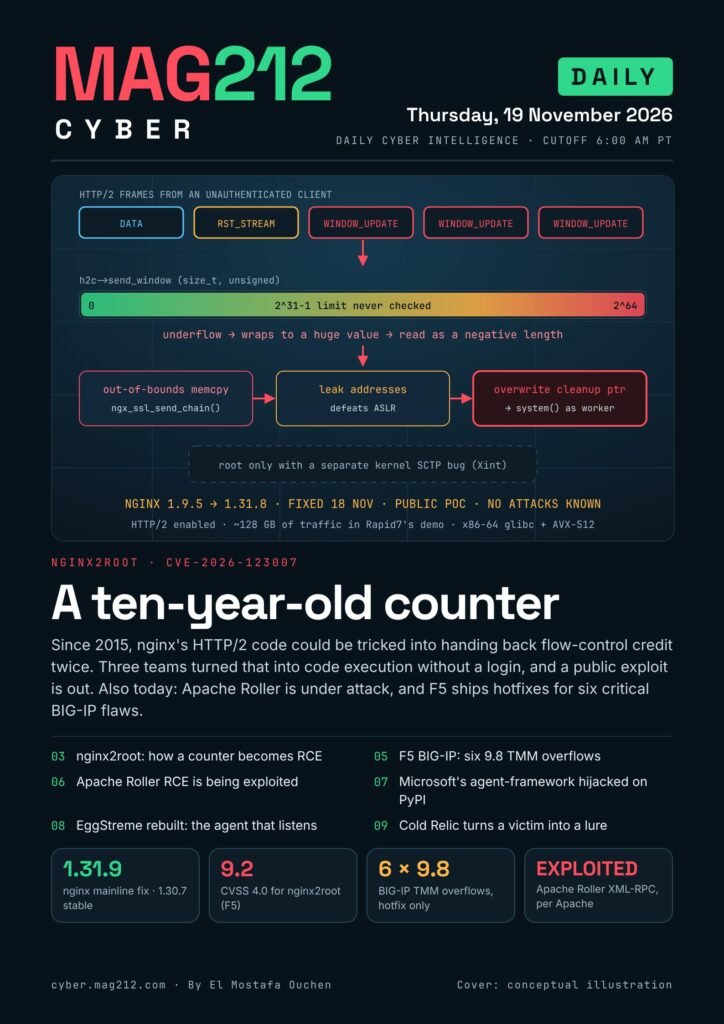
MAG212 CYBER · Daily Cyber Intelligence · Thursday, November 19, 2026. A bug present in nginx’s HTTP/2 code since 2015 lets an unauthenticated attacker run code as the worker user; nginx 1.31.9 and 1.30.7 fix it, and a public proof of concept exists. F5 shipped hotfixes for six critical BIG-IP flaws, Apache says its Roller XML-RPC deserialization bug is being actively exploited, and two poisoned releases of Microsoft’s agent-framework package on PyPI stole cloud and CI tokens. Plus: EggStreme’s silent agents and how Cold Relic turned one victim’s staff into a lure.
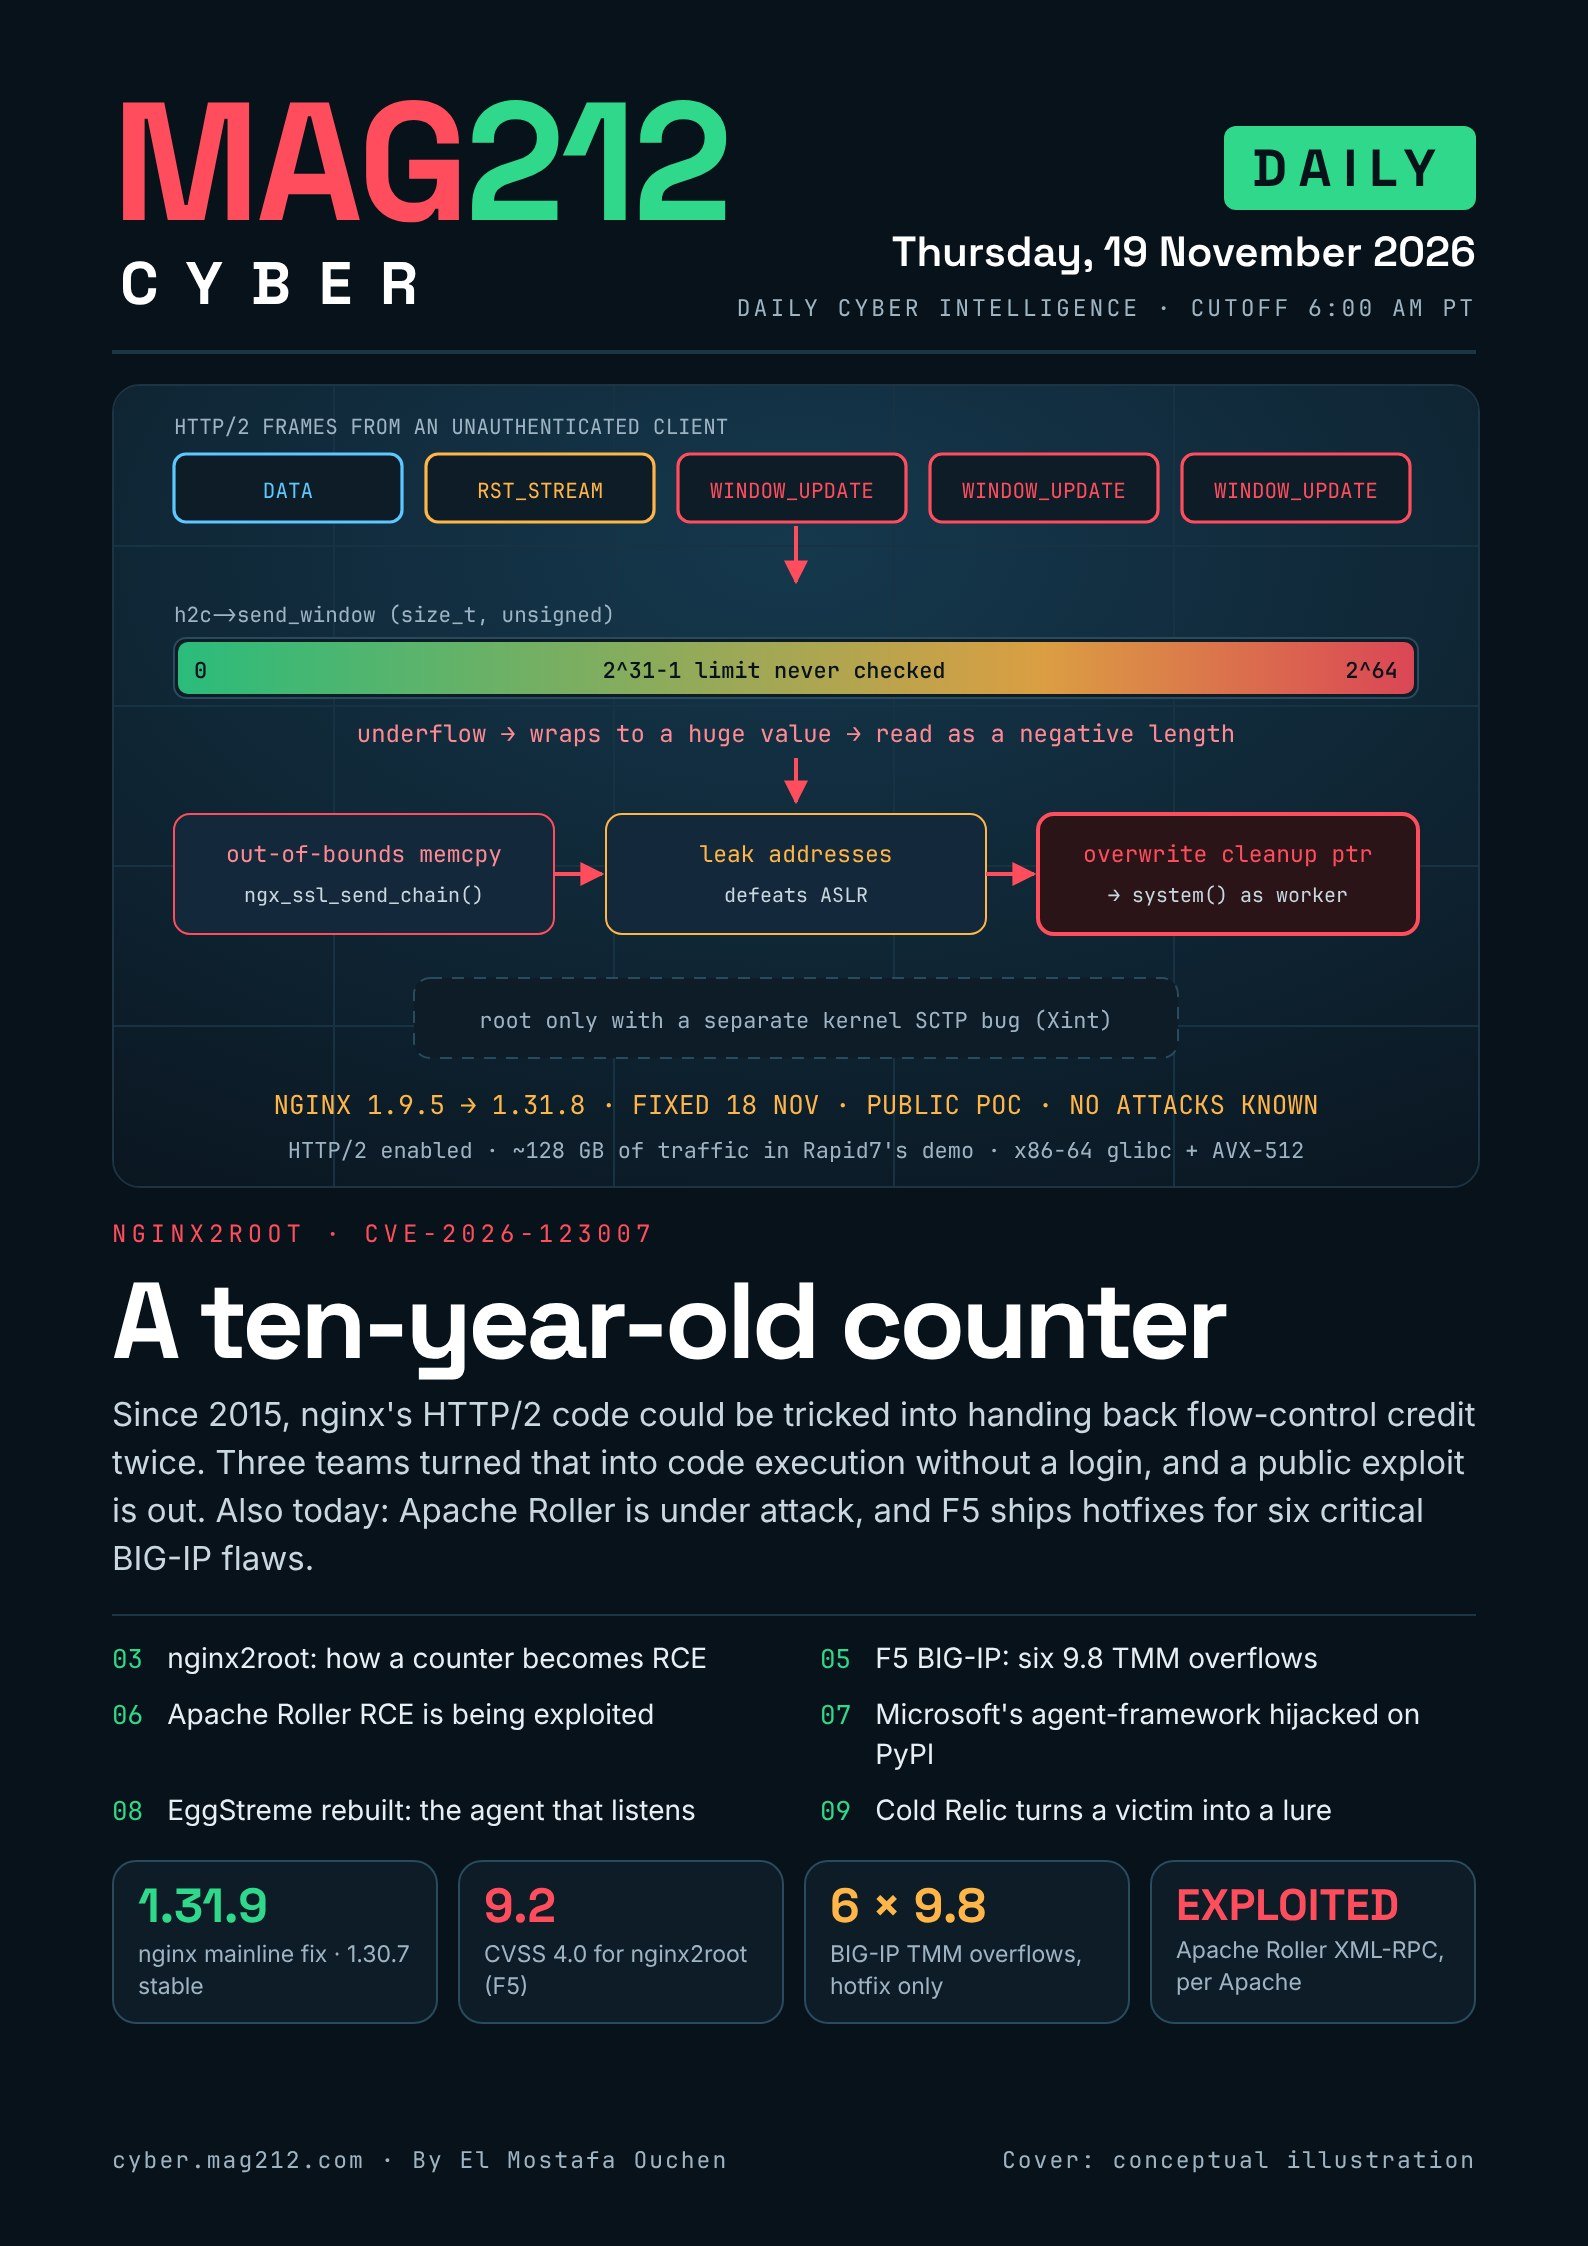
The three priority actions
- Patch nginx to 1.31.9 / 1.30.7 (or your distro's fix) and fully restart it. A reload leaves the old binary running. If you cannot patch yet, turn HTTP/2 off on internet-facing listeners, and check NGINX Plus, ingress and appliance vendors separately.
- Upgrade Apache Roller to 6.1.7, or cut off XML-RPC today. Set enabledForExtensions to false in WEB-INF/web.xml or remove the servlet mapping, then restart. Treat exposed servers as possibly compromised.
- If agent-framework 1.26.1 or 1.26.2 was installed anywhere, rotate every secret it could see. Pin to 1.26.0, look for the two .pth files, and revoke Azure, GitHub, DevOps, npm, PyPI and Docker tokens on those machines and CI runners.
Inside this issue
- nginx2root (CVE-2026-123007): How a Ten-Year-Old nginx HTTP/2 Bug Leads to Pre-Auth RCE, and How to Patch (p. 3–4)
- F5 BIG-IP: Six Critical TMM Flaws That Depend on One iRule or APM Setting, and How to Triage Them (p. 5)
- Apache Roller CVE-2026-129448: Pre-Auth XML-RPC Deserialization RCE Is Being Exploited. What to Do Now (p. 6)
- Microsoft's agent-framework PyPI Package Hijacked: Two Releases Stole Cloud and CI Secrets. How to Check and Respond (p. 7)
- EggStreme Malware Rebuilt: Passive Agents That Listen on Port 5060, New Ciphers and How to Hunt Them (p. 8)
- Cold Relic (COLDRIVER): How a Russian Group Turned One Victim's Staff Into a Lure for the Next (p. 9)
- Fugaku Supercomputer Intrusion, Equinor Cyberattack, Java4Shell Exploitation Attempts, PHP and Ruby Fixes (p. 10)
Also in the PDF: the Defender’s Action Desk (p. 11), an awareness lesson, “When a partner messages you out of the blue” (p. 12), and 32 linked sources (p. 13).
Flip through the edition
How we verified this issue: stories were checked against primary sources where reachable (nginx.org, Rapid7, Wiz, Xint, CIRCL, Ubuntu, the Apache Roller project, Bitdefender), with a research cutoff of 6:00 AM PT on 19 November. F5’s advisories, Google’s Cold Relic post and CISA’s site did not load; those sections rely on The Hacker News, Censys and SecurityWeek and say so. Every command is marked not tested by MAG212.
Previous issues
- One equals sign too many, the 18 November daily.
- Keys that outlived the job, the 17 November daily.
- All MAG212 CYBER magazine issues