
F5 BIG-IP: Six Critical TMM Flaws That Depend on One iRule or APM Setting, and How to Triage Them
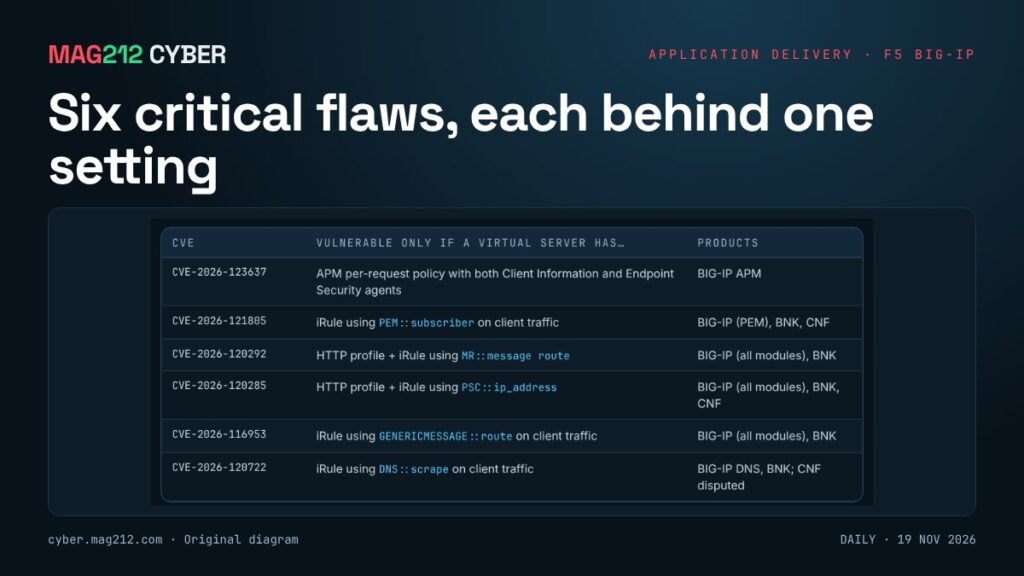
From the MAG212 CYBER Daily, 19 November 2026. Every command is copied from official documentation or the cited analysis and was not tested by MAG212; run it only on systems you are authorised to administer.
Status: Disclosed on 18 November 2026. All six are rated CVSS 3.1 9.8 and CVSS 4.0 9.3. Each needs a specific configuration on a virtual server. Fixes are engineering hotfixes only; F5 lists no workarounds. No exploitation and no public proof of concept had been reported as of 18 November. [1][2]
What happened
F5 published six stack-based buffer overflows in the Traffic Management Microkernel (TMM), the BIG-IP data plane that handles application traffic. An unauthenticated attacker sending crafted traffic to an affected virtual server can crash TMM, interrupting traffic until it restarts, and may be able to run code. F5 says the management interface and control plane are not exposed through these flaws. [1][2]
The six are part of a security notification of 22 advisories, ten of them for NGINX. watchTowr researcher Sina Kheirkhah reported four of the six; F5 found the other two internally. [1]
Why this matters
BIG-IP appliances sit at the edge of many enterprises and carry traffic for critical applications. These flaws need no login, and a crash of the traffic engine drops traffic for everything behind it. F5 offers only engineering hotfixes and no workarounds, which makes many teams hesitate. Knowing whether your iRules use the trigger commands tells you how urgent the hotfix really is. (MAG212 analysis)
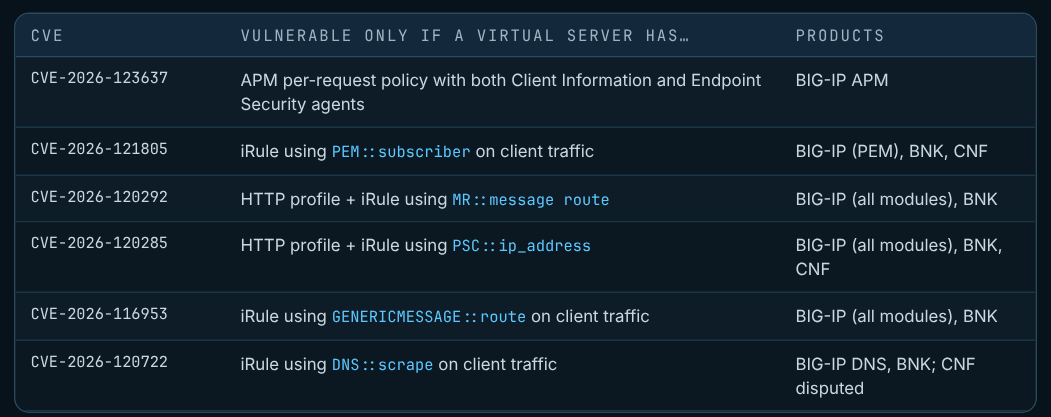
Which configurations are affected
| CVE | Vulnerable only if a virtual server has | Products |
|---|---|---|
| CVE-2026-123637 | APM per-request policy with both Client Information and Endpoint Security agents | BIG-IP APM |
| CVE-2026-121805 | iRule using PEM::subscriber on client traffic | BIG-IP (PEM), BIG-IP Next for Kubernetes (BNK), CNF |
| CVE-2026-120292 | HTTP profile plus iRule using MR::message route | BIG-IP (all modules), BNK |
| CVE-2026-120285 | HTTP profile plus iRule using PSC::ip_address | BIG-IP (all modules), BNK, CNF |
| CVE-2026-116953 | iRule using GENERICMESSAGE::route on client traffic | BIG-IP (all modules), BNK |
| CVE-2026-120722 | iRule using DNS::scrape on client traffic | BIG-IP DNS, BNK; CNF disputed |
Source: The Hacker News and Censys. F5’s own K-articles did not load for us. For CVE-2026-120722, F5’s advisory lists CNF as not vulnerable while the CVE record lists it as affected. Censys notes the records do not say whether the PEM or DNS module must be provisioned for the iRule-based flaws to apply. [1][2]
Affected branches are BIG-IP 21.1.x, 17.5.x and 17.1.x, and BNK and CNF 2.2.x to 2.4.x. F5 only evaluates versions under technical support, so a release missing from its tables is not confirmed safe. [1][2]
Fixes
| Branch | Engineering hotfix |
|---|---|
| BIG-IP 21.1.0 | BIGIP-21.1.0.4.0.19.3-ENG |
| BIG-IP 17.5.0 | BIGIP-17.5.1.11.0.61.12-ENG or BIGIP-17.5.1.10.0.80.35-ENG |
| BIG-IP 17.1.0 | BIGIP-17.1.3.7.0.21.4-ENG or BIGIP-17.1.3.6.0.14.20-ENG |
| BNK 2.2–2.4 | BNK-2.4.2-EHF1, BNK-2.3.4-EHF1, BNK-2.2.5-EHF1 |
| CNF 2.2–2.4 | CNF-2.4.2-EHF1, CNF-2.3.4-EHF1, CNF-2.2.5-EHF1 |
BIG-IP hotfix names come from F5’s records as compiled by Censys, which notes F5 amended some records on 18 November; BNK and CNF names come from The Hacker News. Check F5 directly before deploying. [1][2]
F5 warns that engineering hotfixes “do not undergo the extensive QA assessment of scheduled software releases” and carry no warranty. Systems already running a custom hotfix need a new combined one from F5 support. [1]
How to triage
This is a MAG212 suggestion, not an F5 procedure, and was not tested by MAG212. On a BIG-IP you administer, list iRules that use the five trigger commands, then see which virtual servers attach them:
tmsh list ltm rule one-line | grep -E 'PEM::subscriber|MR::message|PSC::ip_address|GENERICMESSAGE::route|DNS::scrape'tmsh list ltm virtual rulesA match on a virtual server that receives untrusted traffic makes the hotfix urgent. No match lowers the priority but does not remove it, because configurations change. Review APM per-request policies separately for the Client Information plus Endpoint Security combination. [1][2]
What defenders should look for
Neither F5 nor the researchers published indicators. Practical signals are unexpected TMM restarts and core files, failover events on HA pairs without an obvious cause, and spikes of malformed traffic to virtual servers that use the trigger iRules. A TMM crash on an affected configuration before you patch deserves investigation, not just a reboot.
Also in the batch
F5 fixed lower-rated BIG-IP flaws at the same time, including: [1]
- CVE-2026-125274 (CVSS 8.8): an authenticated iControl SOAP user with the Guest role or higher can send management requests that may run commands. Fixed in 21.1.0.3, 17.5.1.10 and 17.1.3.6; restrict SOAP to trusted networks.
- CVE-2026-120718 (CVSS 8.1): iControl REST tokens may not expire as expected. Scripts should delete their tokens when done.
- Four APM and SSL Orchestrator flaws (CVSS 7.5) that let unauthenticated attackers crash TMM in specific SAML, logon-page or policy-trace configurations.
Why this deserves attention
In September a different BIG-IP APM overflow, CVE-2026-94127, was added to CISA’s Known Exploited Vulnerabilities catalog. These six are not known to be exploited, but watchTowr’s involvement and the hotfix-only fix mean defenders should not assume a long quiet period. [1]
Prevention and awareness
Keep an inventory of iRules and which virtual servers use them; it turns advisories like this one into a five-minute check. Restrict BIG-IP management interfaces (SOAP, REST, the configuration utility) to trusted networks regardless of patch status, and plan hotfix installs with HA failover so a patch window does not become an outage.
Related on MAG212 CYBER
- MAG212 CYBER Daily, 19 November 2026: A ten-year-old counter (full issue and PDF)
- MAG212 CYBER Daily, 18 November 2026: One equals sign too many
- MAG212 CYBER Daily, 17 November 2026: Keys that outlived the job
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] The Hacker News, “F5 Warns 6 Critical BIG-IP Flaws Can Crash Traffic in Specific Setups, May Allow RCE“, 18 Nov 2026.
- [2] Censys, “Nov 18 Advisory: F5 BIG-IP iRule and APM TMM Remote Code Execution“, 18 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 19 November 2026, 6:00 AM PT.