
Cyber Briefs, 20 November 2026: CISA KEV Adds Four Exploited Flaws, N-able Cloud Breach, JPMorgan and Visa Vendor Leak
From the MAG212 CYBER Daily, 20 November 2026. Facts are sourced below; analysis is marked as MAG212’s.
CISA adds four exploited flaws to KEV
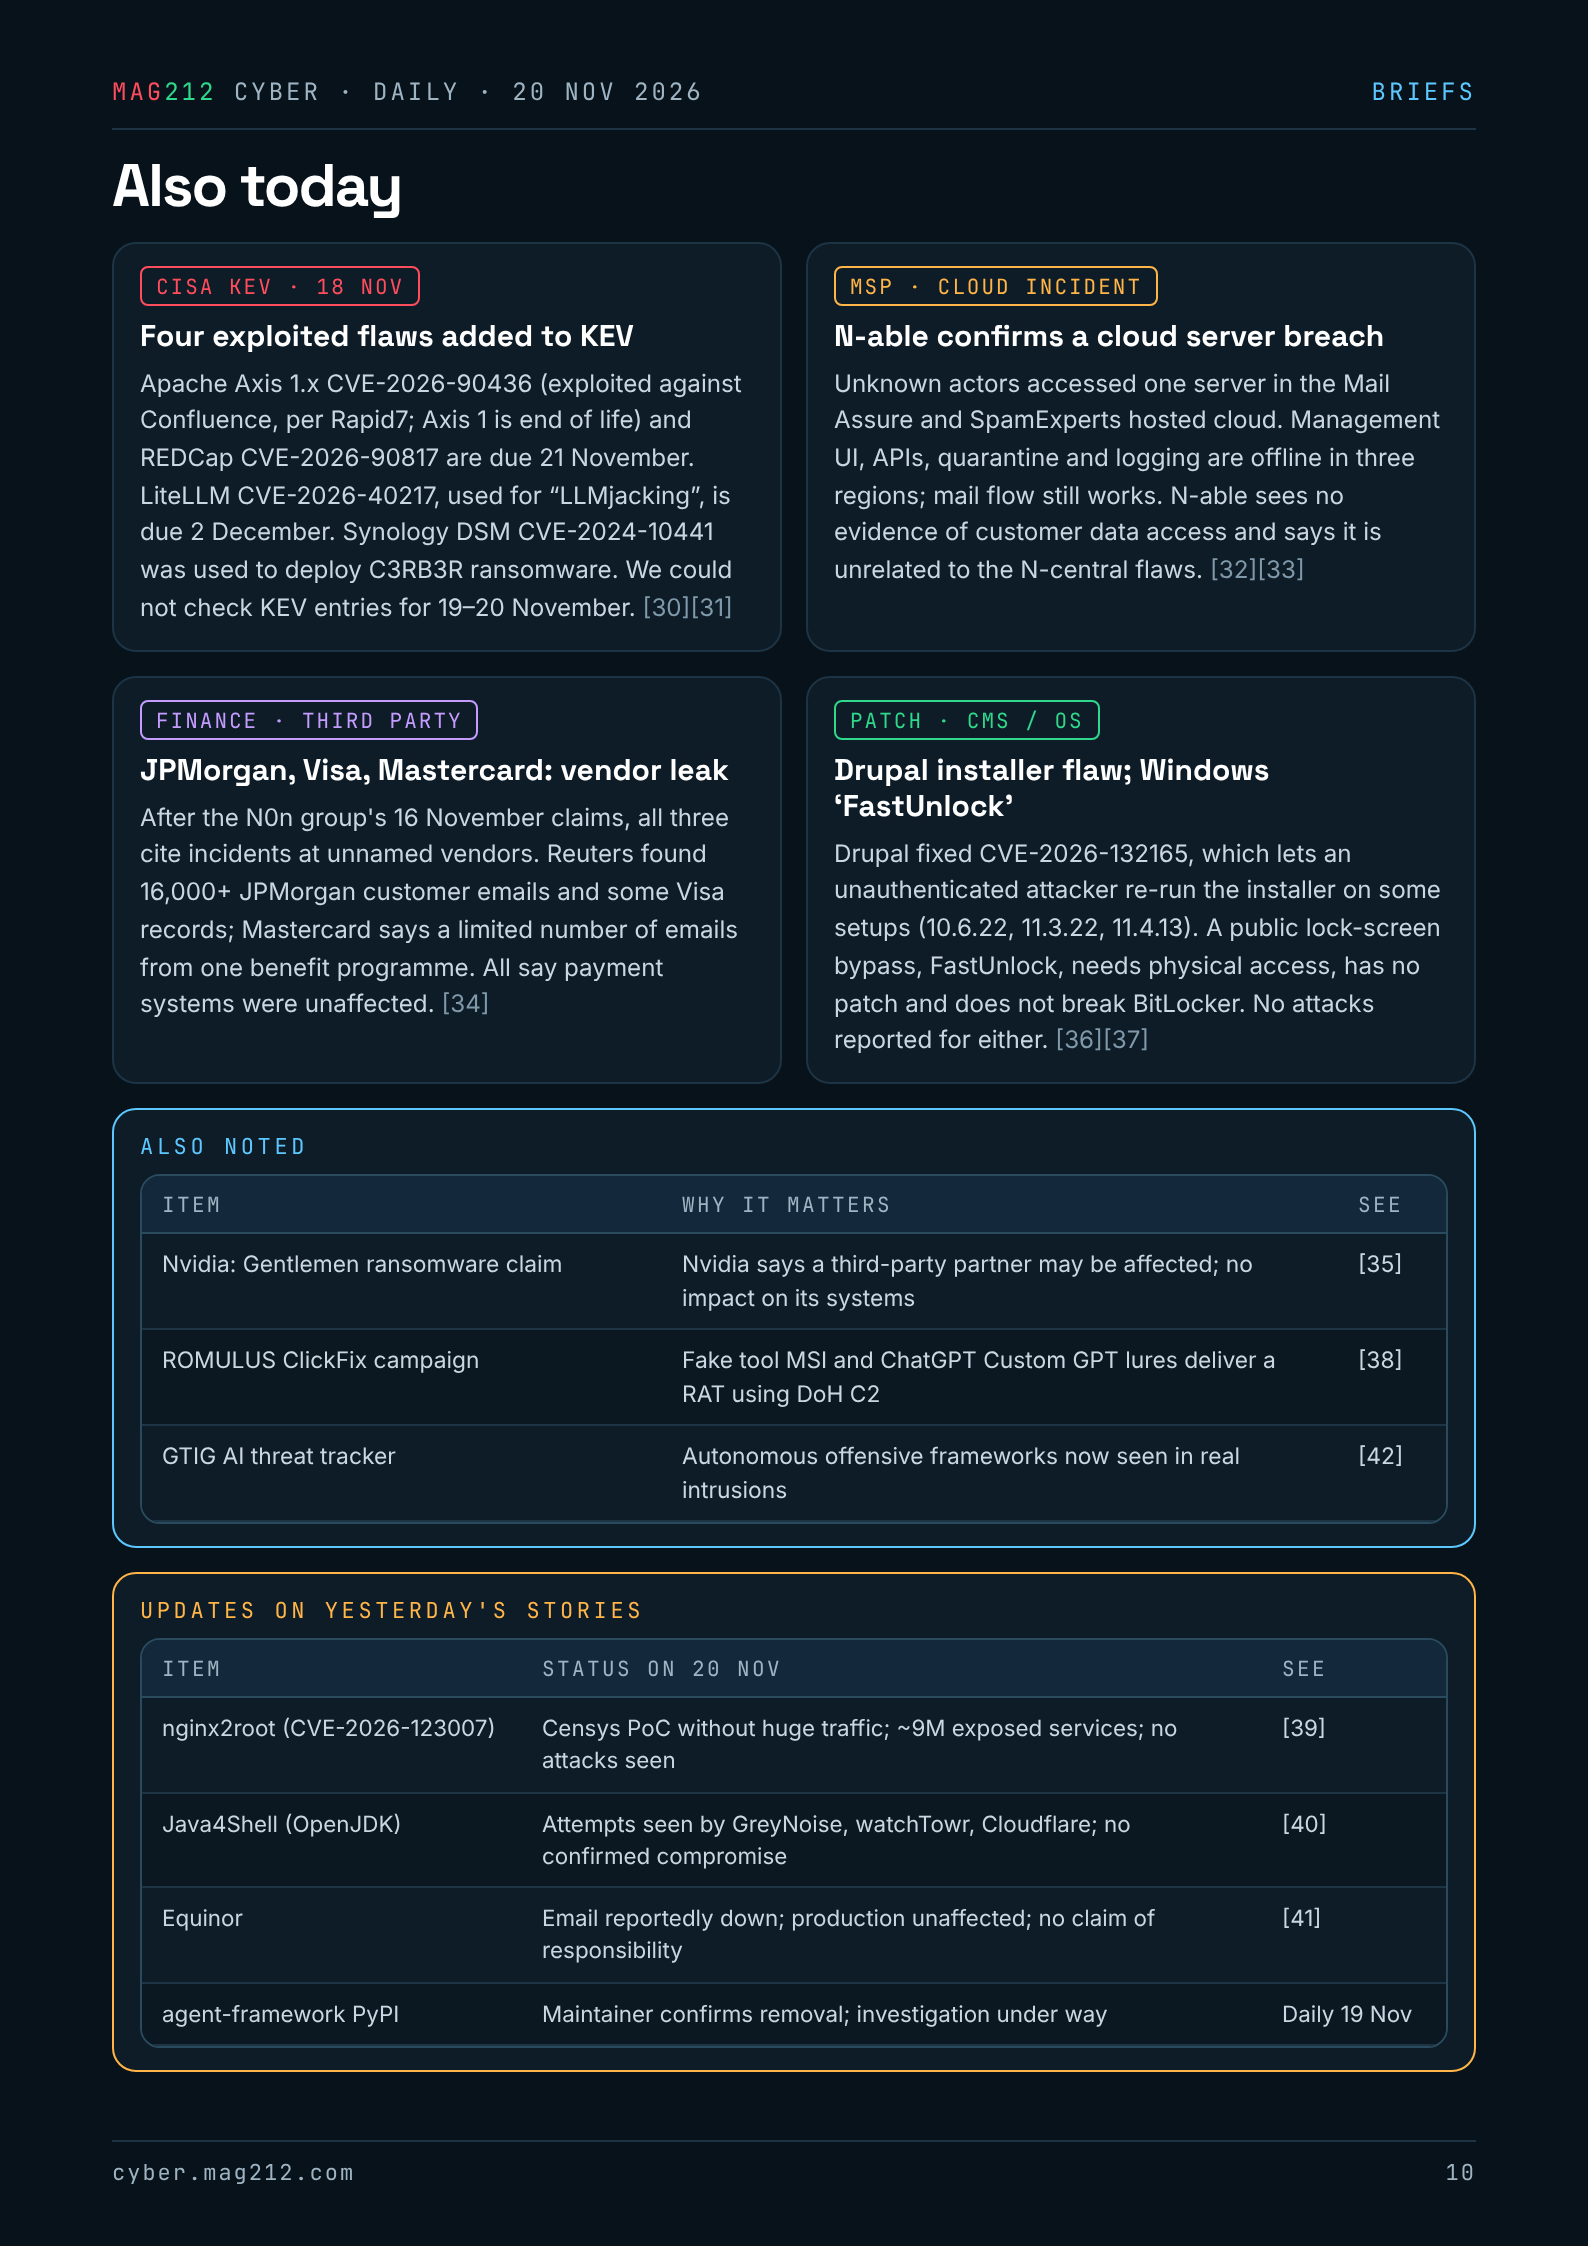
On 18 November CISA added four flaws to its Known Exploited Vulnerabilities catalog, as reported by The Hacker News: [1][2]
- Apache Axis 1.x, CVE-2026-90436 (CVSS 9.8, due 21 November). Unauthenticated code execution. Rapid7 saw it exploited against Atlassian Confluence Data Center. Axis 1 is end of life with no fixed release; migrate to Axis 2.
- Vanderbilt REDCap, CVE-2026-90817 (CVSS 9.8, due 21 November). Attackers delivered cryptominers.
- BerriAI LiteLLM, CVE-2026-40217 (CVSS 8.8, due 2 December). Used in “LLMjacking”: turning limited inference keys into admin access.
- Synology DSM, CVE-2024-10441 (CVSS 9.8, due 21 November). Used to deploy C3RB3R ransomware on NAS devices.
We could not reach cisa.gov to check additions on 19 and 20 November.
Why this matters
Briefs are where the next big story often starts. Today's KEV additions come with federal deadlines that land tomorrow, and two of the incidents are supply-chain stories: attackers reaching big names through their vendors and service providers. (MAG212 analysis)
N-able confirms a cloud server breach
Unknown attackers accessed one server in N-able’s Mail Assure and SpamExperts hosted cloud. The management interface, APIs, quarantine and logging are offline in the Americas, APAC and Europe, while mail flow and filtering still work. The disruption began on 16 November and was first blamed on configuration. N-able sees no evidence that customer data or mailboxes were accessed and says the incident is unrelated to recent N-central flaws. [3][4]
JPMorgan, Visa and Mastercard cite vendor incidents
After the N0n extortion group’s claims on 16 November, all three companies said data came from incidents at unnamed third-party vendors. Reuters found more than 16,000 JPMorgan customer email addresses, some with phone numbers and postal codes, and Visa records mostly from Asia-Pacific. Mastercard says a limited number of emails from one benefit programme were involved. All three say their payment systems were not affected. [5]
Nvidia responds to a ransomware claim
The Gentlemen ransomware group listed Nvidia on its leak site without details. Nvidia says it is investigating an incident that “may have affected a third-party partner” and sees no impact on its own systems. No stolen data has been confirmed. [6]
Drupal installer flaw and Windows “FastUnlock”
- Drupal CVE-2026-132165: on some setups, an unauthenticated attacker can re-run the installer at
/core/install.php, which can lead to site takeover. Fixed in 10.6.22, 11.3.22 and 11.4.13. Drupal calls vulnerable configurations uncommon; a proof of concept exists but no attacks are reported. [7] - FastUnlock: a public Windows lock-screen bypass that needs physical access and a lock screen offering Microsoft-account recovery. It uses Narrator to run programs as a limited account. BitLocker is not broken; there is no patch and no known abuse. [8]
ROMULUS ClickFix campaign
Blackpoint Cyber describes ROMULUS as a likely delivery service for a remote-access trojan and Legion Loader. Lures include ChatGPT Custom GPTs, and the chain runs through an MSI posing as a Stardock tool that sideloads a DLL. The RAT offers remote desktop, microphone and camera capture, and uses DNS over HTTPS for command and control. [9]
Updates on yesterday’s stories
- nginx2root (CVE-2026-123007): Censys reproduced the bug over cleartext HTTP/2 without Rapid7’s huge traffic volume and published its proof of concept. It estimates about 9 million services run an affected version with HTTP/2 on. No in-the-wild exploitation is reported. [10]
- Java4Shell (OpenJDK): GreyNoise, watchTowr and Cloudflare report exploitation attempts and scanning, but no confirmed compromise. Cisco, Siemens and Atlassian products are still waiting on fixes. [11]
- Equinor: Reuters reports internal email is down; production is not affected and nobody has claimed the attack. [12]
- Microsoft agent-framework on PyPI: a maintainer confirmed the malicious releases were removed and an investigation is under way.
Related on MAG212 CYBER
- MAG212 CYBER Daily, 20 November 2026: The keys to vSphere (full issue and PDF)
- MAG212 CYBER Daily, 19 November 2026: A ten-year-old counter
- MAG212 CYBER Daily, 18 November 2026: One equals sign too many
- MAG212 CYBER Weekly, 14 November 2026
- Subscribe free to MAG212 CYBER
Sources
- [1] The Hacker News, “CISA warns of 4 exploited flaws“, 19 Nov 2026.
- [2] SecurityWeek, “Critical Apache Roller, Axis vulnerabilities exploited in attacks“, 19 Nov 2026.
- [3] The Hacker News, “N-able confirms hackers accessed cloud server“, 19 Nov 2026.
- [4] SecurityWeek, “N-able blames service disruption on cyberattack“, 20 Nov 2026.
- [5] SecurityWeek, “JPMorgan, Visa, Mastercard cite third-party incidents amid data leak“, 20 Nov 2026.
- [6] SecurityWeek, “Nvidia responds to Gentlemen ransomware claim“, 19 Nov 2026.
- [7] The Hacker News, “Drupal patches critical installer flaw“, 19 Nov 2026.
- [8] The Hacker News, “New unpatched Windows 0-day FastUnlock“, 20 Nov 2026.
- [9] The Hacker News, “ROMULUS ClickFix attacks deliver RAT“, 20 Nov 2026.
- [10] SecurityWeek, “F5 patches critical nginx2root flaws as PoC exploits go public“, 19 Nov 2026.
- [11] SecurityWeek, “Java4Shell exploitation attempts begin as vendors rush out advisories“, 19 Nov 2026.
- [12] The Record, “Norway's Equinor hit by cyberattack“, 18 Nov 2026.
Written and edited by El Mostafa Ouchen for MAG212 CYBER. Facts checked against the sources above as of 20 November 2026, 6:00 AM PT.