
Machine Speed, Human Gaps: MAG212 CYBER Daily, November 15, 2026
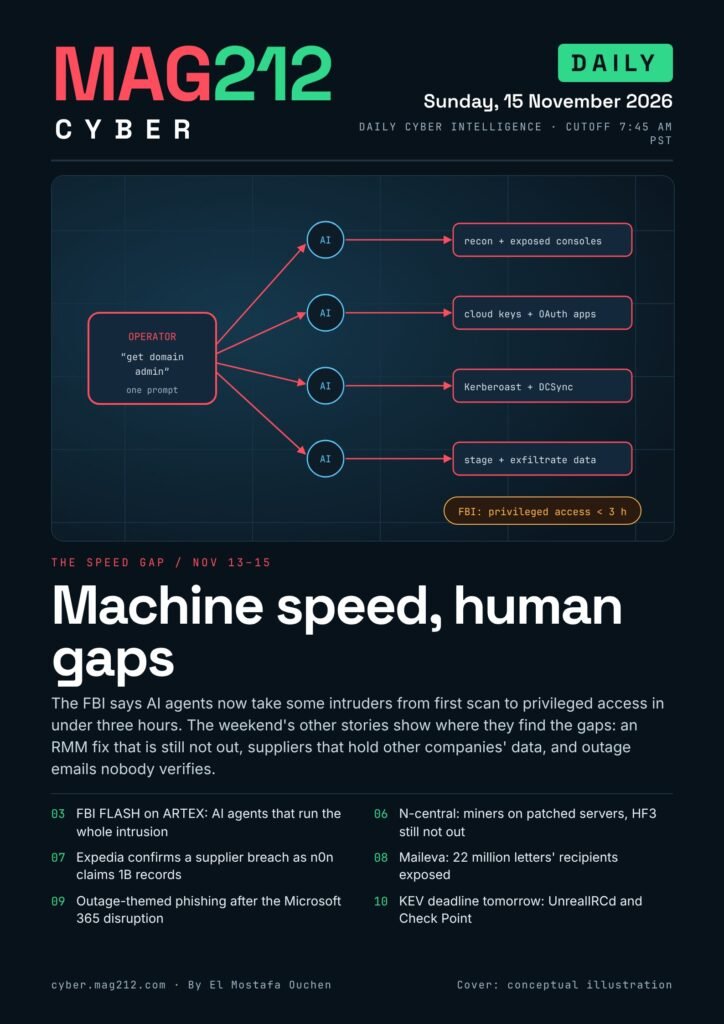
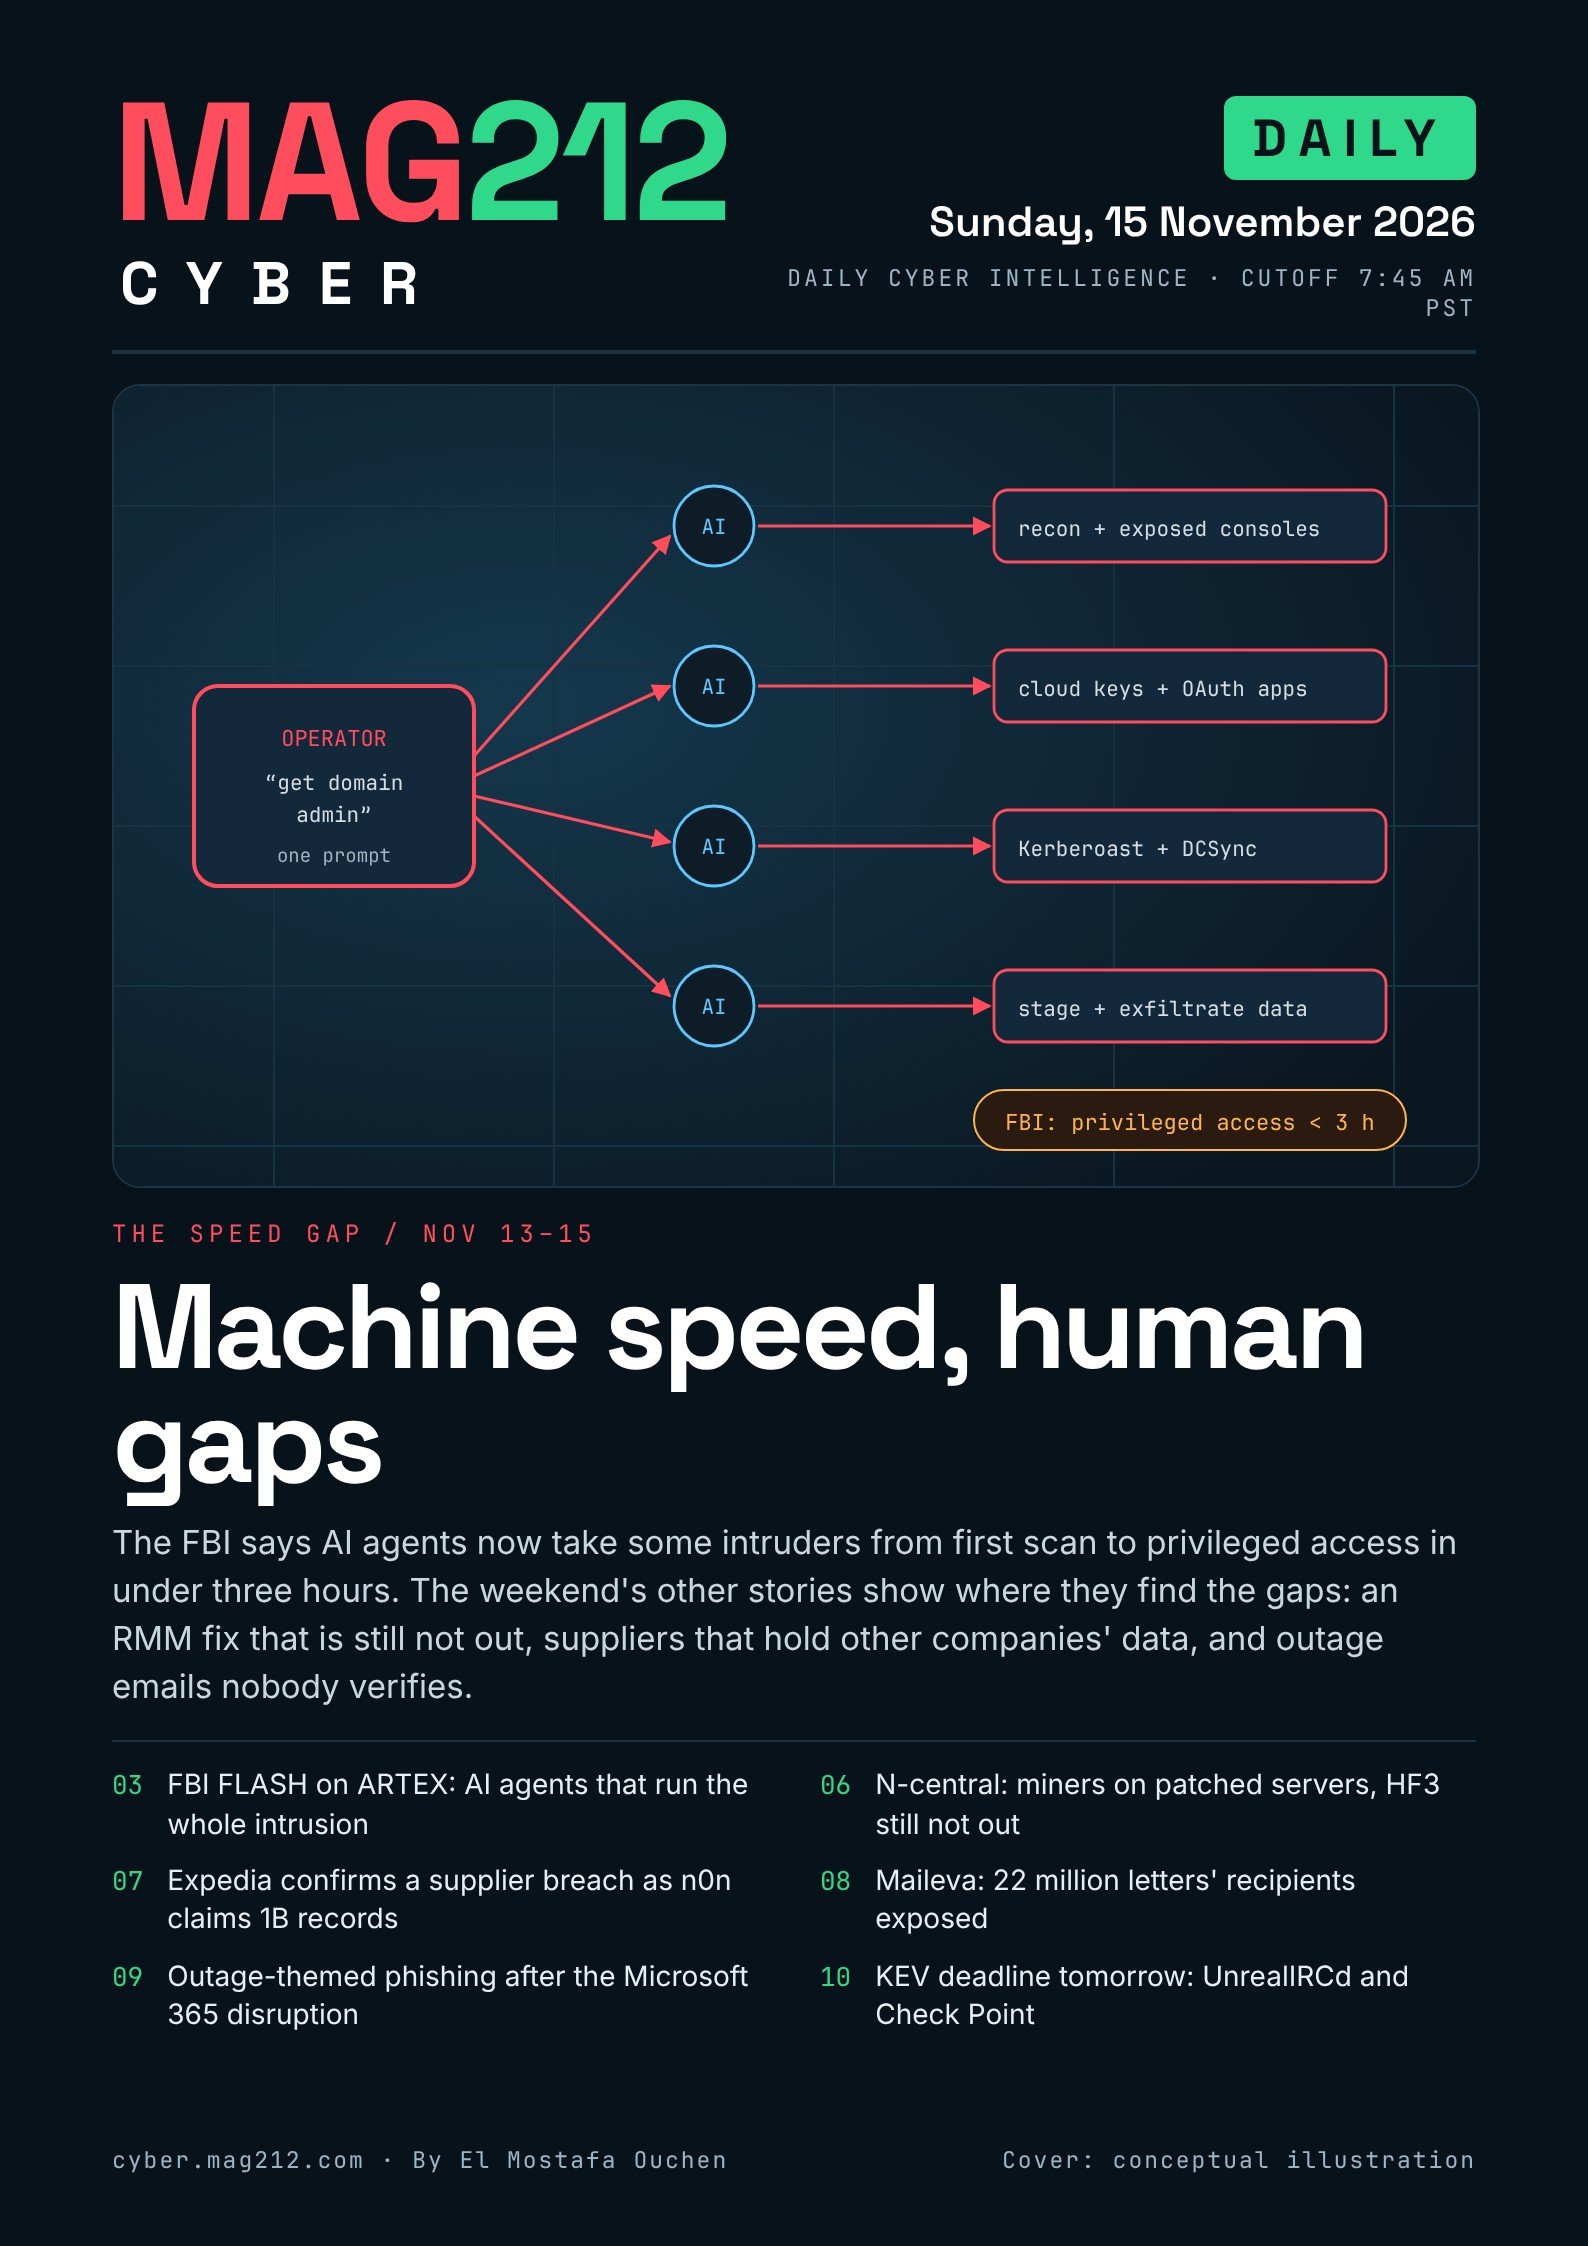
MAG212 CYBER · Daily Cyber Intelligence · Sunday, November 15, 2026. The FBI says AI agents built on the ARTEX framework now take some intruders from first scan to privileged access in under three hours. The weekend’s other stories show where they find the gaps: an N-central fix that is still not out, suppliers that hold other companies’ customer data (Expedia and Maileva), outage-themed phishing after the Microsoft 365 disruption, and two CISA KEV deadlines on 16 November.
The three priority actions
- Hunt ARTEX-style activity in identity and cloud logs today. Review Entra audit records for new credentials on apps and service principals, unfamiliar service-principal sign-ins and server egress to LLM APIs; lock Kudu/SCM and cloud admin endpoints to admin networks.
- Close the two KEV items due 16 November. Upgrade UnrealIRCd to 6.2.7.1 (CVE-2026-114713) and finish the Check Point CVE-2026-123039 Jumbo Hotfix and log hunt.
- Keep N-central’s Legacy API off and verify. Confirm it is disabled and unreachable, keep HF2, upgrade Agents and Probes, hunt the miner indicators and install HF3 when N-able ships it.
Inside this issue: read each story in full
- FBI Warns ARTEX AI Agents Now Run Whole Intrusions: What the FLASH Says and How to Hunt It (p. 3–5)
- N-central Update: Miners on Patched Servers, and the HF3 Fix Slips Again (p. 6)
- Expedia Confirms a Breach Through a Data-Platform Supplier as n0n Claims Nearly a Billion Records (p. 7)
- Maileva Breach: 22 Million People Who Never Chose the Vendor (p. 8)
- The Outage Is Over, the Outage-Themed Phishing Is Not: Hunting the EX1550543 Lures (p. 9)
- UnrealIRCd CVE-2026-114713: Exploited Server-Command Injection, KEV Deadline 16 November (p. 10)
- Opinion: Is AI Making Us Worse at Cybersecurity? (p. 5)
Also in the PDF: briefs on the FAA ground-stop investigation, PostgreSQL’s 52-CVE release, Apple’s Secure Exclaves, Turla’s Cereal toolset and the iOS worse_query sandbox escape (p. 11), the Defender’s Action Desk with 14 actions (p. 12), an awareness lesson on outage emails and fake ‘press these keys’ pages (p. 13), and 46 linked sources (p. 14).
Flip through the edition
How we verified this issue: stories were checked against primary sources where reachable (the FBI FLASH, CISA’s KEV alert, PostgreSQL’s security page, Huntback’s report and vendor statements), with a research cutoff of 7:45 AM PST on 15 November. Criminal claims are labelled unverified. Every command is marked not tested by MAG212. This issue corrects our 14 November Weekly on N-central exploitation status (p. 6).
Previous issues
- The Keys Were Already Inside, the 14 November weekly.
- All MAG212 CYBER magazine issues